

Microsoft 365 Apps is a suite of productivity tools that includes the following apps and services offered by Microsoft through a subscription service:-
- Microsoft Teams
- OneDrive
- SharePoint
- PowerPoint
- Outlook
- Word
- Excel
- Microsoft Office
- Microsoft OneNote
- Microsoft Access
- Microsoft Publisher
- Microsoft Exchange Server
- Skype for Business
- Power BI
- Microsoft Visio
- Microsoft Lists
- Yammer
- Microsoft Project
- Skype
Hackers often target these applications because they are widely used in business environments, providing a large potential attack surface, and successful compromises can provide access to sensitive information and corporate networks.
When Microsoft introduced support for SketchUp (SKP) files in June 2022, it unintentionally revealed 117 vulnerabilities in Microsoft 365 apps.
The cybersecurity analysts at the ThreatLabz research team discovered all these vulnerabilities.
Live API Attack Simulation Webinar
In the upcoming webinar, Karthik Krishnamoorthy, CTO and Vivek Gopalan, VP of Products at Indusface demonstrate how APIs could be hacked. The session will cover: an exploit of OWASP API Top 10 vulnerability, a brute force account take-over (ATO) attack on API, a DDoS attack on an API, how a WAAP could bolster security over an API gateway
Technical analysis
However, to catalog the 117 vulnerabilities, Microsoft assigned the following CVE IDs:-
Besides this, due to these vulnerabilities, Microsoft temporarily disabled SketchUp in June 2023. Microsoft 365 got SketchUp file support in 2022, a new 3D file format. But, unlike other 3D formats, it’s new, and new features like this can bring security risks.
Reverse engineering is key for cybersecurity, letting experts analyze code to uncover and address potential vulnerabilities.
In Microsoft 365, MSOSPECTRE.DLL handles 3D file parsing. Researchers probed vulnerabilities in SketchUp format in version 16.0.16026.20000 (Jan 2023). Using IDA Pro, functions with ‘SU’ prefix were found in MSOSPECTRE.DLL, revealing SketchUp C APIs from SketchUp SDK.
Combining reverse engineering and dynamic debugging, researchers identified Spectre::Transcoder::ImporterSKP::ImportToAsset3D as the SKP parsing function in Microsoft 365.
Microsoft fixed Zscaler-discovered vulnerabilities in April and May 2023:-
- CVE-2023-28285
- CVE-2023-29344
However, a ThreatLabz analysis found a bypass in CVE-2023-29344’s patch, prompting Microsoft’s response via CVE-2023-33146.
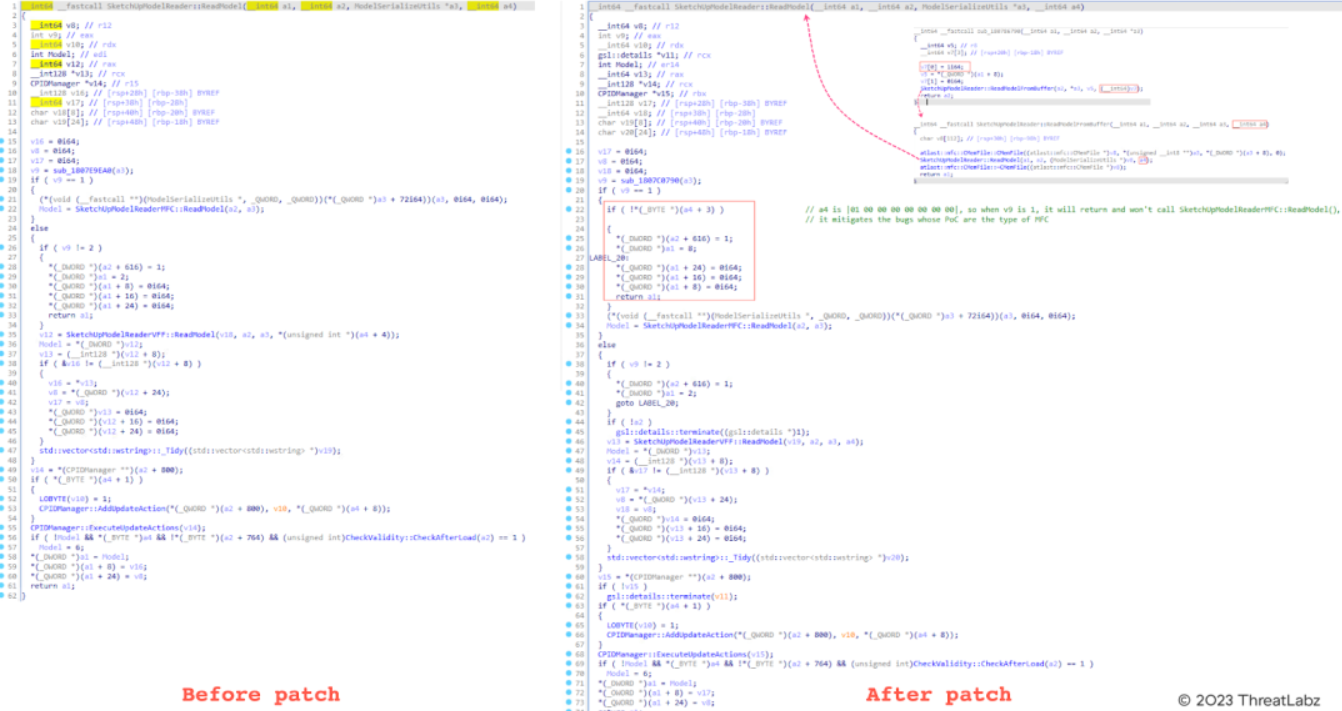
The CVE-2023-29344 patch was released to fix FreeImage vulnerabilities in May 2023, and the following version is the patched version of MSOSPECTRE.DLL:-
- 16.0.16327.20240
Patch disabled MFC-type SKP file support due to reported vulnerabilities. Incomplete fix, as FreeImage library vulnerabilities persist with VFF-type SKP files.
The PoC crafted SKP VFF-type template with SketchUp and embedded zip. The extracted zip was analyzed with the 010 Editor, revealing the image in the materials folder.
Moreover, this approach enabled analysts to reproduce 97 CVE-2023-29344 patch vulnerabilities in Microsoft 365 apps. Since the CVE-2023-33146 was assigned for bypassing the patch, that’s why Microsoft disables SketchUp file insertion in Office docs in response.
Wrapper functions
Here below, we have mentioned all the Wrapper functions:-
- Spectre::Transcoder::ImporterSKP::CountEntities
- Spectre::Transcoder::ImporterSKP::ExportEntities
- Spectre::Transcoder::ImporterSKP::ExportComponentInstance
- Spectre::Transcoder::ImporterSKP::ExportFaces
- Spectre::Transcoder::ImporterSKP::GetMaterial
- Spectre::Transcoder::SkpUtils::GetTextureId
- Spectre::Transcoder::ImporterSKP::GetTexture
- Spectre::Transcoder::ImporterSKP::AddFacesGeometry
Real-World Cases
- Microsoft Office SKP file parsing `CVertex` object use-after-free vulnerability
- Microsoft Office SKP file parsing TIFF image integer overflow vulnerability
- Microsoft Office SKP file parsing uninitialized memory vulnerability
- Microsoft Office SKP File parsing BMP image out-of-bounds write vulnerability
- Microsoft Office SKP File parsing PICT image out-of-bounds write vulnerability
Recommendations
Here below, we have mentioned all the recommendations provided by the researchers:-
- Make sure to prioritize security audits.
- Ensure blackbox fuzzing for third-party libraries to avoid vulnerabilities.
- Always keep Microsoft 365 apps updated with the available latest version.
Experience how StorageGuard eliminates the security blind spots in your storage systems by trying a 14-day free trial.


