

Law enforcement agencies have successfully dismantled a clandestine communication platform known as “Ghost,” which was used by cybercriminals to coordinate illicit activities.
This significant crackdown resulted in the arrest of 12 key suspects, marking a major victory in the fight against cybercrime.
Background on the Ghost Platform
The Ghost platform, designed to operate under the radar, allowed its users to communicate securely using advanced encryption techniques.
It was marketed as an ultra-secure platform, attracting a variety of nefarious actors, including hackers, digital extortionists, and online scammers.
The platform’s anonymity and robust encryption made it a haven for cybercriminals seeking to evade detection.
According to the Europal’s report, the operation to dismantle the Ghost platform culminated months of intelligence gathering and coordination between international law enforcement agencies.
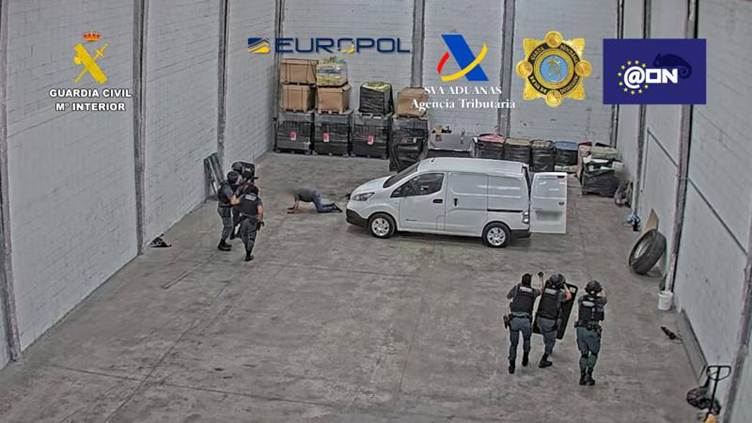
Through meticulous tracking and monitoring, authorities identified key administrators and high-profile users of the platform.
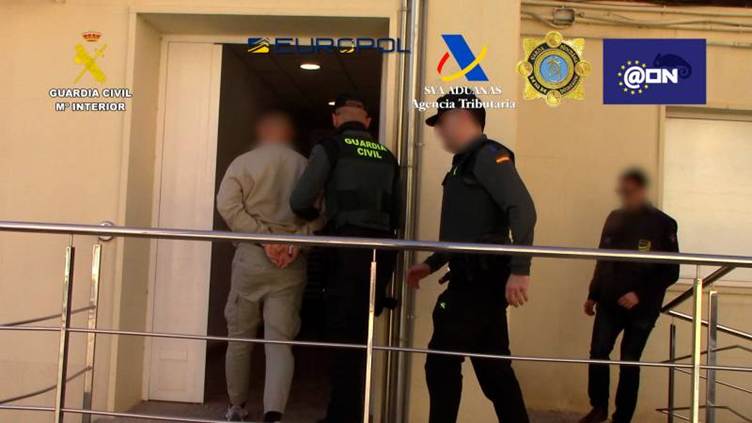
On the night of the operation, simultaneous raids were conducted across multiple countries, leading to the arrest of 12 suspects.
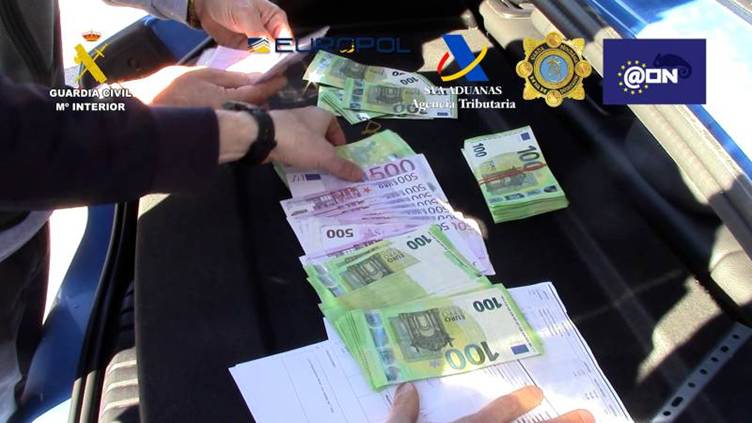
These arrests were backed by substantial evidence collected from surveillance and digital forensics, providing irrefutable proof of the suspects’ involvement in cybercriminal activities.
Charges and Implications
Those arrested face a range of charges, including conspiracy to commit cybercrime, money laundering, and identity theft.
The shutdown of the Ghost platform and the arrests send a strong message to the global cybercrime community that no platform is beyond the reach of law enforcement.
The dismantling of Ghost also highlights the increasing effectiveness of international cooperation in tackling cybercrime.
Sharing intelligence and best practices has become crucial in combating sophisticated networks that operate across borders.
Ghost’s shutdown is expected to disrupt significantly the operations of various cybercrime groups.
Many of these groups relied on Ghost to plan and execute attacks, including ransomware assaults and phishing campaigns.
The sudden loss of this communication channel will likely create temporary chaos within these networks, giving security professionals and authorities a window of opportunity to further pursue these groups.
As technology evolves, so does the sophistication of cybercrime tools and platforms. However, this operation demonstrates that law enforcement agencies are keeping pace, employing advanced techniques to uncover and dismantle such platforms.
The public is advised to remain vigilant and report any suspicious online activities to local authorities.
This significant victory against cybercrime underscores a commitment to protecting digital spaces and ensuring that those who seek to exploit them face justice.
As the world becomes increasingly digital, such operations serve as a reminder of the ongoing efforts to safeguard online security.
Are you from SOC/DFIR Teams? – Analyse Malware, Phishing Incidents & get live Access with ANY.RUN -> Start Now for Free.







