There is a collection of IOCs from VirusTotal and YARA Rules that has been recently open-sourced by the Google Cloud Threat Intelligence team.
As a result, Google has taken this step to make it easier for security researchers to catch Cobalt Strike components within their network.
While apart from this, using these detection signatures cybersecurity analysts will also be able to detect the deployed versions of Cobalt Strike in their environment.
165 YARA Rules to Detect Cobalt Strike
In order to test the resilience of red teams’ cyber defenses, Cobalt Strike is a popular tool that is used by red teams. Over the last decade, it has been subjected to many development changes and improvements in order to reach its current state.
By doing this, malicious activity can be detected more effectively by targeting potential leaked and cracked versions of the software. In this way, it is easier to distinguish between deployments controlled by threat actors versus those controlled by legitimate deployments.
By leveraging the Cobalt Strike set of components, Google has built a detection system that is capable of detecting these malicious variants in the wild at an extremely high degree of accuracy with YARA-based detection.
There are approximately ten to one hundred attack template binaries included in each Cobalt Strike version. An important aspect of Cobalt Strike is that it incorporates multiple software tools into one jar file that functions as a single tool.
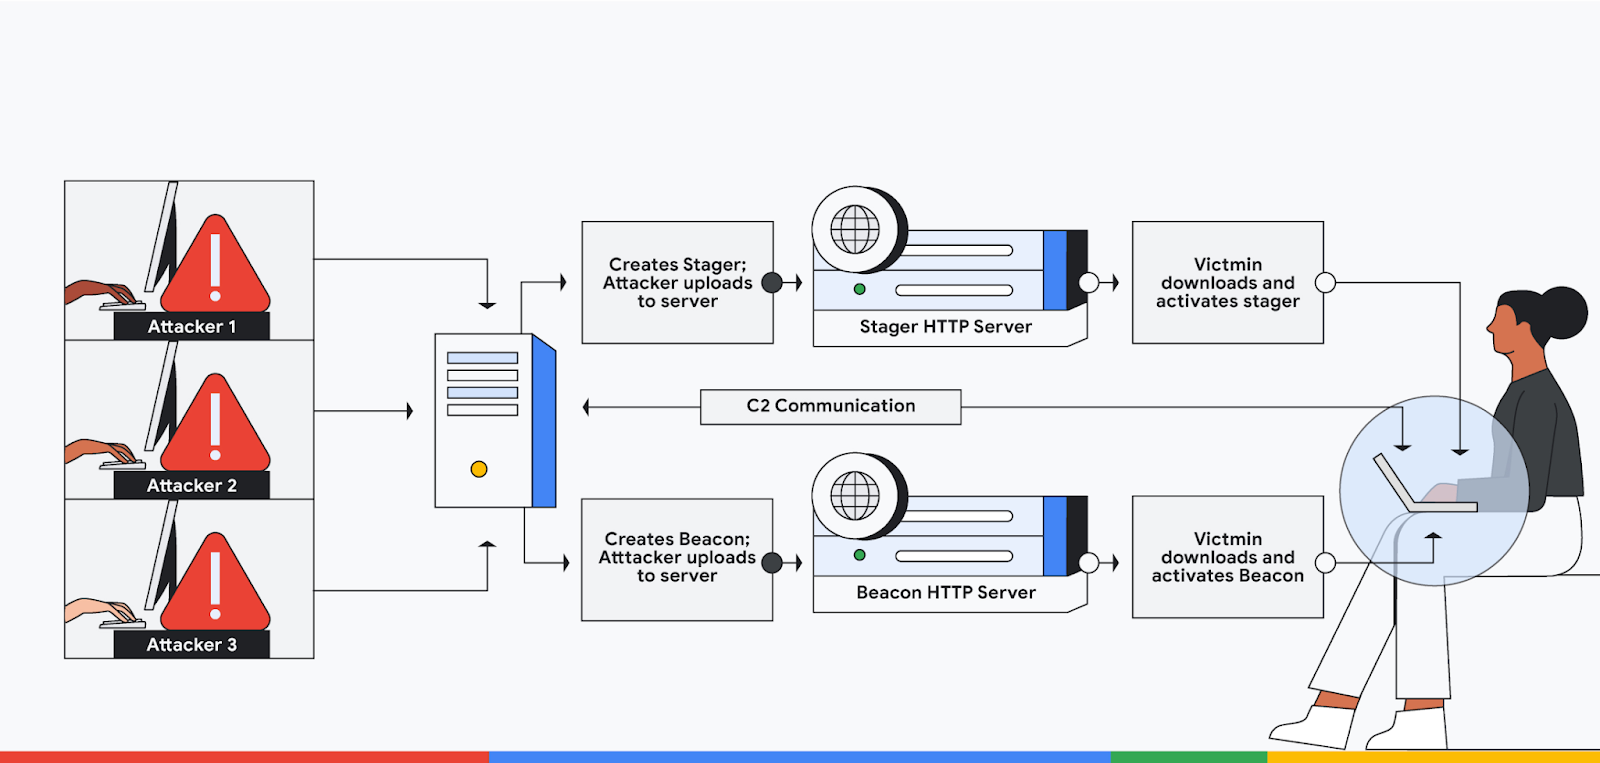
As a client, a JAR file is activated that connects the actors to the Team Server so that they can connect to it. Clients are used by actors to manage their teammates and infected hosts through a graphical user interface (GUI).
Moreover, a collection of detection signatures is also shared by Google for an open-source threat emulation framework, Sliver. While threat actors have also adopted this framework as an alternative to Cobalt Strike to conduct security testing.
It is therefore becoming increasingly common for Cobalt Strike to be used in cyberattacks that might lead to the theft of data and ransomware infections, as it is one of the most widely used tools.
This method of attack is used by threat actors after they have deployed so-called beacons, which enable them to access compromised devices remotely and perform post-exploitation tasks after the attacks have been conducted.
In order to harvest sensitive data from compromised servers or to deploy further malware, attackers access compromised networks through beacons that have been deployed on the networks of their victims.
VirusTotal customers have access to a collection of community signatures containing these YARA rules that have been formalized as the final YARA rules. In order to make the tool more difficult to abuse by threat actors, Google is moving it back to the domain of legitimate red teams.
Managed DDoS Attack Protection for Applications – Download Free Guide