

A critical vulnerability has been discovered in the popular “Really Simple Security” WordPress plugin, formerly known as “Really Simple SSL,” putting over 4 million websites at risk.
The flaw, identified as CVE-2024-10924, exposes websites using the plugin to potential remote attacks, enabling threat actors to gain unauthorized administrative access.
Vulnerability Overview
The vulnerability affects versions 9.0.0 through 9.1.1.1 of the Simple Security plugin, including the Pro and Pro Multisite versions.
Exploiting an authentication bypass flaw, attackers can remotely access any user account, including administrator accounts, if the “Two-Factor Authentication” feature is enabled.
Free Ultimate Continuous Security Monitoring Guide - Download Here (PDF)
The flaw stems from improper handling of user verification in the plugin’s two-factor REST API functions.
This security issue is particularly concerning due to its high CVSS score of 9.8, classifying it as “Critical.”
The vulnerability allows attackers to gain access to privileged accounts and take full control of affected websites.
A large-scale automated attack exploiting this flaw could potentially target millions of WordPress sites globally.
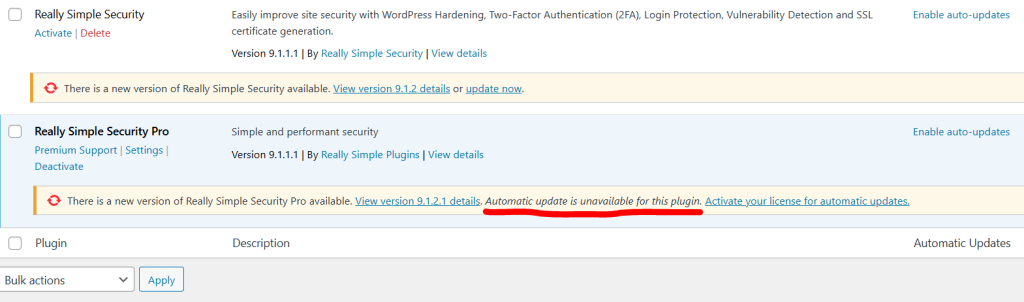
Upon identifying the issue on November 6, 2024, Wordfence Threat Intelligence began working closely with the plugin’s vendor to address the vulnerability.
The developer responded promptly, and a patched version of the plugin (9.1.2) was released on November 14, 2024.
The WordPress.org plugins team also initiated a forced update to ensure that most sites using the plugin are automatically updated to the secure version.
However, site owners are strongly advised to manually verify that their plugins are updated to version 9.1.2 or higher. Websites running older versions remain vulnerable to potential attacks.
With over 4 million websites still relying on this crucial plugin, site administrators are urged to check their WordPress installations and apply the update immediately.
Additionally, users of the Pro and Pro Multisite versions without auto-update enabled should manually install the latest patch to secure their sites.
Analyze Unlimited Phishing & Malware with ANY.RUN For Free - 14 Days Free Trial.


