

Mandiant researchers have recently reported that 55 zero-day vulnerabilities were actively exploited in 2022, most against the following brands and their products:-
- Microsoft
- Apple
Researchers state that hackers are still targeting zero-day vulnerabilities in malicious campaigns. It has been reported that most of these vulnerabilities resulted in the attacker being able to either gain elevated privileges or execute remote code on vulnerable devices.
Zero-days Exploited in 2022
However, it is important to note that compared to recent years, there has been a decline in the overall number and proportion of financially motivated zero-day exploits in 2022.
There were 55 zero-day flaws exploited in 2022; 13 were exploited by cyber-espionage groups, while Chinese cyber spies exploited seven.
Seven zero-day vulnerabilities have been exploited by China so far, making the country the most prolific. And here below, we have mentioned those seven flaws:-
- CVE-2022-24682
- CVE-2022-1040
- CVE-2022-30190
- CVE-2022-26134
- CVE-2022-42475
- CVE-2022-27518
- CVE-2022-41328
One of the flaws exploited by Russian threat actors overlapped with another two flaws exploited by North Koreans. In three cases, Mandiant could not determine the origin of the espionage attack.
Explicit Financial Motives Decline in 2022
Notably, there was a decrease in the proportion of zero-day vulnerabilities exploited as part of financially motivated operations in 2022.
Exploiting n-day vulnerabilities, which have already been patched, is one of the most common vectors used to transmit ransomware and extortion attacks, as observed in Mandiant Incident Response and Managed Defense investigations.
In order for this decline to have occurred, there may have been a number of factors contributing to it. A significant number of zero-day exploits, including extortion campaigns utilizing four Accellion FTA vulnerabilities simultaneously, occurred in 2021. It was an exceptional year for zero-day exploits across the board.
Most Exploited Vendors & Product Type
Three large vendors, whose technology is widely adopted worldwide and whose distribution mirrors previous years, were disproportionately affected by zero-day vulnerabilities in 2022.
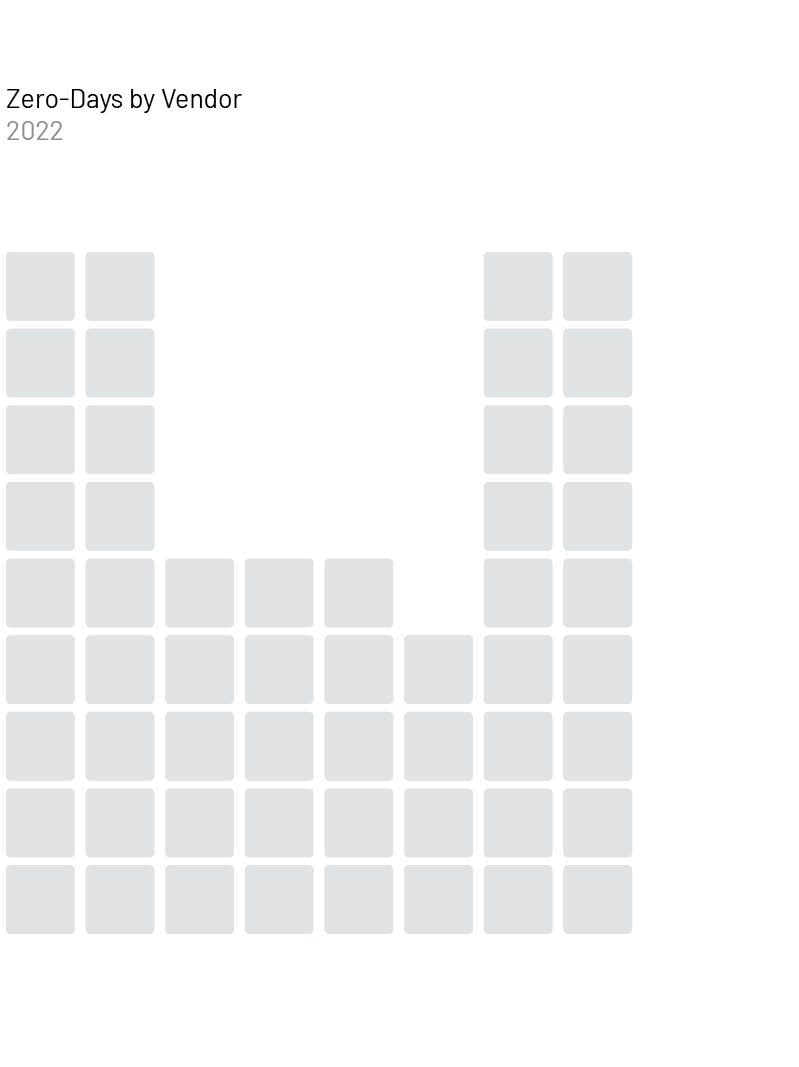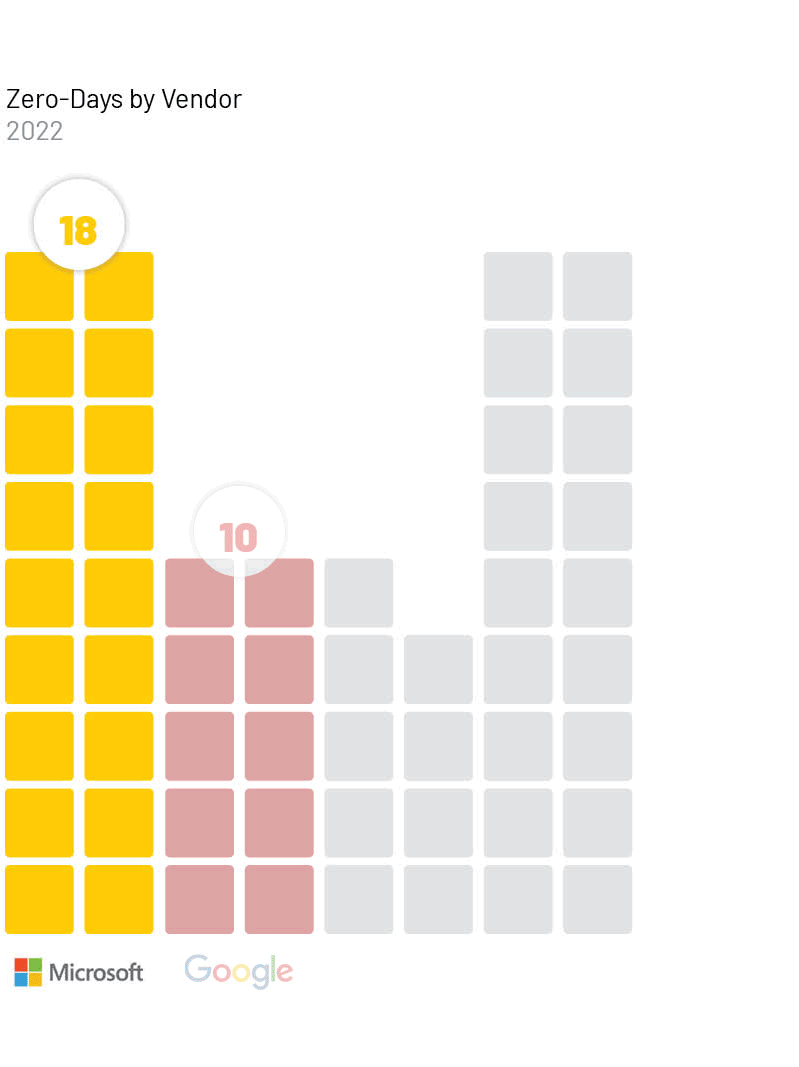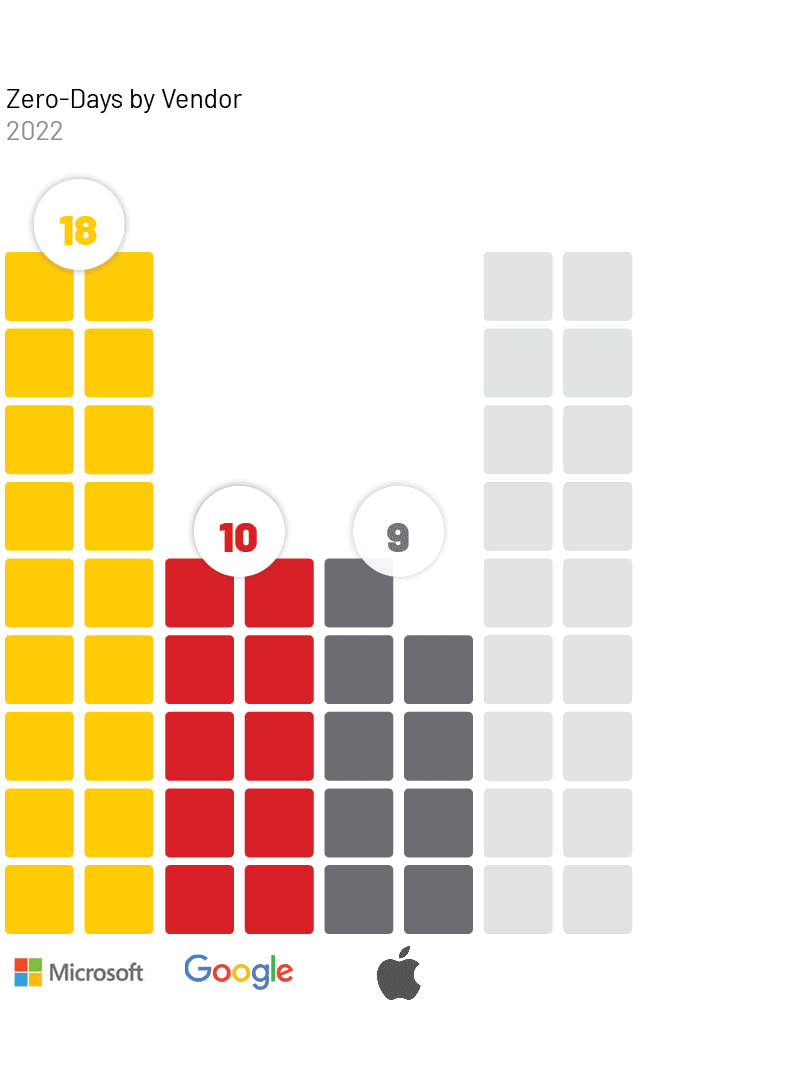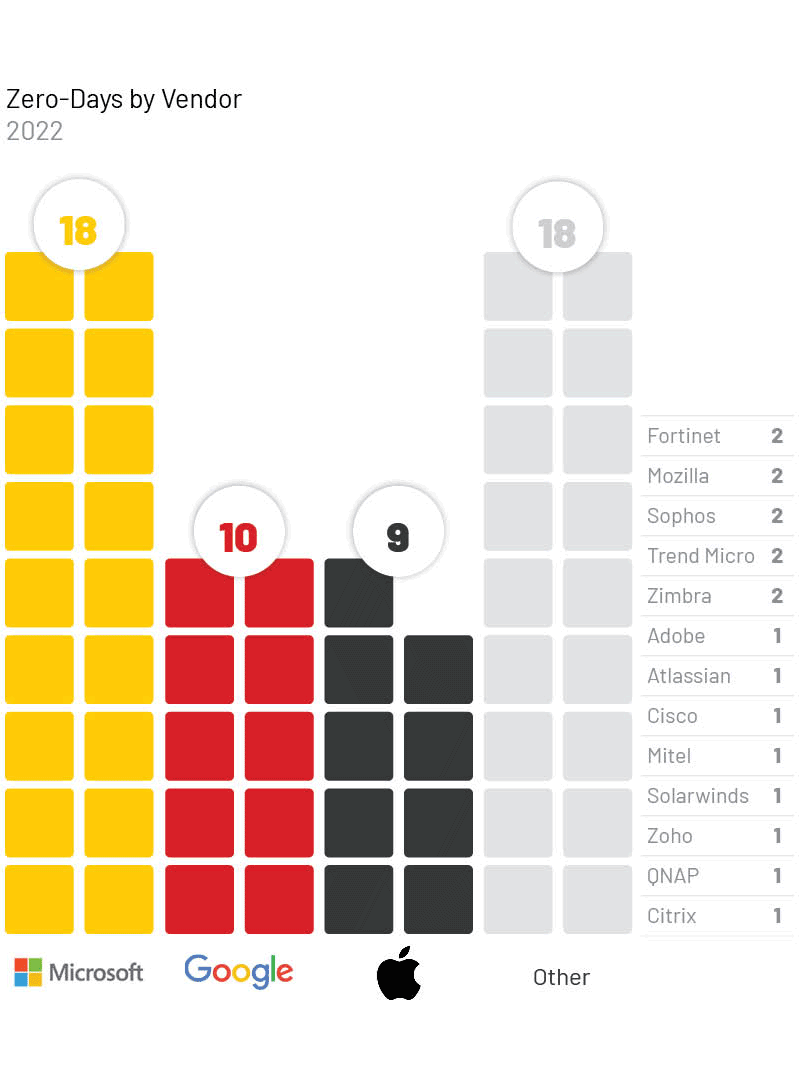
Some threat actors may have targeted unique vendors or niche products based on specific targets or victims of interest. Those technologies were especially useful as attack vectors for those particular targets.
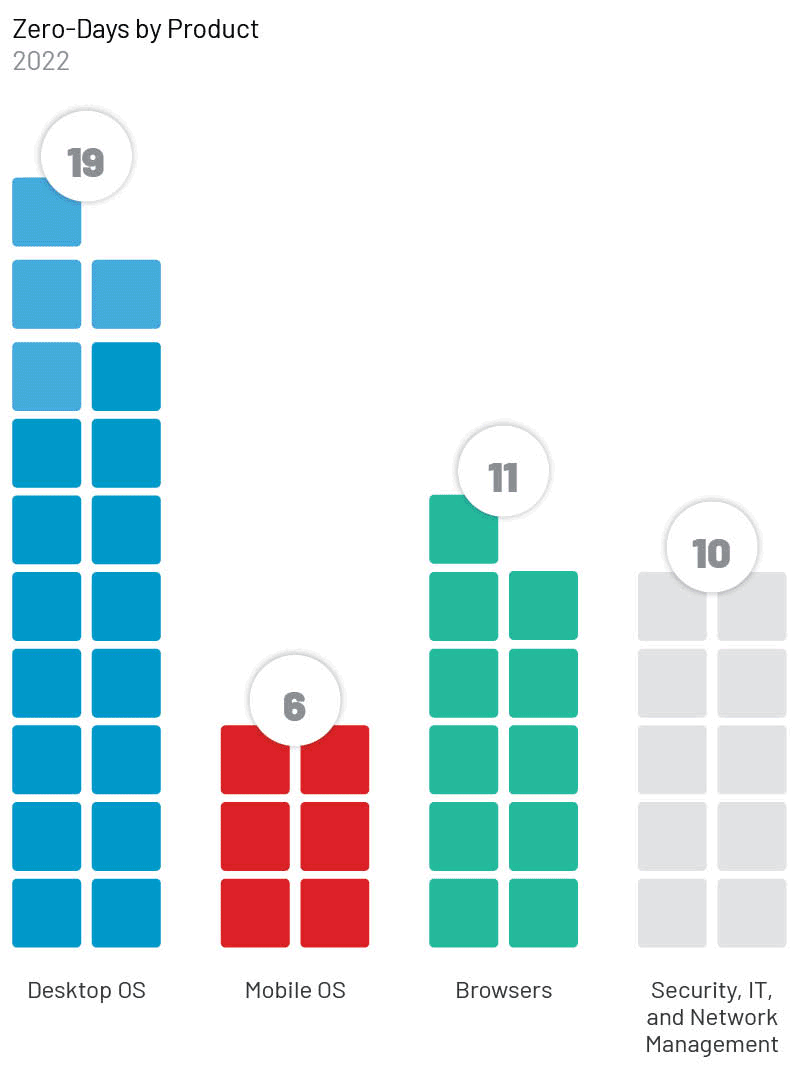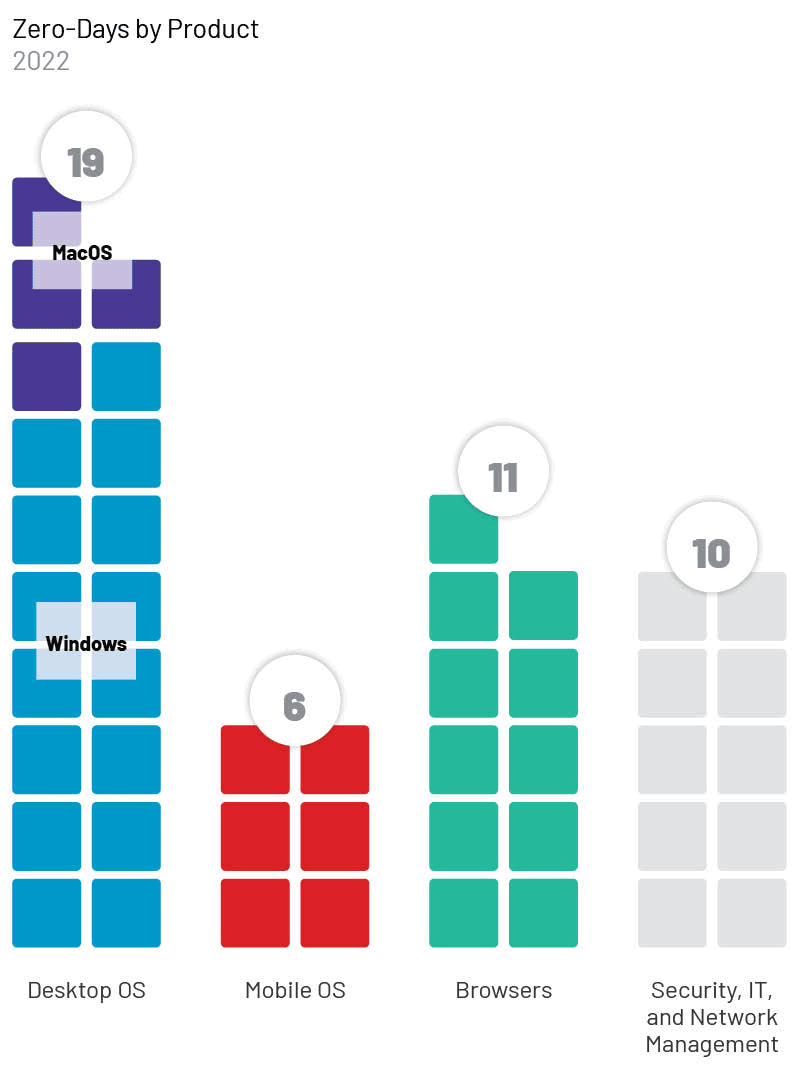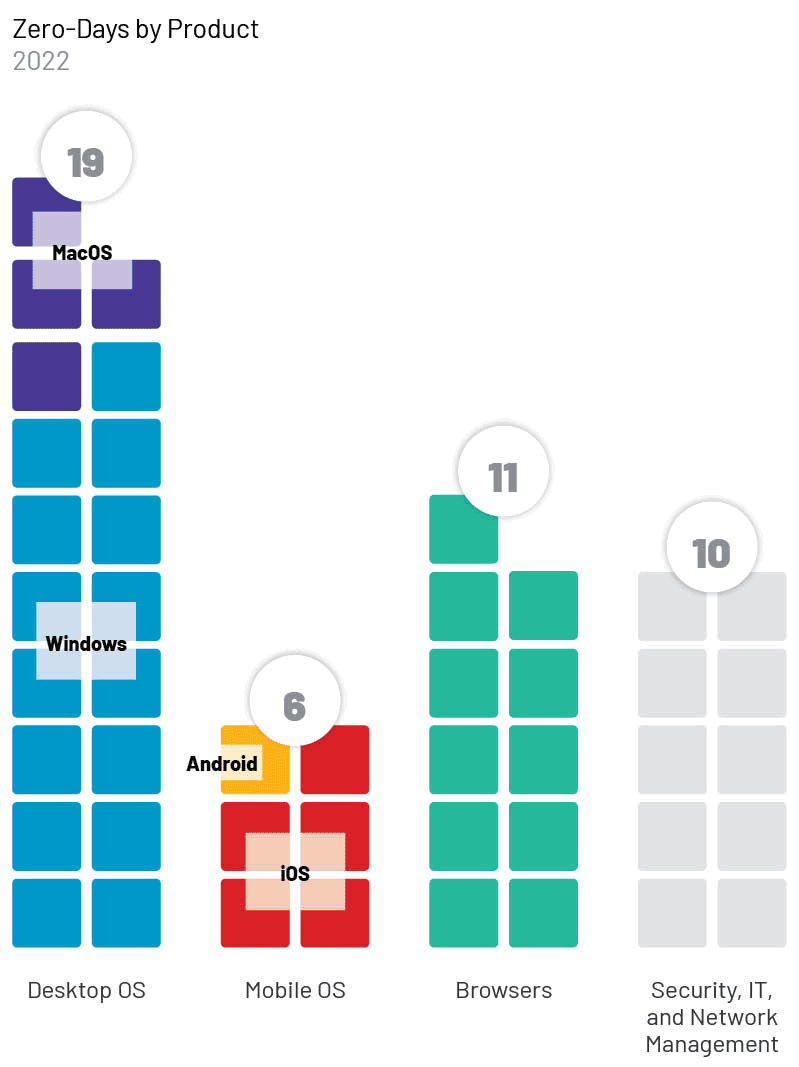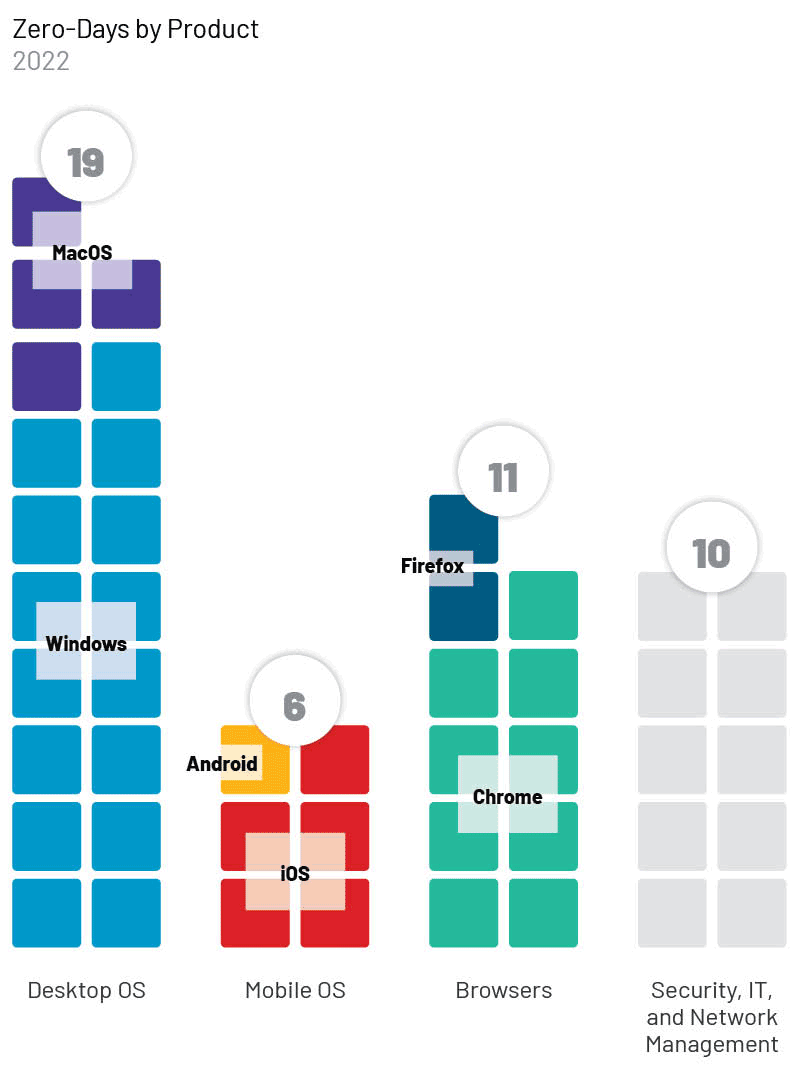
Among the most exploited products were:-
- Operating systems (19)
- Browsers (11)
- Security, IT, and network management products (10)
15 zero-day exploits have been identified in Windows, most of which target the desktop operating system in 2022.
Mitigations
Since zero-day vulnerabilities don’t exist, the patches protecting systems against them can be difficult. However, organizations can take steps to mitigate their impact:-
- When exposing internal devices to the internet, implement IP-based allow lists if necessary.
- Instead of exposing your servers to the internet, use private tunnels or VPNs to access them.
- To maintain the principle of least privilege, it is advisable that the user’s access rights are restricted as much as necessary.
- Segment your network in the case of a breach to reduce the attack’s spread.
- It is imperative to monitor your network.
- Make sure to install firewalls.
- Ensure the use of e-mail and web filtering products.
- Always make sure that your endpoints are secure.
It is imperative to properly configure Microsoft, Google, and Apple products, including network segmentation and least privilege policies since they are the most exploited vendors.
During the first quarter of 2023, it has been estimated that the number of Russian cyber threats had increased by 50%, primarily targeting Ukrainian civilian and military assets and those of its partners.
Building Your Malware Defense Strategy – Download Free E-Book
Related Read
- APT Hackers Group Exploiting the Window OS Using New Zero day Vulnerability
- Hackers Exploit Cisco Zero Day Vulnerability in Wild Resulting in DoS Condition
- Telegram Zero day Flaw Abused by Attackers in Wild to Install Malware and Cryptominers
- CISA Urgent Warning: Adobe ColdFusion Bug Exploited As A Zero-day in the Wild
- Apple WebKit Zero-Day Vulnerability Exploited to Hack iPhones, iPads, and Macs
- Exploit Released for GoAnywhere File Transfer Zero-Day Flaw





