

The U.S. federal government commission has recently detected a new backdoor on Thursday; the backdoor implemented total visibility and complete control over the agency network.
The cybersecurity researchers who have detected this backdoor have claimed that it is a “classic APT-type operation.” Threat actors can use this backdoor to have full control over the network.
However, this is very controversial, and that’s why the exact name of the federal government commission has not been disclosed. Apart from this, Avast remarked that they are trying their best to identify the kind of attacks and consequently inform the agency’s findings.
Files Detected
The primary files that the security analysts detect are:-
- Downloader
- Decryptor
Downloader
It is the very first file that the experts have detected; this file was disguised as oci.dll (“C:\Windows\System32\oci.dll”) (Oracle Call Interface).
Here, the files contained a compressed library dubbed as NTlib by the analysts. This file is specifically used by the threat actors to check the MD5 of the hostname and later stop if it doesn’t match the one they stored.
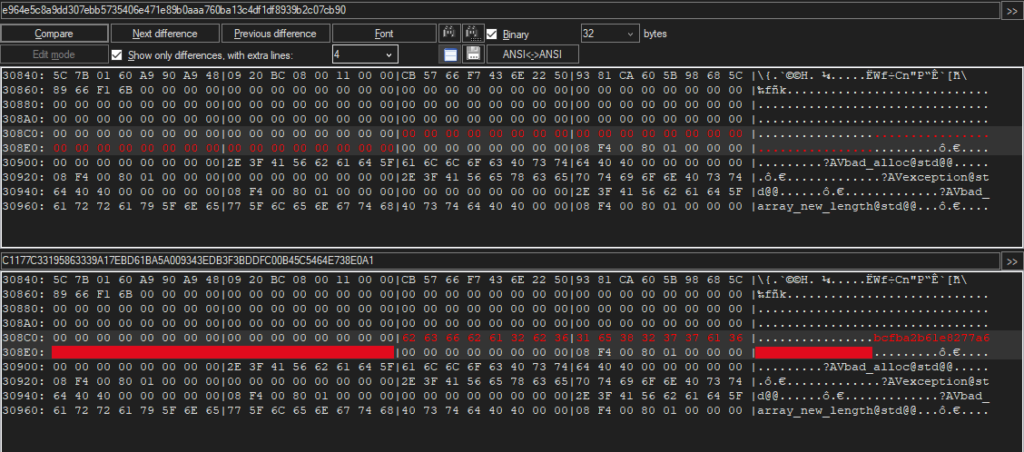
Decryptor
It was the second file detected by the experts, and this file was also disguised as oci.dll, and this file replaced the first file that is used in the next stage of the attack.
While here, in these circumstances, the main function of this file is to decrypt and run in memory the file “SecurityHealthServer.dll.”
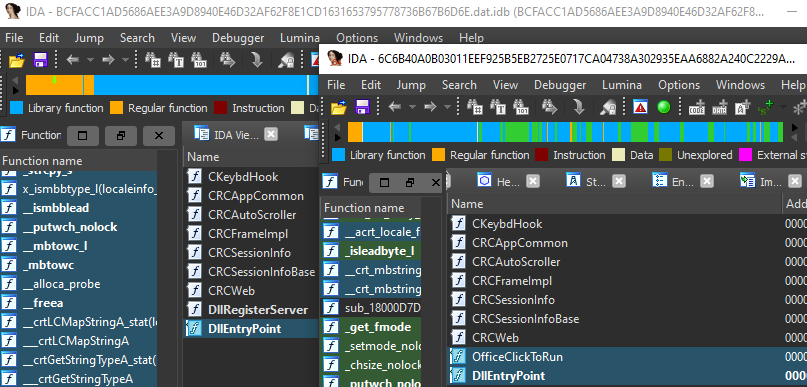
Evading Firewalls and Network Monitoring
After analyzing the backdoor, the security researchers concluded that it generally works by replacing a normal Windows file called “oci.dll” with two malicious ones.
This file enables the threat actors to download and execute malicious code on the targeted system. However, it is being assumed that the main motive of the attack is to bypass firewalls and network monitoring tools and solutions.
That’s why we conveyed that the earlier file is quite similar to the rcview40u.dll; it is likely that the threat actor had access to the source code of the three-year-old rcview40u.dll.
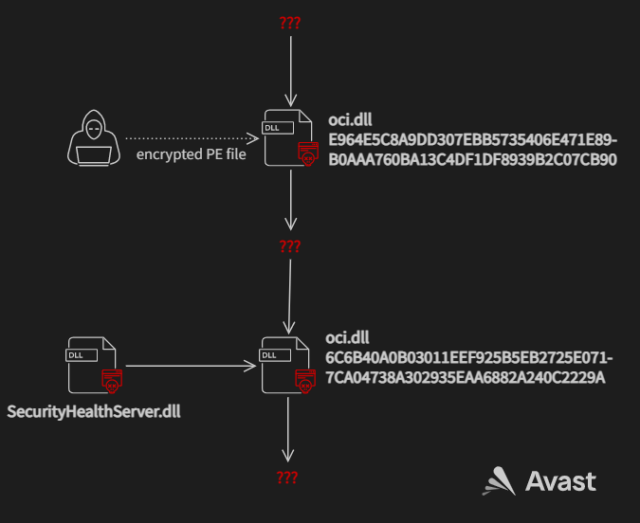
However, this backdoor attack was carried in two-stage, and its main justification was to deploy two malicious binaries that allowed the unidentified adversary to intercept internet traffic.
Not only that even it is also used to execute code of their choice and later allows the operators to take entire control over the infected systems that they attacked.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.





