

Software cracks and keygen sites are used as bait to distribute the latest version of the Amadey Bot malware with the help of SmokeLoader malware.
The malware strain called Amadey was found over four years ago, and is capable of performing the following tasks:-
- System reconnaissance
- Stealing information
- Loading additional payloads
Since 2020, there has been a steady decline in the prevalence of this malware. A new version of the virus has, however, been reported by the Korean researchers at AhnLab.
SmokeLoader malware is also working in conjunction with this new version of the virus, which is also very old, but, still very active. Amadey’s shift away from Fallout and Rig exploit kits represents a significant departure from its previous strategy.
Amadey’s new campaign
It is known that SmokeLoader makes use of software cracks or keygens to disguise itself, stimulating the victims to download and install the software voluntarily.
When cracks and key generators are used, antivirus warnings are activated, making the user have to disable their antivirus program. The ease with which malware can be distributed, and makes them an ideal means for doing so.
It works by injecting its “Main Bot” into the process (explorer.exe) that is currently running on the system so that it becomes trusted by the OS and can download Amadey when it is executed.
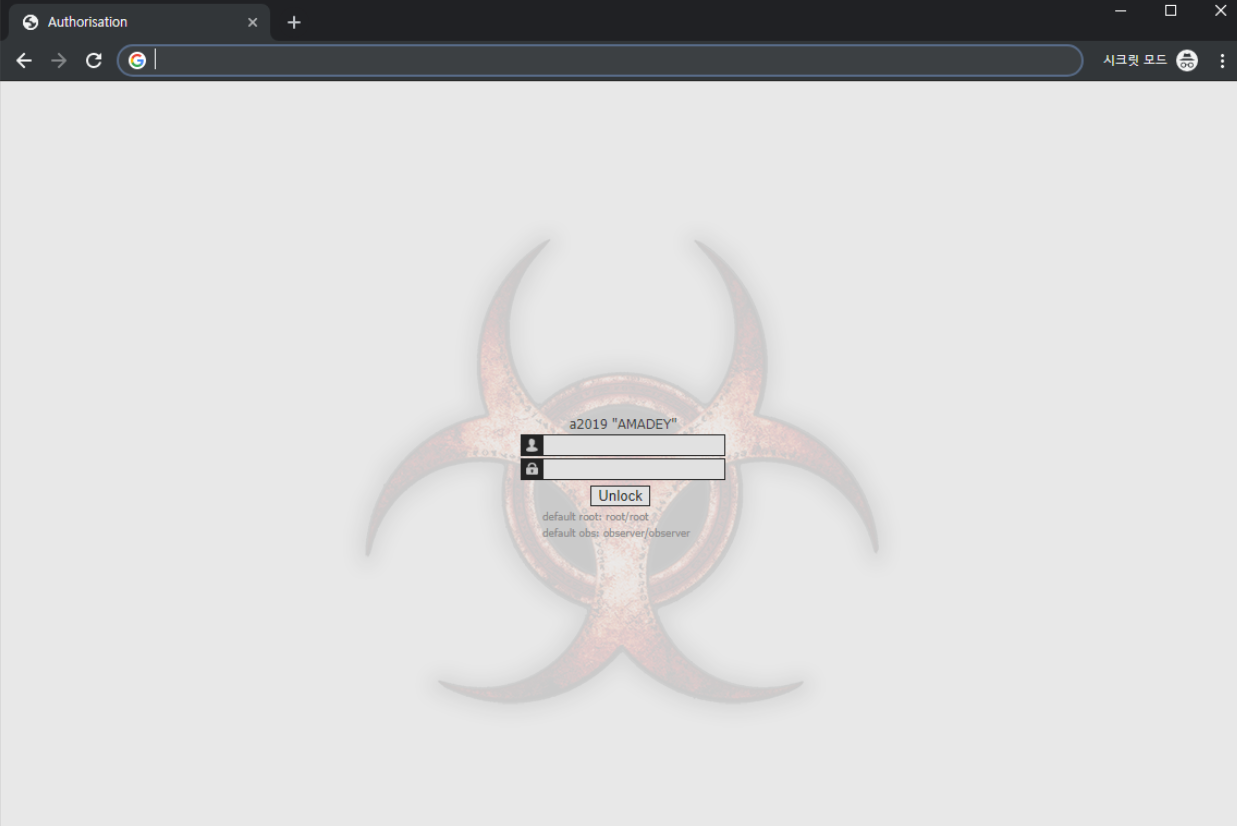
The Amadey program automatically copies itself to the TEMP folder under the name “bguuwe.exe” once it has been downloaded and executed. With the help of the cmd.exe command, this creates a scheduled task that is responsible for maintaining persistence.
In the context of C2 communication, Amadey establishes contact with the threat actor’s server and sends a profile of the system to it.
While the system profile includes the following information:-
- OS version
- Architecture type
- Installed apps list
- List of installed AV tools
To respond, the server delivers instructions to download further plugins, as well as info-stealer malware like RedLine, which is designed to steal personal information from the victims.
With the aid of the ‘FXSUNATD.exe’ tool, Amadey is able to bypass UAC or perform DLL hijacking in an effort to install payloads with elevated privileges.
It has been found that the latest version of Amadey, version 3.21, is capable of discovering 14 different antivirus products.
Targeted & abused Emails, FTPs, VPN clients
Malware can access email accounts, FTP servers, and VPN clients, as well as a variety of other types of information. Several different software applications can be targeted with the info-stealing plug-in, including:-
- Mikrotik Router Management Program Winbox
- Outlook
- FileZilla
- Pidgin
- Total Commander FTP Client
- RealVNC, TightVNC, TigerVNC
- WinSCP
Keep the following things in mind in order to avoid the dangers of Amadey Bot and RedLine:-
- Make sure you don’t download cracked files.
- Activators for software products should not be downloaded.
- Downloading illegitimate key generators should be avoided.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







