

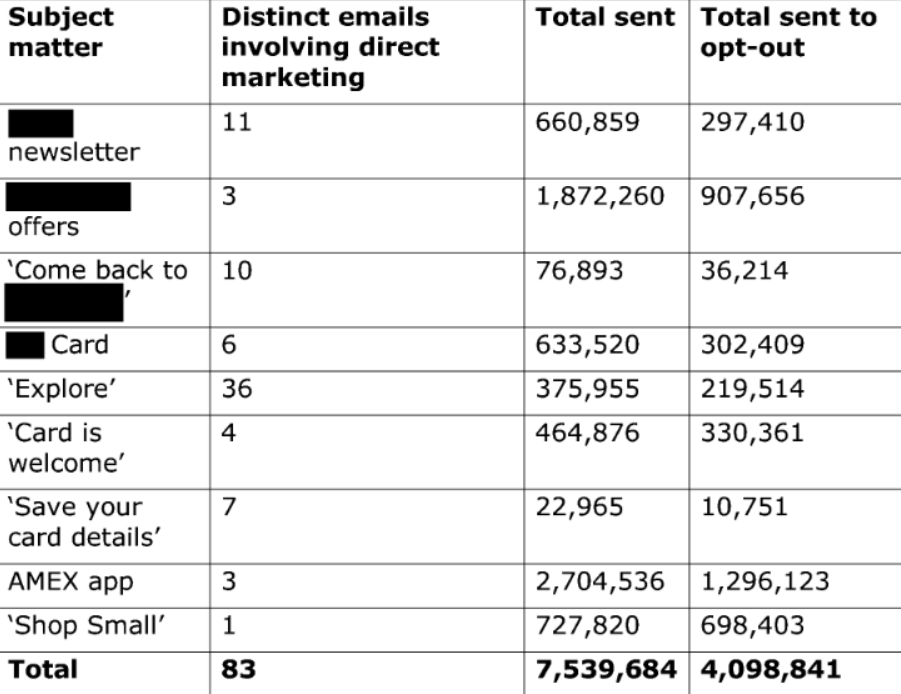
The American Express (Amex) was recently fined £90,000 by the British data regulator for sending more than 4 million spam emails containing marketing campaigns within a year to its customers.
The UK Information Commissioner’s Office (ICO) investigated the whole matter and found that American Express (Amex) had broken the law by firing these spam emails containing marketing campaigns to a total of about 50 million of its customers.
And not only that even they have classed all these spammy emails as servicing emails. The chief investigator of ICO, Andy Curry asserted that “This is a clear example of a company that went wrong and now faces the consequences.”
The spammy emails that were sent by Amex to all its customers between 1st June 2018 and 21st May 2019, which is about 12 months, are specially designed by Amex to encourage all its customers to make purchases via their cards, and in turn, they could gain financial benefits.
This £90,000 fine was effectively a small charge for the American Express (Amex), as according to the balance sheet the bank has made $1.4 billion only in the last quarter of 2020. While in the case of Q1 FY2021 American Express proclaimed a net income of $2.2 billion.
Moreover, during the investigation, the ICO discovered that the customers who were getting these spammy emails have deliberately opted out from them.
But, to defend the reputed image of the company, Amex denied these complaints and claimed that all these emails are mot marketing emails, as they classed these emails as servicing emails.
As a result, the company straightly rejected the proposal of ICO to re-evaluate its marketing strategies, and they defined these emails to ICO as communication of advertising or essential requirements of Credit Agreements with customers.
However, ICO defined that without the free consent of its customers Amex has broke Regulation 22 of the Privacy and Electronic Communications Regulations 2003 (PECR) by sending these spam or marketing emails.
ICO also offered a 20% discount (the reduced amount will be £72,000) on the total fine amount of £90,000 to Amex, if they will pay the fine in advance, while the normal payment date is set by ICO is June 17.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







