
According to researchers at cybersecurity firm Kaspersky, threat actors are abusing Amazon Simple Email Service (SES) to deliver highly convincing phishing emails that bypass traditional security controls, marking a common occurrence in email-based threats
The primary goal of any phishing campaign is to evade detection while tricking victims into revealing sensitive data.
To achieve this, threat actors continuously refine their techniques, using redirect links, QR codes, and more recently trusted cloud infrastructure.
Securelist researchers state there is a “steady trend” of phishing campaigns against Amazon SES, a legitimate cloud-based email delivery service widely used for transactional and marketing communications.
Amazon SES integrates seamlessly with AWS and is designed for reliable, high-volume email delivery. However, its legitimacy is precisely what makes it attractive to attackers.
Unlike traditional phishing campaigns that rely on suspicious domains, SES-based attacks originate from infrastructure that both users and security systems inherently trust.
Emails sent via Amazon SES pass standard authentication checks, including SPF, DKIM, and DMARC. They also often include “amazonses.com” in the Message-ID header, reinforcing their legitimacy.
As a result, these phishing emails appear technically authentic and are rarely flagged by email security solutions.
Researchers state that in early 2026, one of the most common themes in phishing emails sent with Amazon SES was fake notifications from electronic signature services such as DocuSign.
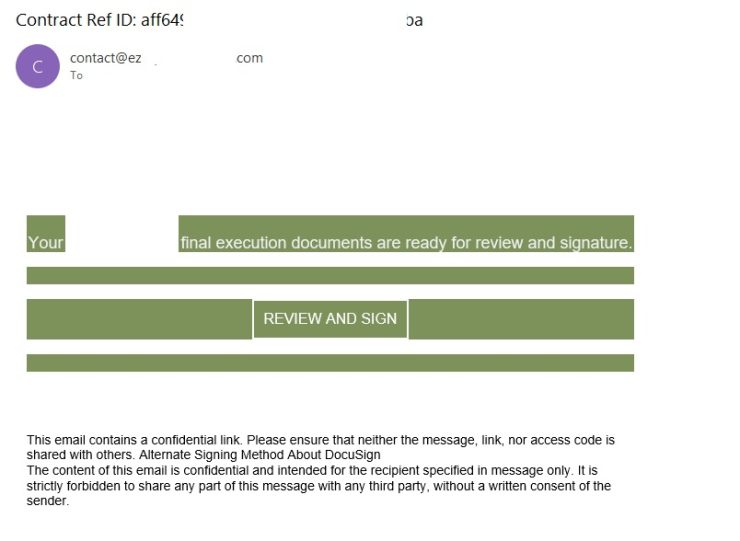
Attackers further enhance credibility by embedding links that appear to point to trusted domains such as “amazonaws.com.”
In reality, these links redirect users to malicious phishing pages. Combined with custom HTML templates, attackers can replicate legitimate brand communications with high accuracy.
How Attackers Gain Access
In most cases, attackers gain control of Amazon SES accounts through exposed AWS IAM (Identity and Access Management) credentials.
Access keys are frequently leaked in public repositories, environment files, Docker images, or misconfigured S3 buckets.
Threat actors actively scan for such exposures using automated tools like TruffleHog, which detects leaked secrets. Once valid credentials are identified, attackers verify permissions and email-sending quotas before launching large-scale phishing campaigns.
In early 2026, researchers observed widespread phishing campaigns impersonating electronic signature services such as DocuSign.
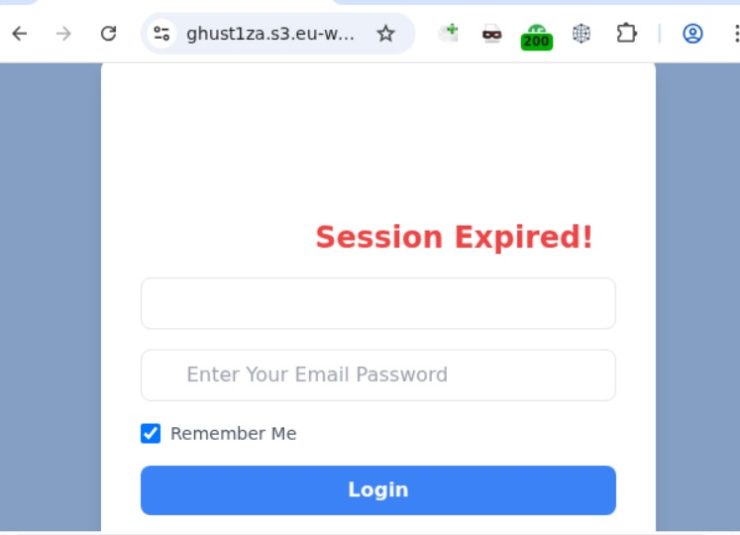
Victims received emails prompting them to review and sign documents. While the email headers confirmed delivery via Amazon SES, the embedded links redirected users to fake login pages hosted on AWS infrastructure.
Because the hosting domain appeared legitimate, many users trusted the process and entered their credentials, unknowingly handing them over to attackers.
Beyond standard phishing, Amazon SES is also being used in sophisticated Business Email Compromise (BEC) attacks.
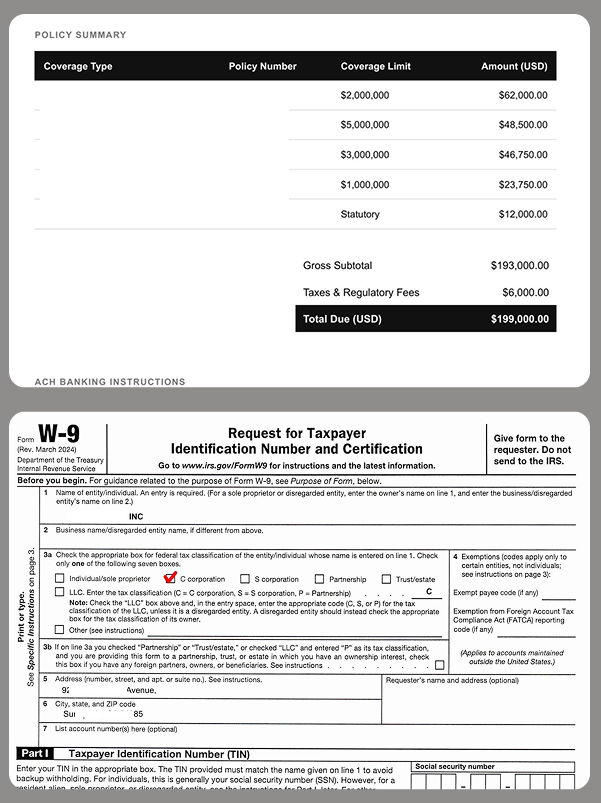
In one case, attackers sent emails that appeared to be part of an internal conversation between an employee and a vendor regarding an overdue invoice. The email included forged message threads and attached PDF documents containing payment details.
These emails contained no malicious links, making them harder to detect. Instead, they relied on social engineering to convince finance teams to transfer funds to attacker-controlled accounts.
Mitigations
The PDF attachments didn’t contain any malicious phishing URLs or QR codes, only payment details and supporting documentation.
“AWS has clear terms that prohibit the use of our services to violate the security, integrity, or availability of others. When we receive reports of potential violations of our terms, we act quickly to review and take appropriate action. As always, we encourage all customers to follow recommended security guidance to help secure their accounts and prevent abuse. If anyone suspects that AWS resources are being used for abusive activity, they can report it to AWS Trust & Safety https://repost.aws/knowledge-center/report-aws-abuse. – AWS Spokesperson
Unexpected requests, especially those involving documents or payments, should be verified through separate communication channels. Carefully inspecting links before clicking can help prevent credential theft.
As attackers continue to exploit trusted platforms like Amazon SES, both organizations and individuals must adapt their defenses to address this evolving threat landscape.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 to deliver highly convincing phishing emails that bypass traditional security controls.)