

A sophisticated supply chain attack hit the SAP developer ecosystem on April 29, 2026, compromising four widely-used npm packages with credential-stealing malware.
The attackers modified package installation scripts to download the Bun JavaScript runtime a legitimate alternative to Node.js during the npm install process.
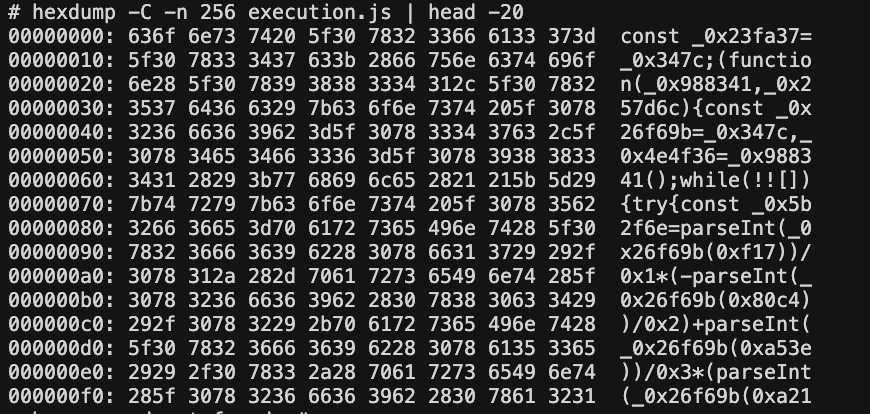
This technique bypasses Node.js-based security monitoring by executing an 11.6 MB heavily obfuscated payload through Bun instead.
The malicious code activates through a preinstall hook, meaning it executes automatically before the package finishes installing, requiring no user interaction beyond running npm install.
The campaign, dubbed “Mini Shai-Hulud,” targeted packages essential to SAP Cloud Application Programming Model (CAP) and Cloud MTA build workflows, affecting developer workstations and CI/CD pipelines across enterprise environments.
The malware harvests credentials across five primary targets: GitHub tokens and Personal Access Tokens, npm authentication tokens, AWS, Azure, and Google Cloud credentials, Kubernetes service account tokens, and configuration files for AI coding tools, including Claude and Visual Studio Code.
Stolen data is encrypted using AES-256-GCM and exfiltrated to public GitHub repositories created under victims’ own accounts with the description “A Mini Shai-Hulud has Appeared”.
Self-Propagation Capability
The payload contains worm-like functionality that validates stolen npm tokens to confirm publishing permissions, then automatically injects malicious code into other packages the compromised account controls.
It also creates malicious GitHub Actions workflows in accessible repositories to extract repository-level secrets on subsequent CI runs.
This self-replicating mechanism mirrors techniques from the original Shai-Hulud campaign that compromised the Bitwarden CLI package in April 2026.
PackageMalicious VersionLast Clean VersionMonthly Downloads
| Package | Malicious Version | Last Clean Version | Monthly Downloads |
|---|---|---|---|
| mbt | 1.2.48 | 1.2.47 | Up to 1M |
| @cap-js/sqlite | 2.2.2 | 2.2.1 | Hundreds of thousands |
| @cap-js/postgres | 2.2.2 | 2.2.1 | Hundreds of thousands |
| @cap-js/db-service | 2.10.1 | 2.10.0 | Hundreds of thousands |
The compromise occurred through two separate methods. The mbt package was hijacked using a stolen static npm authentication token belonging to the cloudmtabot service account, allowing direct malicious publishing without GitHub access.
The three @cap-js packages were compromised through a combination of a hijacked SAP developer GitHub account and a misconfigured npm OIDC trusted publishing setup that granted publishing permissions to any workflow on any branch, rather than restricting trust to specific workflows on the main branch.
Beyond immediate credential theft, the malware injects persistence hooks into Visual Studio Code and Claude Code AI assistant configurations.
Connection to Shai-Hulud
Security researchers confirmed this attack shares identical infrastructure with the Bitwarden CLI supply chain attack from April 2026, including the same Bun runtime version (v1.3.13), encryption cipher (ctf-scramble-v2), and PBKDF2 cryptographic key.
Both campaigns feature Russian locale kill-switches that prevent execution on systems configured for Russian language, a common operational security marker in Eastern European threat actor campaigns. The attack toolchain is attributed to the cybercrime group TeamPCP.
SAP published Security Note 3747787 addressing the incident and released clean superseding versions for all affected packages.
Organizations should immediately uninstall compromised versions using npm uninstall with the –ignore-scripts flag, then reinstall the last clean versions.
All GitHub tokens, npm tokens, cloud credentials, and API keys on any system that installed a malicious version should be rotated immediately, as the encryption used by the attackers makes stolen credentials unrecoverable.
Indicators of Compromise (IoCs)
| File | SHA-256 | Packages |
|---|---|---|
| setup.mjs | 4066781fa830224c8bbcc3aa005a396657f9c8f9016f9a64ad44a9d7f5f45e34 | All four |
| execution.js | 80a3d2877813968ef847ae73b5eeeb70b9435254e74d7f07d8cf4057f0a710ac | [email protected] |
| execution.js | 6f933d00b7d05678eb43c90963a80b8947c4ae6830182f89df31da9f568fea95 | @cap-js/[email protected] |
| execution.js | eb6eb4154b03ec73218727dc643d26f4e14dfda2438112926bb5daf37ae8bcdb | @cap-js/[email protected], @cap-js/[email protected] |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


