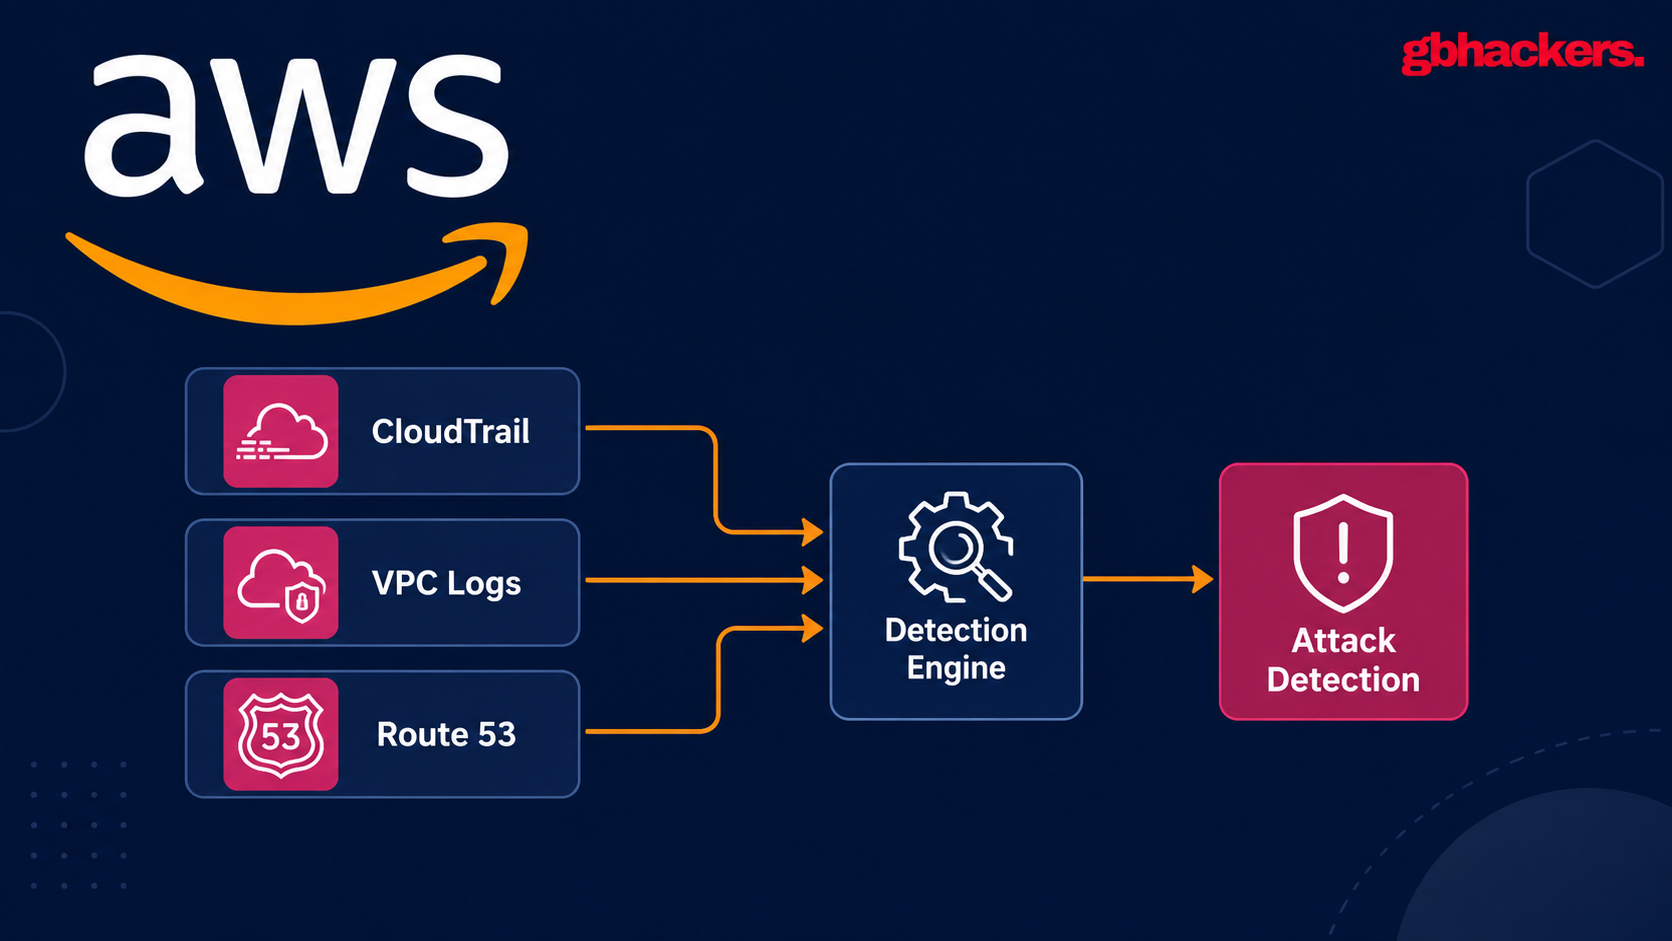

AWS security teams can improve detection of multi-stage intrusions by correlating API activity in CloudTrail with network metadata in VPC Flow Logs and DNS activity in Route 53 Resolver query logs.
The approach turns isolated alerts into an attack narrative spanning credential abuse, reconnaissance, privilege escalation, lateral movement and data exfiltration.
A suspicious GetCallerIdentity request from an unfamiliar address may be low priority by itself.
But risk changes quickly when the same identity starts issuing List and Describe calls across AWS services, generates AccessDenied failures, accesses a sensitive S3 bucket and is followed by high-volume outbound traffic to infrastructure associated with a newly registered domain.
Correlating those events within an appropriate time window gives analysts evidence of intent and progression rather than a queue of disconnected findings.
CloudTrail provides the identity and control-plane layer. It records actions such as AssumeRole, CreateAccessKey, PutRolePolicy, AuthorizeSecurityGroupIngress, and S3 GetObject requests when S3 data events are enabled.
The latter requirement is important: management-event logging alone does not capture object-level reads that may signal bulk collection from sensitive buckets.
Analysts can use them to validate whether the workload associated with a suspicious IAM principal transferred unusually large volumes of data to public IP addresses shortly after sensitive activity.
Route 53 Resolver query logs provide DNS context from VPCs, including queries and associated source addresses.
They can be delivered to CloudWatch Logs, Amazon S3, or Firehose, enabling teams to identify a workload resolving suspicious destinations before or during outbound communication.
Resolver logging records unique queries rather than every cached DNS lookup, an operational limitation teams should account for in correlation logic.
AWS Researchers said that, VPC Flow Logs add the network layer, recording accepted or rejected flows, source and destination addresses, ports, and byte counts.
AWS Threat Hunting
AWS recommends this “logging trifecta” for cloud investigations, but telemetry only becomes a high-fidelity detection layer when teams overlay local context.
For example, a legitimate analytics role may regularly read a reporting bucket, while the same role accessing a customer-records bucket should be exceptional.
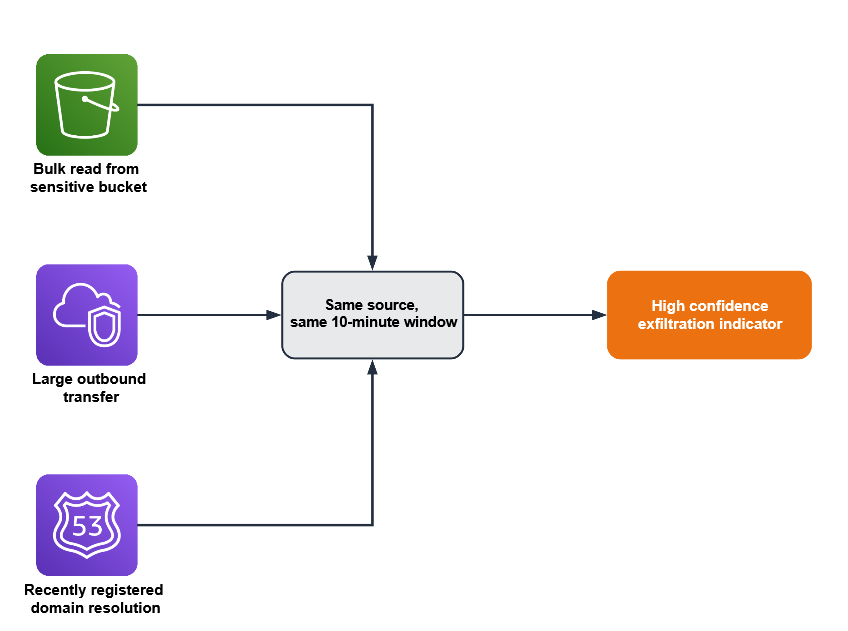
A useful rule can therefore identify high-volume GetObject operations against a sensitive bucket, exclude approved principals, then seek corroboration from VPC egress and DNS activity in the same 10-minute period.
Security teams can alert when a user performs multiple AssumeRole operations from one source and then changes IAM policy.
When an unexpected role calls Decrypt on a workload-specific customer-managed KMS key; or when a human identity makes privileged security-group or access-key changes outside an approved deployment window.
Amazon GuardDuty already detects many generalized cross-service attack patterns.
Extended Threat Detection capability is enabled by default when GuardDuty is enabled in an AWS Region and correlates signals across foundational data sources and activated protection plans to produce attack-sequence findings.
AWS says these can identify chains such as credential compromise followed by exfiltration as a single critical-severity finding.
Current GuardDuty attack-sequence coverage can include CloudTrail management and S3 data events, VPC Flow Logs, Route 53 Resolver DNS logs, EKS audit data and runtime-monitoring signals, depending on enabled services and workloads.
That does not remove the value of custom detections. GuardDuty recognizes patterns that are suspicious across customer environments, while internal controls determine whether a particular identity should access a bucket, use a key, traverse a role chain, or modify production after hours.
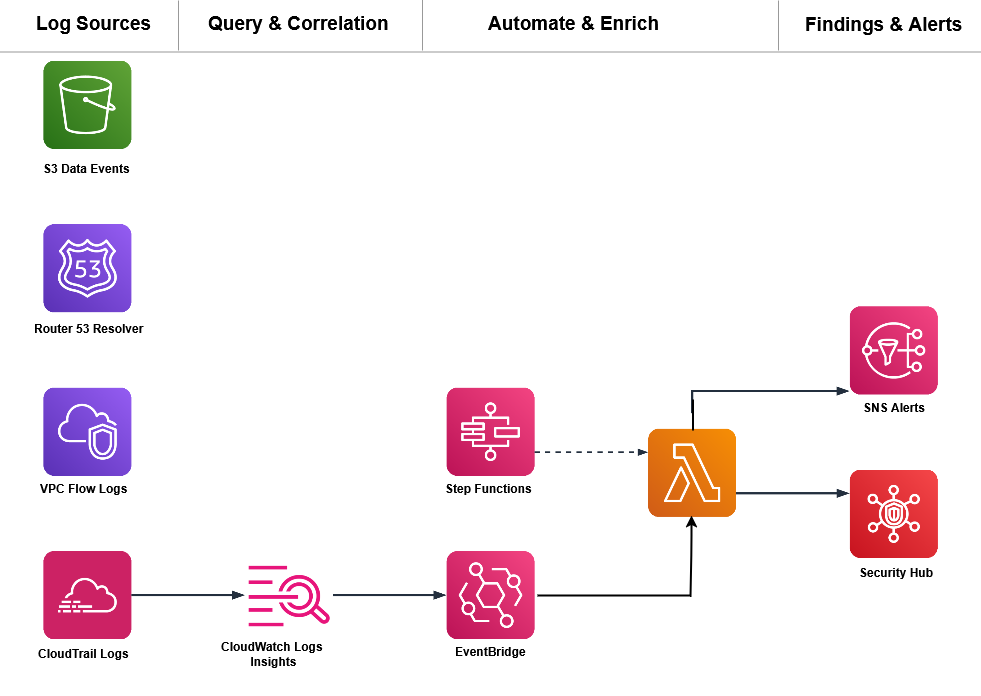
Teams should centralize telemetry in CloudWatch Logs Insights for rapid querying, or use Amazon Security Lake and Athena for longer retention and broader analytics.
AWS’s recommended prerequisites include a CloudTrail trail delivered to CloudWatch, S3 data-event logging for monitored buckets, VPC Flow Logs for production networks, Route 53 Resolver query logging, and GuardDuty with relevant protections enabled.
Thresholds should be baselined rather than guessed. AWS suggests measuring a week of normal access activity and setting an alert threshold above the 95th-percentile read count for the protected bucket.
Correlation windows should use event timestamps, not query time, because CloudTrail delivery latency can delay visibility.
The result is a detection model that connects identity, resource sensitivity, network egress and DNS behavior making a valid API call look like what it may actually be: one stage in an active cloud attack.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide


