

Threat actors are increasingly targeting Azure Blob Storage, Microsoft’s flagship object storage solution, to infiltrate organizational repositories and disrupt critical workloads.
With its capacity to handle exabytes of unstructured data for AI, high performance computing, analytics, media streaming, enterprise backup, and IoT ingestion, Blob Storage has become an attractive vector for sophisticated campaigns aiming to steal, corrupt, or ransom data at scale.
In recent months, security researchers have documented a surge in attacks that exploit misconfigurations, leaked credentials, and weak access controls to breach Blob Storage accounts.
Publicly exposed containers are routinely enumerated using DNS and HTTP header probing, brute-forced subdomain permutations, and dedicated indexers cataloging exposed endpoints.
Once valid storage account names or container URLs are discovered, adversaries scour code repositories, configuration files, and version histories for storage account keys, shared access signatures (SAS) tokens, or service principal credentials.
These credentials often grant full read, write, and delete permissions, enabling threat actors to establish initial footholds and escalate privileges within cloud environments.
Beyond theft of data, attackers leverage Blob Storage to host malicious payloads and spoofed login pages.
Threat groups have been observed injecting macro-enabled documents, executables, or poisoned machine learning datasets into containers left open to anonymous access or secured with overly permissive SAS tokens.
Victims downloading these resources risk executing malware that can spread through Azure Functions, Logic Apps, or downstream data pipelines, triggering lateral movement across subscriptions and resource groups.
Attack Chain Stages Exploiting Blob Storage
Mapping the attack chain to Azure Blob Storage reveals several stages where defenders must apply targeted controls.
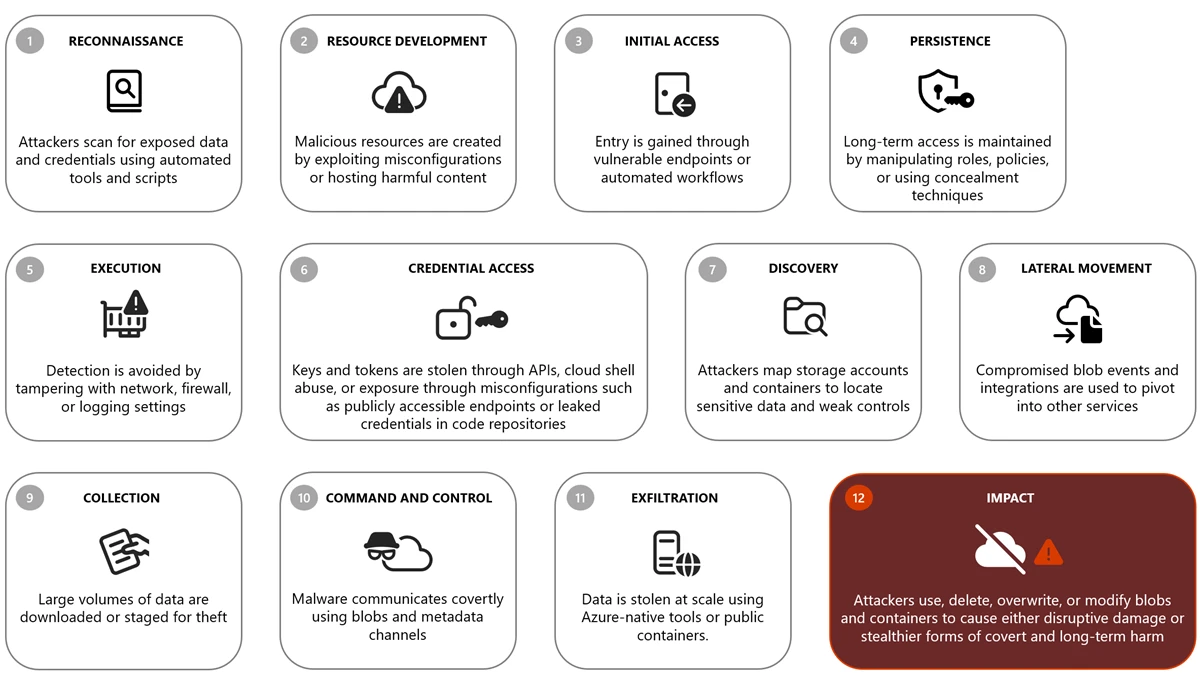
During reconnaissance, tools like Goblob and QuickAZ automate container enumeration, while AI-assisted language models generate plausible account and container names to improve brute-forcing success rates.
In the resource development phase, adversaries exploit misconfigured identity settings to create malicious objects, host phishing sites, or poison training data.
Initial access often occurs through blob-triggered workflows such as Azure Functions or Event Grid subscriptions. Threat actors crafting malicious files can hijack trusted automation, triggering unauthorized code execution under managed identities.
Persistence is maintained by creating broad SAS tokens with extended expiration, altering container policies for anonymous access, and leveraging Azure Hound or AADInternals to embed backdoors resilient to key rotations and password resets.
To evade defenses, attackers manipulate network rules, disable diagnostic logging, and distribute requests across multiple regions.
The collection and exfiltration phases exploit Azure’s high bandwidth and internal network. Attackers use AzCopy, Azure Storage Explorer, or REST API calls to transfer large volumes of sensitive data into staging containers under their control.
Static website hosting of the $web container provides a covert exfiltration path, while object replication policies can propagate malicious payloads to trusted destination accounts, enabling supply chain-style attacks. Clever use of blob metadata as a command-and-control channel further demonstrates the versatility of Blob Storage abuse.
Zero Trust and Continuous Monitoring
Recognizing these evolving threats, Microsoft’s Secure Future Initiative has embedded security-by-default features and continuously updates the MITRE ATT&CK threat matrix for cloud storage.
However, organizations must implement a robust security baseline to defend the data layer. Best practices include enforcing least-privilege access through Azure Entra role-based access control and attribute-based policies, restricting public exposure by disabling anonymous access at the container level, and applying zero trust principles to resource authentication.
Network protections such as private endpoints, virtual network rules, and mandatory TLS encryption safeguard data in transit, while service-side encryption and optional double encryption secure data at rest.
Immutability policies, soft delete, and versioning guard against unauthorized modifications and facilitate rapid recovery from deletion or corruption. Integrating Azure Storage with Microsoft Defender for Cloud and enabling the Defender for Storage plan delivers real-time threat intelligence, sensitive data discovery, and automated malware scanning.
Defender for Storage’s alerts detect anomalous access patterns, data exfiltration attempts, and malicious file uploads before they compromise downstream workloads.
By understanding the unique risks at the data storage layer and applying layered controls across identity, networking, data protection, and monitoring, organizations can mitigate the impact of Blob Storage attacks.
As adversaries continue to innovate, a proactive, zero trust-driven defense posture will remain essential to safeguarding critical repositories and maintaining business continuity.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





