Friday, September 11, 2026

BazarCall Attack Weaponizing Google Forms to Appear Legitimate

A new type of phishing attack known as BazarCall has emerged, and it’s using a clever technique to make it appear more legitimate.

The attack utilizes a Google Form to trick unsuspecting victims into divulging sensitive information.

The method of phishing that is being discussed here is one that poses a high level of risk as it can easily fool even those who are well-versed in technology and its intricacies.

In 2020, the BazarCall attack type gained notoriety for using a unique malware distribution method involving phone conversations with victims.

BazarCall/BazaCall attacks usually start with a phishing email that appears to be a payment notification or subscription confirmation from a well-known company. The email will contain the amount that is going to be charged, which is usually between $49.99 and $500 or more, depending on the subscription or service being impersonated.

It’s worth noting that these days, Google Forms are being utilized by certain individuals or groups to create an impression of authenticity or credibility.
BazarCall Attack Weaponizing Google Forms
BazarCall Attack

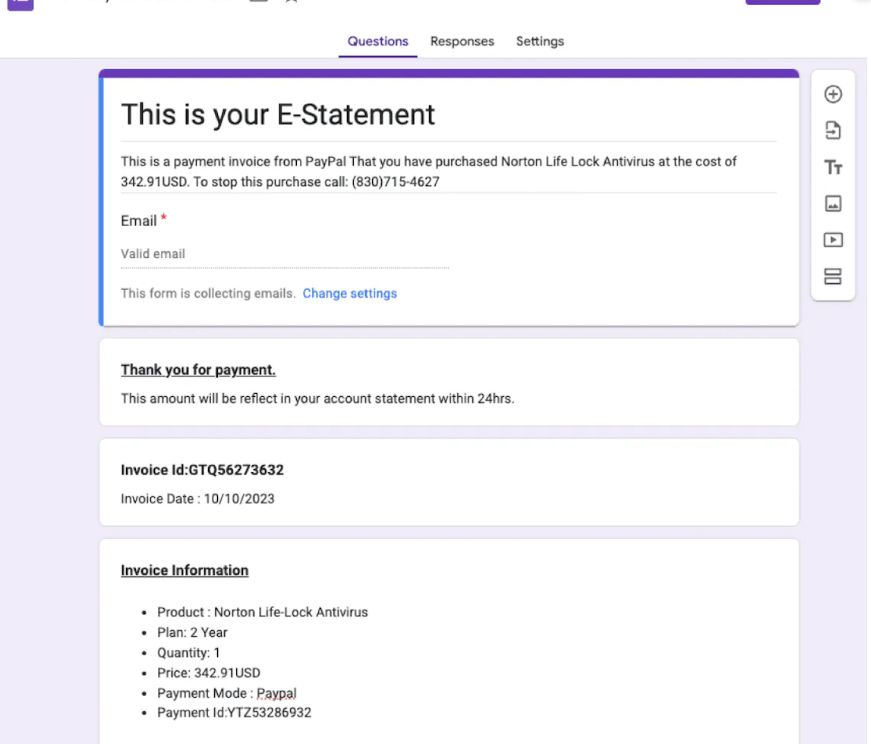
The attacker starts by creating a Google Form and filling it out with information regarding the fictitious transaction, such as the product or service that was allegedly purchased, the payment method, and the invoice number and date.

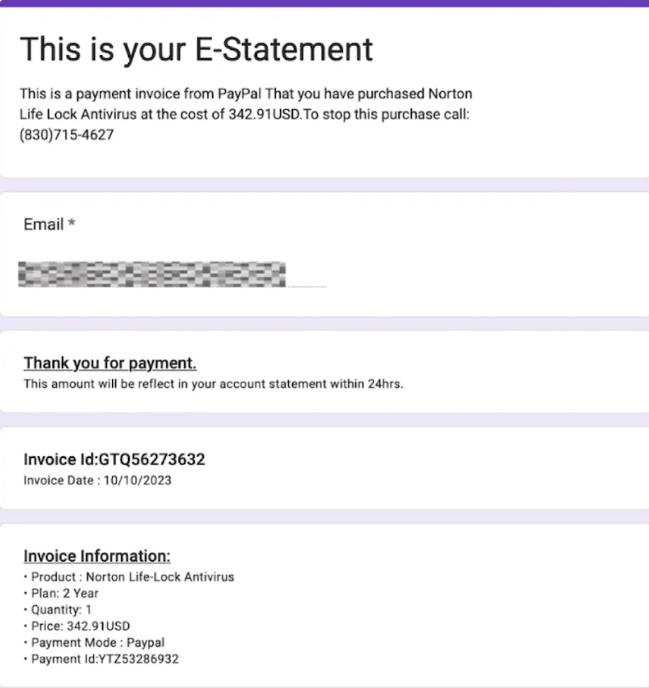
Secondly, to enable the response receipt option, the form sends a copy to a hacker’s forum. The hacker then sends an invitation to the victim to complete the form by themselves.

First, the attacker enters the target’s email address in the “Your email” area and then clicks on Submit. Upon submission, the victim will receive a copy of the completed form.

The attacker can trick the victim into believing that the form is a payment confirmation for Norton Antivirus software by activating the response receipt option.
BazarCall Attack Weaponizing Google Forms
The attacker’s mail

It is difficult for inaccurate email security solutions, such as secure email gateways, to reliably identify this email as a possible threat.

A popular and reliable tool for making surveys, quizzes, and forms is Google Forms. Because the emails used in BazarCall attacks come from a reliable source and could seem harmless, it can be difficult for SEGs to tell them apart from authentic ones.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

OpenMatter Network Realigns Leadership Team to Accelerate Global Commercial Growth

Melbourne, Florida, September 10th, 2026, CyberNewswire With its Verification Architecture...

Hackers Can Turn Vulnerable LiteLLM AI Gateways Into Root Access and Cloud Credential Theft

Nearly one in 10 internet-exposed LiteLLM AI gateways accepted...

Skullcandy Dime 3 Bluetooth Flaw Lets Nearby Attackers Hijack Audio and Microphone

Skullcandy Dime 3 wireless earbuds have a serious vulnerability...

Hackers Steal Active Directory Password Hashes Without Attacking Domain Controllers Directly

Threat actors are increasingly exploiting Active Directory replication mechanisms...

Fake GTA 6 Installer Steals Browser Passwords, Discord Tokens and Crypto Data From Gamers

Threat actors are exploiting anticipation around Grand Theft Auto...

Apple Xcode Integer Underflow Flaw Lets Crafted Archives Leak Memory and Crash Builds

A recently disclosed integer-underflow vulnerability in Apple’s modern Mach-O...

Palo Alto PAN-OS Buffer Overflow Lets Attackers Execute Arbitrary Code as Root

Palo Alto Networks has announced a high-severity buffer overflow...

New Phishing Attack Uses Blob URLs to Hide Malicious Pages From Security Scanners

A phishing campaign that moves the credential-harvesting page out...

Related Articles

Recent News