

Researchers from Cybereason Global Security Operations Center (SOC) Team, one of the world’s leading cybersecurity companies, have discovered a new Windows worm called Raspberry Robin.
Through removable USB devices, the malware spreads from one computer to another. A malicious DLL file is downloaded from a QNAP-associated domain using Windows Installer.
An alternative C2 infrastructure is provided by TOR exit nodes used by the malware. This is also known as the LNK Worm, primarily since it is associated with the Raspberry Robin campaign.
An old but still effective way of enticing people to fall victim to this kind of attack is to use “LNK” shortcut files.
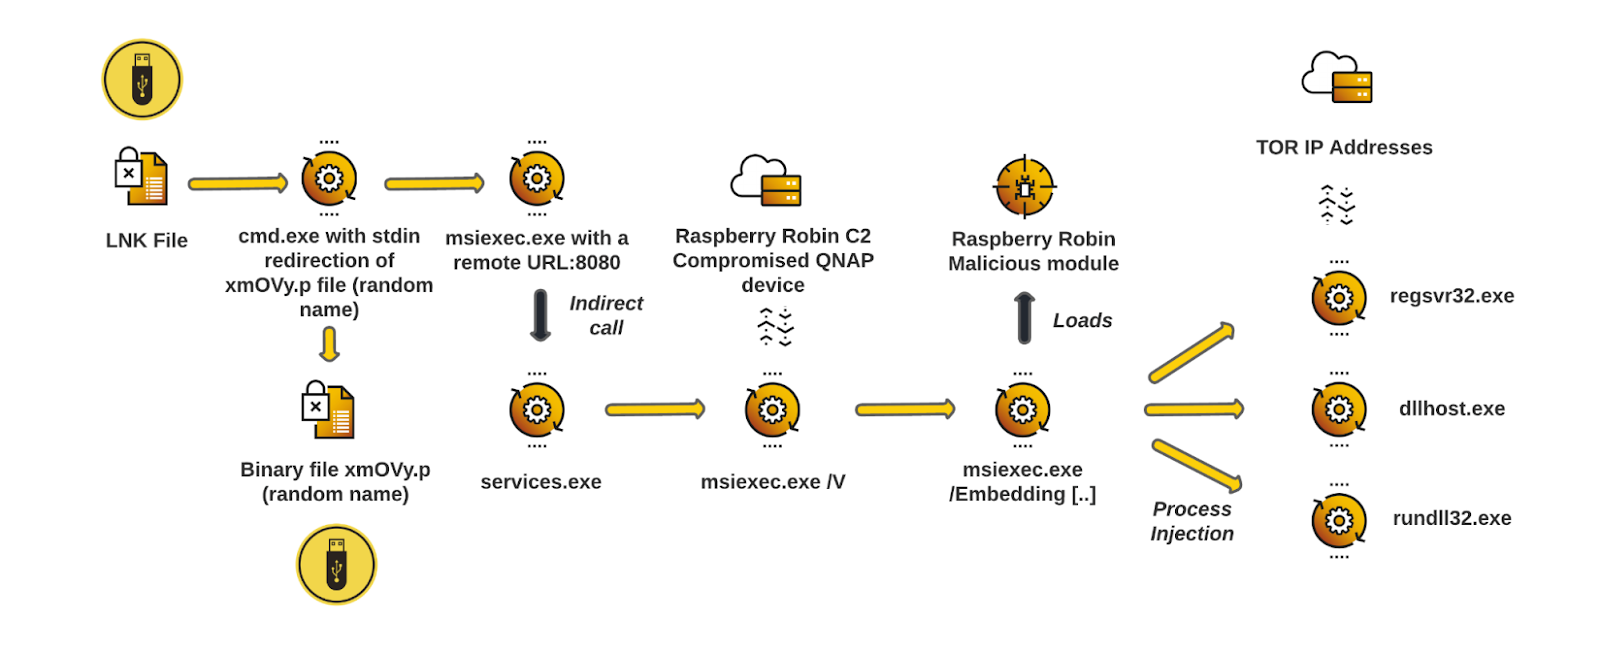
LNK Worm Infection Key Highlights
- In order to infect its victims, Raspberry Robin uses specially crafted Microsoft links (LNK files) that are specifically crafted for this virus.
- There was a delivery through a file archive, USB device, or ISO file that Cybereason observed.
- As a persistent threat, Raspberry Robin has been identified.
- Upon infection, the malware creates a persistent backdoor and runs as soon as the computer is restarted, in order to maintain its control.
- Most of the victims were found to be located in Europe, according to Cybereason.
- Raspberry Robin activities are detected and prevented by the Cybereason Defense Platform.
Raspberry Robin Infection
As a summary of a Raspberry Robin infection, the GSOC team has outlined the following:-
- There are two files that are the cause of the Raspberry Robin infection: A “LNK” file and a “BAT” file.
- By leveraging the LOLBin called “msiexec.exe” from a compromised NAS device from QNAP, Raspberry Robin downloads and executes a malicious shared library (DLL).

- Raspberry Robin does the following things to make it more difficult for people to detect it:
- Injects malicious code into three legitimate processes in the Windows operating system
- Tor Exit nodes (The Onion Router) are used by Raspberry Robin to communicate with the rest of the Raspberry Robin infrastructure
According to the report, A registry key in Raspberry Robin’s code allows it to automatically load a malicious module by using the malware binary “rundll32.exe” in the Windows operating system. This allows Raspberry Robin to persist on the infected system.

Moreover, this module is quite weird because there is a break in the chain of certification. This makes the Windows system unable to verify the module’s signature despite the fact that it has been signed.
In order to check for similar samples, you can use VirusTotal.com’s filter function to search for samples with the code signing name “OmniContact.”.
Recommendations
Here below we have mentioned all the recommendations offered by the security researchers at Cybereason:-
- In order to prevent Raspberry Robin from communicating with TOR exit nodes outside of the organization, it is recommended to block outgoing connections (inside the organization) to TOR-related addresses.
- It is imperative to re-image infected devices so they can no longer be infected by Raspberry Robin since it displays persistence mechanisms and creates a multitude of deceptive attacks on infected systems.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.




 Team, one of the world's leading cybersecurity companies.)