

Threat actors targeting macOS have increased lately as there were several cases of macOS information stealer malware found in the past, and many are being currently exploited in the wild.
According to reports, there was a new macOS malware found that is capable of taking over the complete macOS system without any permission required from the user end. This malware was found on a Russian hacking forum called “Exploit”.
HVNC (Hidden Virtual Network Computing)
Virtual Network Computer (VNC) is a technology that allows remote control over another system over a network which is clearly visible to the user on what kind of actions are being performed on the user’s computer from the controller end.
It has been useful for technical support on remote location systems.
However, HVNC varies only on a single element: the activities performed by the controller end are not visible to the user.
The remote sessions, the controlling activities, and the software being installed are completely unknown to the user.
[$100,000 – macOS Secure-WebSocket HVNC]
Recently an HVNC (Hidden Virtual Network Computing) tool was discovered, which requires a $100,000 deposit to acquire the tool.
As the publisher claims, the tool is capable of providing a reverse shell, remote file manager, sensitive data stealing, and persistence on the victim’s system.
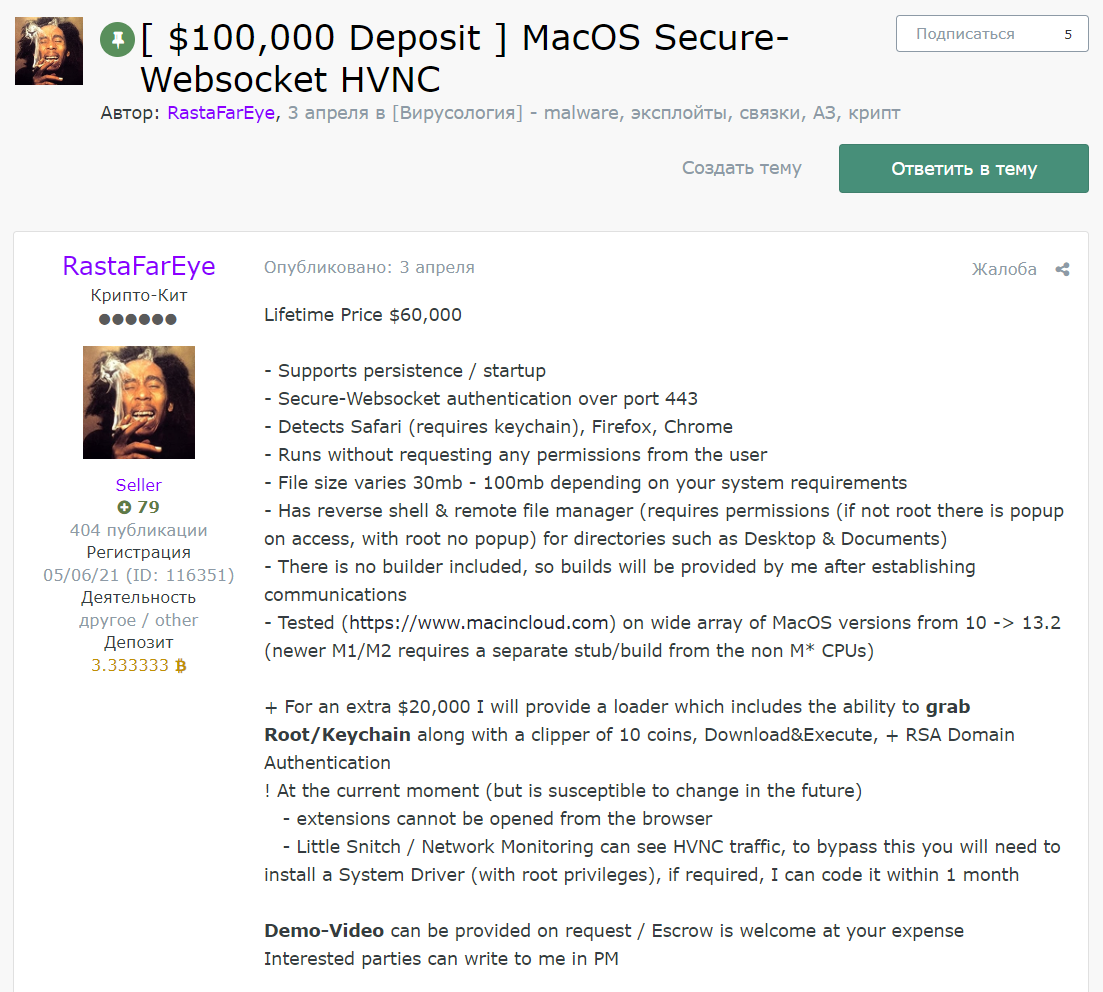
This tool has been available since April 2023 and was provided a technological update in July 2023.
The owner of this post, “RastaFarEye,” has been active since May 2021 and has a previous record of many HVNC variants for Windows, cryptocurrency targeting malicious software, and Extended validation certificate creation services.
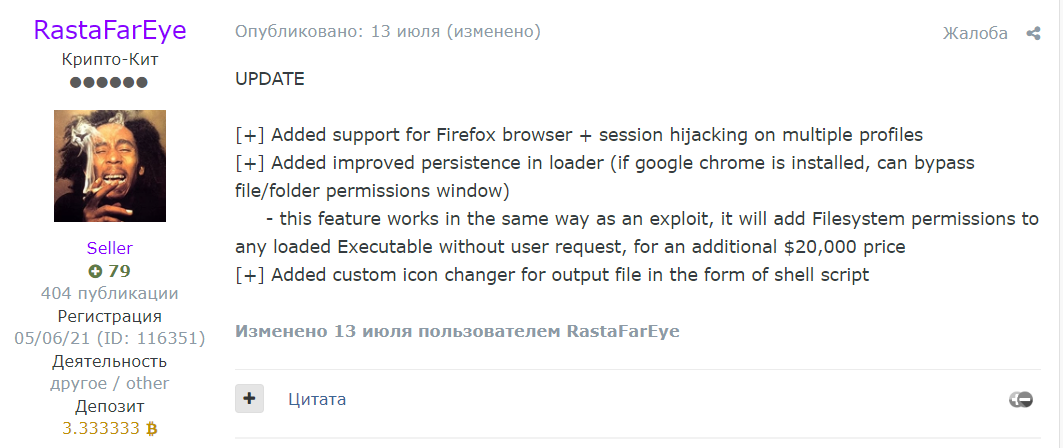
Escrow based Selling
The “$100,000 deposit” indicates the money kept in the escrow account of the forum administration, which acts as insurance for the buyers in case the sold product is not as described on the post. The higher the deposit money, the more legitimate the seller is.
There was another account under the name “Rodrigo” that posted that the threat actor has been working for more than 6 months on macOS information-stealing malware, reads the report shared by Guardz.
It seems like there have been several threat actors who were working to target macOS systems for malicious purposes.
It is recommended for Small Business Owners and Managed Service Providers to keep up-to-date information on the cyber security community for the latest versions of malware and protect themselves from getting exploited.
Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


