

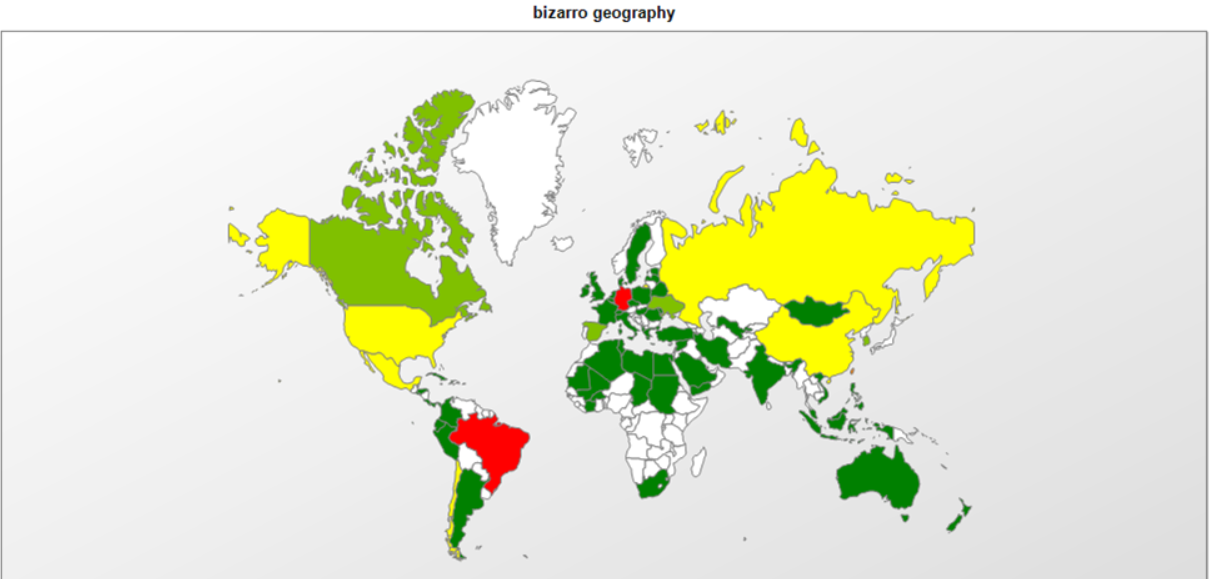
A new banking trojan has been discovered recently by the security experts at Kaspersky, and it has been dubbed as “Bizarro,” and this new trojan steals credentials from customers of 70 banks in Europe and South America.
Bizarro is a family of Trojans that is originating in Brazil, and it has already attacked banking entities in various countries around the world.
This new banking trojan uses tactics like social engineering to convince all its victims to hand over their banking credentials. Bizarro is distributed via MSI (Microsoft Installer) packages that the victim downloads from the links attached in spam emails.
According to the Kaspersky report, Once the victim launches the malicious links from the spam emails they received, Bizarro automatically downloads a ZIP file from a compromised website.
Working Method of Bizarro
To carry out its attacks Bizarro uses affiliates or hires mediators, either by collecting money or simply helping with interpretations.
Here, in return, the threat actors who are after this malware family use different techniques to complicate analysis and detection to trick their victims and gain access to their banking credentials.
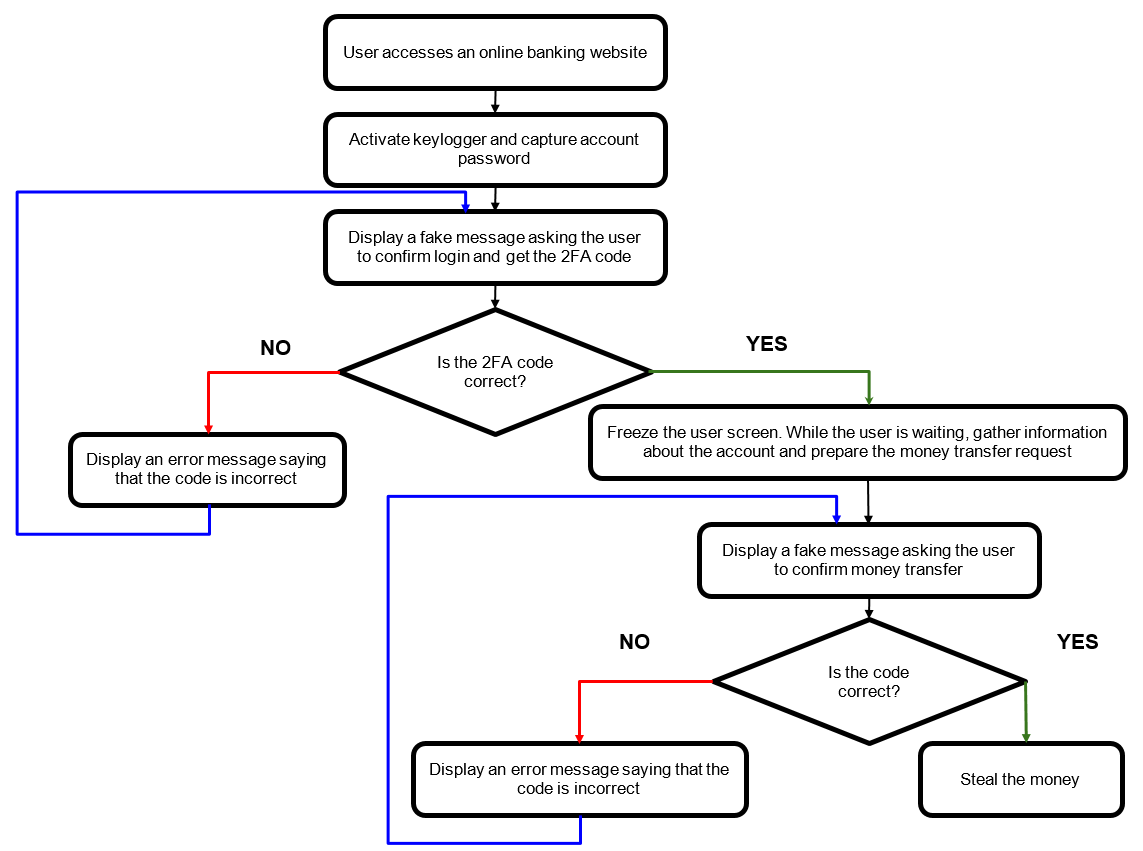
Bizarro displays different pop-up windows that imitate the real online banking processes, as in this it tricks the user. All these genuine-looking pop-up windows ask the users for their different data and then use them to carry out monetary or financial transactions.
The operators of this malware could launch 100 commands from a remote server to accumulate all the key data from targeted Windows systems.
Like this, the threat actors take access to the infected system and get the ability to control the victim’s mouse, keyboard, log keystrokes, capture screenshots, and even limit the functionality of Windows.
Moreover, to store the malware and collect telemetry data, Bizzaro also uses the servers that are hosted on Azure, Amazon (AWS), and even the hacked WordPress servers as well.
So, when these data sent to the telemetry server, Bizarro quickly starts its screen capture module. In short, the major role of Bizarro is to seize and exfiltrate all the banking credentials of their victims.
Abilities of Bizarro
- It has the ability to capture login credentials that are entered by their victims on their respective banking sites.
- It uniformly monitors the victims’ clipboard to find and replace any Bitcoin address with its own.
- It has the ability to produce fake prompts to solicit 2FA codes.
- It instantly gets fired up once the user visits one of a set of hardcoded banking sites.
Mitigation
To mitigate this banking trojan, the researchers have strongly recommended some mitigations, and here they are mentioned below:-
- The cybersecurity experts have strongly recommended the users not to click on any unknown links.
- They have recommended keeping an eye out for unexpected behavior on your system.
- Even they have also recommended to keep eye on the pop-up windows, especially while browsing any banking site.
- Always double check your destination bitcoin addresses before sending them any funds.
However, currently, the analysts have pronounced that there is no exact data is available that how many users were affected by this trojan; as no bank has made any information public regarding this matter.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







