

Security researchers uncovered a new vulnerability dubbed “BootHole” present in the GRUB2 bootloader utilized by Windows and Linux systems.
Attackers can exploit this vulnerability to install a stealthy malware that gives total control of the victim machine.
“The vulnerability affects systems using Secure Boot, even if they are not using GRUB2. Almost all signed versions of GRUB2 are vulnerable, meaning virtually every Linux distribution is affected,” Eclypisum said.
GRUB2 is the replacement of GRUB(Grand Unified Bootloader) Legacy boot loader, it functions to take over from BIOS at boot time, load itself, load the Linux kernel into memory, and then turn over execution to the kernel.
According to the detailed report shared with GBHackers On Security, the flaw affects a majority of laptops, desktops, servers, and workstations that are affected, as well as network appliances and other special-purpose equipment used in industrial, healthcare, financial, and other industries.
BootHole – Buffer Overflow Vulnerability
Researchers identified a buffer overflow vulnerability in the way that GRUB2 parses content from the GRUB2 config file(grub.cfg).

The config file also not signed, the vulnerability allows attackers to enable arbitrary code execution within GRUB2 and to gain control over the operating system.
It also allows an attacker to escalate privileges and persistence on the device, even with Secure Boot enabled.
The vulnerability can be tracked as CVE-2020-10713 and received a CVSS rating of 8.2. By exploiting the Boot Hole vulnerability attackers can install persistent and stealthy boot kits or malicious bootloaders that operate even when Secure Boot is enabled and functioning correctly.
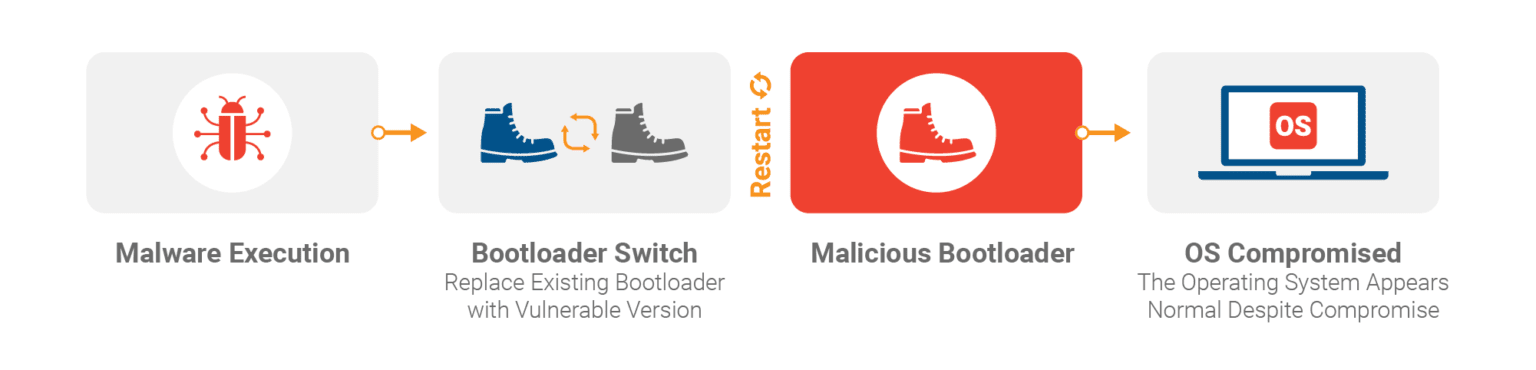
“In addition to Linux systems, any system that uses Secure Boot with the standard Microsoft UEFI CA is vulnerable to this issue.”
Researchers believe that majority of modern systems in use today, including servers and workstations, laptops and desktops, and a large number of Linux-based OT and IoT systems are affected by the vulnerability.
Mitigations
Researchers said that full mitigation of this issue will require coordinated efforts of Microsoft, open-source projects, and owners of affected systems.
“However, the full deployment of this revocation process will likely be very slow. UEFI-related updates have had a history of making devices unusable, and vendors will need to be very cautious,” researchers said.
Following are the list of advisories released by the vendors;
Researchers recommended monitoring the contents of the bootloader partition (EFI system partition) and to continue installing OS updates as usual across desktops, laptops, servers, and appliances.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.


