

Hackers are increasingly breaking into trucking and freight companies to quietly hijack real-world cargo shipments, turning digital access into physical theft at scale.
Researchers say organized crime rings are teaming up with cybercriminals to exploit the systems carriers and freight brokers use every day to book and dispatch loads.
Cargo theft is already a multi‑billion‑dollar problem, and the rapid digital transformation of trucking has created new entry points for cyber‑enabled theft.
Instead of following trucks on the highway, attackers now steal freight by compromising user accounts, manipulating broker platforms, and abusing remote access tools.
Proofpoint is tracking a cluster of activity where hackers infiltrate trucking carriers and freight brokers, then use that access to bid on legitimate freight loads, which are later stolen and resold, often online or overseas.
In reported cases, criminals have gone after commodities such as food, beverages, and electronics, which are easy to move and hard to trace once they leave the supply chain.
How the Attack Chain Works
In the campaigns analyzed by Proofpoint, the operation often starts with phishing or account takeover on broker “load boards” – online marketplaces where loads are posted, and carriers bid for them.
The attack chain in the observed campaigns leading to cargo theft attempts, which will be described in subsequent sections, is as follows: the threat actor will compromise a broker load board account.
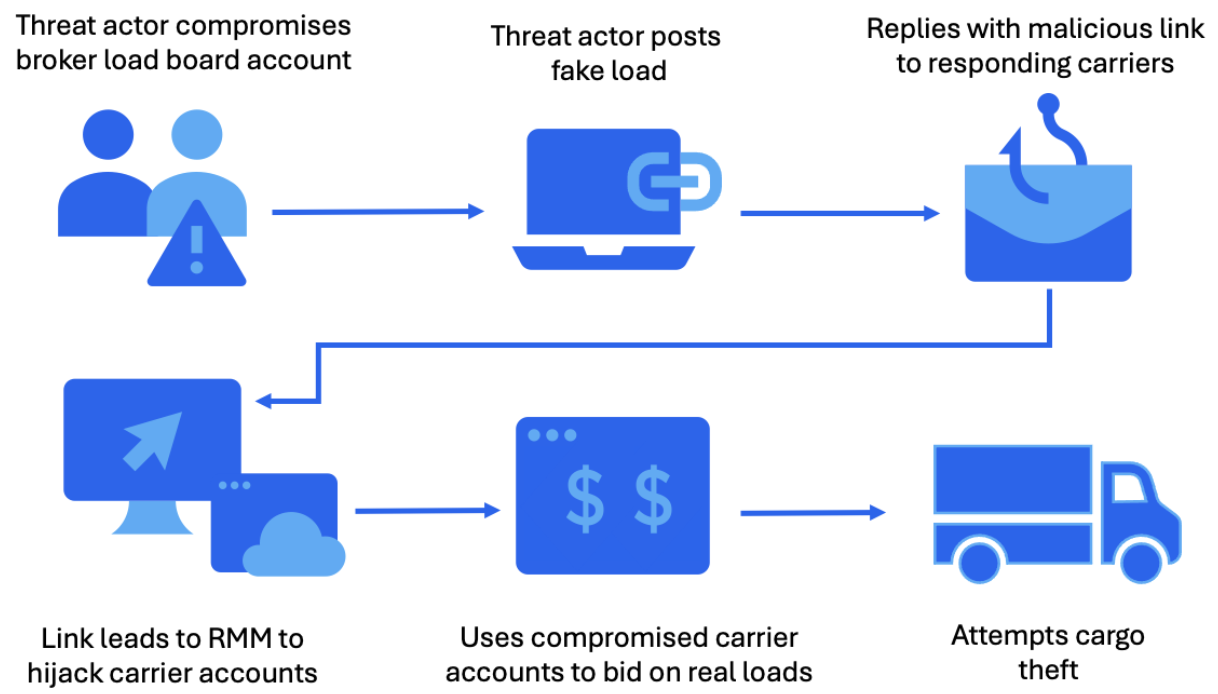
Attackers compromise a broker or carrier account, post fake or manipulated loads, and trigger the attack chain when a legitimate carrier responds to the offer.
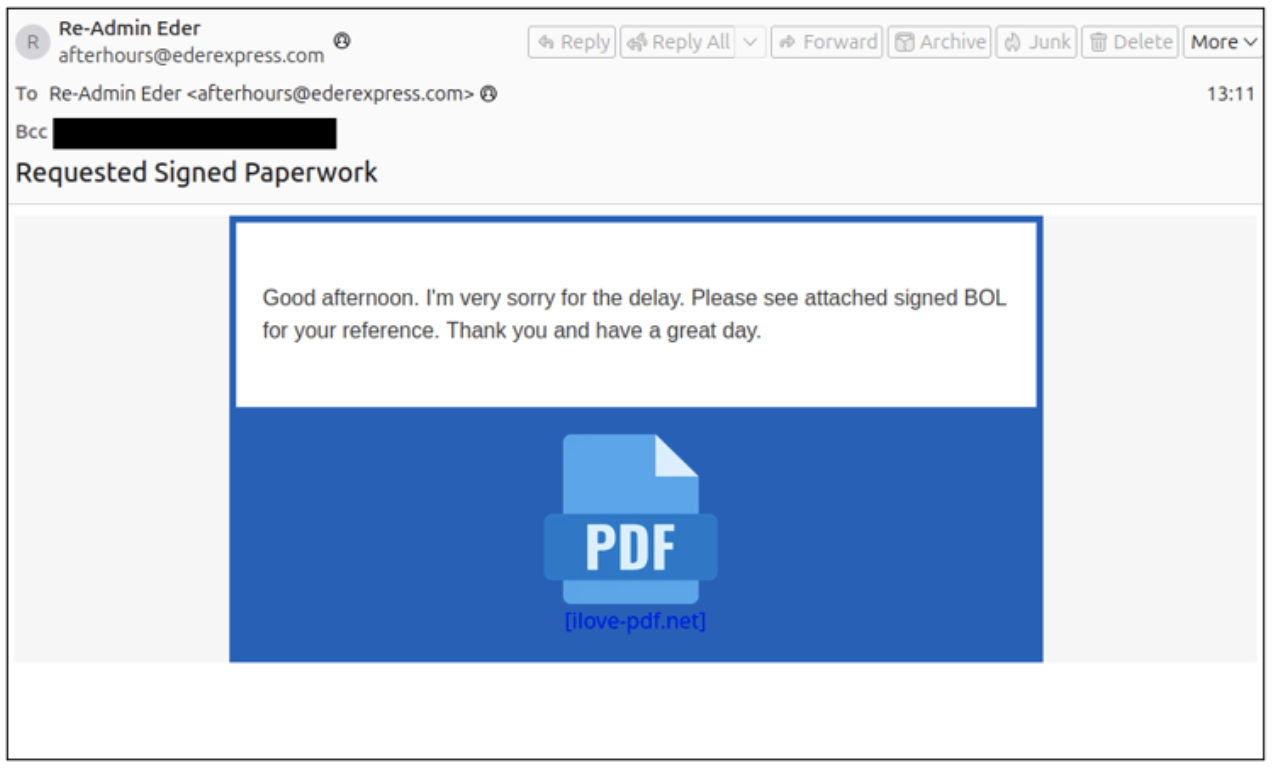
From there, victims receive highly tailored emails that contain malicious links to installer files, typically executables or MSI packages.
When opened, these files install remote monitoring and management (RMM) or remote access software that gives the threat actor full control of the system while looking like legitimate IT tooling.
With that access, attackers perform reconnaissance, harvest credentials from browsers, pivot deeper into the environment, and take over additional accounts used for dispatch and freight booking.
Proofpoint also tracked a threat actor targeting ground transportation organizations distributing DanaBot, NetSupport, Lumma Stealer, and StealC, which we previously reported on.
Once embedded, the criminals use stolen identities to bid on real shipments under the name of trusted carriers and then coordinate the physical pickup of cargo by their accomplices.
Public reports describe cases where attackers canceled legitimate bookings, blocked dispatcher notifications, added their own devices to phone extensions, and quietly redirected loads to be stolen.
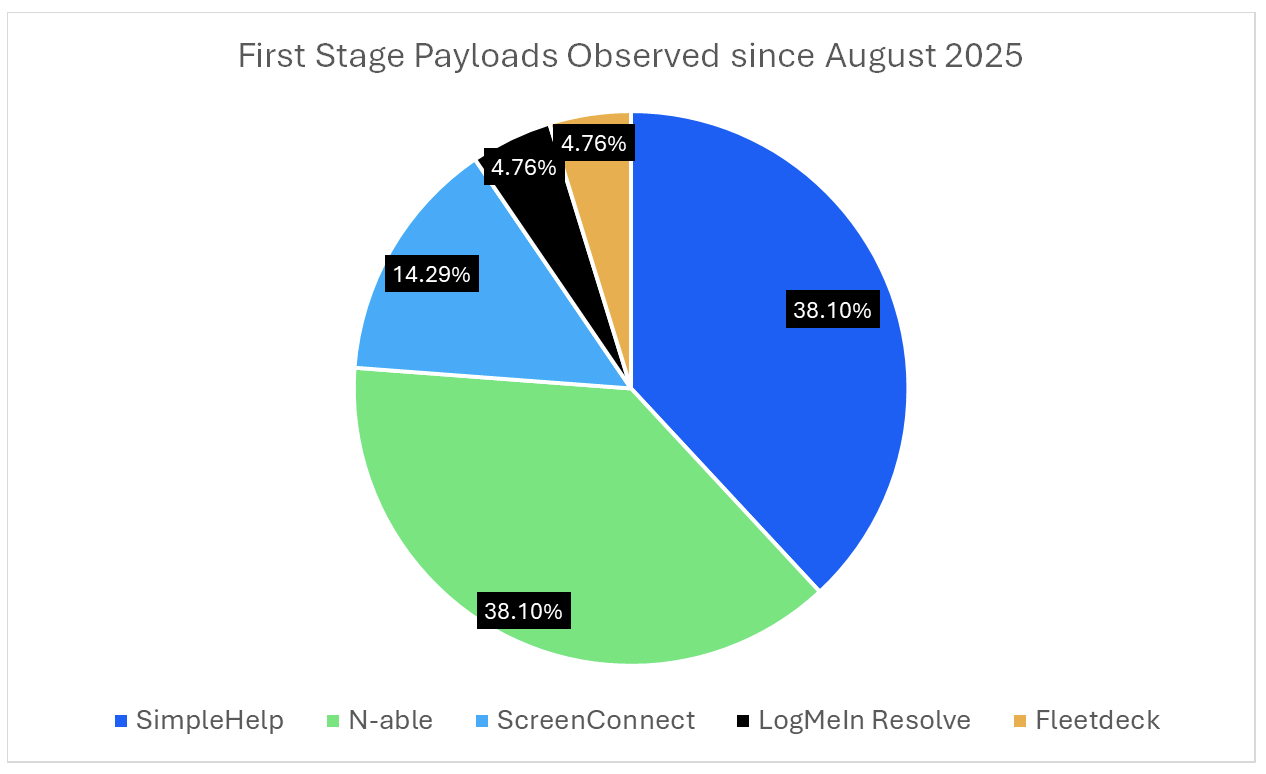
A notable aspect of these campaigns is the heavy use of commercial RMM tools such as ScreenConnect, SimpleHelp, N-able, PDQ Connect, and related remote access software.
These products are common in legitimate IT support, which makes them less suspicious to users and more likely to bypass antivirus and network defenses when signed installers are abused.
This fits a broader cybercrime trend: threat actors increasingly choose RMM tools as early‑stage payloads instead of traditional remote access trojans because they blend in with normal administrative activity.
Whether the final goal is data theft, account takeover, or cargo fraud, both infostealers and RMMs ultimately serve the same purpose of providing persistent remote access to valuable systems.
Mitigations
Although the latest campaigns highlighted by Proofpoint focus on North American trucking and freight, insurers and risk experts warn that strategic, cyber‑enabled cargo theft is rising globally, with hotspots in markets including the U.S., Brazil, Mexico, India, Germany, Chile, and South Africa.
Industry reports note that average loss values are climbing as criminals selectively target higher‑value loads and blend identity fraud, phishing, and remote access abuse into well‑planned theft operations.
Industry groups advise transportation firms to tightly control which RMM tools are allowed, block unknown installers from email, improve monitoring for remote access traffic, and train staff to spot suspicious load offers and unexpected software prompts.
With email‑driven campaigns already numbering in the dozens and losses projected to keep rising, experts warn that trucking and logistics organizations must treat cyber‑enabled cargo theft as a critical operational risk, not just an IT problem.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


