
A sophisticated malvertising and social-engineering campaign that pivoted from weaponized GitLab Pages to abusing claude.ai’s shared chat feature, enabling operators to deliver an in-memory remote-access trojan (RAT) via a China-themed loader chain.
Across seven weeks (April 8–June 14, 2026) investigators tracked 106 unique malicious hostnames across six attack waves, revealing rapid infrastructure rotation, targeted geographic focus, and iterative lure testing that prioritized AI developer tooling keywords.
The attack flow blended paid search malvertising, trusted-host abuse, and copy-paste “ClickFix” social engineering.
Google Ads lured technically proficient users searching for AI developer tools with ads impersonating legitimate brands Claude, ChatGPT Codex, Perplexity, Cursor IDE, JetBrains and others and directed them either to GitLab Pages subdomains or, later, to claude.ai shared-chat URLs.
Using free, high-reputation platforms (gitlab.io and claude.ai) let the actors bypass domain-based filters and browser heuristics; victims landed on valid, properly certified pages where standard URL- and certificate-based defenses offered no signal of compromise.
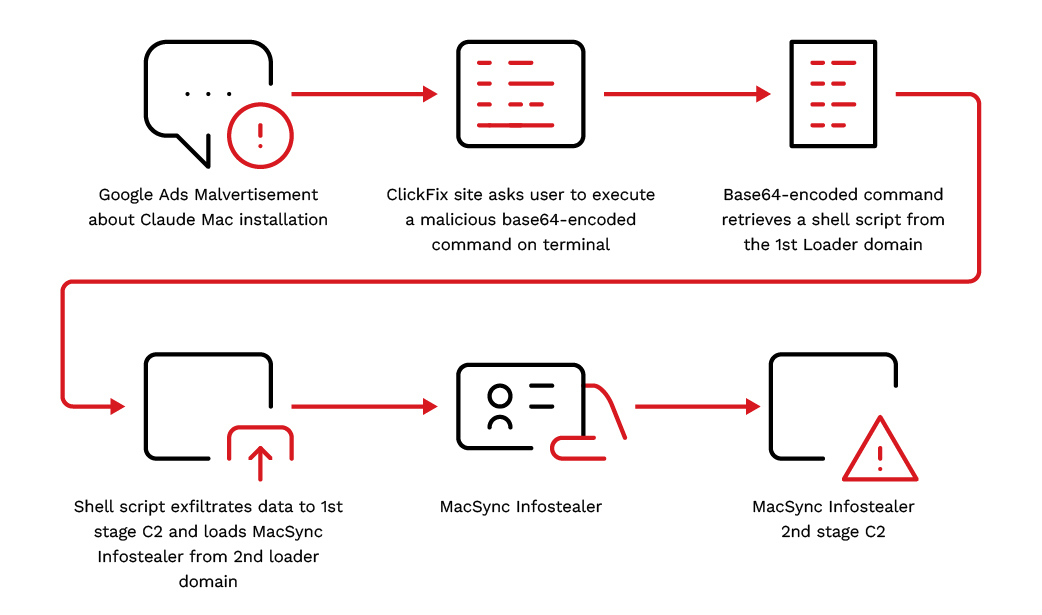
Early waves relied on 92 malicious GitLab Pages hostnames that mimicked software download pages and delivered ClickFix instructions prompting victims to open Terminal or PowerShell and paste a command.
According to TrendAI™ Research tracked 106 unique malicious hostnames deployed across six distinct attack waves over just seven weeks with operators continuously rotating infrastructure and testing new AI brand lures.
That command fetched and executed a multi-stage loader hosted on attacker infrastructure. The loader chain incorporated a China-themed motif in its naming and behaviors, but analysis shows the primary purpose was to stage an in-memory RAT rather than to install a persistent disk-resident payload.
China-Themed Loader Chain
The loader decrypted and executed the RAT entirely in memory, reducing forensic artifacts and complicating detection by endpoint protection solutions that rely on file-based signatures.
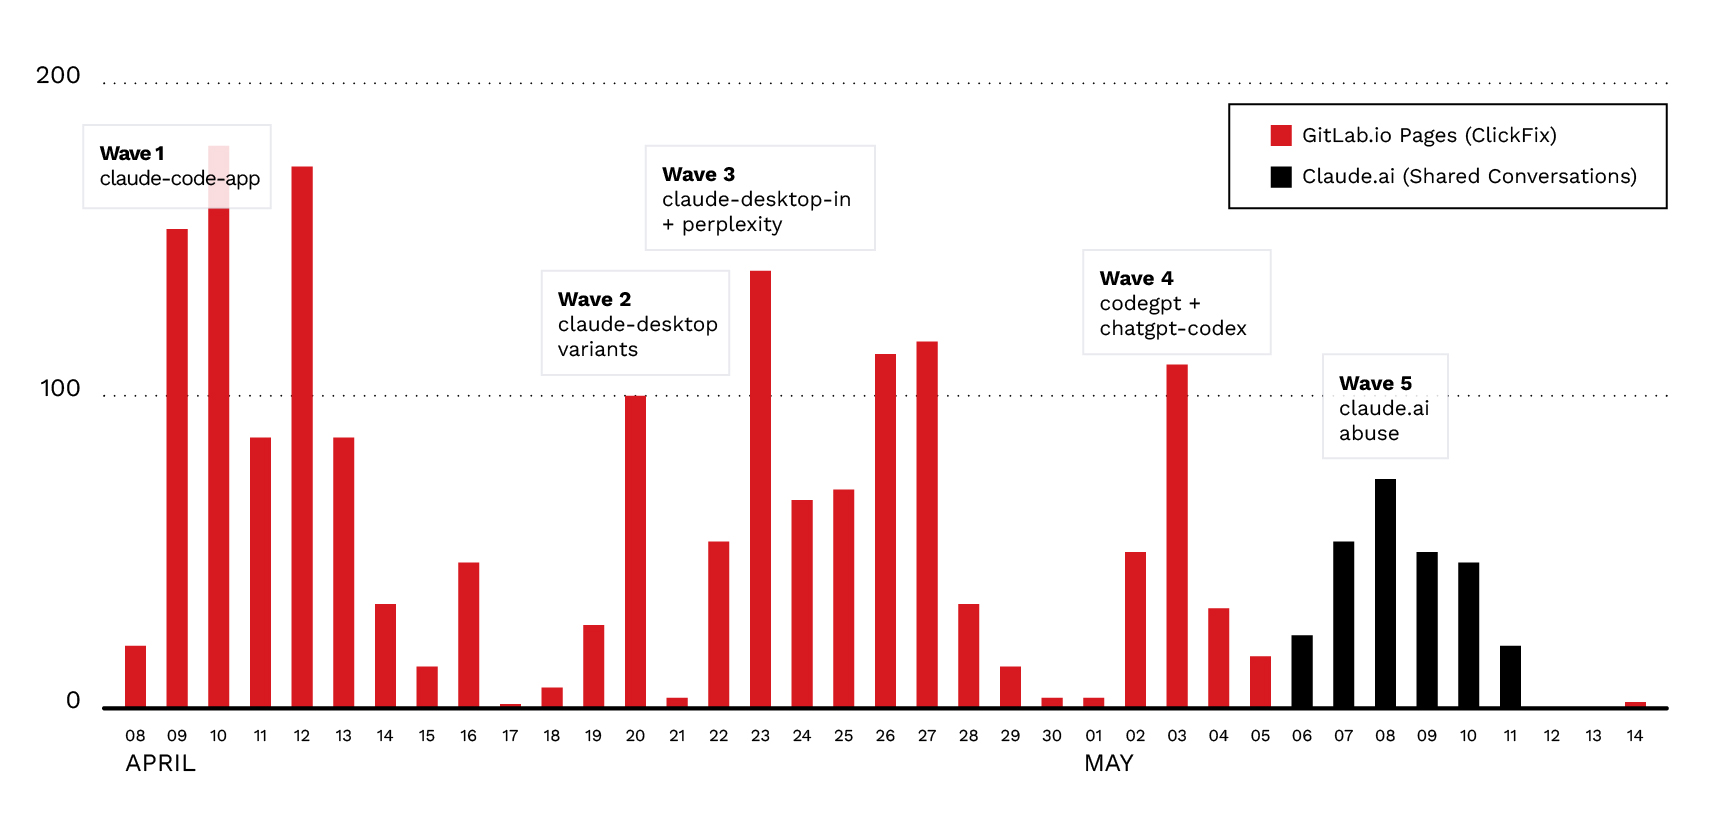
A significant tactical escalation occurred when operators weaponized claude.ai’s Share feature. TrendAI™ observed at least 61 unique shared conversation IDs and multiple Google Ads campaign IDs directly pointing to claude.ai/share/<uuid> URLs.
Because the malicious content resided on claude.ai itself, defenses that flag low-reputation domains or certificate anomalies were effectively neutralized.
The shared chats impersonated trusted support personas (for example, “Apple Support” or “Corda Team”) and presented curated instructions typically a single curl piped through base64 decode that ultimately fetched a loader script.
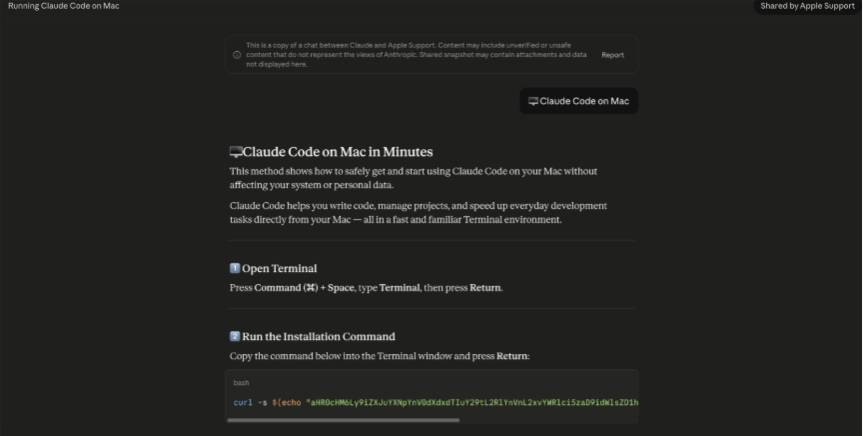
That script performed environment checks (notably excluding systems with Russian keyboard layouts) and, if cleared, retrieved and executed a MacSync infostealer variant before pivoting to the in-memory RAT stage.
The campaign’s dual-use infrastructure also hosted Mac utility scams, illustrating operator diversification to maximize clickthroughs.
Geographically the campaign disproportionately impacted the Asia-Pacific region, which accounted for roughly 67% of confirmed victims; Taiwan alone contributed about 30.5% of traffic.
The concentrated distribution signals deliberate geo-targeting in Google Ads and iterative keyword testing across AI brands to optimize engagement.
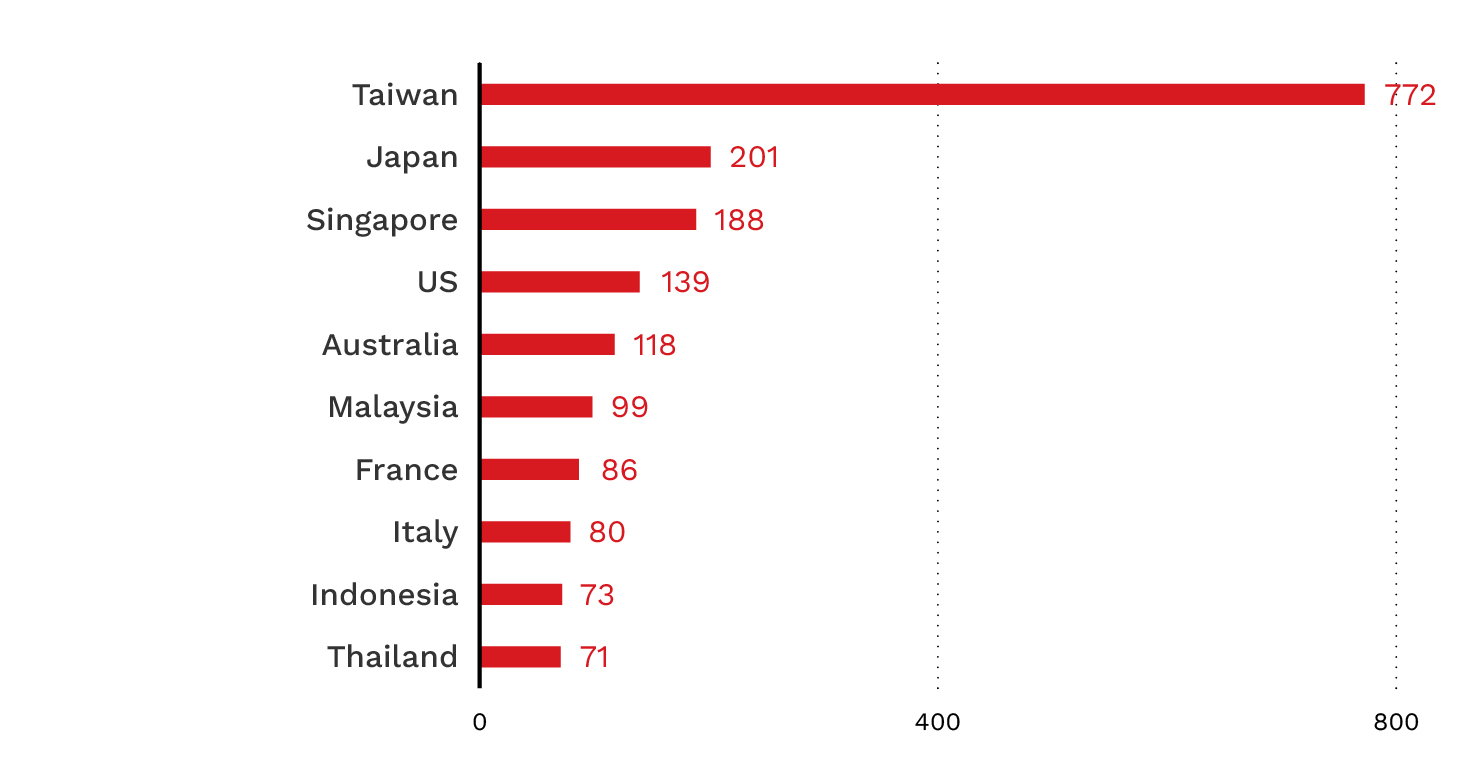
Operators continuously rotated pages and campaign parameters across weekly waves, using performance telemetry to refine lures and broaden targeting to Singapore, India, and European countries in later waves.
Upon notification, Anthropic removed the malicious shared conversations, banned the responsible accounts, and implemented additional abuse mitigations for shared chats.
TrendAI™ continues to monitor the campaign and recommends immediate defensive actions: disable risky copy-paste execution workflows, educate users on ClickFix-style prompts, implement script-blocking and shell command inspection at endpoints, monitor for in-memory RAT indicators.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


