

Chinese state-aligned hackers compromised a Microsoft Exchange server at a major energy firm. They repeatedly reused that same entry point to run a months‑long espionage operation, deploying the Deed RAT and Terndoor backdoors to maintain deep access across the network.
The activity is attributed with moderate‑to‑high confidence to FamousSparrow, a China‑aligned APT cluster that overlaps tactically with Earth Estries and Salt Typhoon.
Investigators assess the campaign as long‑running cyber‑espionage, not ransomware or smash‑and‑grab data theft.
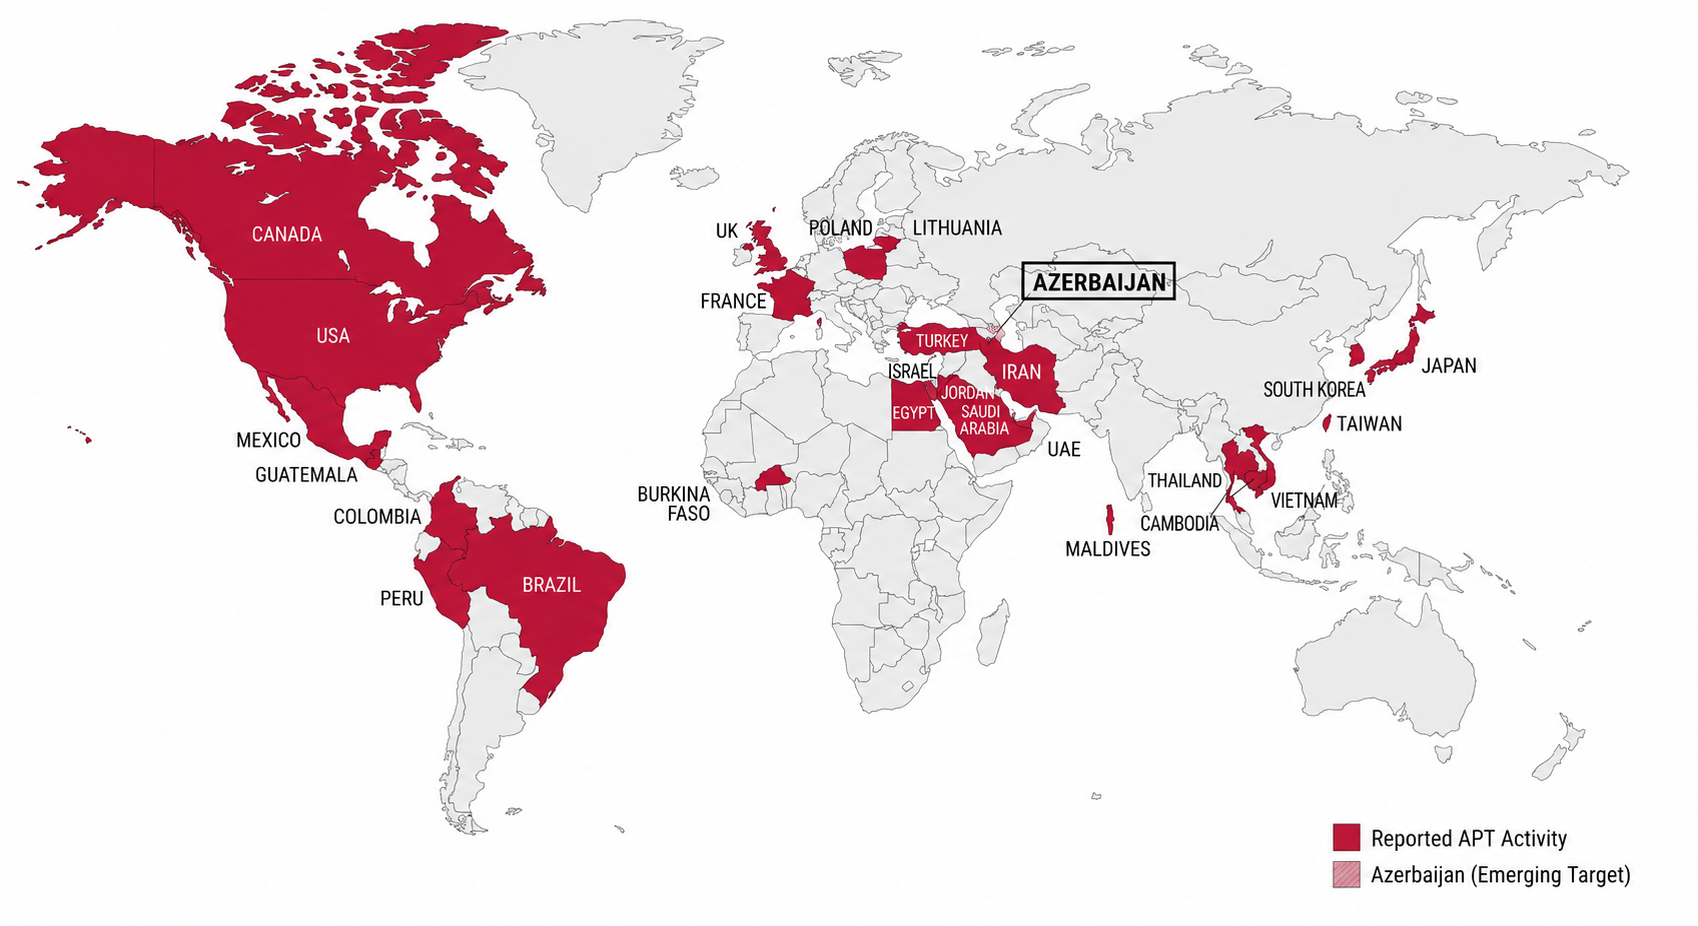
The timing and location are strategically significant, as Azerbaijan’s role in supplying gas to Europe has grown sharply since the end of Russia’s Ukraine transit agreement and disruptions in the Strait of Hormuz.
By targeting an energy company in this corridor, the attackers gain visibility into European energy flows at a moment of heightened geopolitical tension.
The intrusion started on December 25, 2025, when the Exchange IIS worker process w3wp.exe attempted to write an ASPX web shell into a public directory while running under the MSExchangePowerShellAppPool, indicating exploitation of the ProxyNotShell Exchange exploit chain.
Bitdefender researchers uncovered a multi‑wave intrusion against an Azerbaijani oil and gas company between late December 2025 and late February 2026, expanding Chinese APT activity into the South Caucasus energy sector for the first time in public reporting.
Over the following days, the attackers dropped multiple web shells with benign‑looking names such as key.aspx, log.aspx, errorFE.aspx, and signout.aspx to harden their foothold.
These web shells then served as control points to execute commands and stage malware payloads directly from the vulnerable server.
Prior public reporting documents activity against telecoms, government, and technology sectors across the United States, Asia-Pacific, Middle East, and South Africa.
ProxyShell and ProxyNotShell are long‑known exploit chains that allow remote code execution on unpatched Exchange servers, yet many organizations still expose these systems without proper patching or segmentation.
Bitdefender notes that the attackers repeatedly returned to exactly the same Exchange entry point even after partial cleanup, illustrating how unremediated vulnerabilities become durable access channels for APTs.
Chinese APT Exploits Microsoft Exchange
In the first wave, the group deployed Deed RAT using a sophisticated DLL sideloading chain that abused the legitimate LogMeIn Hamachi service.
A trusted binary (LMIGuardianSvc.exe) was used to load a malicious DLL (LMIGuardianDll.dll), which in turn decrypted and executed an encrypted payload file (.hamachi.lng) containing the Deed RAT backdoor.
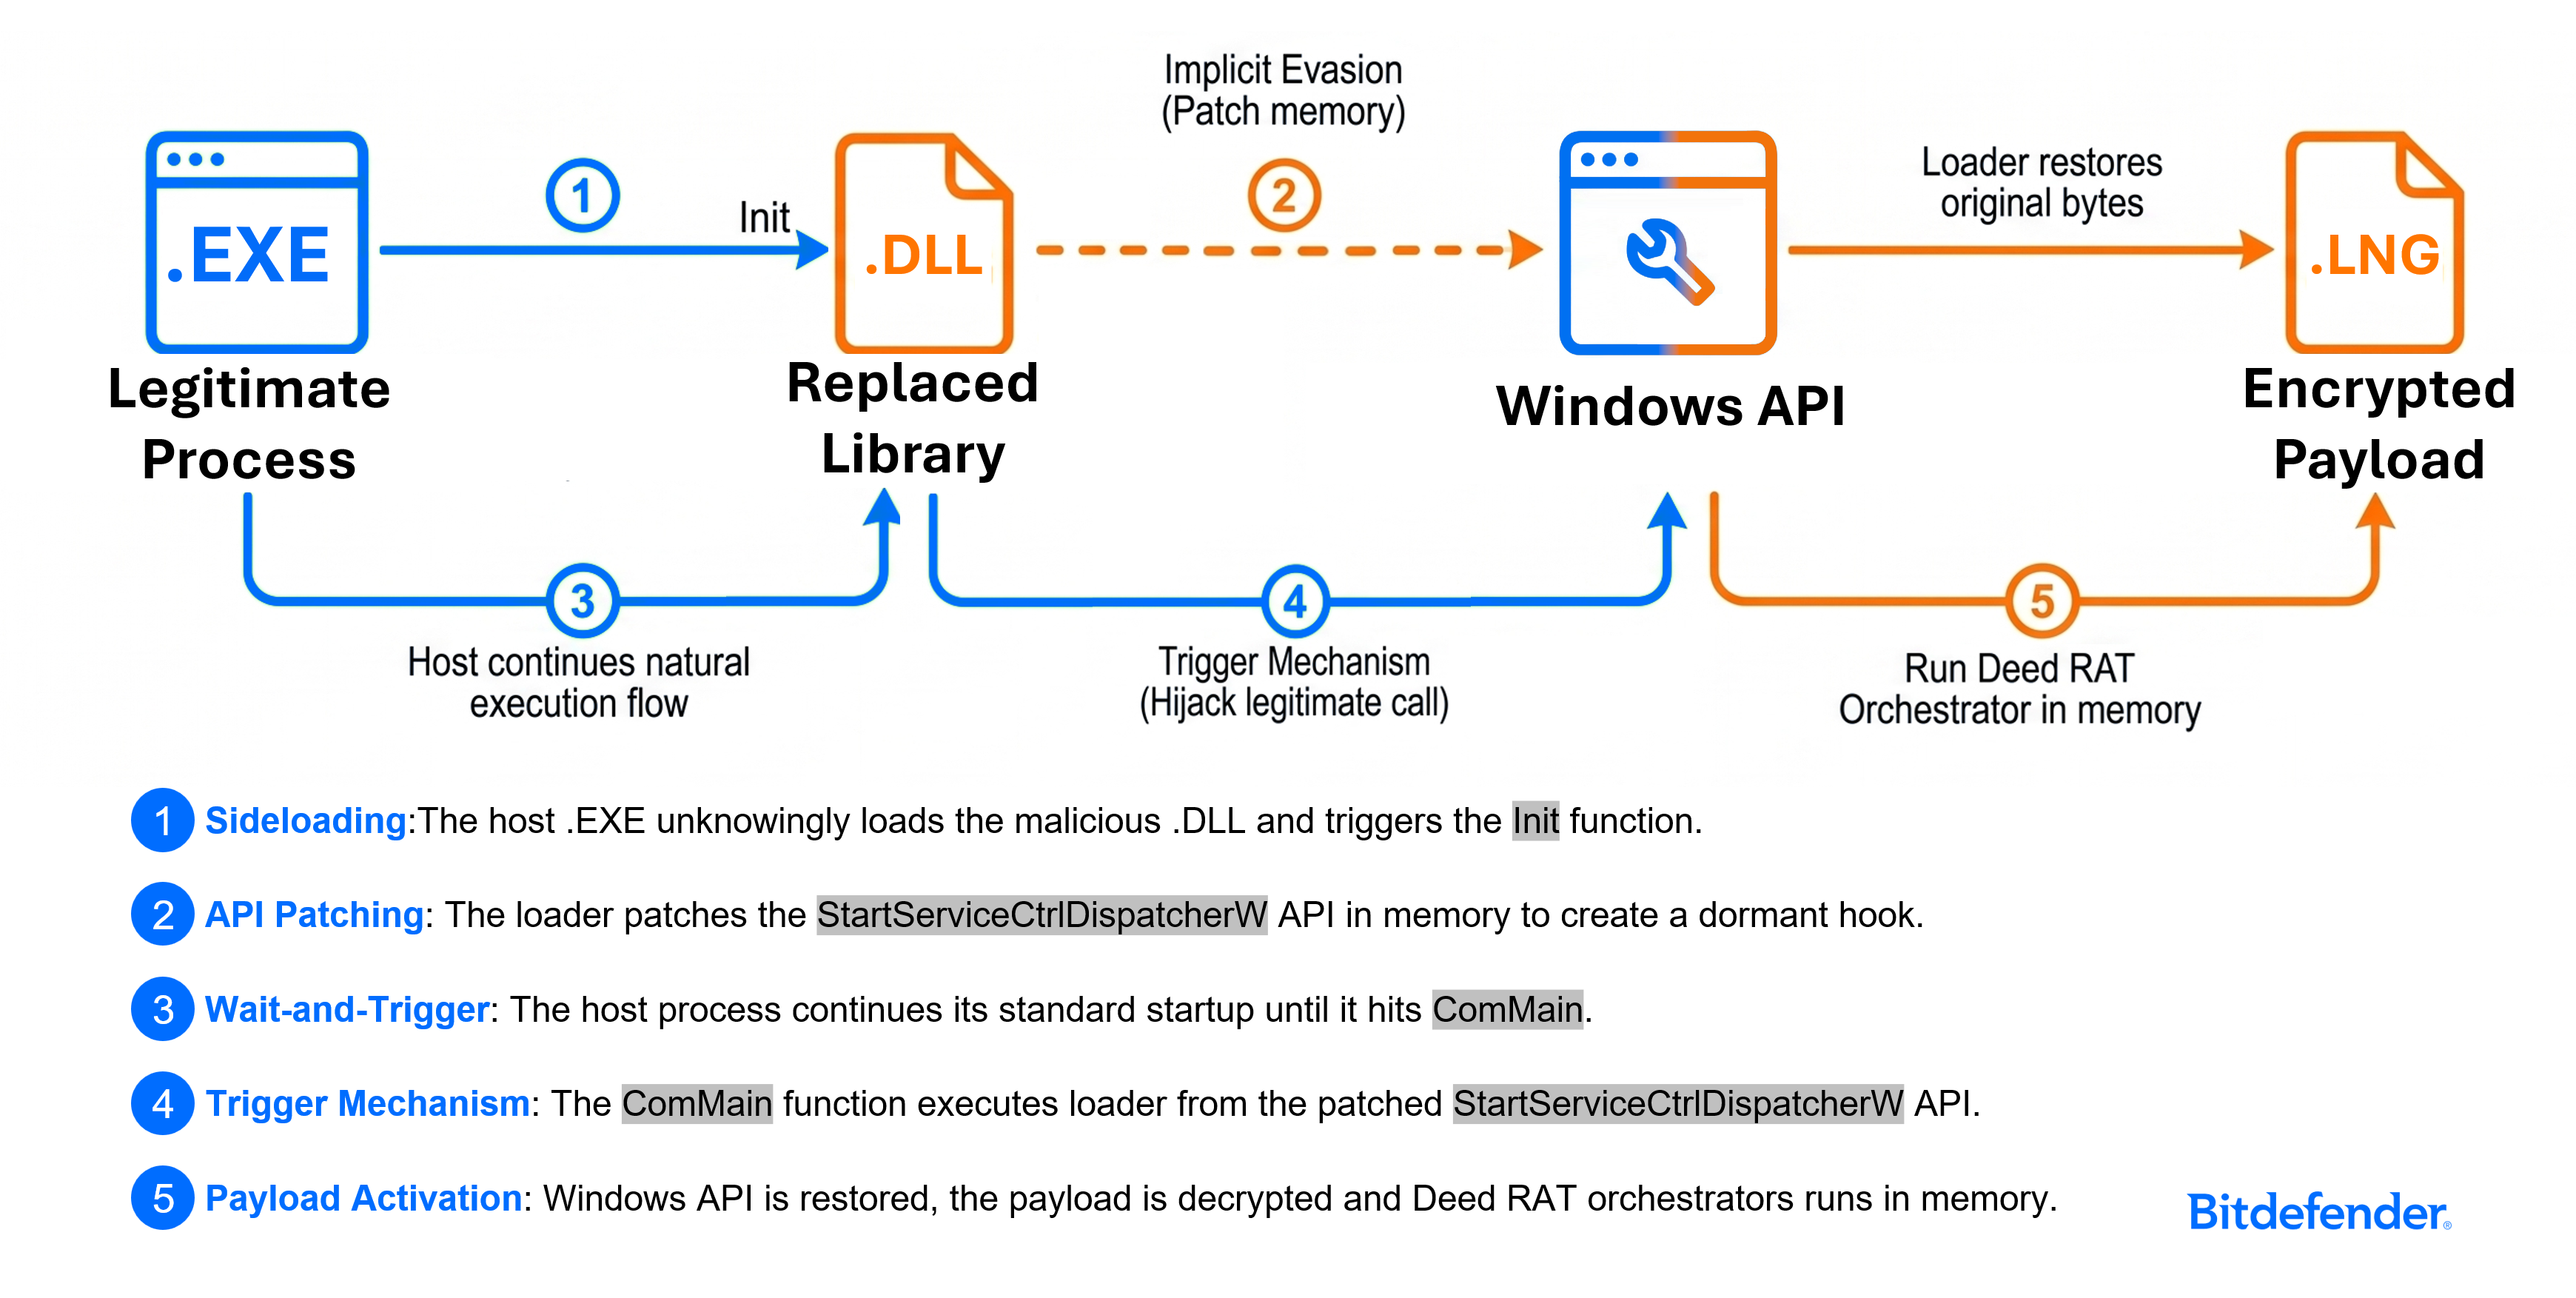
Unlike classic sideloading, this loader split its logic across two exported functions, Init and ComMain, and only triggered the payload after the host application followed its normal startup path and called a patched Windows API.
This two‑stage trigger acts as an implicit anti‑analysis layer, because sandboxes that execute the DLL in isolation or call a single export never reach the real malicious code.
The toolchain also shows evolution: magic constants were changed (for example to 0xFF66ABCD) and plugin compression moved from Snappy to Deflate, indicating ongoing development of the Deed RAT ecosystem.
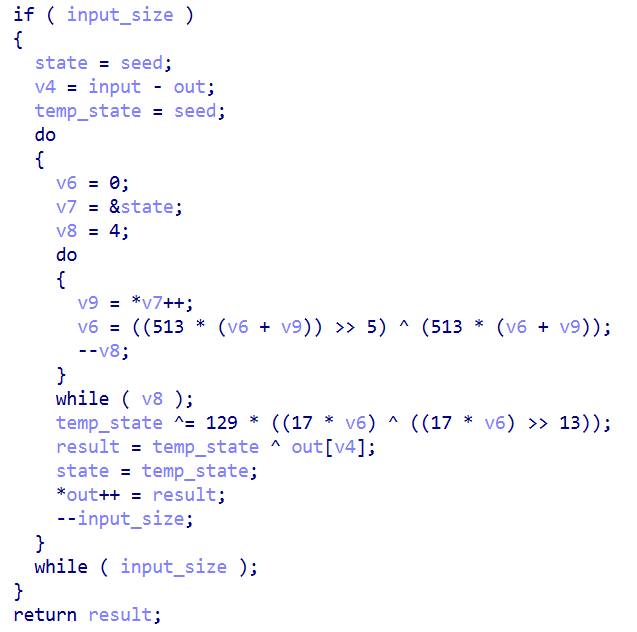
The blob data is XOR-decrypted using the byte stream generated by a custom PRNG algorithm. Following this decryption stage, the plugin is only partially recovered, with the header (including the 0xFF66ABCD magic value).
Once active, Deed RAT loads multiple plugins for configuration management, networking, proxying, installation, and process injection, giving FamousSparrow full remote control over compromised hosts.
Command‑and‑control communications in one later wave were routed over HTTPS to domains impersonating security vendors, including sentinelonepro[.]com.
After defenders removed some implants, the attackers launched a second wave, again entering through the same vulnerable Microsoft Exchange server but this time trying to deploy the Terndoor backdoor via the Mofu loader.
They abused another signed binary, a renamed deskbandinjector64.exe, to sideload a malicious DLL and eventually drop a kernel‑mode driver (vmflt.sys) as part of a rootkit‑like persistence chain.
Although security controls blocked this attempt before full installation, memory forensics revealed Mofu‑style shellcode that decrypted an LZNT1‑compressed PE payload assessed to be Terndoor, based on section layout, RC4 implementation, and driver‑loading behavior matching Cisco Talos’ UAT‑9244 reporting.
From the initial Exchange host, the attackers moved laterally using Remote Desktop Protocol with domain administrator credentials, then relied on Impacket‑style atexec and smbexec techniques to spread Deed RAT to additional servers.
This gave them redundant footholds deeper in the network, ensuring that cleaning a single machine would not evict them from the environment.
Defenders are urged to immediately patch or isolate exposed Exchange servers vulnerable to ProxyShell and ProxyNotShell, and to monitor for IIS worker processes writing ASPX files in web‑accessible paths.
Security teams should also watch for DLL sideloading chains involving well‑known signed binaries, suspicious kernel‑driver services in non‑standard locations, and administrator RDP sessions that quickly spawn PowerShell and drop executables.
Finally, any environment that detects Deed RAT or Terndoor activity should treat the incident as a long‑term espionage campaign, rotate high‑privilege credentials, and conduct thorough memory and network forensics to evict the intruders.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


