

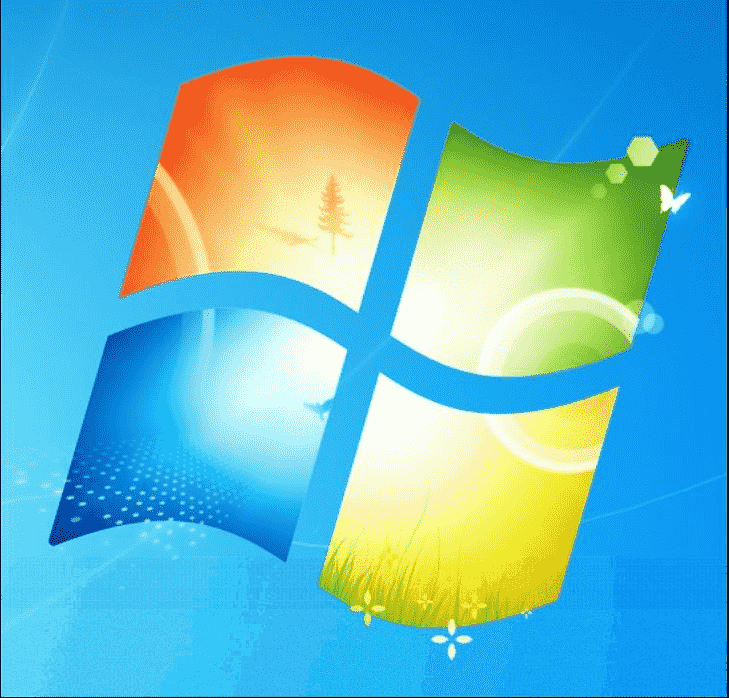
In a recent discovery made by Symantec’s security researchers, the Witchetty group has been found to be launching a malicious campaign that hides a backdoor behind the Windows logo using steganography.
Several countries in the Middle East and the African stock exchange are being targeted by this cyber-espionage campaign, which began in February 2022.
An old bitmap of the Windows logo is steganographed in the campaign to hide an XOR-encrypted malware.
Witchetty
ESET is the first security company to detect Witchetty, which was discovered in April 2022, and it is one of the sub-members of TA410 (aka Cicada).
There has been a steady update of the toolset of the Witchetty hacker group (aka LookingFrog), using new malware to attack targets across a variety of fields, mainly in the following regions:-
- Middle East
- Africa
The group has recently begun using a number of new tools in their arsenal, including a backdoor Trojan called “Backdoor.Stegmap”.
Technical Analysis
According to a Symantec report, The malware that is encrypted with XOR is hosted on a trusted cloud service instead of hosted on the attacker’s C&C servers. Consequently, when the backdoor is retrieved and activated, the security tools will not be able to detect it.
Security tools are less likely to suspect a download from a trusted host, like GitHub, than a download from a C&C server, as a download from GitHub is more likely to be legitimate.
By using Microsoft Exchange ProxyShell and ProxyLogon bugs, attackers gain initial network access and then drop the malicious web shells on vulnerable servers.
Following the extraction of the backdoor from the image file, the cybercriminals can then perform the following actions:-
- Editing and manipulating files and directories
- Start, enumerate, and kill processes can be done from the command line
- Edit the Windows registry to make the malicious changes
- Ensure that additional payloads are delivered
- Extraction of files
New Tools Used
Here below we have mentioned all the new tools used by the attackers:-
- Custom proxy utility
- Custom port scanner
- Custom persistence utility
Infected computers are configured to act as servers and communicate with the C&C servers as clients, without actually being configured to act as a client themselves.
Hackers were exploiting old vulnerabilities by taking advantage of poorly administered public servers as part of this campaign in order to compromise the target network.
There is a strong possibility that Witchetty is affiliated with the state-backed Chinese group APT10. In every part of the world, governments and government organizations are vulnerable to threats from TA410 and Witchetty.
But, there is no doubt that they target primarily Asian and African organizations in their attacks or malicious campaigns.
Cyber Attack with Zero Trust Networking – Download Free E-Book


