

It has been reported by the Recorded Future’s Insikt Group that RedGolf, a Chinese state-sponsored threat actor group, was using a backdoor designed especially for Windows and Linux systems called KEYPLUG to infiltrate networks.
As one of the world’s most prolific threat groups, RedGolf has been active against a variety of industries around the world for many years.
RedGolf Infrastructure & TTPs
There is a history of this group developing and using a variety of custom malware families over the years. It has demonstrated an ability to weaponize newly reported vulnerabilities quickly.
Here below, we have mentioned the recently reported malware families used by this group:-
- Log4Shell
- ProxyLogon
The industries and organizations primarily targeted by RedGolf are:-
- Aviation
- Automotive
- Education
- Government
- Media
- Information technology
- Religious organizations
Apart from this, there are a number of public and zero-day flaws that the RedGolf threat group has historically exploited for the purpose of gaining initial access to internet-facing devices, including:-
KEYPLUG Malware
During 2021 and 2022, RedGolf targeted US state government entities using KEYPLUG, a custom and modular Linux backdoor.
Several KEYPLUG samples and infrastructures that RedGolf used from at least 2021 until 2023 have been identified by Insikt Group.
In a campaign that compromised the security of at least six state governments in the USA, RedGolf heavily used the KEYPLUG platform between May 2021 and February 2022, as first exposed by Google-owned Manidant in March 2022.
KEYPLUG C2, including the following, supports a total of 5 network protocols:-
- HTTP
- TCP
- KCP
- UDP
- WSS
Technical Analysis
In October 2022, Malwarebytes published information on a separate set of attacks exploiting an unexplored implant dubbed DBoxAgent to use KEYPLUG on government entities in Sri Lanka early in August of that year.
As Recorded Future puts it, these campaigns appear to share a very close connection with RedGolf’s campaign, which was also attributed to Winnti (aka APT41, Barium, Bronze Atlas, or Wicked Panda).
According to security analysts, the latest RedGolf activity has not yet been associated with any specific victimology.
Due to the overlaps between this action and previously reported cyber espionage campaigns, they believe these activities may be conducted for intelligence purposes instead of financial gain or profit.
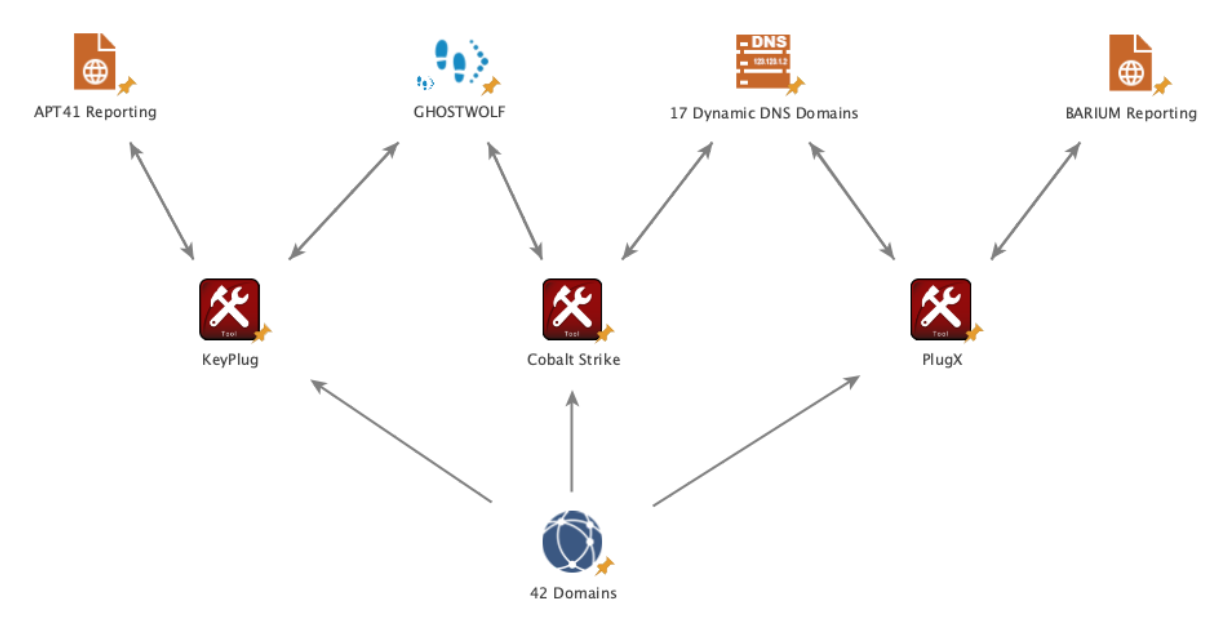
Furthermore, it was noted that the hacking group used other tools such as Cobalt Strike and PlugX in addition to the KEYPLUG samples and its operational infrastructure, which is codenamed GhostWolf.
42 IP addresses comprise the GhostWolf infrastructure and are used as commands and controls for the KEYPLUG system.
To gain initial access to targets’ networks, RedGolf will keep demonstrating the operational tempo that will allow it to rapidly exploit vulnerabilities in externally facing enterprise appliances and quickly weaponize those vulnerabilities.
Recommendation
To defend against RedGolf attacks, organizations are required to follow the mitigations recommended by the experts that we have mentioned below:-
- Ensure that patches are applied regularly.
- Check access to the devices connected to the networks external to the organization.
- Identify the command and control infrastructure used by threat actors and block it.
- To monitor for malware, intrusion detection, and prevention systems need to be configured in a way that they detect malware.
Searching to secure your APIs? – Try Free API Penetration Testing
Related Read:
- Chinese Hackers Exploit FortiOS Zero-Day Vulnerability to Deploy New Malware
- Chinese Hackers Using 42,000 Phishing Domains To Drop Malware On Victims Systems
- Chinese Hackers ScanBox Framework To Deploy Malware on Selected Targets
- Chinese Hackers Deploy Malware in Firmware Images of Certain Motherboards







