

A coordinated supply-chain campaign has been weaponizing GitHub proof-of-concept (PoC) repositories to compromise vulnerability researchers and penetration testers, delivering a stealthy Python Remote Access Trojan (RAT) dubbed “ChocoPoC.”
The lure is simple and effective: newly disclosed high-severity CVEs create urgency for fast PoC and scanner module development.
Adversaries create seemingly legitimate PoC repositories that include malicious entries in requirements.txt (notably packages named frint and skytext) so that when researchers run pip install to set up an exploit environment, a compiled native Python extension is loaded.
That binary (gradient.so / gradient.pyd) contains obfuscated code that dynamically resolves Python and OS APIs, implements anti-analysis checks (PEB walking, debugger and hardware breakpoint detection, export hashing), and decrypts embedded payloads only when executed in a specifically gated runtime (for example, when a PoC file name hash matches EXPLOIT_POC.py).
This environment keying allows the malware to remain dormant in sandboxes and evade many automated detections.
Discovered in a joint investigation by YesWeHack and Sekoia TDR, the attack chain abuses transitive Python dependencies published on PyPI and leverages Mapbox datasets as a covert command-and-control (C2) channel to exfiltrate browser credentials, files, and system intelligence from developer machines.
Once activated, the native extension drops a trojanised _distutils_hack package and malicious .pth files into site-packages, ensuring persistence by auto-executing on every Python interpreter startup.
ChocoPoC Campaign Abuses GitHub
A downloader named choco.py then boots a dead-drop retrieval mechanism: it uses DNS-over-HTTPS (DoH) to resolve api.mapbox[.]com to an attacker-controlled IP, sends HTTPS requests with the legitimate Mapbox host in the SNI/Host header, fetches a Base64-encoded payload stored in a Mapbox dataset feature, decodes and exec()s it.
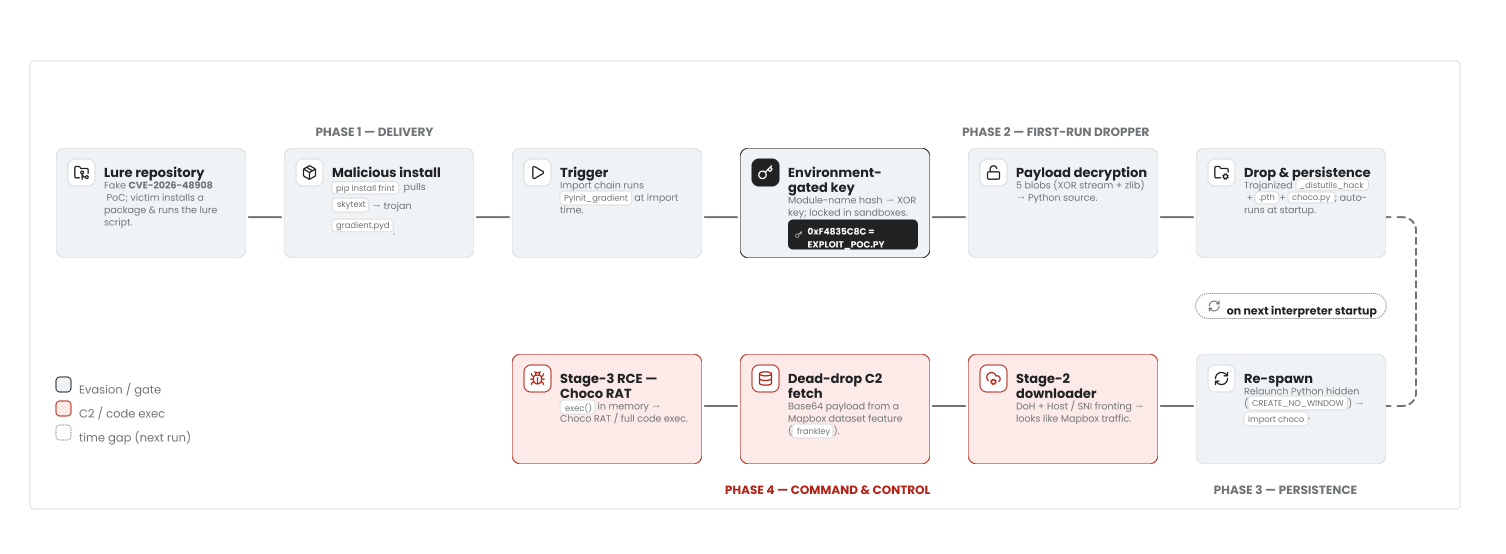
The final stage is a fully functional RAT that polls the Mapbox-hosted C2 for commands or falls back to a dedicated IP for bulk exfiltration.
ChocoPoC’s capabilities are extensive: automated extraction of stored credentials, cookies, autofill entries and history from Chrome, Edge, Brave and Firefox; targeted file discovery and compression (.txt, .md, .db variants); shell history harvesting; system reconnaissance; arbitrary command execution and dynamic Python code execution via exec().
Commands and variable names show Spanish-language artifacts (hola, dormir), and minor coding errors indicate an actor iterating on a bespoke tool rather than relying on polished commercial malware.
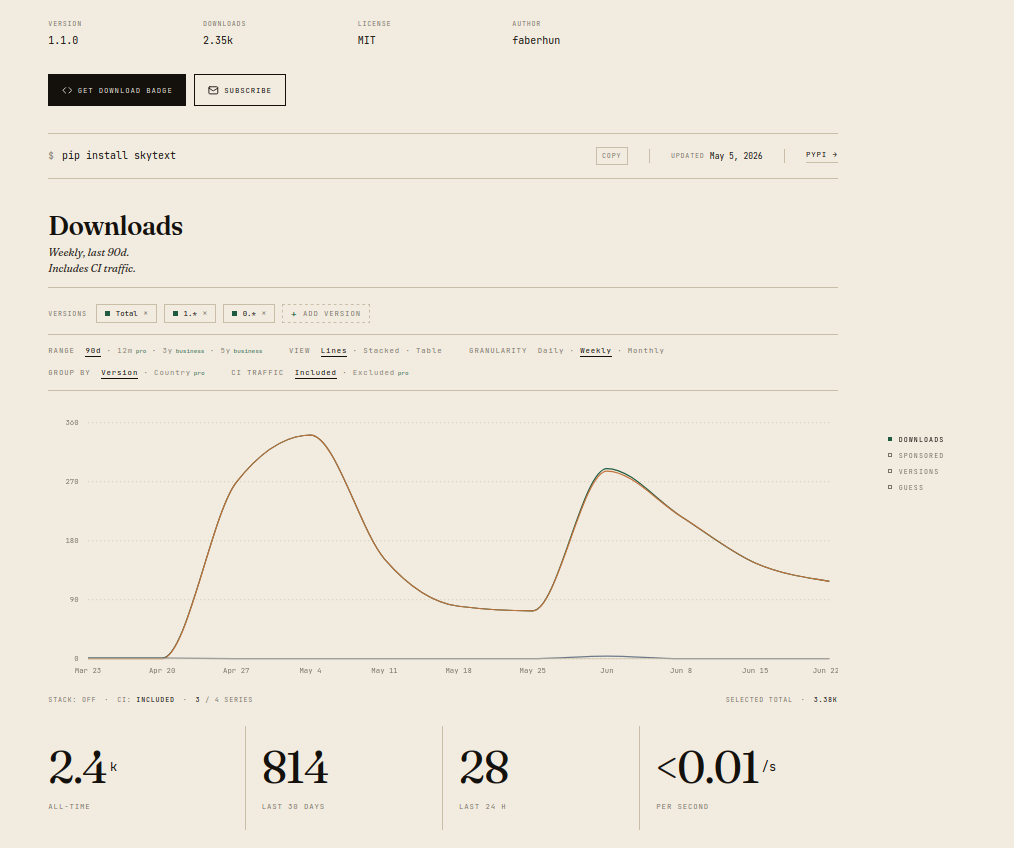
The campaign is broad and persistent. At least seven malicious PoC repositories tied to high-profile CVEs (FortiWeb, React2Shell, Joomla SP Page Builder, Ivanti Sentry, PAN-OS, CheckPoint VPN and others) have been identified; PyPI download metrics for skytext and frint show thousands of pulls timed around vulnerability disclosures.
Investigators link multiple GitHub and PyPI accounts often ephemeral or created from leaked credentials to the same operational patterns: reused Mapbox feature IDs, identical hashing gates, and similar persistence techniques, pointing to a single actor reusing an “opsec” kit across waves in late 2025 and 2026.
Mitigations are straightforward but require discipline: never pip install unreviewed PoC requirements on a production or user-profiled machine; perform dependency installs inside fully isolated, disposable environments (ephemeral VMs or containers).
Prevent credential access and persist only for the test; audit native wheels (.so/.pyd) in dependencies with static and dynamic analysis tools; monitor PyPI and GitHub for sudden new packages tied to PoCs; and block suspicious Mapbox API keys or unexpected Mapbox dataset access at network egress where practicable.
IOCs
Malicious PyPi Packages
| Package | Version | SHA-256 (wheel) |
|---|---|---|
| skytext | 1.1.0 | 93739477cd379adef95126b22758c0e644282d2028dd297328ce856fa111dd06 |
| frint | 0.1.2 | 17997e9e0256d0f5d5d21a4852c37f16b338e4bb9c2bec09bdfd822b24aa76b4 |
| slogsec | * | 5abd45d6f4a1705dca55d882f017d4768888dce9ad99cea40b3da35c23de5cae |
Malicious Binaries / Native Python Extensions
| File | SHA-256 |
|---|---|
| gradient.pyd (Windows) | 40569318e89db751ff3886b2617d990d8a343f0d1d8727b7f978a28129ca36bc |
| gradient.so (Linux) | 320b29844892e3c59bc6fcb07e701b2b3230a37cb4a13176174e9e294ec6d43e |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 repositories to compromise vulnerability researchers and penetration testers.)