

In order to steal cryptocurrency and clipboard contents, ViperSoftX was detected by the security analysts at Avast, a Windows malware that is using a Google Chrome extension called VenomSoftX.
A JavaScript-based RAT and crypto-hijacker are hidden within this Chrome extension which constantly attempts to steal the cryptocurrency and clipboard contents.
Approximately 93,000 ViperSoftX infection attempts were detected and stabilized by Avast experts since the beginning of 2022 in the following countries:-
- The US
- Italy
- India
- Brazil
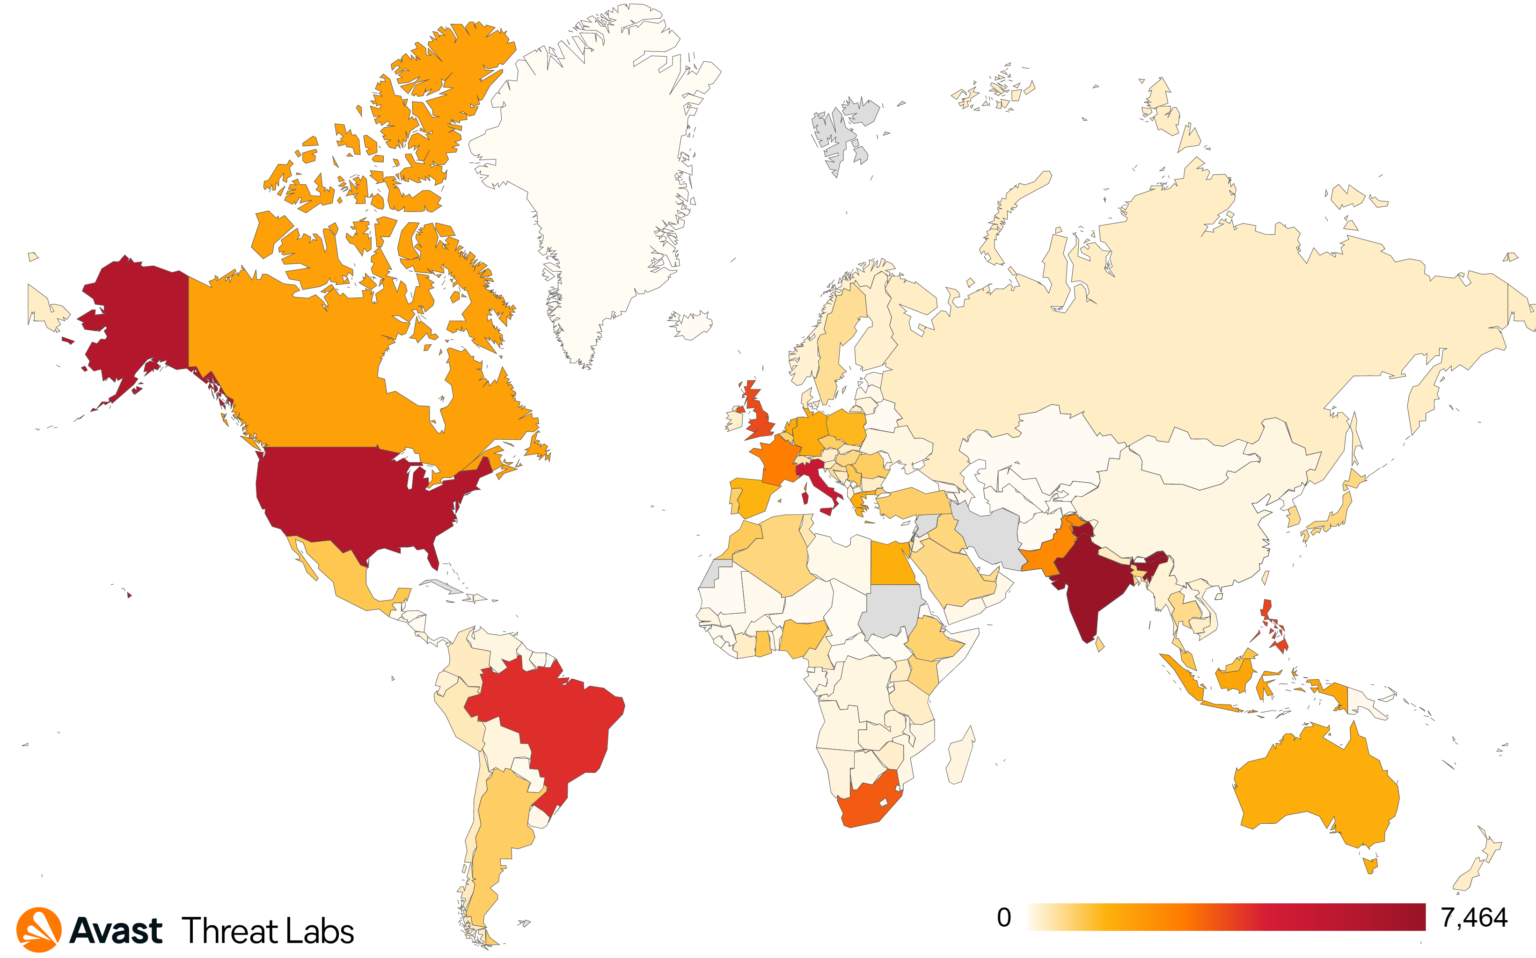
While the following are the countries that have been most affected by the crisis:-
- India (7,000+)
- USA (6,000+)
- Italy (5,000+)
Furthermore, this extension is also capable of hijacking other web browsers in addition to Chrome, including:-
- Safari
- Firefox
- Brave
- Edge
- Opera
Security researchers Cerberus and Colin Cowie released data on ViperSoftX in 2020, indicating that it had been circulating since 2020.
Abilities of the Malware
In addition to granting full access to every page the victim visits, the malicious extension also provides a number of other abilities including:-
- Attacks the user by using the man-in-the-browser technique.
- Change cryptocurrency addresses on popular cryptocurrency exchanges by altering API data.
- Steal credentials.
- Steal clipboard contents.
- Intruders attempt to tamper with the cryptographic addresses on the websites that they visit.
- Send events reports to a command and control server via MQTT.
- Arbitrary command execution.
- Downloads of payloads from the C2.
Financial Gains
VenomSoftX and ViperSoftX are both malware programs that target infected computers in order to steal crypto assets from them. Here below we have mentioned the estimated statistics of their monetary gains:-
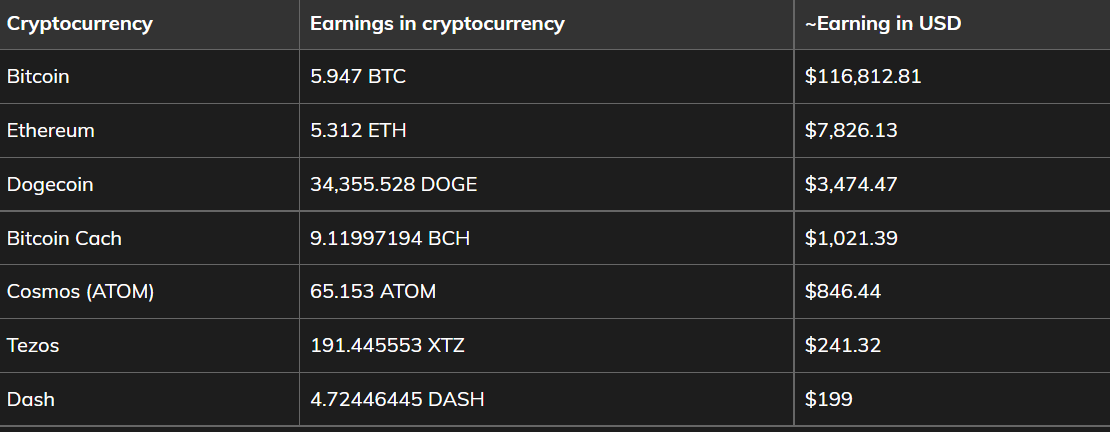
As of November 8, 2022, there is approximately $130,421.56 in the wallets of the operators of ViperSoftX and VenomSoftX that redirect stolen cryptocurrency.
There is a difference between this amount and the other possible profits from other activities since this figure only includes the amount sent to wallets for cryptocurrencies.
Infection Chain
ViperSoftX is mostly distributed through torrent files containing the cracked software and game cracks that are embedded in the torrent files.
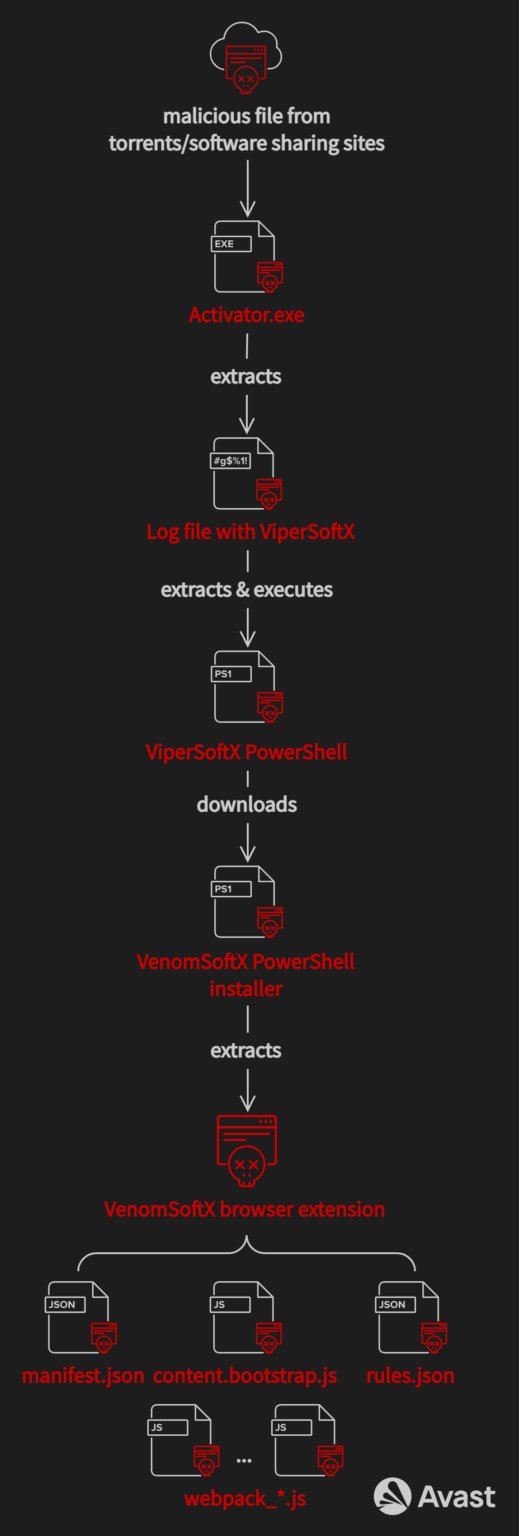
Upon downloading the file, you will find a file that contains an executable which is a malware loader that decodes the AES data in an attempt to create the following files:-
- A log file with a hidden additional payload resulting in the ViperSoftX PowerShell
- XML file for the task scheduler
- SyncAppvPublishingServer.vbs that is used to create a scheduled task for persistence
- Application binary that is supposed to be cracked
- Manifest file
As soon as the malicious code line is executed, it starts decrypting a payload called ViperSoftX stealer, which is hidden somewhere toward the bottom of the 5MB log file.
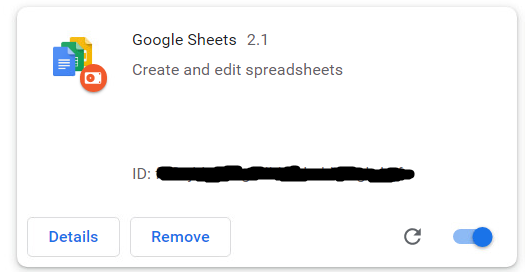
The extension’s intention is to disguise itself as a Google productivity app called “Google Sheets 2.1” so as to avoid detection by victims.
It appears that VenomSoftX and ViperSoftX activities overlap a bit since they both target cryptocurrency assets owned by victims. Since it has a different method of completing the theft, so it will have a higher chance of being successful.
Services Targeted
There are several services targeted by VenomSoftX, including the following:
- Blockchain.com
- Binance
- Coinbase
- Gate.io
- Kucoin
Besides monitoring the clipboard, the extension also monitors whether any wallet addresses have been copied to the clipboard. A user’s cryptocurrency wallet address can also be displayed on a website with the help of this extension by modifying the HTML on the website.
The extension not only redirects payments to the threat actor during this process but also controls elements in the background that make this possible.
The extension must be removed and the browser data needs to be cleared in order to ensure that the malicious extension has been completely removed from your computer.
Managed DDoS Attack Protection for Applications – Download Free Guide







