
Threat actors are exploiting the CitrixBleed 2 vulnerability, tracked as CVE-2025-5777, to hijack active NetScaler sessions protected by multi-factor authentication and gain a foothold in enterprise environments.
The activity indicates a standardized operator playbook, potentially operated by an initial access broker or ransomware affiliate.
Victims spanned unrelated organizations and sectors, yet attackers repeatedly used the same access method, privilege-escalation technique, rogue administrator accounts, and remote-management tooling.
CVE-2025-5777 affects NetScaler ADC and Gateway appliances configured as Gateway or AAA virtual servers.
The pre-authentication memory-overread flaw can be triggered through malformed POST requests sent to NetScaler login endpoints, including /p/u/doAuthentication.do.
By submitting an empty login parameter at scale, attackers can cause the appliance to disclose fragments of adjacent heap memory.
Those memory fragments may contain active session tokens, HTTP headers, internal addresses, certificate data, and session metadata.
An attacker can replay a stolen valid session token from another IP address without completing a new login, effectively neutralizing MFA because authentication has already been completed by the legitimate user.
In one Huntress investigation, a user legitimately authenticated with LDAP and MFA before the user’s session was accessed from an attacker-controlled IP address only 21 minutes later.
Huntress Tactical Response investigated approximately six intrusions between January and June 2026 and identified a highly consistent attack chain culminating in DragonForce ransomware deployment.
Investigators found no corresponding successful authentication event for the attacker, providing strong evidence that the session was stolen and replayed.
The earliest indicator was not conventional password spraying. NetScaler logs contained thousands of AAA LOGIN_FAILED events with unprintable binary values in the username field.
CitrixBleed 2 to Hijack MFA
Huntress determined that these values represented leaked heap memory rather than failed username guesses.
Defenders should investigate high-volume malformed login requests, empty form parameters, unusual binary data in ns.log, and active sessions lacking a matching successful login event.
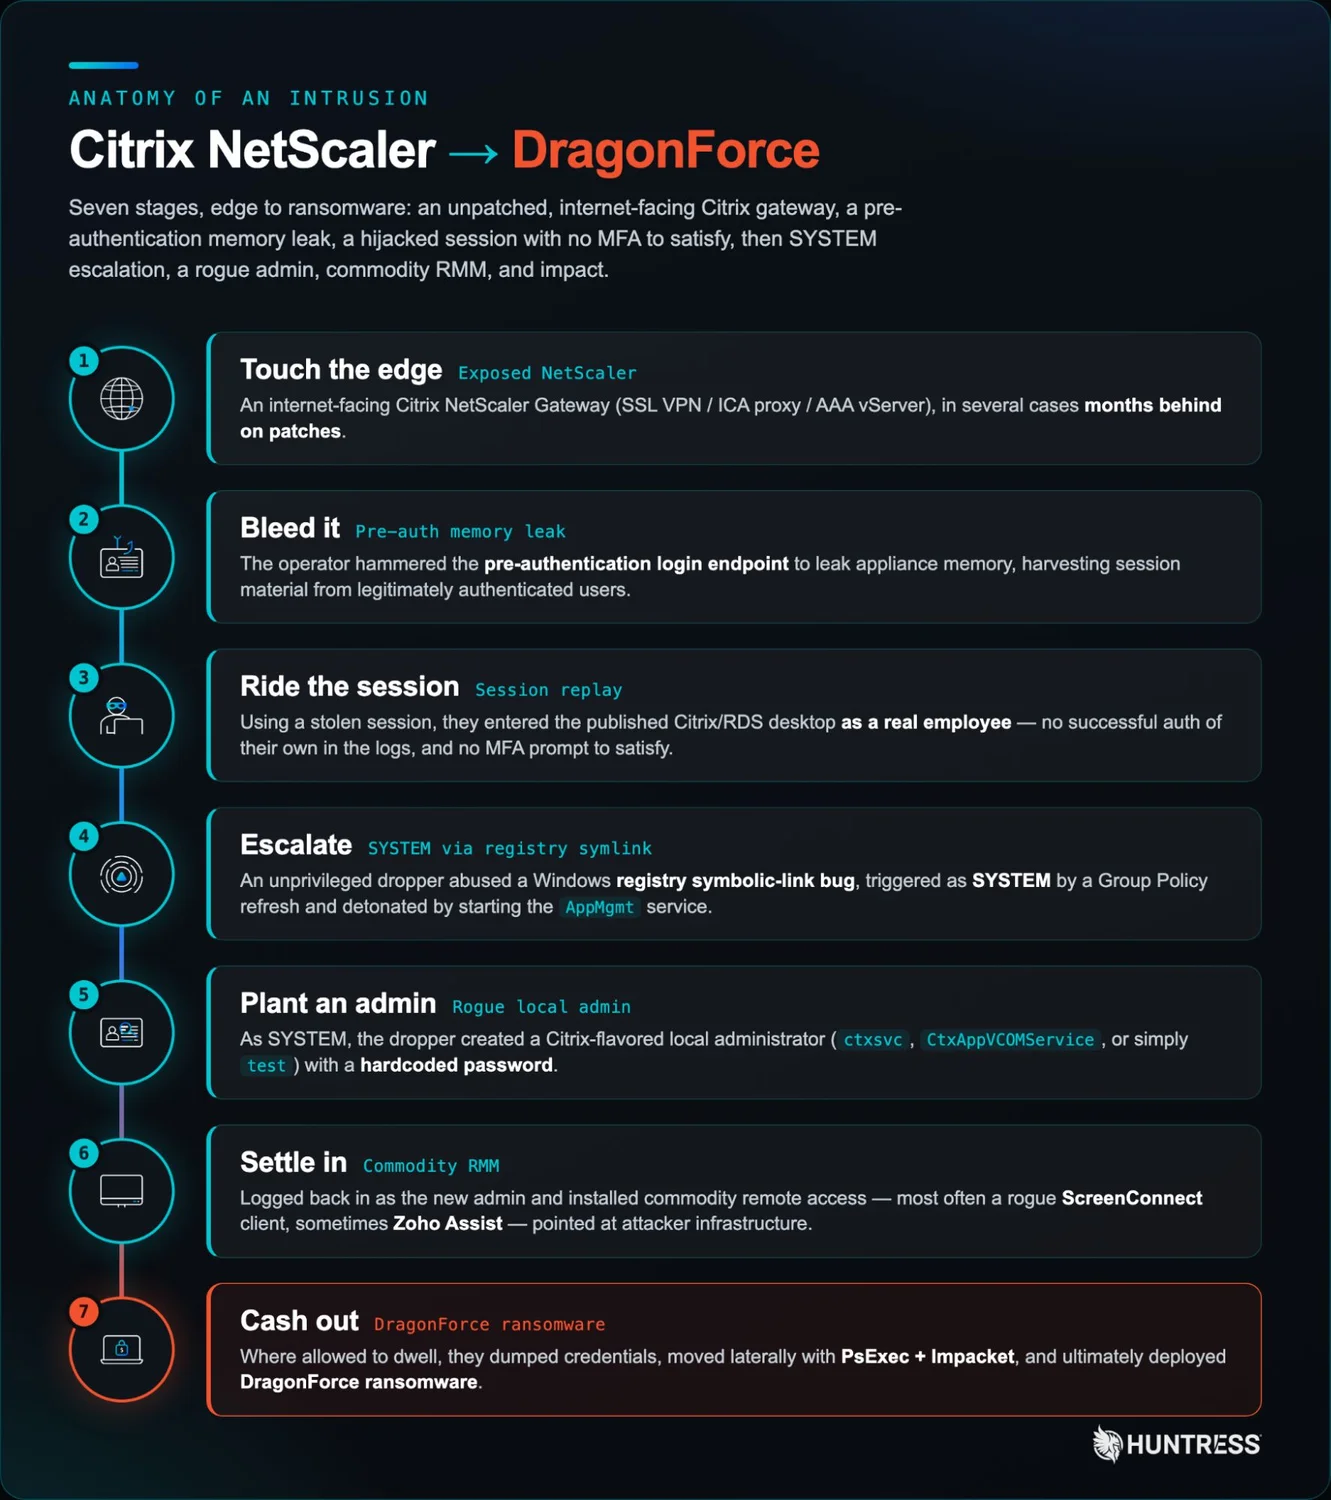
After accessing a Citrix-published desktop, the attackers used a portable local privilege-escalation tool to obtain NT AUTHORITY\SYSTEM.
Huntress most frequently observed ScreenConnect MSI installers configured to connect to attacker-controlled relay servers. Other cases involved Zoho Assist, while an earlier intrusion used NetBird and Atera.
The tool abuses Windows Registry symbolic links and the Application Management service, known as AppMgmt, to redirect privileged Group Policy processing and relaunch the malicious executable in a SYSTEM context.
Attackers then created rogue local administrator accounts, commonly using Citrix-themed names, and installed legitimate remote access software for persistence.
With privileged access established, operators performed interactive RDP access, reconnaissance, PsExec execution, credential dumping, and Impacket-based remote activity against domain infrastructure.
In the most advanced incident, the attackers executed a DragonForce ransomware payload named 1.exe. Rapid response limited encryption to a single host, but the incident demonstrates the ransomware impact linked to this access chain.
Sophos has separately tracked related activity as STAC3725, reporting overlapping tactics involving NetScaler exploitation and ransomware delivery.
While Huntress did not observe QEMU usage in its cases, the overlap reinforces concerns that CitrixBleed 2 is being operationalized by multiple criminal groups.
Organizations should immediately apply Citrix security updates to internet-exposed NetScaler appliances, terminate all outstanding sessions after patching, and preserve gateway logs before they rotate.
Security teams should also review administrator account creation, ScreenConnect or Zoho Assist installations, suspicious AppMgmt service starts, registry modifications, and RDP sessions associated with unfamiliar client hostnames.
Indicators of Compromise (IoCs)
| Indicator | Description |
|---|---|
| ctxsvc | Adversary Account |
| CtxAppVCOMService | Adversary Account |
| test | Adversary Account |
| WIN-4E0AP4JTJR9 | Adversary Hostname |
| WIN-VI960VQI4I6 | Adversary Hostname |
| eng.exe, legal.exe, exsym.exe, as.exe, exp6.exe | LPE Tooling Names |
| Us.msi, SC.msi | ScreenConnect Installers |
| za.msi | Zoho Assist Installer |
| asas.zip, ex.zip, *_update.zip | Password-protected archives from temp[.]sh |
| 1.exe | Dragonforce Ransomware |
| c84739655ce1af0a0269138263d47567418f69e0f75e249f8e23bc21802209e2 | LPE SHA256 |
| eb083365dc70d0294e8c4f55a2e78be0edb0f3497f2a06a70c9f474dafab48d8 | LPE SHA256 |
| c4fcae3847946173bf0b3cedf5d97a9e3d18090023842f942ba544fa7fda180d | DragonForce ransomware SHA256 |
| cmd.exe /c sc start AppMgmt >nul 2>nul | LPE Command Line Emission |
| cmd.exe /c gpupdate /force >nul 2>nul | LPE Command Line Emission |
| relay.dltsolutions[.]top | ScreenConnect Relay |
| relay.eurofin[.]digital | ScreenConnect Relay |
| vpts[.]us | ScreenConnect Relay |
| opa[.]tlsd[.]shop | Netbird Relay |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stop Accepting SLAs Written for 2019 SOCs – Here’s the 2026 AI SLA Vendor Checklist – Download Free AI SOC SLA Guide


