
A sophisticated ClickFix social engineering campaign in May 2026 triggered a full hands-on-keyboard intrusion spanning 11 hosts, deploying a novel trio of malicious tools: Potemkin loader, RMMProject RAT, and EtherRAT.
The attack chain began when the user visited a compromised website and pasted a base64-encoded PowerShell command into Win+R.
This command abused pcalua.exe as a LOLBIN to proxy mshta.exe execution, fetching a remote HTA payload that silently downloaded and installed an MSI package containing Potemkin loader.
Potemkin is a custom x64 Windows loader that uses a deterministic Domain Generation Algorithm (DGA) with seed 151678 to generate 10,000 candidate domains, probing each until finding its command-and-control server.
The loader employes reflectively loaded follow-on modules entirely in memory, avoiding disk writes for its primary payloads.
The module served through Potemkin was RMMProject, a 4.4 MB Lua-scriptable DLL with extensive post-exploitation capabilities.
Huntress researchers documented this multi-stage attack originating from an unmonitored endpoint where a victim was tricked into executing a malicious command via the Windows Run dialog.
This RAT features browser credential theft with a sophisticated Chrome App-Bound Encryption bypass via embedded DLL injection, a hidden-desktop remote control module (RTSC), and 15 distinct task types including password theft (task 1001), cookie stealing (task 1002), and autofill data extraction (task 1013).
ClickFix Attack Deploys Potemkin Loader
The RTSC module creates a hidden Windows desktop where attackers interact with an authenticated browser session invisible to the victim a capability commonly used for banking fraud.
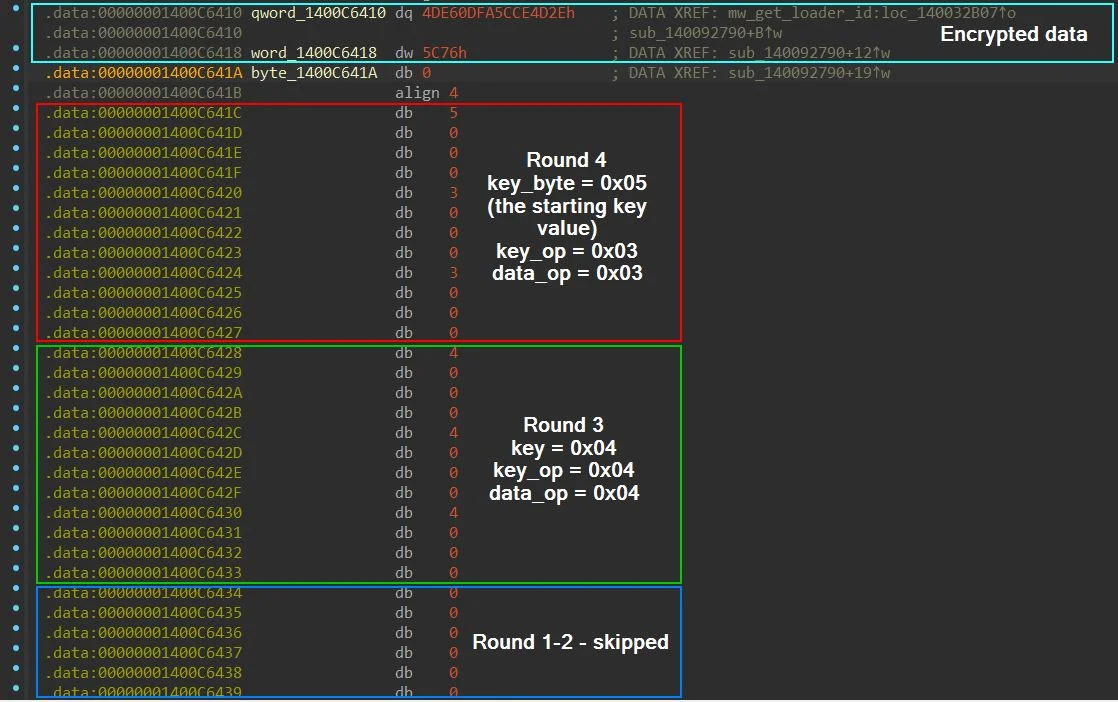
Different strings have different data_op, key_op, and starting key byte values baked into their structs at compile time, so each string has its own unique decryption recipe despite all of them running through the same cipher code.
RMMProject embeds LuaJIT scripting engine and native modules for HTTP client operations, SQLite database access, Windows registry manipulation, and ASN.1 decoding for NSS certificate formats.
Separately, attackers deployed EtherRAT, a known Node.js backdoor that resolves its C2 address from the Ethereum blockchain using EtherHiding evasion.
The RAT reads its C2 from smart contract 0xb3f2897f2bc797e5b9033faef8c81e92b01cb831, issuing eth_call requests across seven public Ethereum RPC providers including Tenderly, Flashbots, and MEV Blocker.
This blockchain-based C2 resolution allows operators to update the botnet’s destination via a single transaction, with every infected host picking up the change on its next poll.
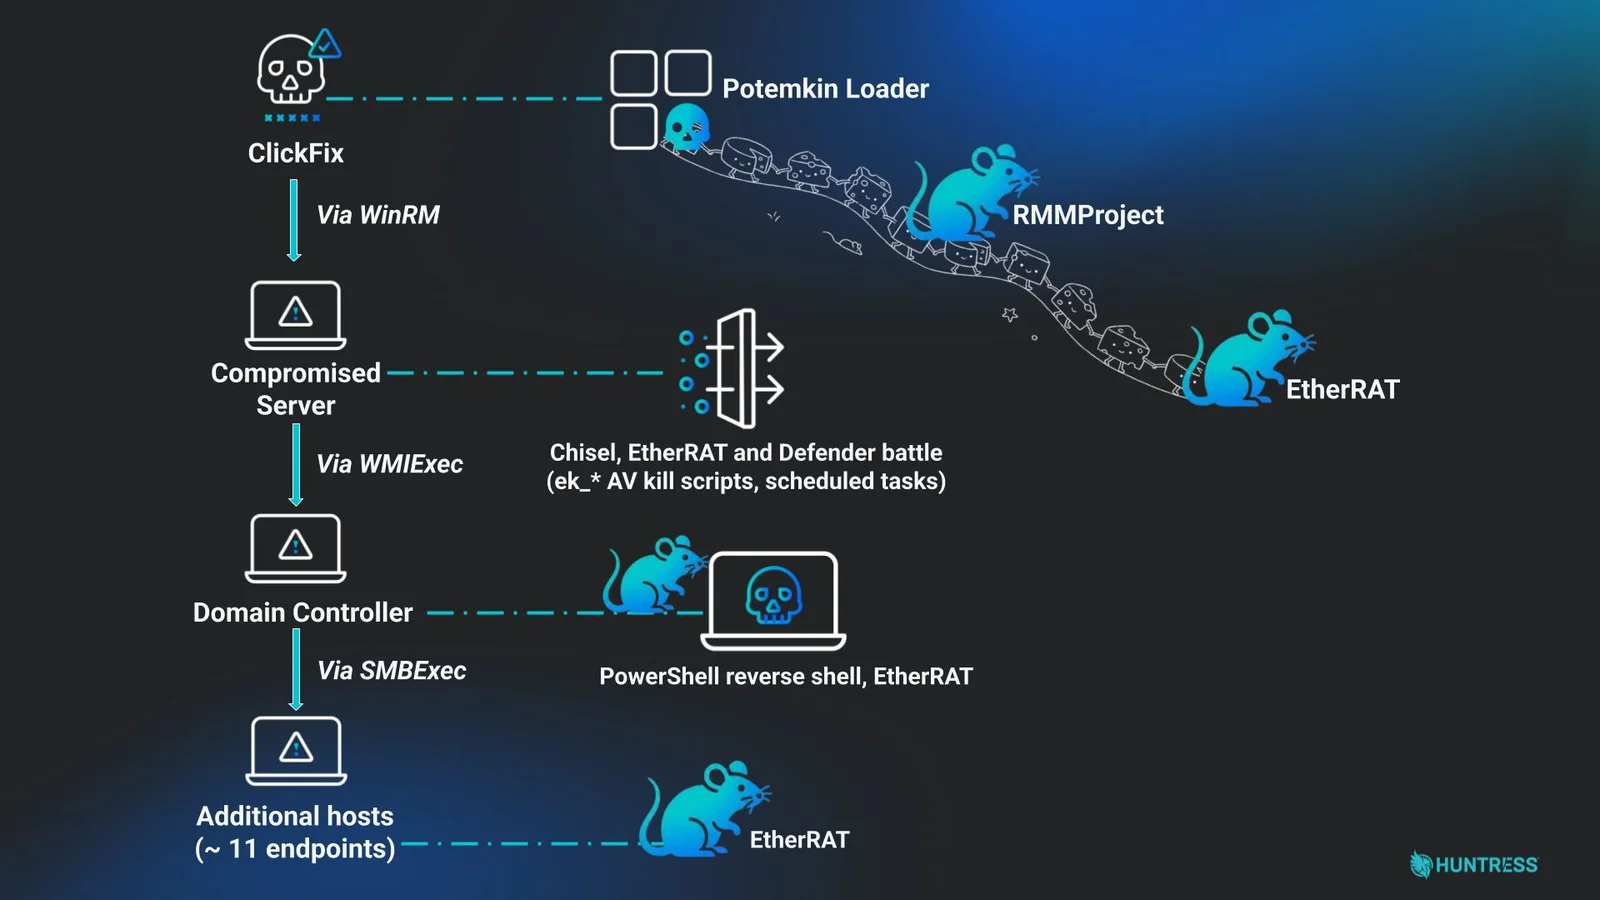
With these footholds established, the operator engaged in sustained hands-on-keyboard activity, fighting Windows Defender while deploying Chisel reverse SOCKS tunnels for lateral movement.
The attacker spread across the network via WMIExec and SMBExec, ultimately reaching the domain controller and spraying EtherRAT across over 11 hosts.
Persistence was maintained through the per-user Run key HKCU\Software\Microsoft\Windows\CurrentVersion\Run under the benign-sounding value WindowsHost, executing Node.js via conhost --headless to suppress console windows.
ClickFix remains effective because it exploits human nature users naturally follow authoritative-looking instructions like “press Win+R, paste this, hit Enter” without questioning.
This case demonstrates why endpoint coverage matters: the initial infection originated from an unmonitored endpoint, giving attackers an unchallenged foothold before lateral movement occurred.
Security experts recommend disabling the Run prompt via Group Policy, blocking unapproved remote management tools, and implementing robust security awareness training.
The campaign targets education and financial sectors through social engineering, utilizing PowerShell commands with DLL side-loading and in-memory execution to evade detection.
Indicators of Compromise (IoCs)
| Indicator | Description |
|---|---|
| RunSearch.exeSHA256: 2abe5dd3a057fdef935722e50e9251c272d29fd26113187b853a1f9a9cb89d9b | Potemkin Loader |
| avast_update.bin SHA256: 3b7ae925e2d64522b4f69b56285b05aeca8c5aab5ab46a9c02c4fafb69d881ce | RMMProject |
| ABE helper DLL SHA256: cd4e5e2c65b1660470d3446539ee68adf5faeece3eaeb46583623be9911ee145 | DLL embedded inside RMMProject. Injected into a spawned Chrome/Edge process to decrypt App-Bound Encryption cookie keys via Chrome’s IElevator COM interface. |
| inst24.msiSHA256: 79f7b67ce8b39070f3e1c2b90fce0ce84134782a7dedcccc1edac197ee9e089b | MSI installer that drops Potemkin loader |
| cons_1.0.1.msiSHA256: 2ada24dd6e517f37942b749c2bd57ddd97445e9853002cee70a0bc30d0b0ce3a | Delivers EtherRAT |
| 77.110.122[.]58 | Primary C2 / staging |
| 213.165.41[.]26 | Chisel reverse SOCKS server |
| C:\Windows\Temp\D0OK1nWwId9W.ps1 | First malicious PS dropped (content unrecovered) |
| C:\Windows\Temp\lQhEQui9a4lZ.exe | Chisel client |
| C:\ProgramData\p\O67tak2KFRmJ.ps1 | In-memory reflective loader |
| C:\ProgramData\p\J6Gupb9TpYNI.ps1 | PowerShell script to download the Chisel client |
| C:\ProgramData\p\fsjH6IHuUkhh.ps1 | AMSI bypass + Defender registry policy disable + reflective Chisel load |
| C:\ProgramData\p\ek_full.ps1 | Registry-based Defender disable script |
| C:\ProgramData\p\ek_kill_av.ps1 | Defender kill: registry policies, Set-MpPreference toggles, and direct service stops of WinDefend, wscsvc, and SecurityHealthService. |
| C:\ProgramData\p\ek_disable_av.ps1 | Defender disable script |
| C:\ProgramData\p\yH88LG8yCOnU.ps1 | Reverse shell: loops a TCP connection to 77.110.122[.]58:43301, bridges it to a hidden powershell.exe process, and reconnects every 30 seconds if the connection drops. |
| 0xb3f2897f2bc797e5b9033faef8c81e92b01cb831 | Ethereum contract |
| 0x40b57c3622c1CbfD699207F71F2dE5A8Fe256893 | Storage key |
| ab653feb-9e78-4578-87ed-2e30329fe858 | EtherRAT build ID |
| sonra.eutialyson[.]com | MSI download domain |
| cl.distritovagas[.]com | ClickFix HTA domain |
| anus-staylard[.]xyz | C2 domain for Potemkin and RMMProject |
| resumeacceptable[.]com | EtherRAT C2 resolved from blockchain |
| %LOCALAPPDATA%\hyper-v.ver | Potemkin UUID file |
| %TEMP%\dll_debug.log | Potemkin debug log |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


