
CloudZ is a new modular remote access trojan that abuses Microsoft’s built‑in Phone Link feature to steal SMS one‑time passwords (OTPs) and other mobile notifications directly from Windows PCs, without infecting the phone itself.
Microsoft Phone Link (formerly “Your Phone”) is integrated into Windows 10 and 11 to mirror smartphone SMS messages, application notifications, call logs and other events from Android or iPhone devices to the desktop over Wi‑Fi and Bluetooth.
The app stores synchronized data, including SMS and notification history, in local SQLite database files such as “PhoneExperiences-*.db” on the Windows machine.
CloudZ uses the custom Pheno plugin to hijack this PC‑to‑phone bridge by continuously scanning for Phone Link‑related processes such as “YourPhone,” “PhoneExperienceHost,” and “Link to Windows.”
Cisco Talos recently detailed an ongoing intrusion active since at least January 2026, in which an unknown attacker deployed CloudZ alongside a previously undocumented plugin named Pheno to harvest credentials and authentication codes from enterprise systems.
Once active sessions are detected, Pheno locates Phone Link’s local database and allows CloudZ operators to potentially intercept SMS‑based OTPs and authenticator app notifications, all without deploying malware to the mobile device.
This effectively turns the trusted sync channel into a stealthy surveillance path for sensitive mobile data.
CloudZ RAT Exploits Microsoft Phone Link
Talos telemetry shows the intrusion begins with an unknown initial access vector that leads victims to run a fake ScreenConnect update executable.
This executable drops and runs a Rust‑compiled 64‑bit loader disguised as “systemupdates.exe” or “Windows-interactive-update.exe,” compiled on January 1, 2026 and containing a developer path string “rustextractor.pdb.”
When executed, the Rust loader decrypts and drops an embedded .NET loader binary masquerading as “update.txt” or “msupdate.txt” under “C:\ProgramData\Microsoft\windosDoc\”.
In some cases, the .NET loader is fetched from attacker‑controlled infrastructure using curl, such as a staging server hosted behind a Cloudflare Workers domain, and saved into the same directory.
The loader then conducts hardware and environment checks to identify virtual machine (VM) or sandbox characteristics.
A PowerShell script then establishes persistence by creating a scheduled task named “SystemWindowsApis” that runs at startup under the SYSTEM account, abusing the regasm.exe LOLBin to launch the .NET loader with high privileges.
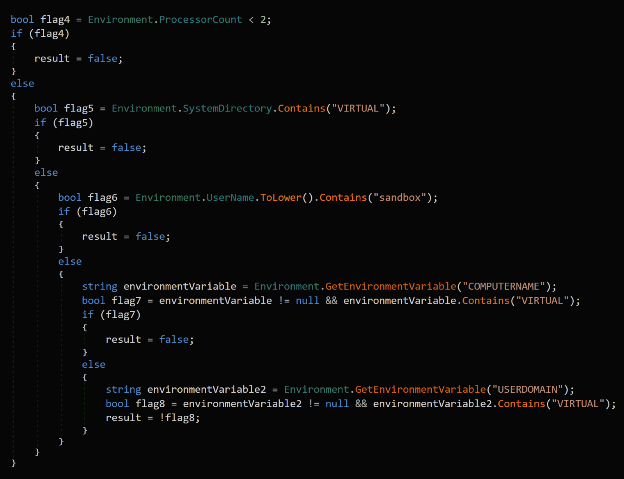
The .NET loader performs multiple anti‑analysis checks, including timing‑based sleep validation, scanning for security tools like Wireshark, Fiddler, Procmon and Sysmon, and inspecting hardware and environment details to detect virtual machines or sandboxes.
It then reconstructs large hexadecimal blobs embedded in the binary, decrypts them with a XOR key, and either reflectively loads .NET assemblies or writes non‑.NET payloads to a temporary directory and executes them.
CloudZ itself is a modular, ConfuserEx‑obfuscated .NET RAT compiled in mid‑January 2026 that decrypts an embedded configuration at runtime and executes key logic dynamically in memory using .NET DynamicMethod and ILGenerator APIs to hinder reverse engineering.
Its configuration defines C2 commands for browser credential theft, file download and management, shell execution, screen recording, and full plugin lifecycle management, including loading, saving and removing plugins such as Pheno.
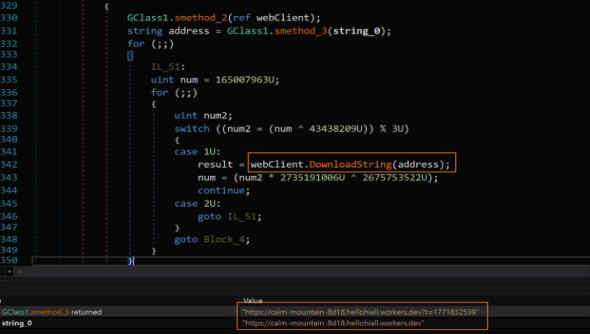
The RAT retrieves secondary configuration from attacker‑controlled staging URLs, extracts the C2 IP address and port, and connects over encrypted TCP sockets while rotating between several hard‑coded browser user‑agent strings and using strict anti‑caching HTTP headers to blend into normal traffic.
Pheno Plugin Reconnaissance
The Pheno plugin focuses on reconnaissance of the Phone Link application on compromised systems.
It scans running processes for Phone Link indicators and writes results, including process IDs and paths, to output files named “phonelink-<COMPUTERNAME>.txt” in staging folders under ProgramData and the user’s temp directory.
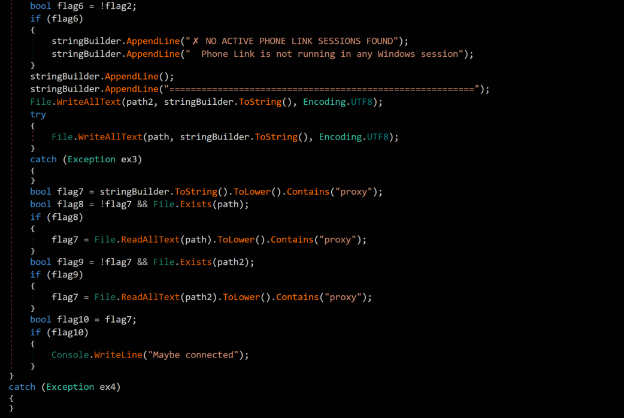
Pheno then re‑reads these logs and searches for the keyword “proxy,” which is associated with the local proxy channel that Phone Link uses to relay traffic between the PC and paired mobile device.
If this keyword is present, Pheno annotates the output with “Maybe connected,” signaling to the attacker that an active PC‑to‑phone relay is likely in use and that Phone Link database files may contain live SMS and OTP traffic.
CloudZ then exfiltrates these logs and related Phone Link artifacts to the C2 server, giving the operator a potential window into users’ authentication flows and other sensitive mobile notifications synchronized to Windows.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


.)