
Microsoft and international partners have disrupted infrastructure supporting CoGUI. This phishing kit Proofpoint says generates more than 100 million malicious emails monthly.
The coordinated action targeted a Chinese-speaking fraud ecosystem encompassing related phishing kits, infrastructure providers, and services enabling credential theft and financial fraud.
Microsoft and Health-ISAC filed a civil lawsuit in the U.S. District Court for the Southern District of Florida against YAM Store operators and individuals linked to the operations.
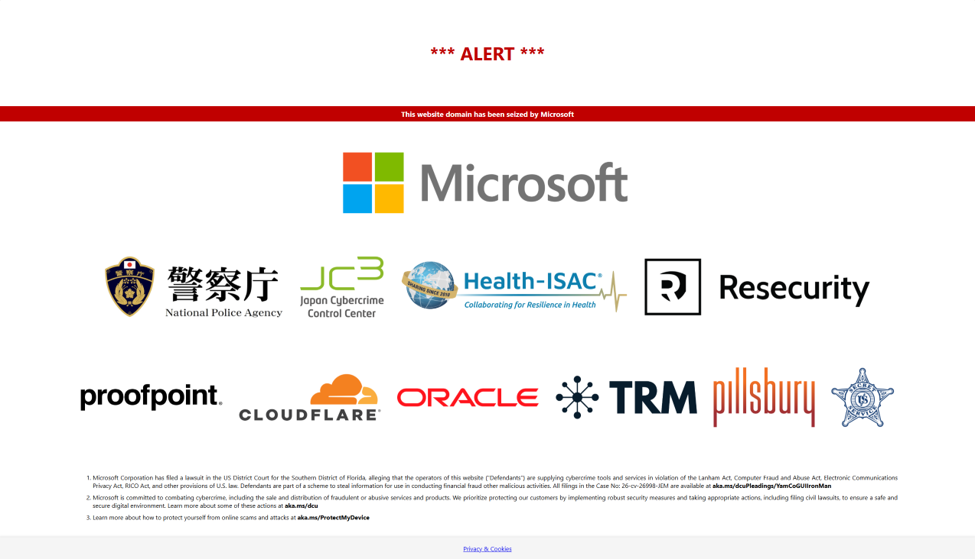
Domains supporting YAM Store, CoGUI, and Iron Man fraud were seized and redirected to seizure notices.
Proofpoint supported the action with malicious-domain intelligence, campaign analysis, and a declaration.
Other participating organizations included Japan Cybercrime Control Center, Resecurity, Cloudflare, Oracle, and TRM Labs.
The disruption extends beyond CoGUI to CoAceV and CoFish_Ws, two closely related kits targeting Japanese organizations.
Proofpoint assesses with high confidence that all three share common roots and overlapping affiliates, based on similarities in targeting, URL structures, and evasion behavior.
According to Microsoft figures cited in the supplied research, YAM Store, CoGUI, and Iron Man collectively enabled more than one billion malicious messages targeting over 75,000 organizations worldwide since January 2026.
Those ecosystem-wide figures should not be confused with Proofpoint’s monthly CoGUI detection volume.
Proofpoint recorded 1,081 CoGUI campaigns using 13,586 unique domains, compared with 242 CoAceV campaigns across 2,812 domains and 19 CoFish_Ws campaigns across 191 domains.
Across the three kits, researchers observed approximately 17,000 unique domains.
Between July 1 and September 17, 2026, the kits used 3,788 unique fully qualified domain names, demonstrating sustained infrastructure rotation and substantial operational resources.
Proofpoint Researchers identified that, 66 impersonated brands, including Amazon, Apple, PayPay, Rakuten, SMBC, JCB, and Yamato Transport.
CoGUI Phishing Kit
Email themes span account verification, payment problems, banking notifications, retail transactions, and shipping updates.
Embedded links direct recipients through filtering mechanisms, including CAPTCHA challenges, before displaying counterfeit authentication or payment portals. These pages harvest usernames, passwords, and credit card information.
Proofpoint’s original CoGUI investigation, published in May 2025, documented geofencing, browser fingerprinting, and header-based filtering.
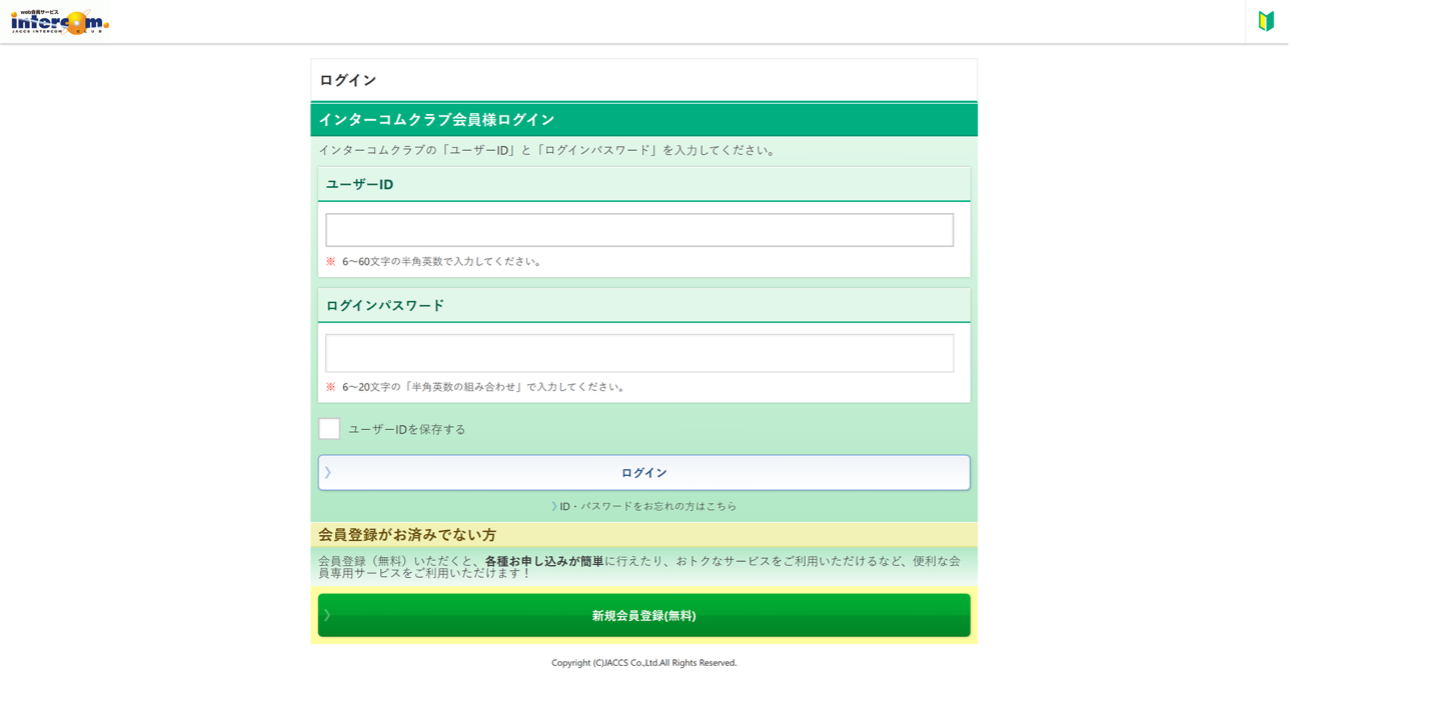
The kit evaluates attributes including geographic location, browser language, operating system, and screen dimensions before deciding whether to serve phishing content or redirect visitors elsewhere.
The newer research describes shared decoy behavior emerging in February 2026, when CoGUI and subsequently CoAceV redirected unsuitable visitors to identical alternative destinations.
Matching URL paths and distinctive patterns spanning all three kits further support their assessed relationship.
Japan accounts for most tracked activity, with smaller numbers of campaigns affecting the United States, Australia, and Italy.
Financial services and healthcare are the most frequently affected sectors, followed by government, education, and manufacturing.
Japan’s Financial Services Agency warning describes stolen brokerage credentials enabling unauthorized share sales and purchases of domestic and foreign small-cap stocks.
However, that warning does not establish direct attribution to CoGUI; Proofpoint previously characterized the connection as possible rather than confirmed.
The seizures are expected to impose operational, financial, and reputational costs, but their lasting effect remains unmeasured.
Frequent domain replacement demonstrates why infrastructure disruption alone cannot establish eradication.
Defenders should retain layered phishing detection and prioritize phishing-resistant authentication.
Japan’s regulator recommends passkeys where available, bookmarked brokerage websites, transaction monitoring, and immediate contact with providers following suspected compromise.
These measures address the account-takeover objective that remains relevant even when individual phishing domains disappear.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.