

Cacti, the widely utilized network monitoring tool, has recently issued a critical security update to address a series of vulnerabilities, with the most severe being CVE-2024-25641.
This particular vulnerability has been assigned a high severity rating with a CVSS score of 9.1, indicating its potential impact on affected systems.
Free Webinar on Live API Attack Simulation: Book Your Seat | Start protecting your APIs from hackers
CVE-2024-25641– Critical RCE Vulnerability
CVE-2024-25641 allows authenticated users with the “Import Templates” permission to execute arbitrary PHP code on the server hosting the Cacti application.
The vulnerability stems from improper sanitization and validating file names and content within uploaded XML data in the import_package() function.
This flaw could lead to arbitrary file writes on the web server. Security researcher Egidio Romano has demonstrated the exploitability of this vulnerability through a proof-of-concept PHP script.
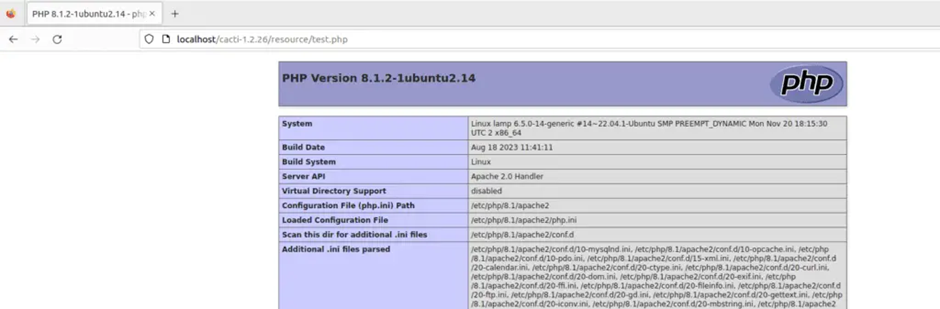
This script showcases how attackers can easily manipulate the import process to inject and execute malicious code, thereby gaining unauthorized access to the system.
Additional Vulnerabilities and Fixes
In addition to CVE-2024-25641, the latest Cacti update addresses several other security issues:
- CVE-2024-34340 (CVSS 4.2): An authentication bypass issue due to older password hashes, potentially allowing unauthorized access.
- CVE-2024-31443 (CVSS 5.7) and CVE-2024-27082 (CVSS 7.6): These vulnerabilities relate to XSS flaws that could enable attackers to inject client-side scripts into web pages and manipulate sessions.
- CVE-2024-31444, CVE-2024-31458, CVE-2024-31460, and CVE-2024-31445 (ranging from CVSS 4.6 to 8.8): A series of SQL injection flaws that could allow attackers to alter the framework’s database queries, leading to unauthorized data manipulation or access.
- CVE-2024-31459: An RCE vulnerability linked to file inclusion via plugins, which could allow the execution of arbitrary code.
- CVE-2024-29894: An XSS vulnerability in the JavaScript-based messaging API exploitable for executing malicious scripts.
These vulnerabilities vary in severity, with potential impacts ranging from cross-site scripting (XSS) attacks to SQL injection and arbitrary code execution.
With technical details and proof-of-concept code for these vulnerabilities now public, the urgency for Cacti users to update their systems cannot be overstated.
All platform users are strongly encouraged to upgrade to version 1.2.27 or later as soon as possible to mitigate the risks associated with these vulnerabilities.
The release of these patches highlights the ongoing challenges and the critical importance of maintaining up-to-date security practices in network monitoring tools like Cacti.
Users must remain vigilant and proactive in applying security updates to protect their networks from potential threats.
On-Demand Webinar to Secure the Top 3 SME Attack Vectors: Watch for Free


%20(2).webp?fit=1600,900&ssl=1&description=Cacti, the widely utilized network monitoring tool, has recently issued a critical security update to address a series of vulnerabilities.)