
Aurora ransomware operators have been observed using Cursor Agent, powered by Claude Sonnet, to support hands-on intrusion activity across ten victim organizations, while deploying a purpose-built Linux encryptor designed to disrupt VMware ESXi environments.
The findings show how ransomware affiliates are integrating agentic AI into established post-compromise workflows rather than relying on it as a standalone attack capability.
The exposed environment provided visibility into the actor’s tooling, attack workflow, and an ESXi-capable ransomware sample named encrypt.out, with SHA-256 a4af136d159a8eb96b54924fa80355ca52874913301300f55af7d67ae97edcfe.
Between April 8 and May 21, 2026, the Aurora operator used Cursor Agent with claude-4.5-sonnet-thinking in multiple victim environments.
The actor supplied the agent with valid credentials or an existing route, including SOCKS-based access, then instructed it to carry out reconnaissance, privilege assessment, internal scanning, and exploitation tasks.
The recovered sessions indicate that the operator used AI as an iterative technical assistant. In some cases, the attacker asked broad questions, such as identifying a user’s effective privileges.
In others, the operator directed the agent to use specific offensive tools or follow a prebuilt attack plan.
The agent often needed multiple command revisions before a task succeeded, underscoring that the human operator remained in control of execution and decision-making.
Observed tasks included deploying VPN clients and ProxyChains, scanning internal networks with Nmap and NetExec, collecting Active Directory information with BloodHound.
Attempting NTLM relay attacks with PetitPotam, Coerce Plus and PrinterBug, and conducting Active Directory Certificate Services attacks through Certipy.
The operator repeatedly instructed the AI not to perform DCSync, avoid account lockouts, and refrain from adding computer objects to the domain operational constraints apparently intended to reduce detection risk and prevent disruptive changes before encryption.
Aurora’s Linux payload was hosted on Cloudflare R2 and manually copied to internal victim hosts. The malware encrypts data in place using ChaCha20 and encrypts each session key with an embedded RSA-4096 public key.
Its command-line options support partial encryption, file-size limits, worker-thread control, folder targeting, and a dedicated -esxi mode.
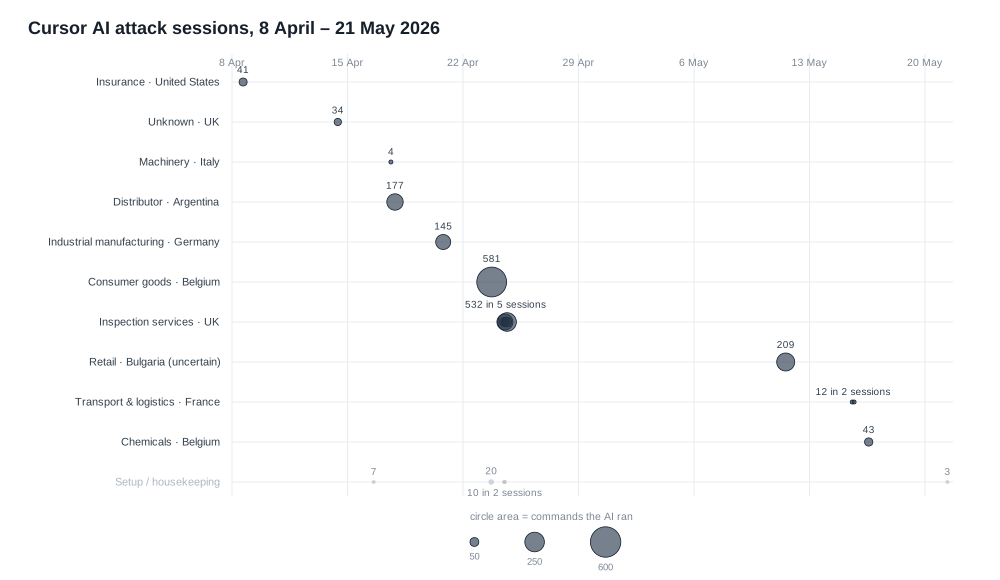
Gambit Security’s Threat Intelligence team uncovered Cursor, exposed infrastructure linked to the Aurora operation, which has been active since about April 2026 and operates a public data-leak site.
Cursor AI-Powered Ransomware
When executed with the ESXi option, encrypt.out runs esxcli vm process list to enumerate active guest virtual machines and obtain their World IDs.
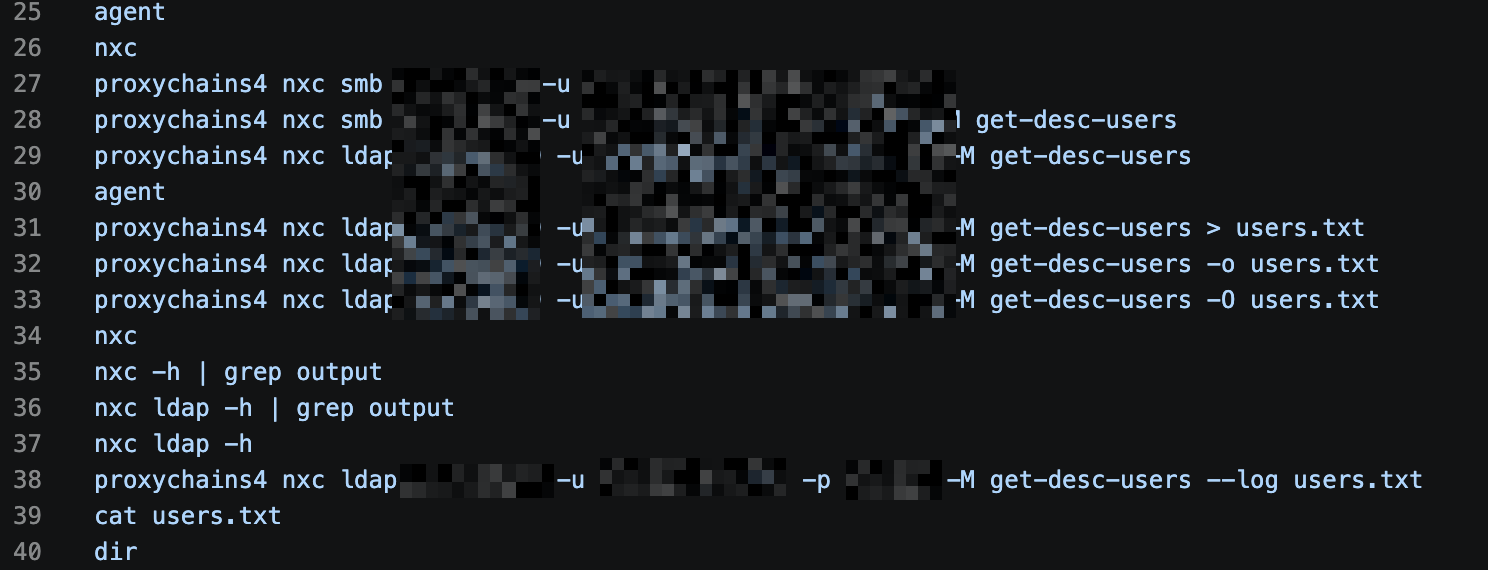
NetExec driven LDAP and SMB discovery, password policy retrieval, ASREPRoasting, Kerberoasting the same sequence, the same output file naming convention, every time.
It then force-terminates each guest through esxcli vm process kill –type=force –world-id=<world-id>, releasing locks on virtual disk files before encrypting them. Targeted files include VMDK, VMX, VMSD, VMSN, NVRAM, VMEM, VSWP and log files.
Notably, the malware avoids ESXi system volumes such as BOOTBANK* and OSDATA*. That choice leaves the hypervisor bootable, enabling administrators to access the host and encounter the extortion demand after the virtual machines have been taken offline.
Aurora writes the ransom message to /etc/ssh/sshd-banner, presenting it to administrators before the SSH login prompt.
The group also used esxi_finder.py, a custom NetExec LDAP module, to discover ESXi and vCenter infrastructure.
The module identifies internal subnets through Active Directory or an operator-provided range list, scans ports 443 and 902, examines TLS certificates for ESXi signatures, and queries /sdk, /ui/, and root paths to fingerprint the VMware product and determine exact build versions.
Separate research by CloudSEK linked an exposed directory to a Russian-speaking Aurora affiliate active against more than 20 organizations across nine countries from April through July.
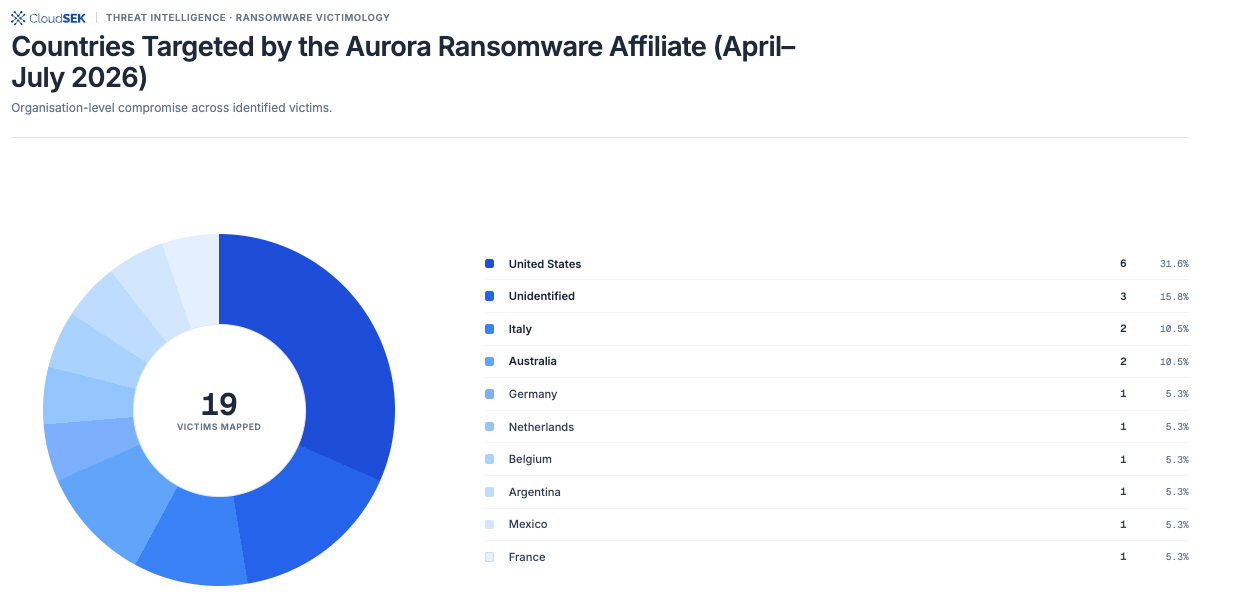
The directory held credential material, Kerberos tickets, shell history, Cursor chat logs, custom NetExec modules, and Windows and Linux Aurora lockers compiled from a shared Zig codebase. Four recorded victims later appeared on Aurora’s leak site.
CloudSEK and TRM Labs also traced a settled victim payment through shared laundering infrastructure, identifying two confirmed Aurora victim payments and two additional flows consistent with separate victims.
The evidence supports the assessment that the actor operated as a direct ransomware affiliate, progressing from access and domain compromise to data theft, encryption, and extortion rather than simply brokering network access.
The campaign highlights the need to treat ESXi platforms, Active Directory Certificate Services, backup infrastructure, and remote administration paths as high-priority ransomware exposure points.
Organizations should isolate management networks, restrict SSH and ESXi access, monitor esxcli vm process kill activity, enforce SMB signing and Extended Protection for Authentication, and audit AD CS templates for ESC1, ESC6, and ESC8 misconfigurations.
Aurora’s operational model also reinforces a broader concern: AI agents can lower the time and skill required for iterative post-exploitation, but they do not eliminate the need for stolen credentials, valid access paths, and traditional offensive tooling.
In this case, the AI component accelerated an already mature ransomware workflow built around Active Directory compromise, lateral movement, data theft, and virtualization-layer disruption.
IOCs
| Type | IOC | Note |
|---|---|---|
| IP | 172.86.113.245 | c2 |
| IP | 172.86.90.75 | c2 |
| IP | 89.106.83.49 | SOCKS proxy |
| IP | 104.194.134.167 | SOCKS proxy |
| IP | 68.210.224.231 | SOCKS proxy |
| Indicator | Type | Value |
|---|---|---|
| Aurora Tor Negotiation Site | Onion Address | ijexszhscln27nl263lmcd7tx3jttkhm4wjhd4e3y6r4csdbfyeprvid.onion |
| sap.exe (Windows locker) | SHA-256 | eb0aab1e892d7e09e2c7bcf1d21fd83c1743ed9196b3efac6c78482fb0d99207 |
| encrypt.out (Linux/ESXi locker) | SHA-256 | a4af136d159a8eb96b54924fa80355ca52874913301300f55af7d67ae97edcfe |
| Ransom Note | Filename | !!!README!!!DO_NOT_DELETE.txt |
| Operator VPS | IPv4 | 172.86.113.245 |
| Operator VPS | IPv4 | 172.86.90.75 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide




