

Recently, the attackers hacked a number of Cisco Systems servers using the Cisco Virtual Internet Routing Lab Personal Edition (VIRL-PE) platform; it’s a service that allows users to create and test network topologies (the consortium of the elements of a network) without installing the device.
In this attack, the cybercriminals have exploited the critical vulnerabilities in the SaltStack Salt open-source framework.
It is widely used for automation services, as well as in the implementation of data center systems management.
According to Cisco experts, the Cisco Modeling Labs Corporate Edition (CML) is also vulnerable to attacks because it includes a version of SaltStack that runs the vulnerable Salt Master (“master”) installation.
In general, CML allows users to simulate Cisco devices and third-party devices. At the same time, the VIRL-PE enables the users to design and test virtual networks in a development and testing environment, as we told earlier.
Vulnerable Products
To make it more clear, here are the products that are affected by these vulnerabilities:-
- Cisco Modeling Labs Corporate Edition (CML)
- Cisco Virtual Internet Routing Lab Personal Edition (VIRL-PE)
Servers That Were Compromised
According to the company, the cyber attackers have managed to compromise six server infrastructure, and here they are:-
- us-1.virl.info
- us-2.virl.info
- us-3.virl.info
- us-4.virl.info
- vsm-us-1.virl.info
- vsm-us-2.virl.info
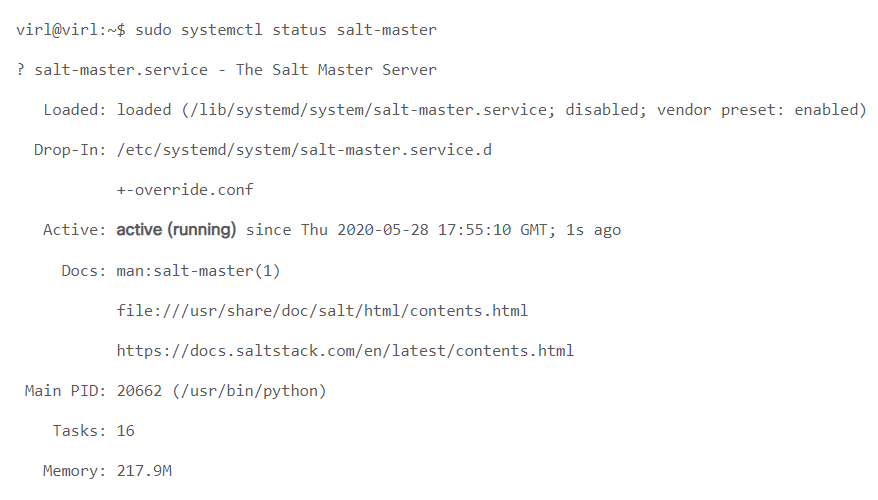
From the image that we have mentioned below, you can see the example that shows a device where the salt-master service is enabled:-
Security Flaws
The vulnerabilities correspond to an authentication bypass that is identified as CVE-2020-11651, and a directory traversal that is identified as CVE-2020-11652.
Collectively, these two flaws can allow the attackers to gain unauthorized access to the entire file system of the servers that are configured in SaltStack.
- CVE-2020-11651: Authentication Bypass Vulnerability
- CVE-2020-11652: Directory Traversal Vulnerability
Moreover, Cisco updated the compromised servers on May 7, 2020, and applied all the necessary patches that address authentication bypass vulnerabilities (CVE-2020-11651) and directory traversal vulnerabilities (CVE-2020-11652) that affect SaltStack servers.
Cisco has released two essential updates for the VIRL-PE services and related product Cisco Modeling Labs Corporate Edition. Apart from this, the security experts point out that without the updates, any version of both services could remain vulnerable to these security flaws.
The SaltStack Salt is meant to observe and update the servers, as it’s an automation and remote execution engine, that allows its users to run commands on multiple systems utilizing the master node that applies the changes to target servers.
Apart from this, Cisco is not the first and only company that was attacked by the attackers using these flaws, as earlier the attackers have also attacked other popular companies as well using these security flaws.
Ghost reported that hackers hacked their servers and infected their systems with bitcoin mining malware using these security flaws in early May.
Not only that, even Xen-Orchestra have also reported that they have suffered from the same problem. However, we strongly recommend you all to update your devices immediately with the latest security patch released by Cisco to stay secure.
So, what do you think about this? Share all your views and thoughts in the comment section below.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.





 platform)