
DarkBlinders has compromised a high-profile Israeli individual associated with the security sector and a government cloud environment in Iraqi Kurdistan, combining credential phishing, a fake meeting application, and GitHub-based backdoors.
Dream Security observed the cyberespionage campaign between August and October 2026 and reported that it remained active at publication.
Confirmed activity included credential theft and the exfiltration of at least 1 GB from the government environment.
The operation extends the activity behind Unit 42’s previously documented Blinder Tunnel campaign.
Attackers used government webmail, cloud-drive, and meeting-service impersonation to establish access, then reviewed infected systems before selectively deploying a second-stage implant.
This selectivity separated initial infections from systems chosen for operational exploitation.
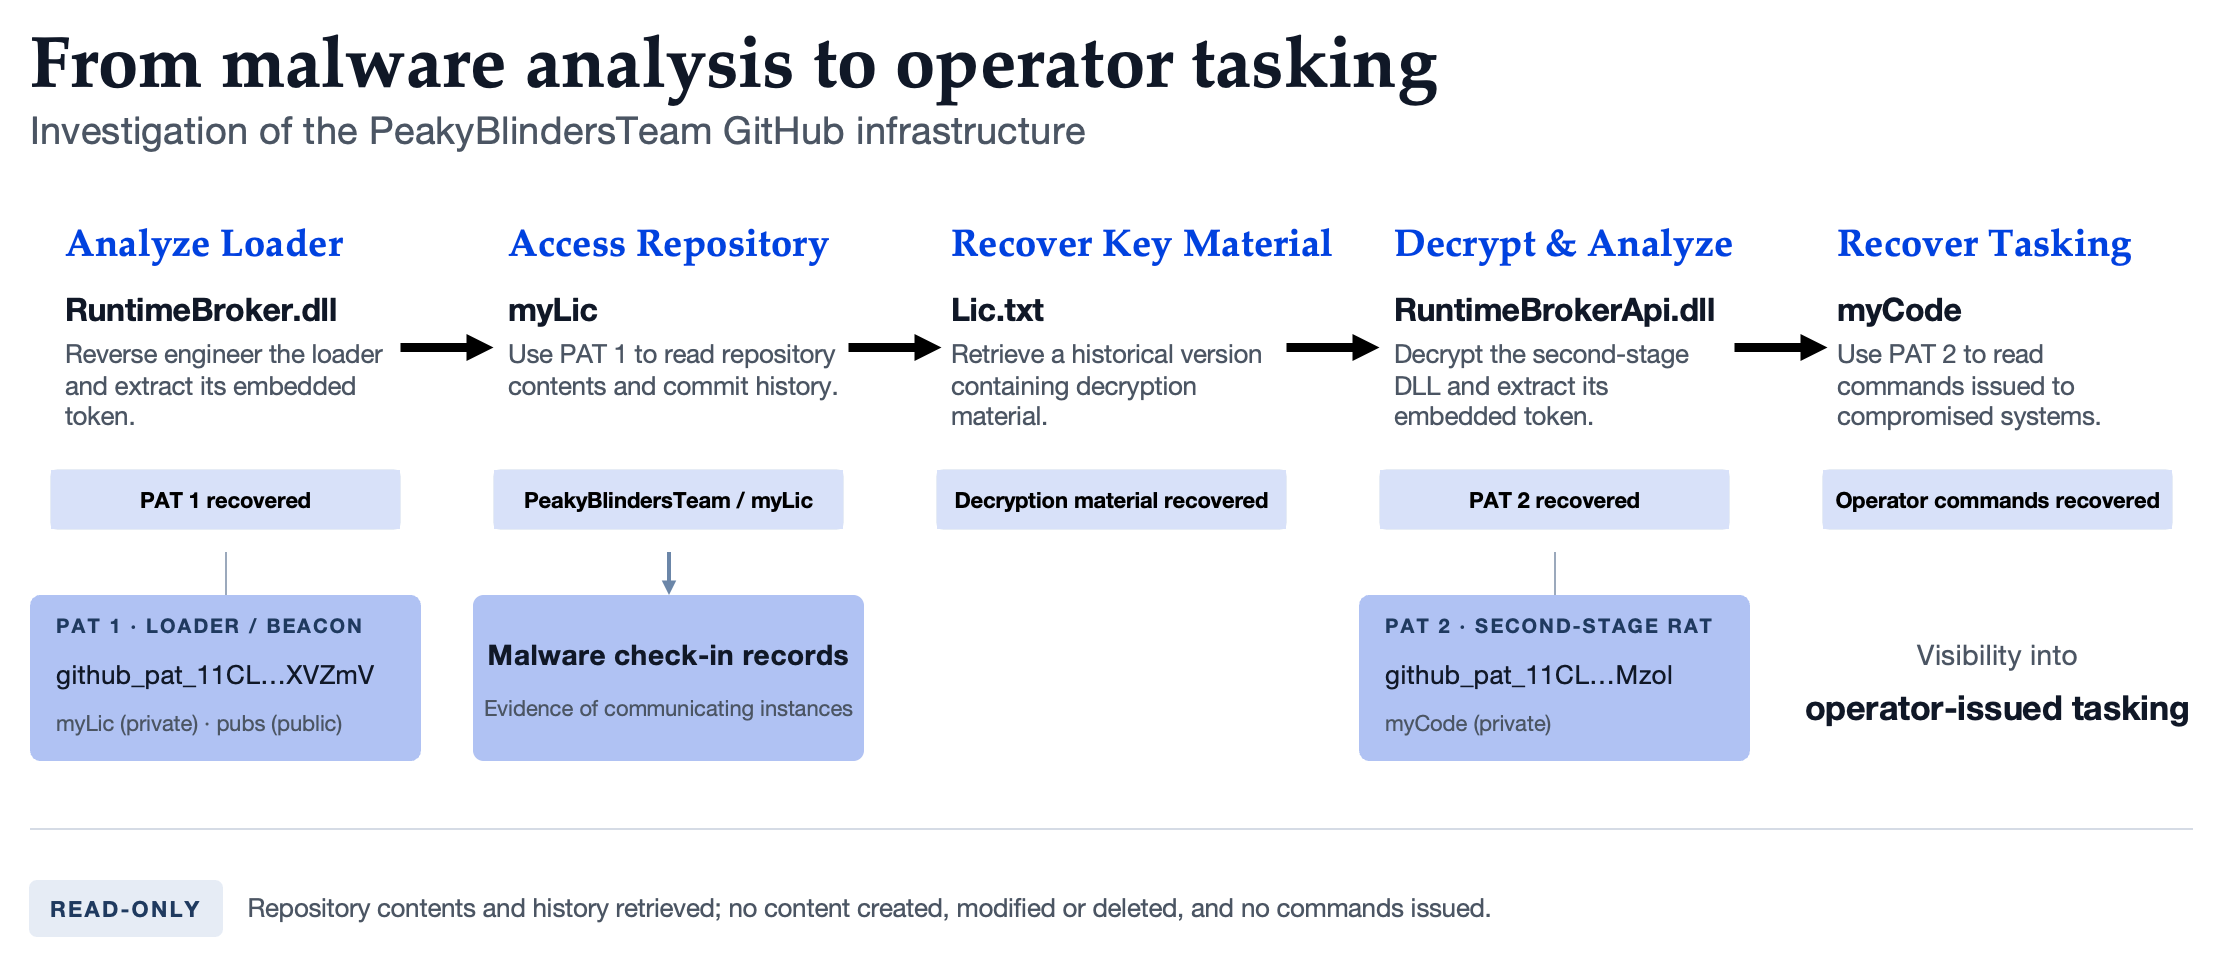
Its interface offered local camera, microphone, and screen-sharing previews, but joining a meeting always returned a fixed connection error.
Researchers found no networking or payload-deployment functionality within the decoy application itself.
Instead, the installer placed separate malicious components under %LOCALAPPDATA%\Microsoft\RuntimeBroker.
A legitimate, signed vshost.exe, renamed RuntimeBroker.exe, loaded RuntimeBroker.dll through an AppDomainManager-based mechanism.
Persistence relied on the MicrosoftRuntime value in the current user’s Run registry key, allowing the malicious branch to survive removal of the visible application.
Dream Security observed that, StarkMeet masqueraded as a video-meeting application, using an unsigned Inno Setup installer labeled version 3.2.
DarkBlinders APT Attack
Parallel phishing pages impersonated Kuwait’s Ministry of Foreign Affairs and the Gulf Cooperation Council Secretariat General.
Outlook Web App lookalikes harvested credentials, while Google Drive-style pages encouraged downloads of attacker-controlled archives.
The original message delivering StarkMeet.zip was not recovered, leaving its precise delivery route unconfirmed.
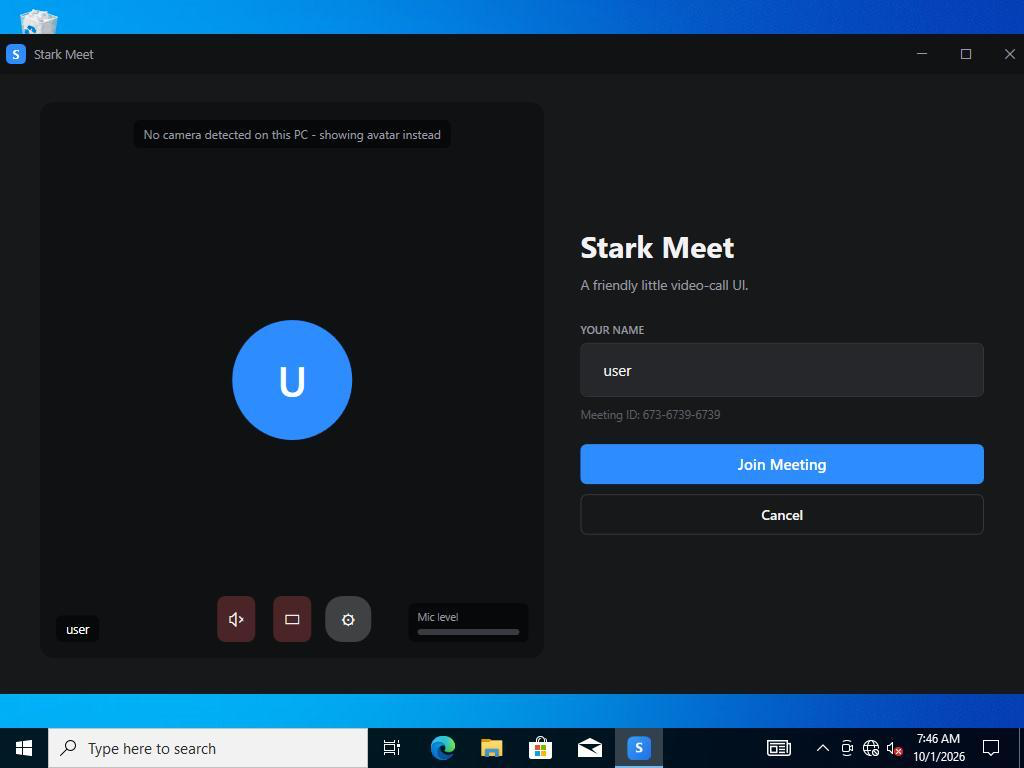
The loader used an embedded GitHub personal access token to register victims in the PeakyBlindersTeam/myLic repository.
Reports exposed usernames, domains, keyboard layouts, persistence status, and anti-analysis findings. These checks informed operator decisions rather than automatically terminating execution.
Approximately ten hosts registered, but researchers identified only two victims in the second-stage tasking repository. Selected systems received host-specific activation material that unlocked RuntimeBrokerApi.dll.
The loader derived an AES-256-CBC key from the license string’s SHA-256 hash and used the first 16 key bytes as the initialization vector.
The decrypted assembly ran directly in memory and communicated through myCode, polling for commands approximately every 63 seconds.
An embedded PsProxy.dll executed PowerShell through System.Management.Automation runspaces without launching powershell.exe, reducing visibility for detections dependent on that child process.
Additional commands supported file uploads, downloads, and ZIP extraction.
An hourly recovery mechanism searched public Microsoft/vscode issues for encrypted configuration hidden inside comments.
Valid instructions could replace repository ownership, repository names, and tokens, providing a recovery path when primary credentials failed.
Dream recovered historical license material from GitHub commit history, decrypted the payload, and examined operator tasking through strictly read-only access.
Dream assessed medium-to-high confidence that DarkBlinders overlaps with UNC5795 and Dust Specter, while assigning medium confidence to possible relationships with UNC5187 within APT34.
Separately, Unit 42’s Blinder Tunnel research documented fake Dubai Airports recruitment lures and GitHub API abuse, reinforcing the broader pattern of disguising espionage communications as routine cloud traffic across targeted Middle Eastern enterprise networks.
IOCs
| Domain | Description | Target or role |
|---|---|---|
gcc-sg[.]cloud | GCC Secretariat General cloud and webmail lure | GCC and Gulf diplomacy |
gcc-sg[.]online | GCC Secretariat General webmail lure | GCC and Gulf diplomacy |
mfakuwait[.]org | Kuwait Foreign Affairs Outlook phishing | Kuwait |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.


