Sunday, October 18, 2026

DarkGate, Which Abused Microsoft Teams, Now Leverages MSI Files

A new wave of cyberattacks has been discovered by Netskope Threat Labs, involving the use of SharePoint as a delivery platform for the notorious DarkGate malware. 

This alarming trend is driven by an attack campaign that exploits vulnerabilities in Microsoft Teams and SharePoint, posing a serious risk to online security.

DarkGate: A Versatile Threat

DarkGate, also known as MehCrypter, emerged in the cybersecurity scene in 2018. 

Since then, it has become a popular choice among cybercriminals due to its versatile feature set, including HVNC (Hidden VNC), keylogging, information theft, and the ability to download and execute additional payloads. 

This malware variant has been involved in multiple campaigns in the past few months, making it a persistent and evolving threat.

Document
FREE Webinar

Webinar on Cyber Resilience for Financial Sector

Ensure your Cyber Resiliance with the recent wave of cyber-attacks targeting the financial services sector. Almost 60% respondents not confident to recover fully from a cyber attack.

The Infection Path

The recent DarkGate variant detected by Netskope Threat Labs follows a clever infection path. 

It begins with a phishing email, masquerading as a fake invoice containing a PDF document. 

Once opened, the PDF prompts the user to review a document, initiating the download of a CAB file. 
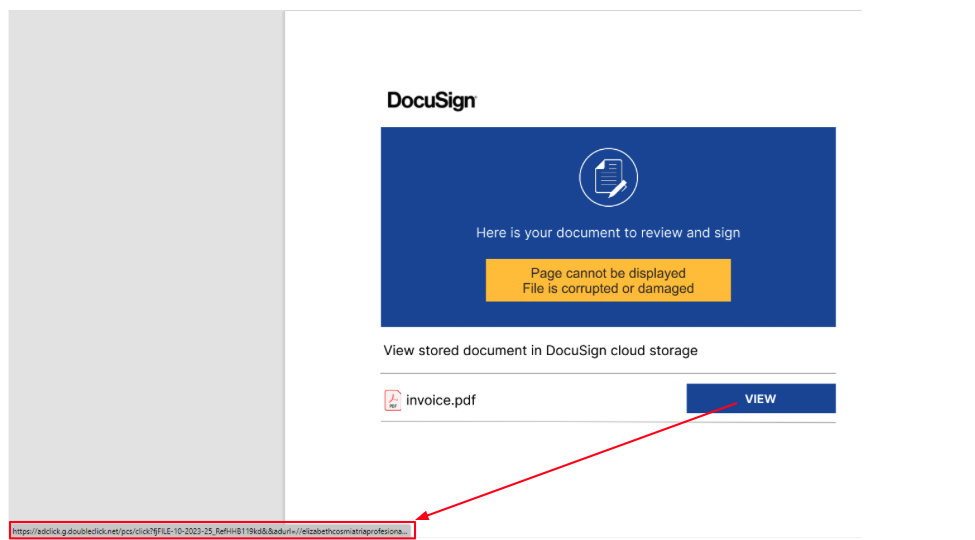
Example of the malicious document sent to the victim

Within this file lies an internet shortcut leading to the download of an MSI file, the entry point for DarkGate’s infiltration.
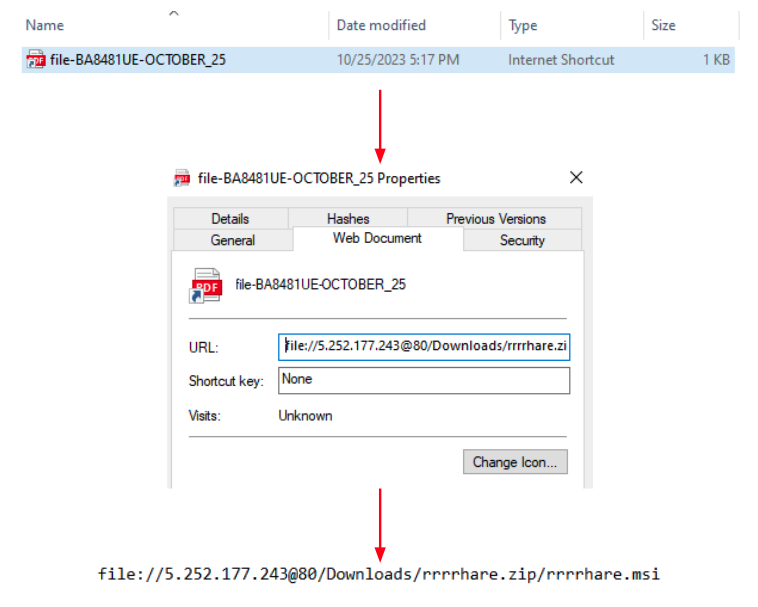
Once the MSI file is executed, a complex chain of loading techniques is triggered. 

DarkGate uses DLL side-loading techniques, hiding its presence by executing a fake version of the dbgeng.dll DLL file. 

This DLL, written in Delphi programming language, facilitates the execution of malicious payloads while avoiding detection.

Multiple Layers of Evasion

The malware’s evasion techniques are not limited to a single layer. 

DarkGate’s multi-stage loading process involves the use of AutoIt scripts, further concealing its intentions. 

These scripts construct a PE (Portable Executable) file, executing it through a callback function, adding another layer of complexity to its operation.

Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


