

CloudSEK’s STRIKE team has uncovered a sophisticated cryptocurrency theft operation orchestrated by the threat actor “RedLineCyber,” who deliberately impersonates the notorious RedLine Solutions to establish credibility within underground communities.
Rather than collecting comprehensive system data, the malware employs a highly targeted approach: continuously monitoring the Windows clipboard for cryptocurrency wallet addresses and performing silent substitution with attacker-controlled addresses at the precise moment users attempt to paste them.
This surgical technique dramatically increases attack effectiveness while maintaining a minimal detection profile.
The threat actor exploits trust relationships within Discord communities focused on gaming, gambling, and cryptocurrency streaming.
Through extensive human intelligence operations conducted in December 2025, researchers identified a targeted campaign leveraging Discord communities to distribute Pro.exe, a Python-based clipboard-hijacking trojan designed specifically to substitute real-time cryptocurrency addresses during user transactions.
Distribution occurs through direct social engineering, where RedLineCyber cultivates relationships with potential victims particularly cryptocurrency streamers and influencers over extended periods before introducing the malicious payload as a “clipboard protection tool” or “streaming utility.”
Intelligence gathering revealed eight primary Discord communities actively targeted, including servers dedicated to crypto streaming platforms and gaming broadcasts where high-frequency cryptocurrency transactions occur.
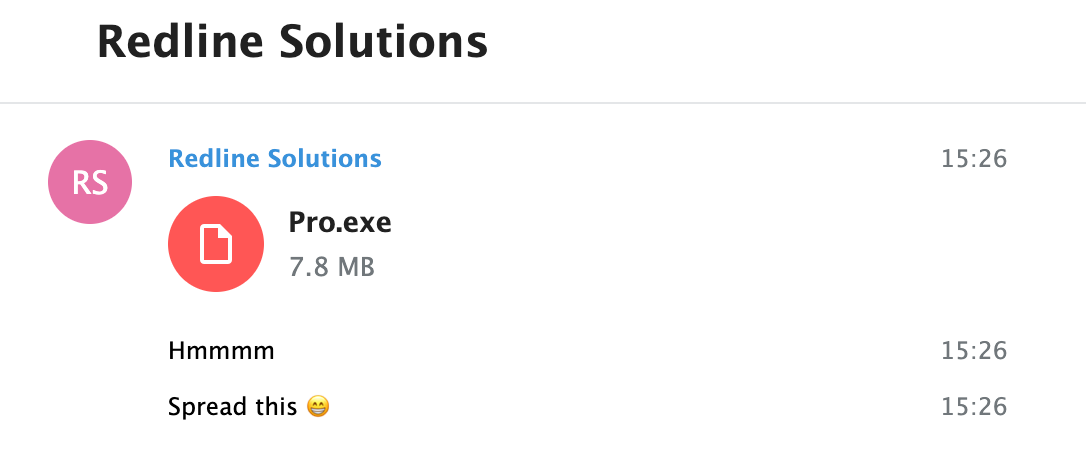
This community-focused approach proves highly effective. The fast-paced nature of streaming and gambling environments creates conditions where users are susceptible to social engineering, and the shared focus on cryptocurrency transactions identifies communities where clipboard hijacking delivers maximum financial impact.
Technical Architecture
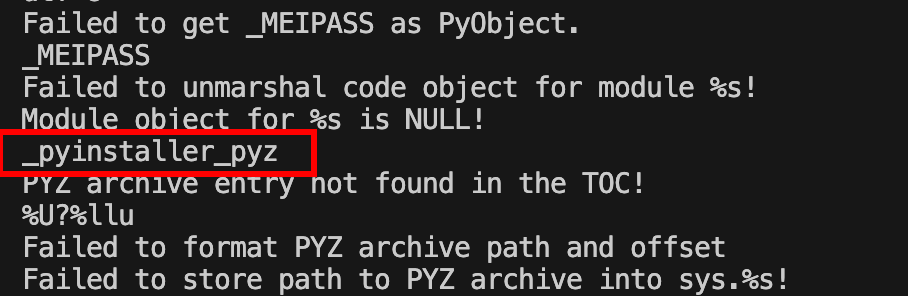
Despite its practical design, Pro.exe demonstrates moderate technical sophistication. The malware is packaged as a PyInstaller executable containing obfuscated Python 3.13 bytecode, uses base64-encoded regular expressions for wallet detection, and implements basic persistence through Windows Registry Run keys.
Upon execution, the malware creates a %APPDATA%\CryptoClipboardGuard\ directory and establishes an autostart entry, ensuring continuous clipboard monitoring across system restarts.
The monitoring mechanism operates on a 300-millisecond polling cycle approximately three checks per second enabling near-real-time detection while maintaining low CPU utilization to avoid performance-based security alerts.
When new clipboard content is detected, base64-encoded regex patterns identify wallet addresses across six cryptocurrency formats, as shown in the table below:
| Cryptocurrency | Address Pattern | Detection Method |
|---|---|---|
| Bitcoin (BTC) | bc1[a-zA-Z0-9]{39,59} | SegWit format matching |
| Ethereum (ETH) | 0x[a-fA-F0-9]{40} | Hex-encoded address format |
| Solana (SOL) | [1-9A-HJ-NP-Za-km-z]{32,44} | Base58 encoding validation |
| Dogecoin (DOGE) | D[5-9A-HJ-NP-U][1-9A-HJ-NP-Za-km-z]{32} | Prefixed base58 format |
| Litecoin (LTC) | ltc1[a-zA-Z0-9]{39,59} | Bech32 format matching |
| Tron (TRX) | T[A-Za-z1-9]{33} | T-prefix base58 format |
Upon successful wallet address detection, the malware overwrites the clipboard with corresponding attacker-controlled addresses and maintains logs within activity.log, enabling the threat actor to track successful infections and monitor theft effectiveness.
Evasion and Attribution
The malware’s narrow operational focus clipboard monitoring without network communication or data exfiltration allows it to maintain an exceptionally low detection profile.
VirusTotal analysis shows 34 of 69 antivirus vendors flagging the sample, with detection classifications ranging from Trojan.ClipBanker to Trojan-Banker.Win32.ClipBanker.
Notably, the malware implements no command-and-control infrastructure, eliminating network-based detection vectors entirely.
Blockchain analysis of embedded attacker-controlled wallets reveals successful compromise and financial theft from multiple victims, with RedLineCyber maintaining separate wallets for each cryptocurrency to capture transactions across multiple blockchain networks.
Open-source intelligence correlation identified RedLineCyber advertising over 4,200 stolen LinkedIn credentials on the BreachStars marketplace in October 2025, suggesting a diversified criminal operation combining real-time cryptocurrency theft with traditional credential harvesting.
Indicators of Compromise (IOCs)
| Indicator Type | Value | Context |
|---|---|---|
| SHA-256 | 0d6e83e240e41013a5ab6dfd847c689447755e8b162215866d7390c793694dc6 | Primary sample (Pro.exe / peeek.exe) |
| SHA-256 | d011068781cfba0955258505dbe7e5c7d3d0b955e7f7640d2f1019d425278087 | Related ClipBanker variant observed in the wild |
| File Path | %APPDATA%\CryptoClipboardGuard\activity.log | Clipboard swap activity log with timestamps |
| Directory | %APPDATA%\CryptoClipboardGuard\ | Persistence directory created by malware |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.







