

Botnets are the networks of compromised devices that have evolved significantly since the internet’s inception. Threat actors exploit vulnerabilities to control these devices remotely by leveraging them for malicious activities.
These activities range from spamming to launching devastating distributed denial-of-service (DDoS) attacks, as the decentralized nature of botnets presents significant challenges to defenders.
By orchestrating attacks from numerous compromised devices, threat actors overwhelm targets and mask their origin by making it difficult to identify and block the source of the attack.
Malicious botnets orchestrate a wide range of cyberattacks and launch devastating DDoS attacks by crippling targets with overwhelming traffic. They spearhead spam and phishing campaigns by flooding inboxes and exploiting vulnerabilities for data theft.
The operations of credential stuffing and data theft are automated, which allows for the exploitation of weak credentials and the exfiltration of sensitive information.
Investigate Real-World Malicious Links & Phishing Attacks With Threat Intelligence Lookup - Try for Free
Cryptojacking leverages compromised devices for illicit cryptocurrency mining. Botnets also serve as proxies, masking attacker origins, and perpetrating click fraud that generates fraudulent ad revenue.
A late November malspam campaign impersonated DHL by distributing malicious zip files disguised as freight invoices. The emails that featured consistent filenames like “Invoice 123.zip” or “Tracking 456.zip” enticed recipients to open the attachments.
This triggered a malware infection that could potentially lead to data exfiltration, system compromise, or other malicious activities. Analysis of tens of thousands of these spam emails revealed a sophisticated and potentially widespread attack.
The JavaScript file is obfuscated and designed to download and execute a PowerShell script that establishes an outbound connection to a malicious command and control (C2) server hosted on 62.133.60[.]137, which is an IP address associated with Global Connectivity Solutions (AS215540).
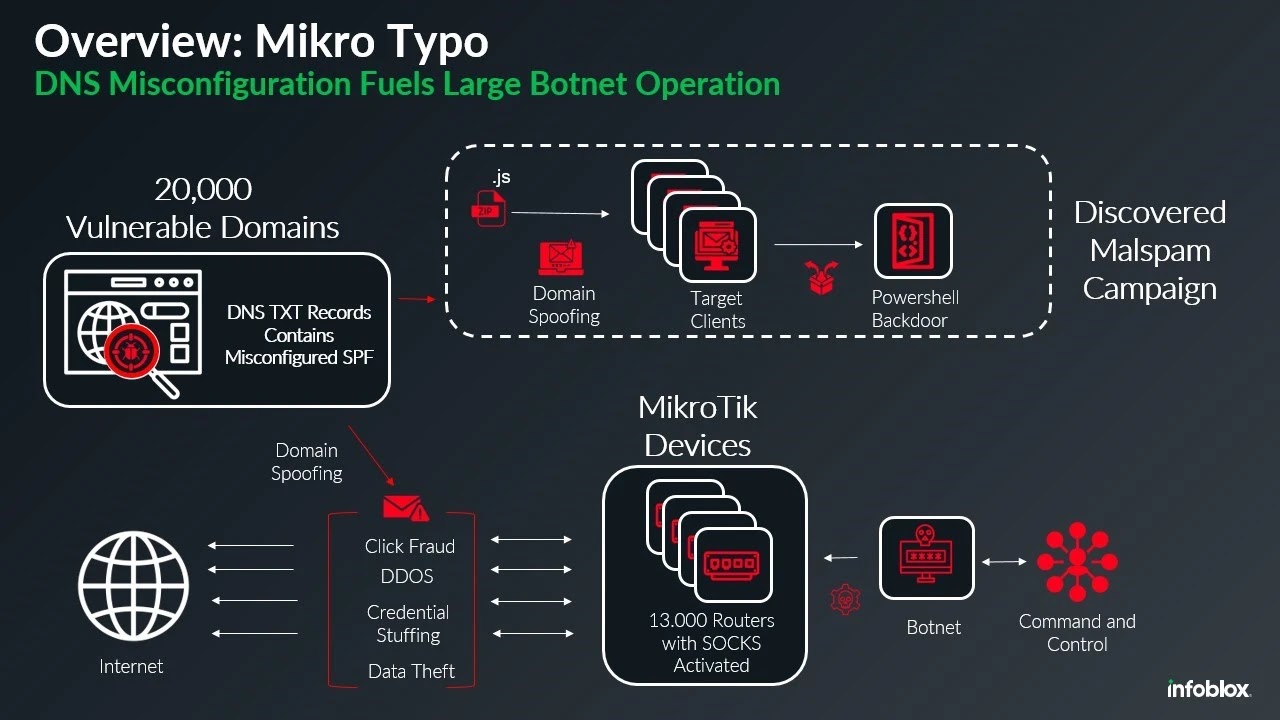
The botnet leverages a vulnerability in routers that likely exploits a previously known flaw to gain remote access. An actor installs a script on each compromised device by turning it into a SOCKS proxy.
It allows other malicious actors to leverage the botnet for various malicious activities, including DDoS attacks, data exfiltration, phishing campaigns, and malware distribution.
According to Infoblox, the widespread use of these proxies significantly amplifies the botnet’s impact by masking the origin of attacks and providing anonymity to the attackers.
A misconfiguration in the SPF records of domains allowed malspam actors to bypass the email security measures—that is, a DNS record that identifies the authorized servers to send emails for a domain.
A properly configured SPF record specifies the authorized servers and rejects emails from unauthorized servers.
However, the misconfigured SPF record included ‘+all’ at the end which allowed any server to send emails on behalf of the domain and defeats the purpose of the SPF record.
The malspam campaign leveraged over 13,000 compromised MikroTik devices functioning as SOCKS4 relays to send spoofed emails from 20,000 domains. By exploiting misconfigured DNS SPF records, the threat actors bypassed email protections.
It highlights the critical need for robust security measures, including regular audits of device accessibility and proper DNS configurations and to mitigate the risks posed by this evolving botnet that can facilitate various malicious activities beyond malspam.
Integrating Application Security into Your CI/CD Workflows Using Jenkins & Jira -> Free Webinar






