

DragonForce is a ransomware group that emerged in late 2023 and has grown into a serious threat to businesses by combining data theft with file encryption.
The group uses dual extortion: it steals sensitive data, encrypts systems, and then threatens to publish the stolen information on dark web leak sites if victims do not pay.
DragonForce has targeted multiple sectors, with a notable focus on manufacturing and construction, and it has impacted high-profile organizations.
The group has also shown it can adapt quickly by refining its tooling and shifting from dedicated victim sites to a centralized domain for hosting leaked data.
Cybereason notes this rapid evolution helps keep DragonForce a persistent, growing risk worldwide.
RaaS platform and features
DragonForce operates as a ransomware-as-a-service (RaaS) platform that helps affiliates run attacks across Windows, Linux, ESXi, BSD, and NAS systems.
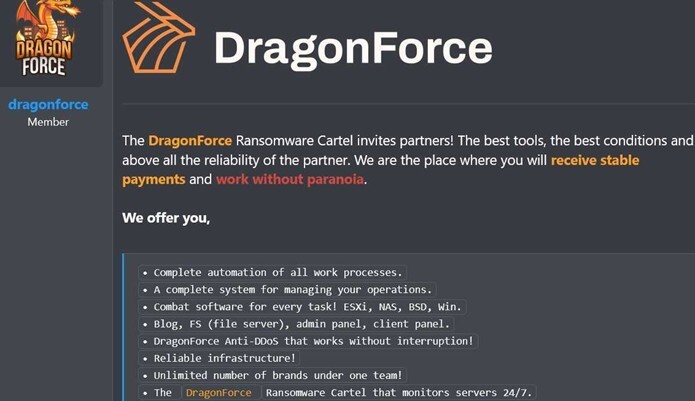
The platform supports multiple encryption approaches (full, header, and partial encryption) and promotes automation for encryption, server management, and attack execution.
Reported features include delayed-start options, multithreading for speed, detailed logging, and a “dry-run” mode that tests an attack flow without actually encrypting data.
For ESXi environments, Cybereason highlights command-line and configuration options that control targeting and behavior, including file-system search modes, delay timers, thread counts, logging settings, and allows for paths, extensions, filenames, and virtual machines.
These controls can help affiliates tailor impact (for example, prioritizing VM infrastructure) while reducing noisy failures that slow down ransomware deployment.
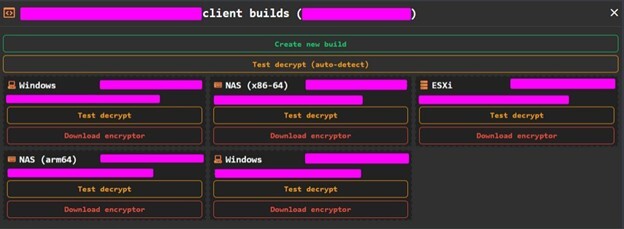
DragonForce has announced a strategic shift: affiliates can create their own brands under a “DragonForce ransomware cartel” umbrella and run their own projects while still using shared infrastructure and experience.
The group also introduced an automated registration service for new affiliates, reducing prior friction like approval steps, deposits, and vetting.
DragonForce has teased an upcoming product called “DragonForce – Atom,” but did not publish technical details in the cited analysis.
The same reporting describes ecosystem “professionalization,” including a “Company Data Audit” service intended to strengthen extortion by analyzing stolen data and producing negotiation materials like risk reports, call scripts, and executive-facing letters.
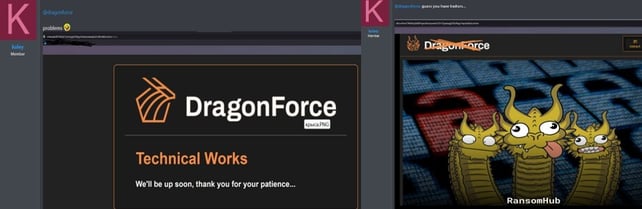
DragonForce has also engaged in public disputes with other ransomware operations, including claims and counterclaims involving RansomHub and the defacement of a competitor’s leak site.
Cybereason further notes claims of a relationship between DragonForce Malaysia and the ransomware group remain unsubstantiated, and DragonForce Malaysia publicly denied affiliation in October 2025.
What defenders should do
Cybereason observed behaviors aligned with real-world ransomware playbooks, including scanning SMB ports for reconnaissance and deleting Volume Shadow Copies using WMIC (for example, wmic.exe shadowcopy where “ID='{id}'” delete).
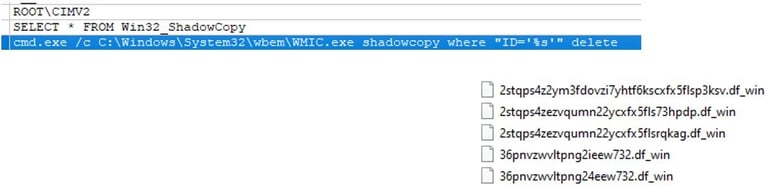
The analysis states the Cybereason platform detected the DragonForce payload and blocked shadow-copy deletion and file encryption activity.
Practical steps recommended include hunting for DragonForce affiliate pre-ransomware behavior, enforcing MFA, maintaining strong patch management, and ensuring reliable backups and tested restore processes.
If suspicious activity is found, the guidance advises quickly involving Incident Response to investigate, contain, and remove the threat actor.
For Cybereason Defense Platform users, the report recommends enabling Anti-Malware, Anti-Ransomware (PRP) with shadow copy protection, Application Control, and Variant Payload Prevention in prevent mode.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





