

LinkedIn messages were used as a way to launch identity theft attacks in a malicious campaign that Cluster25 detected.
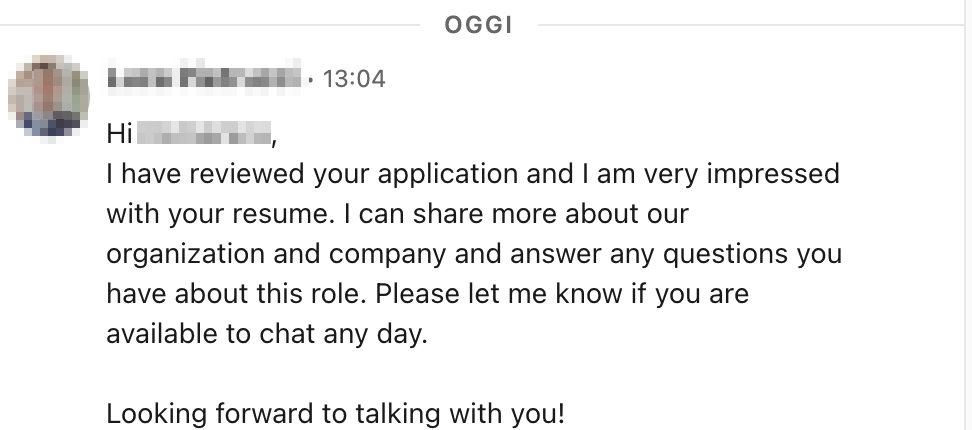
They send messages from hacked accounts with PDF files that look like job offers. But these files have links to dangerous websites that can steal your data.
Cluster25 is a cybersecurity firm that specializes in threat intelligence and incident response. They discovered this campaign by analyzing the malicious domains and URLs used by the attackers.
The hackers are using a type of malware called DuckTail, which can also take over your Facebook Business account.
They are mainly targeting people who work in sales and finance in Italy.
How the Scam Works
The hackers send you a message from a hacked LinkedIn account with a PDF file with a job offer. For example, they might offer you a Senior Manager position at Electronic Arts (EA).
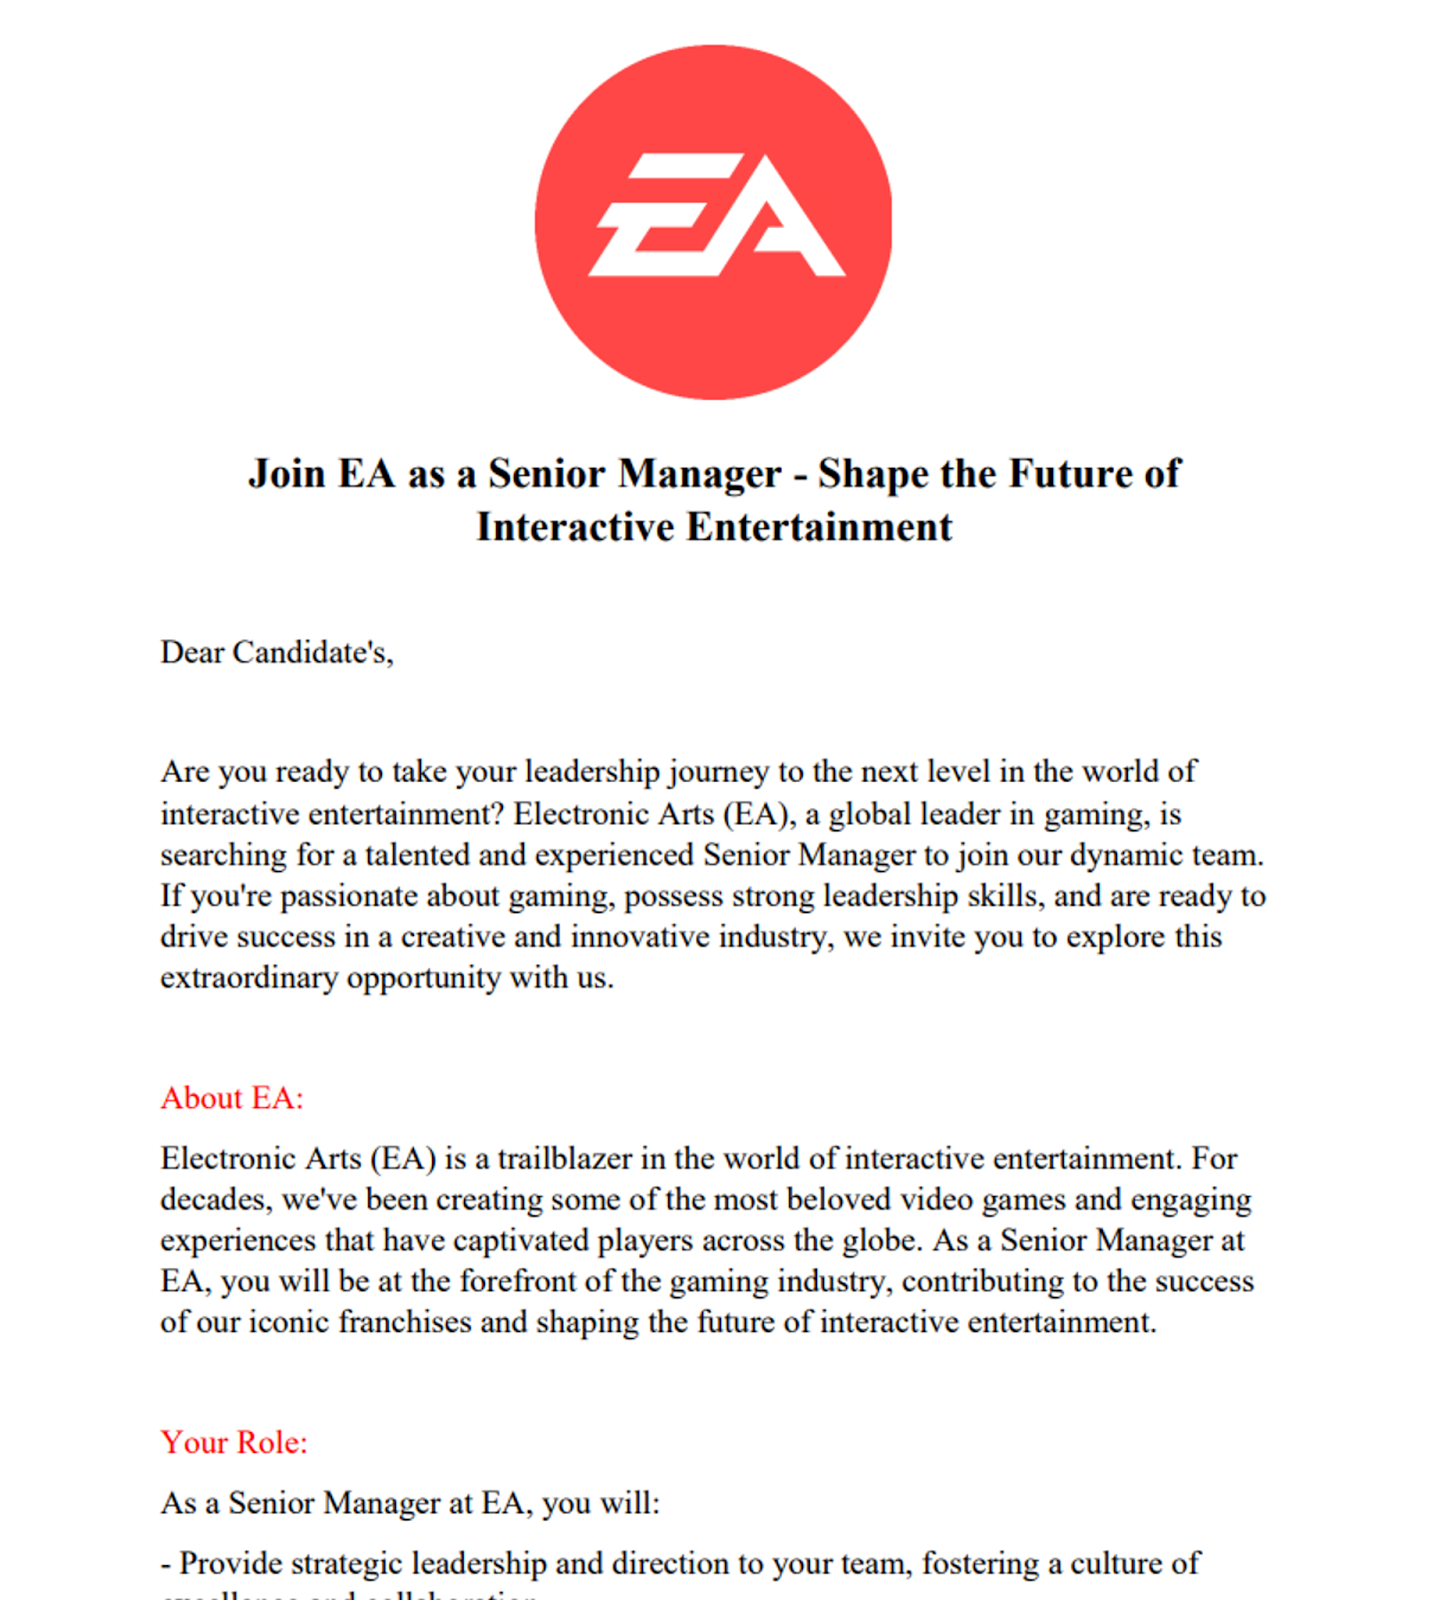
The PDF file has two links. One link takes you to a fake website that looks like EA’s website. It asks you to upload your resume and cover letter.
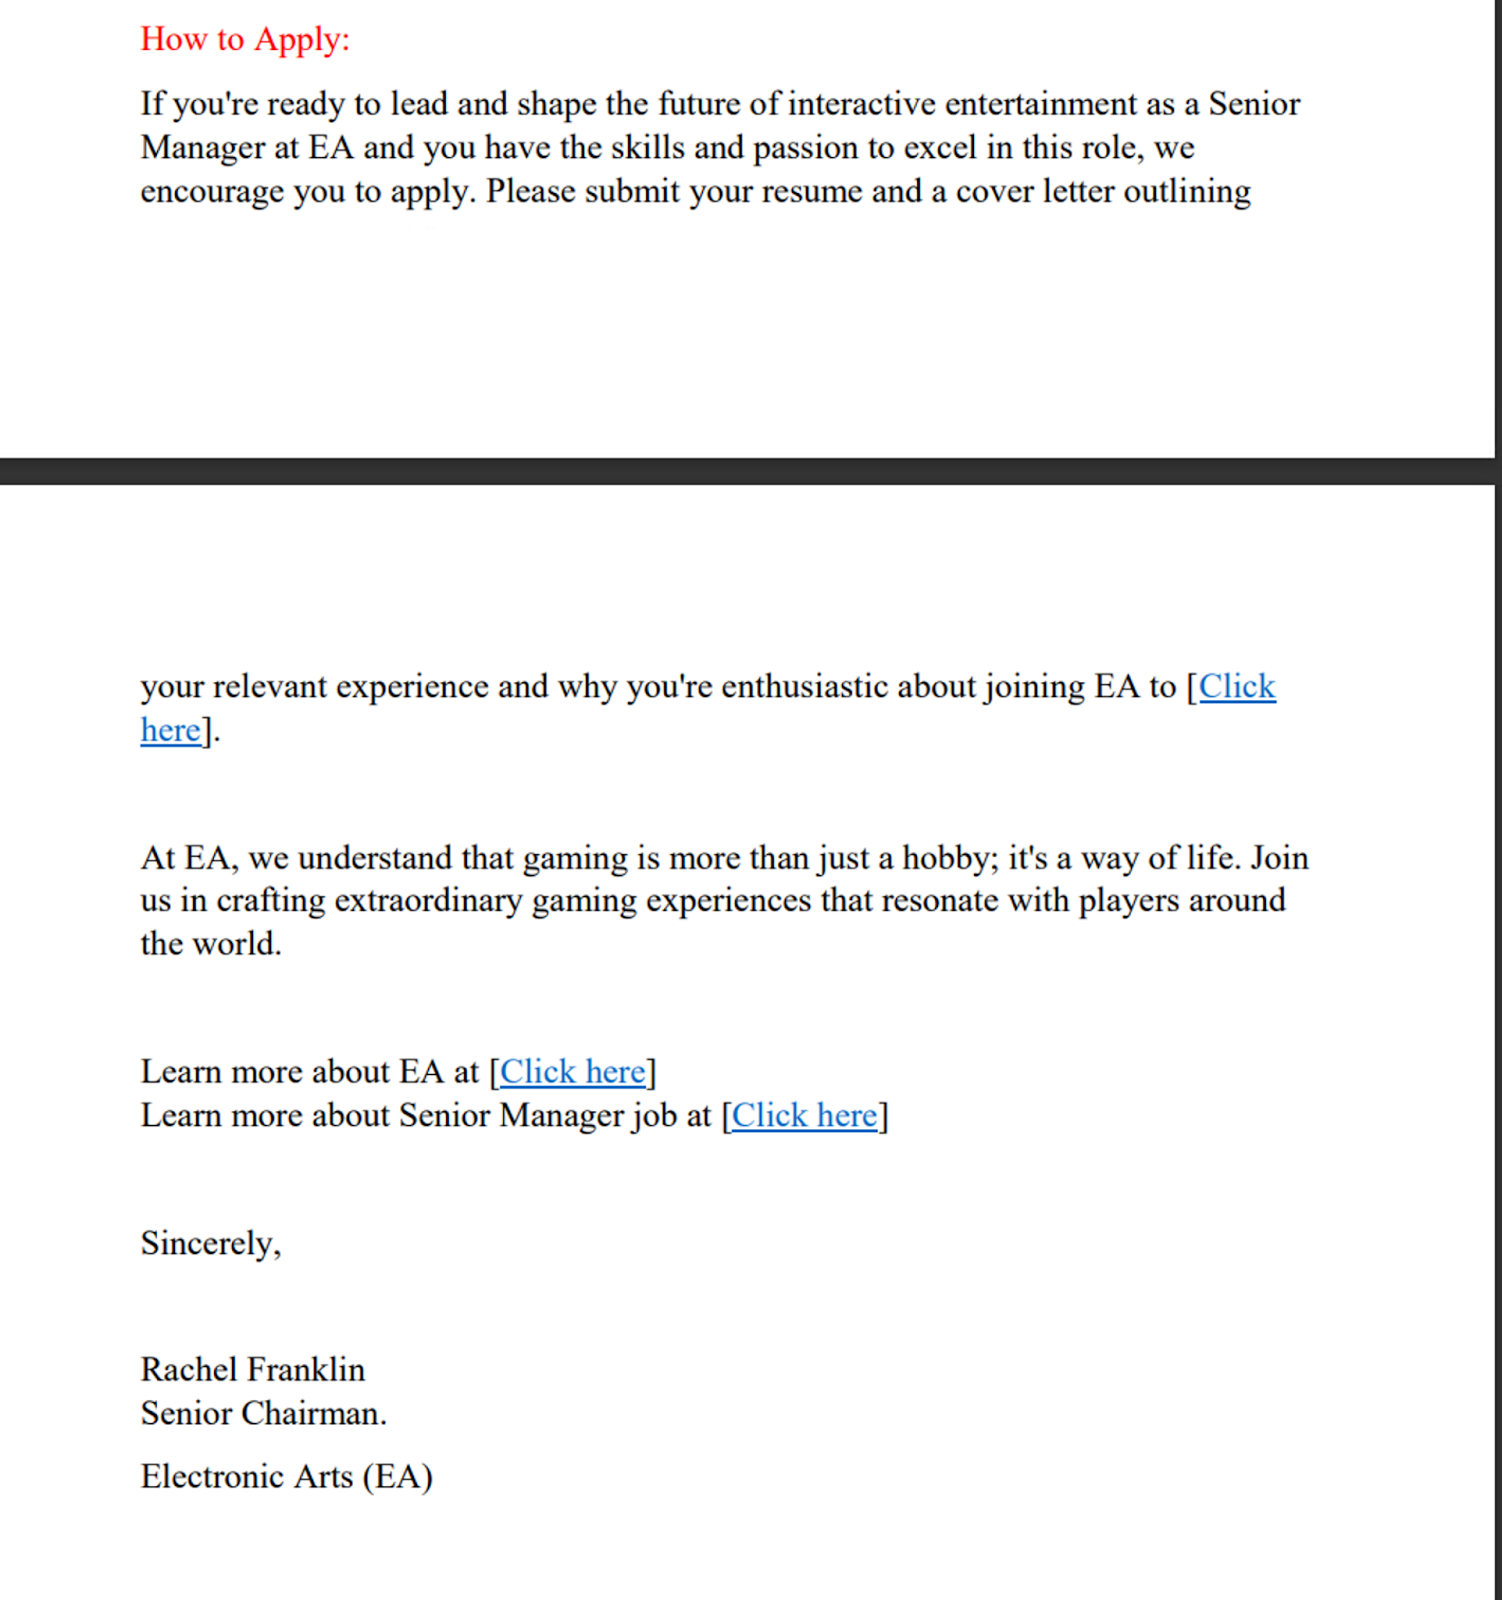
The other link downloads a ZIP file from Microsoft OneDrive. The ZIP file has some video files and two files that look like Word documents but are malware.
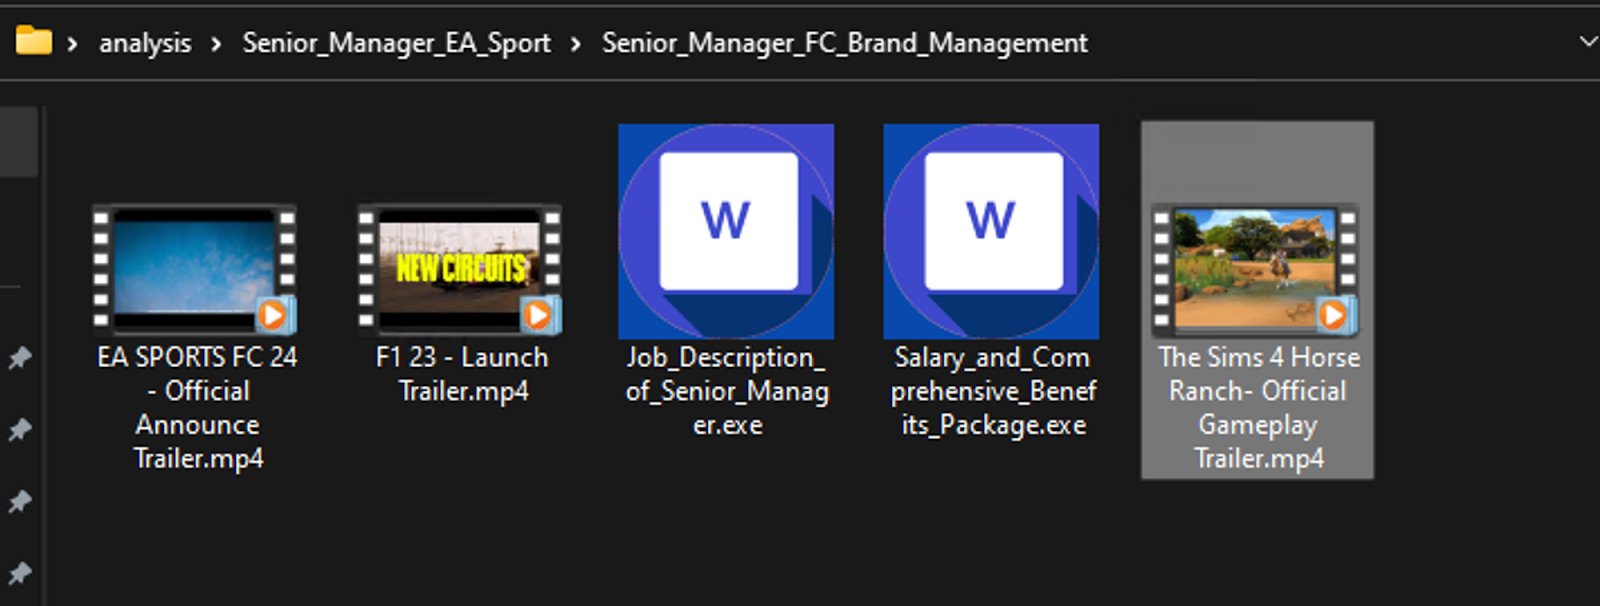
The malware files are very hard to detect by antivirus software because they use a special technique called single-file application. They hide the malicious code inside other files of the application.
If you run the malware files, they will infect your computer and try to steal your information, such as cookies, session data, and browser credentials.
They will also try accessing your Facebook Business account using the linked email.
Some hackers have made a fake DLL file that can spy on your web browser and send your data to them through Telegram.
They trick you into running this file by sending you a PDF with a LinkedIn job offer.
The DLL file is made with Microsoft .NET and was created on September 18, 2023. It checks if there is another copy of itself running on your computer.
If not, it makes a file with information about your computer, like your GUID and IP address. It also opens a PDF file with a job description to make you think everything is normal.
The DLL file then contacts the hackers through Telegram, using a BOT ID 6263348871. It sends them a message with your ChatID and some text.
Then, it sends them ZIP files with your data using the /sendDocument API. The hackers have a configuration file with encryption keys, the Telegram Bot’s Token, the ChatID, and some email addresses.
The DLL file can steal cookies, session information, and saved credentials from web browsers like Microsoft Edge, Google Chrome, Brave Browser, and Mozilla Firefox.
The hackers can use this data to pretend to be you online and access your accounts.
The DLL file also keeps running in the background, sending more data to hackers.
It can also try to take over your Facebook Business account by sending links to email addresses from the configuration file.
If you click on these links, the hackers might get access to your Facebook Business account.
This very dangerous and clever attack targets professionals who use LinkedIn.
You should be careful about opening files or links from unknown sources and always use antivirus software to protect your computer.
Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.


