Monday, October 5, 2026

WordPress Easy WP SMTP zero-day Vulnerability Exposes Hundreds of Thousands of Sites to Hack

Easy WP SMTP, a WordPress plugin, with more than 500,000 installations, allows one to configure and send all outgoing mails via a SMTP server, the major benefit of which is that the mails do not end up in the recipient’s junk/spam folder.

The team managing this plugin had fixed a zero-day vulnerability affecting versions 1.4.2 (current version 1.4.4) and lower that would allow an unauthenticated user to reset the admin password which would enable the hacker to take complete control of the website.

The vulnerability is in a debug file that is exposed because of a fundamental error in how the plugin maintained a folder.

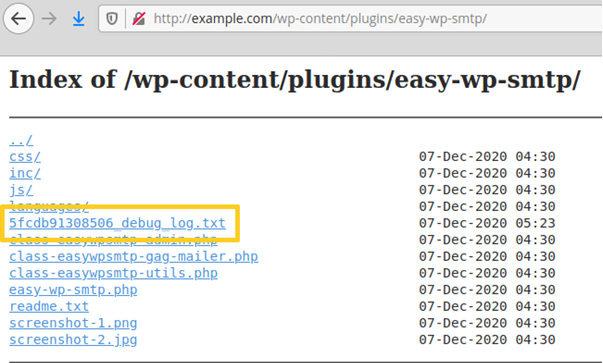
The Easy WP SMTP plugin has an optional debug log where it writes all email messages (headers and body) sent by the blog. It is located inside the plugin’s installation folder, “/wp-content/plugins/easy-wp-smtp/”.

The log is a text file with a random name, e.g., 5fcdb91308506_debug_log.txt. The plugin’s folder doesn’t have any index.html file, hence on servers that have directory listing enabled, hackers can find and view the log:
https://blog.nintechnet.com/wp-content/uploads/2020/12/easy-wp-smtp-zero-day_1.png

Once this is done, the username enumeration scan is performed to find the admin login.
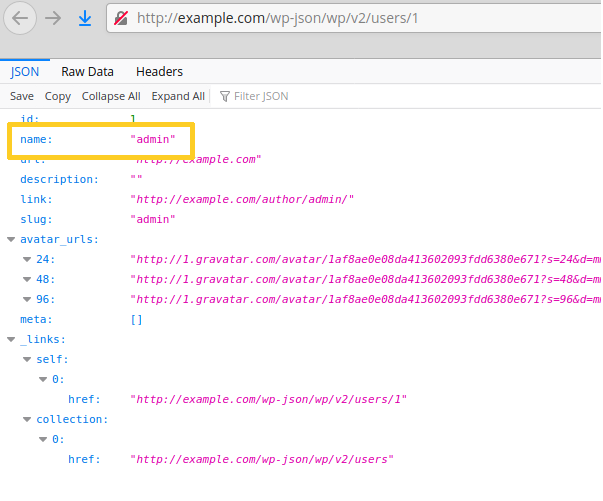
Hackers can also perform the same task using the author achieve scans (/?author=1).They access the login page and ask for the reset of the admin password:

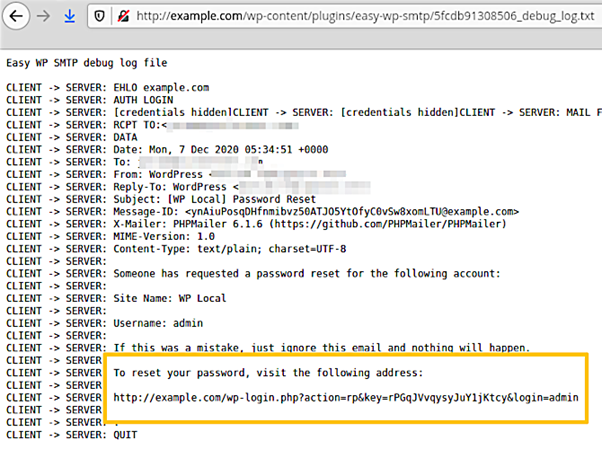
Then, they access the Easy WP SMTP debug log again in order to copy the reset link sent by WordPress:
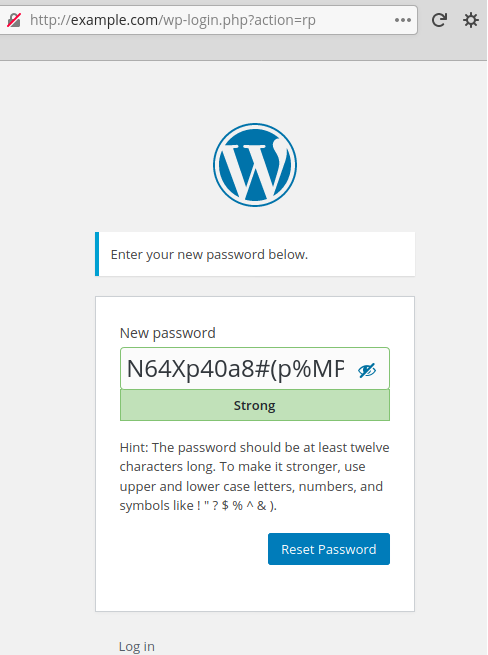
Once the link is received, they reset the admin password:
Once they had logged in to the admin dashboard, rogue plugins were installed.

It is highly recommended and advised that all users immediately update this plugin.

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.

Also Read

100,000 WordPress Sites Impacted with Cross-Site Scripting(XSS) Flaw

Massive Hacking Campaign Targets WordPress Websites to Steal Database Credentials

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Cling Malware Masquerades as Google STUN Traffic to Control Compromised IoT Devices

A newly identified IoT botnet, Cling, disguises its command-and-control...

Microsoft Warns ClickFix Attacks Use Fake CAPTCHA Lures to Execute Malicious Commands

Microsoft Threat Intelligence has identified a ClickFix campaign in...

Critical GitLab AI Gateway Flaw Lets Attackers Execute Arbitrary Commands

GitLab has issued emergency security updates for a critical...

AWS AI Agent Vulnerabilities Let Attackers Bypass Authentication and Steal Credentials

AWS has released security fixes for four vulnerabilities affecting...

Citrix NetScaler Appliances Reboot Repeatedly After 0-Day Security Update

Citrix NetScaler administrators report repeated appliance crashes and forced...

Sony PS5 Relapse Jailbreak Exploit Uses JSC Memory Corruption and Kernel UAF

A newly released PlayStation 5 jailbreak chain, called Relapse,...

Zammad Vulnerabilities Let Attackers Execute Code and Escalate Privileges to Root

Two critical vulnerabilities in the open-source Zammad helpdesk and...

Safari History Database Tags Can Reveal Users’ Browsing Themes in Forensic Investigations

Safari's History database contains a lesser-known tagging artifact that...

Related Articles

Recent News