
Educational institutions are now facing a coordinated mix of state espionage, spear‑phishing, and supply chain intrusions, even as classic ransomware and vulnerability volumes show signs of easing.
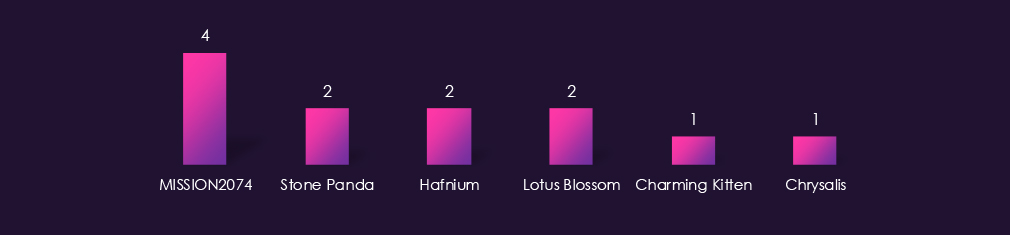
Every attributed campaign was linked to state actors, with no financially motivated groups observed. China-aligned clusters led by MISSION2074 dominate, with additional activity from Stone Panda, Hafnium, Lotus Blossom, and Iran-linked Charming Kitten.
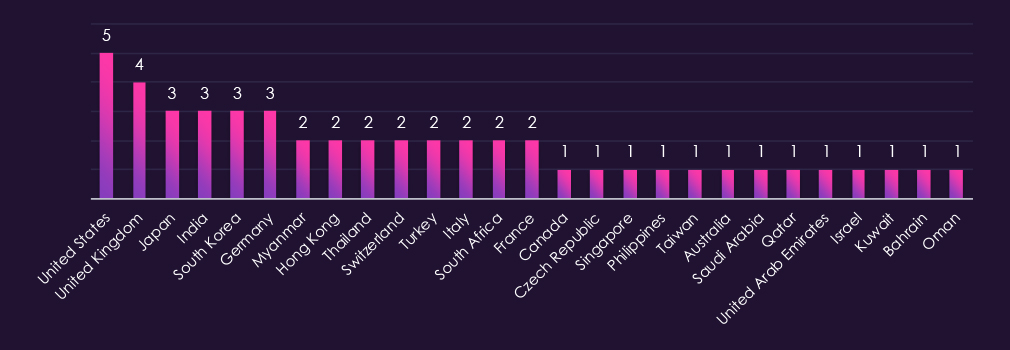
Victims span 27 countries, led by the United States, followed by the United Kingdom, Japan, India, South Korea, and Germany, reflecting the sector’s global research footprint.
CYFIRMA telemetry shows a clear shift toward state-driven APT activity against education. In the last 90 days, education organizations appeared in 5 of 25 tracked APT campaigns, after recording zero presence in the previous period.
Unlike other industries, attackers focused on email, FTP, and SSHD servers rather than VPNs and routers, signaling a priority on research data and institutional communications over raw infrastructure compromise.
Supply Chain and Spear‑Phishing
Publicly reported cyber incidents against education remain relatively low in volume but are strategically targeted.
Over 90 days, 12 education incidents were identified, just 1.49% of all industry‑linked reports, ranking the sector 10th of 14.
Where techniques were disclosed, supply chain intrusions and spear‑phishing each appeared twice, blending infrastructure compromise with highly targeted social engineering.
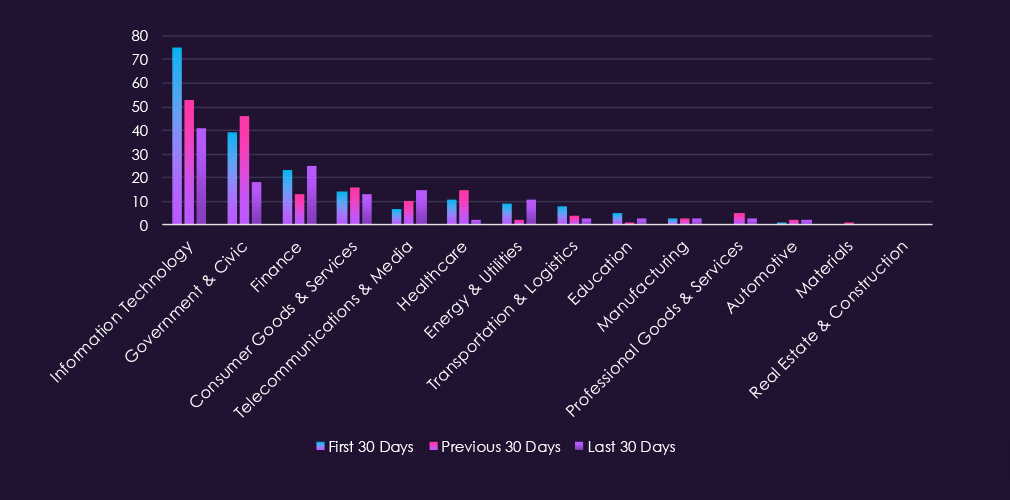
Activity dropped sharply from nine incidents in the first month to one or two in each subsequent 30‑day window, suggesting quieter but more selective operations.
BYOVD (Bring Your Own Vulnerable Driver) surfaced once, indicating the use of more advanced, defense‑evasion tradecraft usually associated with APTs.
China was the only identified attacking country in these reports, and victims were concentrated in the United States, the United Kingdom, Taiwan, and Italy.
On underground and dark web forums, education accounted for 3,536 mentions out of 46,851 industry‑linked references, or 7.55%, placing the sector 7th overall. The chatter profile, however, is changing rapidly.
Mentions of data breaches and leaks initially climbed before collapsing in the final period, while ransomware and claimed hacks also declined.
In their place, hacktivism grew more than sevenfold and DDoS chatter exploded 24‑fold in the final 30 days, pointing to ideologically motivated campaigns aimed at disrupting online learning platforms and university portals rather than monetizing stolen records.
This pivot toward disruption aligns with broader reporting that education remains one of the most frequently attacked sectors globally, in part due to exposed remote services, flat networks, and vast personal data stores.
Vulnerabilities and Ransomware
Vulnerability telemetry paints a more moderate picture. Education accounted for 156 of 3,959 industry‑linked CVE mentions (3.94%), ranking 9th of 14.
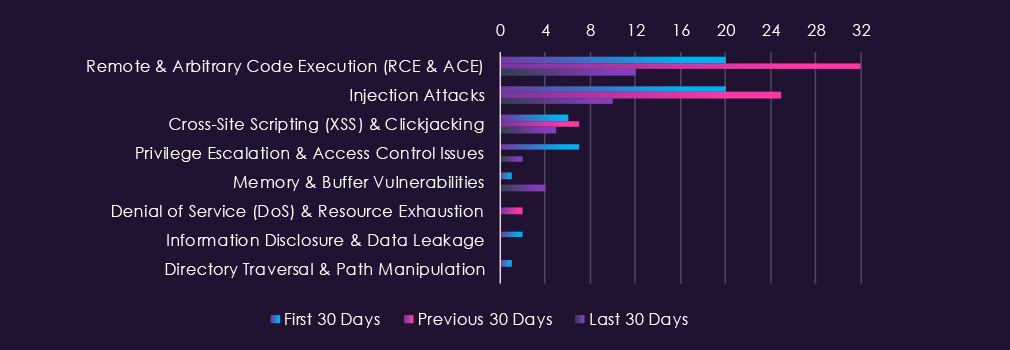
High‑impact remote code execution and injection vulnerabilities spiked mid‑period before falling sharply, while categories like cross‑site scripting, privilege escalation, and denial of service remained at low, uneven levels.
This suggests a concentrated disclosure window rather than a sustained escalation in exploitable weaknesses.
Ransomware, historically a top concern for schools and universities, is trending downward in this dataset. CYFIRMA recorded 54 verified education victims, just 2.36% of 2,291 global cases, placing the sector 13th out of 14.
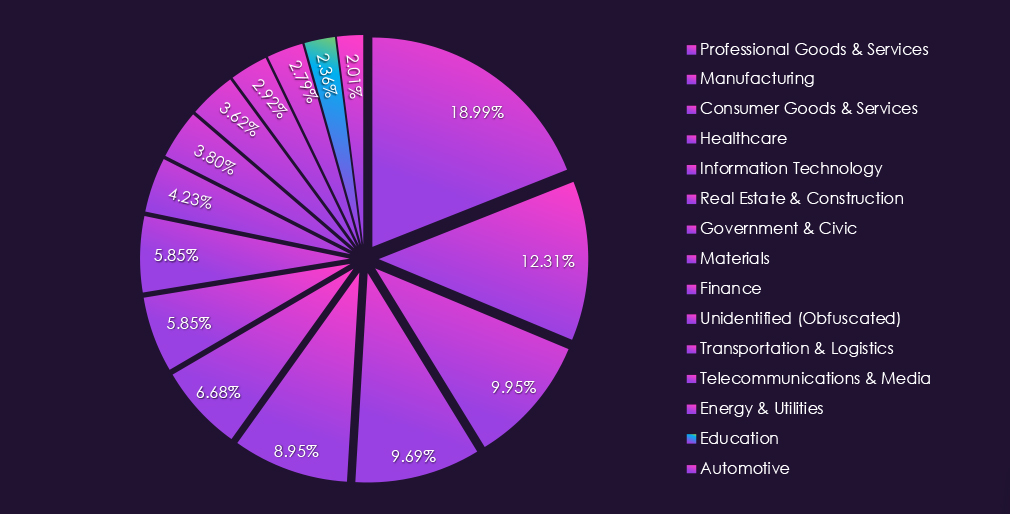
That figure represents a 25% drop from the previous quarter’s 72 victims, with overall share also declining from 3.29% to 3.04%.
Universities and research institutes remain the primary targets, followed by public schools and districts, but gang participation is only 29%, the lowest of any sector.
Most groups spread their efforts thinly; Interlock is the outlier, directing 27.3% of its victims at education, indicating a niche but deliberate focus.
State‑aligned espionage, spear‑phishing, and supply chain compromises are converging on universities and research institutions, while dark‑web‑driven hacktivism and DDoS aim to knock critical services offline.
Taken together, the indicators show an education sector where classic ransomware and vulnerability volumes are easing, but strategic risk is rising.
For security teams, this means shifting priority from just backup and patching to hardening email and research infrastructure, securing third‑party links, and preparing for ideologically motivated disruption rather than purely financial extortion.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


