A new wave of Emotet malware campaign With New Wi-Fi Spreader takes advantage of the wlanAPI interface to enumerate all Wi-Fi networks in the area and spreads the infection.
The Emotet is a banking Trojan detected in the year 2014, it was designed to steal sensitive and private information.
It is one of the most dangerous malware and it is capable of delivering payloads based on the specific tasks. It’s warm like capability helps to spread rapidly with other connected computers.
Emotet primarily distributed through social engineering techniques such as the emails with the links to download the malware.
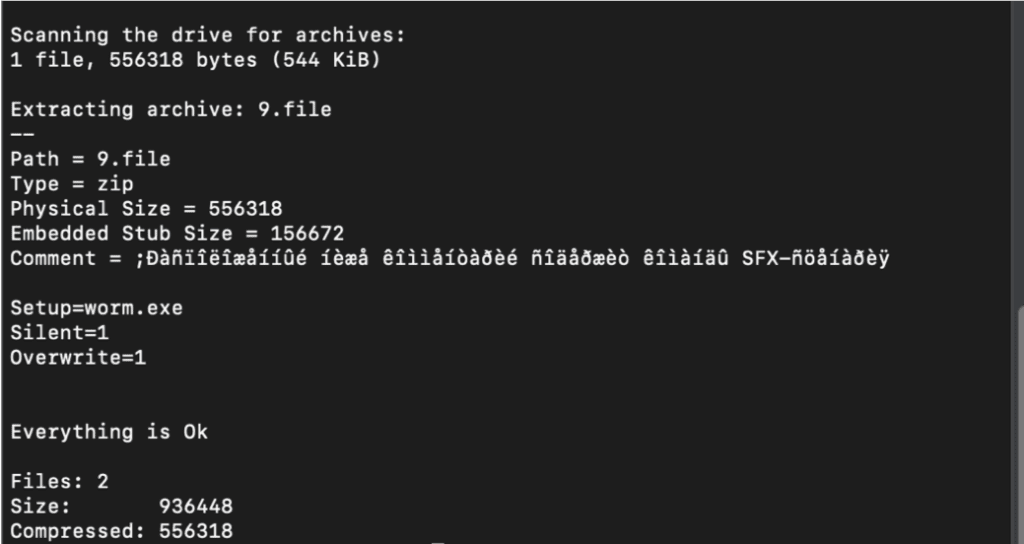
With the new Emotet campaign it arrives with a new Wi-Fi Spreader module downloads to the system C:\ProgramData. The downloaded binary contains a self-extracting RAR that has two (service.exe and worm.exe) binaries to spread the infection through WiFi.
The worm.exe is the executable used for spreading the malware, once it executed it copies the service.exe to a variable for using it while spreading.
Then it calls wlanAPI.dll class that used by Native Wi-Fi to manage the wireless network profiles and connections for spreading the infection to other networks.
“The Worm enumerates all Wi-Fi devices currently enabled on the local computer, which it returns in a series of structures. These structures contain all the information relating to the Wi-Fi device, including the device’s GUID and description,” read the Binary Defense analysis.
It gathers possible information from every available Wi-Fi network present in the list of networks.
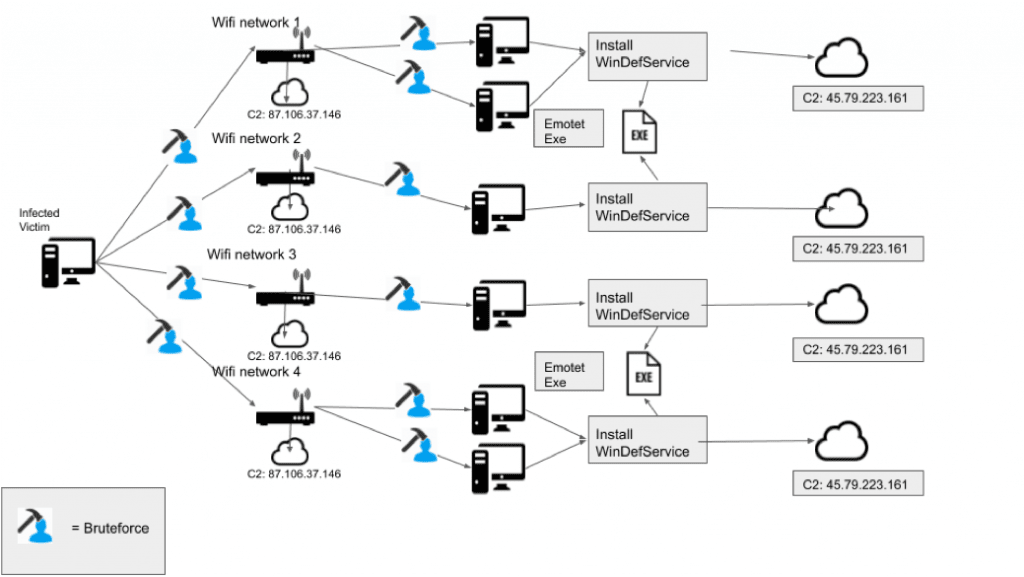
Once the connection established with the Wi-Fi network it enumerates users and attempts brute-force for all users on the network.
Next, the Service.exe is the payload installed by worm.exe on the machine, once installed it communicates with the C2 server and executes the binary embedded in service.exe.
Previously Emotet known to distributed only through malspam and infected networks, with this new loader it spreads through nearby wireless networks that use weak passwords.
9.file            865cf5724137fa74bd34dd1928459110385af65ffa63b3734e18d09065c0fb36

Worm.exe    077eadce8fa6fc925b3f9bdab5940c14c20d9ce50d8a2f0be08f3071ea493de8

Service.exe    64909f9f44b02b6a4620cdb177373abb229624f34f402335ecdb4d7c8b58520b
Attackers abused compromised ConnectWise Cloud Backup credentials to access Microsoft 365 customer environments, prompting ConnectWise…
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds…
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to…
A newly disclosed OpenBSD kernel exploitation chain combines a shared memory accounting flaw with a…
GhostAction attackers have expanded their GitHub credential theft campaign with a second stage that disguises…
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with…