
ESET’s H1 2026 threat report shows attackers accelerating the use of familiar playbooks with AI-flavored lures, social engineering, and defense evasion rather than inventing entirely new ones.
The clearest signals are the rise of malicious AI skills, a doubled ClickFix footprint, first-wave AI-powered Android malware, record QR-code phishing, and a growing ecosystem of EDR killers.
That matters because AI agents access are increasingly allowed to browse, execute commands, access files, and interact with third-party services, which turns small “skills” into high-risk supply-chain components.
The report highlights behaviors such as credential loading, obfuscation, command execution, and tool downloading as warning signs that can mask abuse inside otherwise useful automation.
For defenders, the key shift is that compromise is no longer limited to prompt injection; it can now land in the agent’s extensions, scripts, and dependencies.
ClickFix continues to be one of the most effective initial-access patterns because it exploits urgency and user trust.
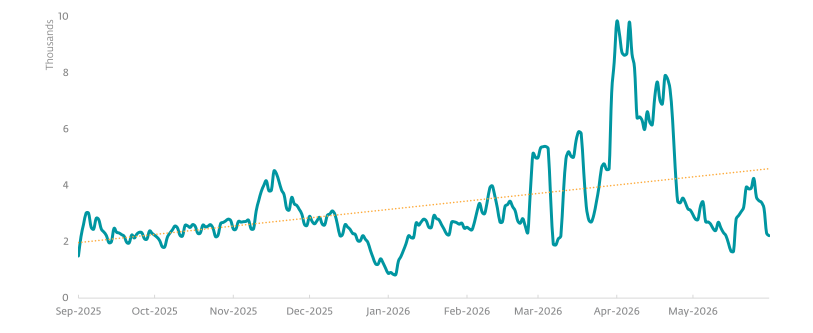
ESET says detections under HTMLFakeCaptcha grew 108 percent between H2 2025 and H1 2026, with the technique moving beyond fake CAPTCHA boxes into AI-themed help pages, browser environments, workspace workflows, and even macOS lures.
ESET Researchers said that, nearly 900,000 AI skills from public repositories and found 25,000 suspicious and more than 3,000 outright malicious entries.
The newer AI-fix variant is especially telling: attackers reuse legitimate AI branding to make fake troubleshooting steps look authoritative, while the actual execution chain remains the same old copy-paste-and-run payload path.
ESET Threat Report H1 2026
CrashFix and ConsentFix show the same trend in different settings, using browser errors and OAuth token theft to hijack sessions without traditional credential capture.
PromptSpy stands out as the first known Android malware to use generative AI at runtime, according to ESET. It behaves like a remote-access trojan, but it also calls Gemini to interpret on-screen UI elements and decide which gestures to execute, helping the malware adapt across devices without relying on hardcoded taps.
That is a meaningful evolution because Android UI automation has always been brittle, and the use of LLMs can make malware more resilient to interface changes.

Even if current guardrails slow adoption, the report suggests this design pattern could become attractive for thin-client malware that offloads logic to AI services.
Ransomware crews still rely heavily on EDR killers to blind defenses before encrypting systems. ESET says it tracks more than 100 such tools, with BYOVD remaining the dominant method because a vulnerable but legitimate driver can terminate protected processes from the kernel.
The report notes more than 60 EDR killers abusing over 40 different drivers, with new variants appearing weekly. That is a strong indicator that defense evasion has become a commodity layer in ransomware operations, not a specialty skill.
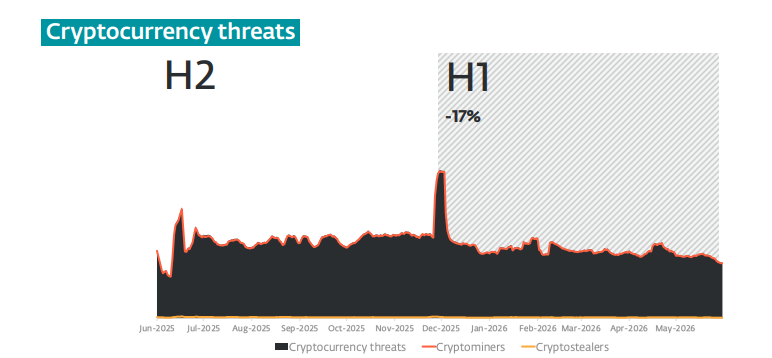
The operational theme across H1 2026 is adaptation speed. Attackers are packaging old techniques inside newer interfaces, whether that means AI branding, QR codes, browser prompts, or autonomous agent tooling.
For defenders, this reinforces three priorities: inspect AI supply chains, harden user-assisted execution paths, and treat EDR tampering as a core ransomware signal rather than a post-compromise afterthought.
Relevant related details in the report include QR-code phishing reaching record levels, continued ransomware pressure despite lower ransom payment rates, and the emergence of additional defense-evasion tooling used in active intrusions.
Stop Accepting SLAs Written for 2019 SOCs – Here’s the 2026 AI SLA Vendor Checklist – Download Free AI SOC SLA Guide