
Ransomware operators are now abusing Ethereum smart contracts as stealthy command‑and‑control resolvers, with a Gentlemen ransomware affiliate using the EtherRAT backdoor to pull rotating C2 domains directly from the blockchain instead of hardcoding them in the malware.
The toolkit shows a clear progression: scheduled tasks that bootstrap PowerShell, privileged account creation (“support2” with Supp0rt2@2026!).
LSASS and registry‑hive dumping, ESET service tampering, and multiple tunneling and reverse‑shell payloads staged for lateral movement and eventual ransomware deployment.
The same server and a secondary open directory at 77.110.122[.] Huntress had previously flagged 137 as proxy infrastructure in The Gentlemen’s defense‑evasion TTPs.
Hunt.io’s IOC Hunter and AttackCapture telemetry now tie those endpoints to Sliver beacons, SOCKS proxies, and EtherRAT delivery.
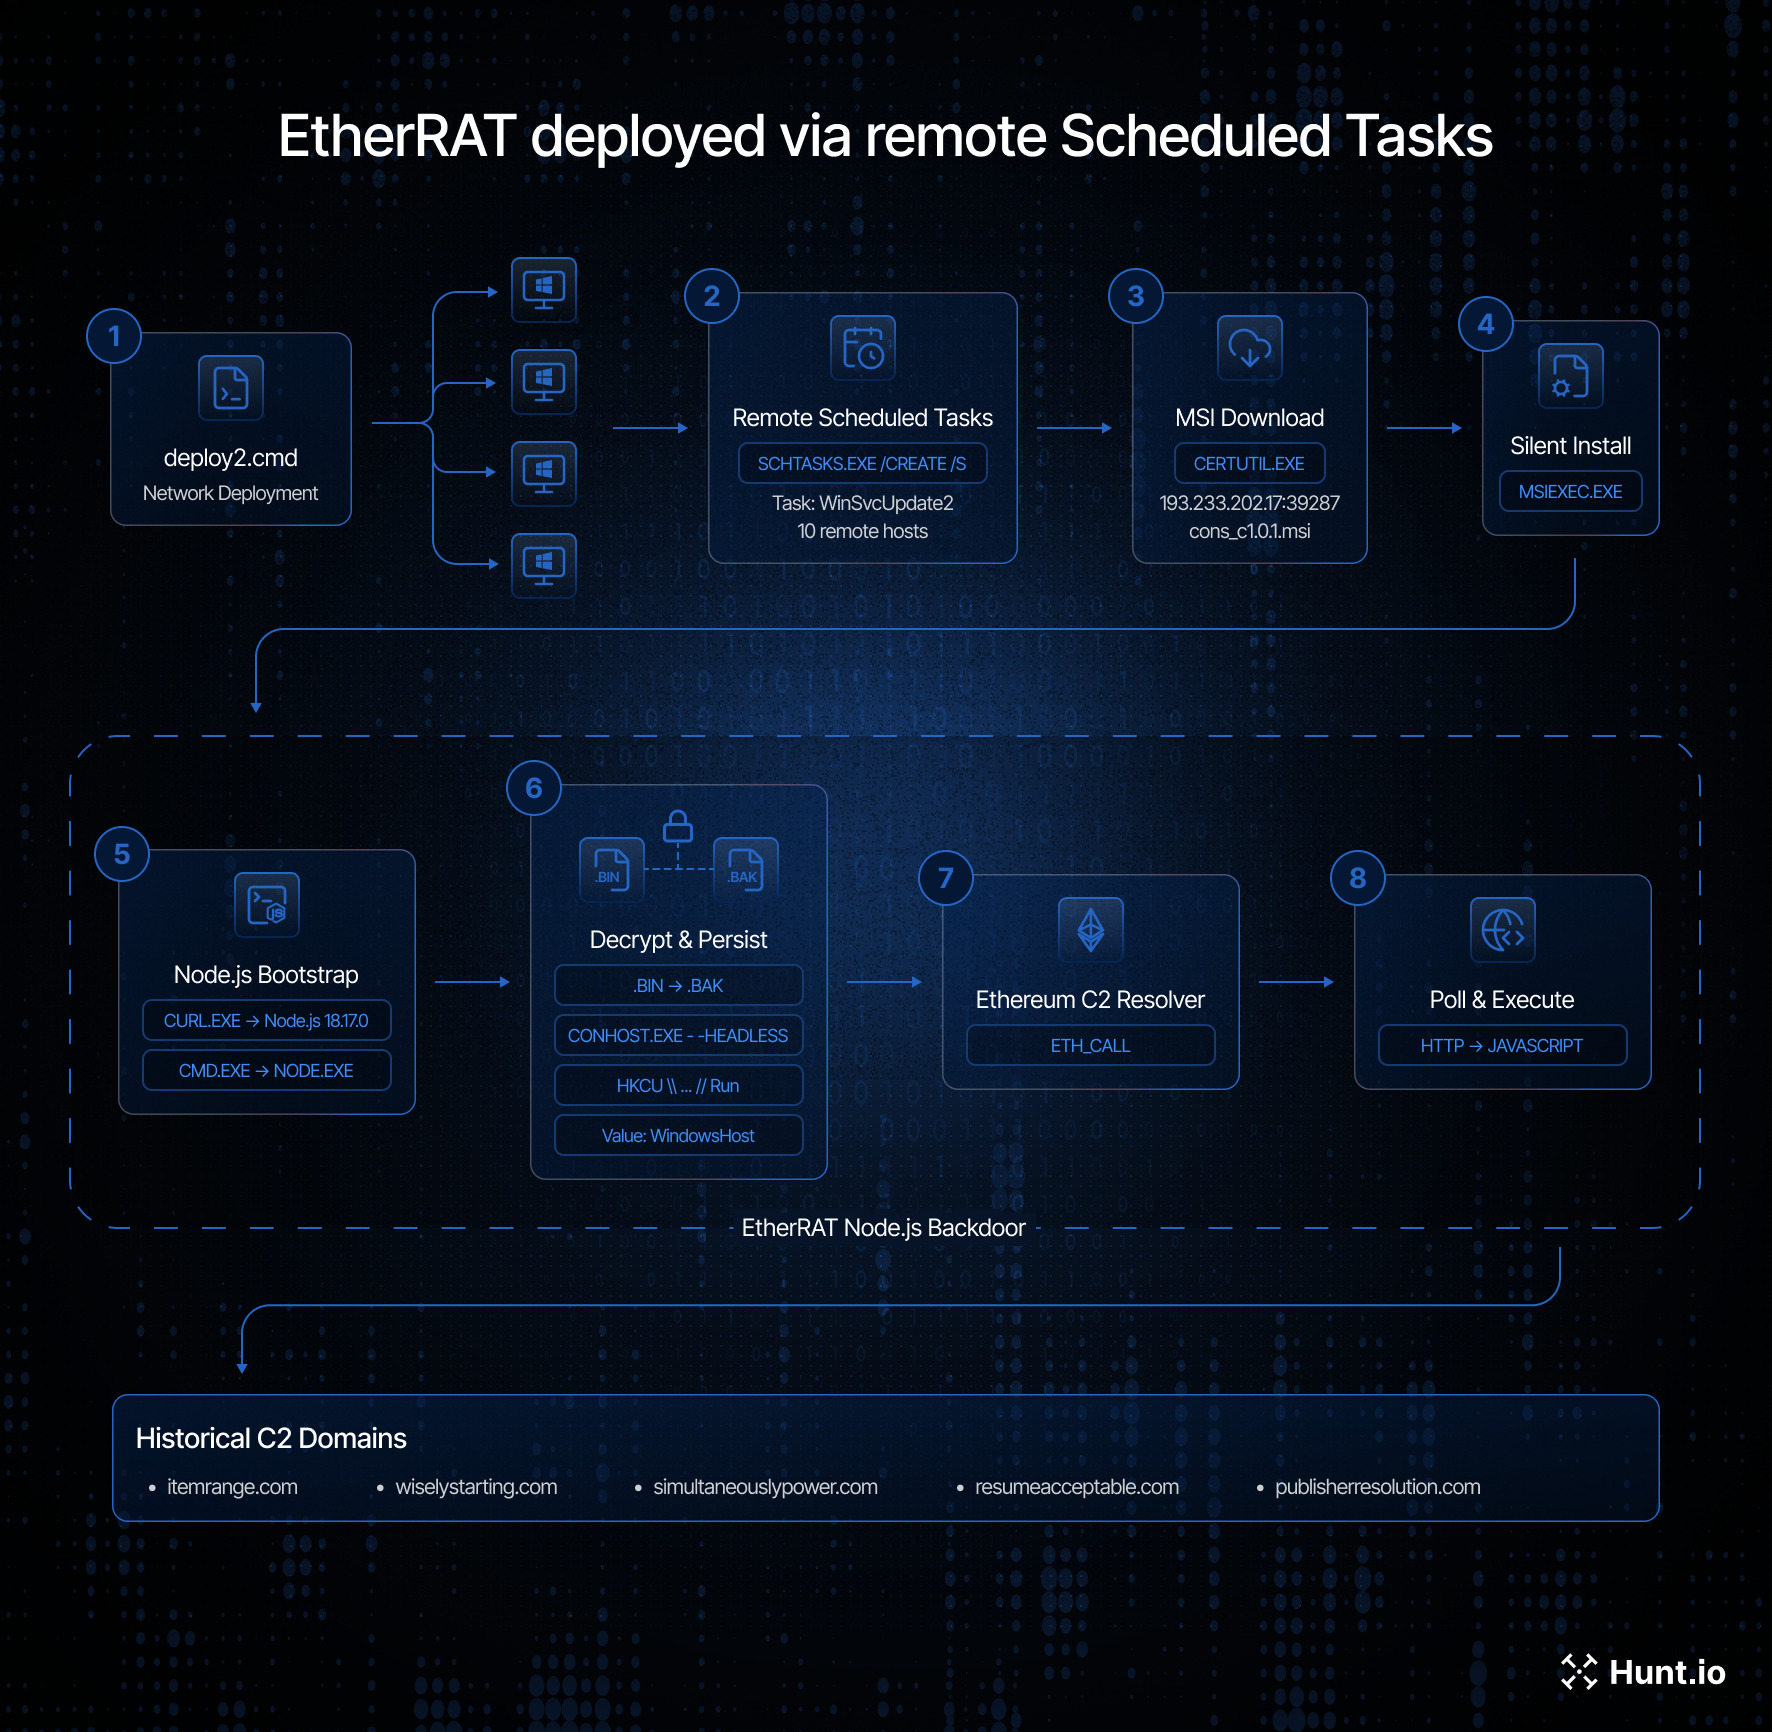
At the core of this campaign is EtherRAT, a Node. js‑based remote access trojan delivered via MSI payloads (cons_c1.0.1.msi / cons_1.0.1.msi) and deployed at scale via remote scheduled tasks.
Once cu.msi has run through certutil.exe and msiexec.exe, EtherRAT prepares a portable Node.js runtime if missing, decrypts an XOR‑encoded backdoor, and establishes Run‑key persistence under “WindowsHost,” launching its payload via conhost.exe in headless mode.
Instead of embedding fixed infrastructure, EtherRAT hardcodes an Ethereum smart contract a lookup key, and a selector, then queries a pool of public Ethereum RPC endpoints Tenderly, Flashbots, MEVBlocker, BlastAPI, PublicNode, drpc.org, merkle.io to resolve its current C2 domain.
Every C2 rotation is written permanently on‑chain, giving operators cheap, takedown‑resistant agility while handing defenders a historical ledger of all prior domains.
In this operation, the contract reveals five sequential C2s publisherresolution.com, resumeacceptable.com, simultaneouslypower.com, wiselystarting.com, itemrange.com mirroring EtherHiding‑style campaigns previously documented in npm ecosystem supply‑chain attacks and other Ethereum‑powered malware.
Hunt.io Researchers said that, an exposed open directory on 193.233.202[.]17 captured a Gentlemen ransomware affiliate mid‑operation, exposing 82 local artifacts (145 MB) that reconstruct the full intrusion chain against a Windows domain.

EtherRAT’s C2 protocol abandons traditional command schemas. Beacon traffic masquerades as benign static asset requests, with randomized paths and extensions (png, jpg, gif, css, ico, webp).
Ethereum Smart Contracts
Parameters (“id”, “token”, “key”, “b”, “q”, “s”, “v”), while a custom X‑Bot‑Server header identifies the resolved controller an indicator already seen in other EtherRAT and DPRK‑adjacent campaigns.
Any HTTP response longer than ten characters is treated as JavaScript source code and executed via a dynamically constructed async function with access to require, process, Buffer, filesystem paths, and console.
This design gives the operator arbitrary code execution on infected hosts, lets them continuously extend functionality without redeploying implants, and further blurs behavioral signatures.
EtherRAT also persists identity via UUID‑based bot IDs stored in local configuration and svchost.log telemetry, so compromised hosts remain consistently trackable across sessions.
The open directory shows that EtherRAT is only one layer in a dense C2 mesh. Sliver shellcode, dynamically fetched via inject_sliver.ps1 and executed in memory, beacons over TLS to 193.233.202[.]17.
The VOCATIONAL_GORILLA profile, while multiple Go binaries (pb39_new.exe, update.exe, ws_stable.exe, ws35.exe, ws36.exe, ws_3srv.exe) implement concurrent reverse shells to 193.233.202[.]17, 146.103.127[.]44, and 77.110.126[.]46.
Chisel and Ligolo‑ng provide SOCKS‑style tunneling from C:\ProgramData\csvc.exe back to 193.233.202[.]17:22673, enabling operators to pivot through victim networks using commodity tooling.
Pivoting on the recovered binaries and Hunt.io telemetry clusters the campaign around AS203273 (NetCrafters OU) with historical ties to AEZA ASN ranges, plus a third EtherRAT cluster on 77.110.122[.]58 using the same smart contract and MSI naming convention.
Additional EtherRAT C2s on 38.110.228[.]43 and 38.110.228[.]125 sit in the same /24 as 38.110.228[.]33, a VPS endpoint highlighted by Gambit Security that exposed victim artifacts for a US‑based Gentlemen case, reinforcing attribution and linking blockchain‑anchored C2 to a specific ransomware ecosystem.
IOCs
| Indicator | ASN | Provider | Country | Context |
|---|---|---|---|---|
| 193.233.202[.]17 | AS203273 | NetCrafters OU | Estonia | Primary staging, C2, Sliver, tunnelling and registry-hive exfiltration server. |
| 146.103.127[.]44 | AS216071 | SERVERS TECH FZCO | Netherlands | Secondary controller compiled into the multi-controller Go reverse-shell family. |
| 77.110.126[.]46 | AS203273 | NetCrafters OU | Estonia | Secondary controller compiled into the multi-controller Go reverse-shell family. |
| 77.110.122[.]137 | AS203273 | NetCrafters OU | Estonia | Case-observed The Gentlemen infrastructure. |
| 77.110.122[.]58 | AS203273 | NetCrafters OU | Estonia | Staging server associated with cons_1.0.1.msi. |
| 38.110.228[.]43 | AS174 | Cogent Communications, LLC | United States | Historical resolution for wiselystarting[.]com. |
| 38.110.228[.]125 | AS174 | Cogent Communications, LLC | United States | Historical resolution for itemrange[.]com. |
| 38.110.228[.]33 | AS174 | Cogent Communications, LLC | United States | Open directory containing disclosed The Gentlemen victim artefacts |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Why use the 2026 Agentic SOC Buyer’s Guide? 8 Best Platforms Compared – Download the 2026 Buyer’s Guide





